 Pierluigi Paganini
 August 29, 2022
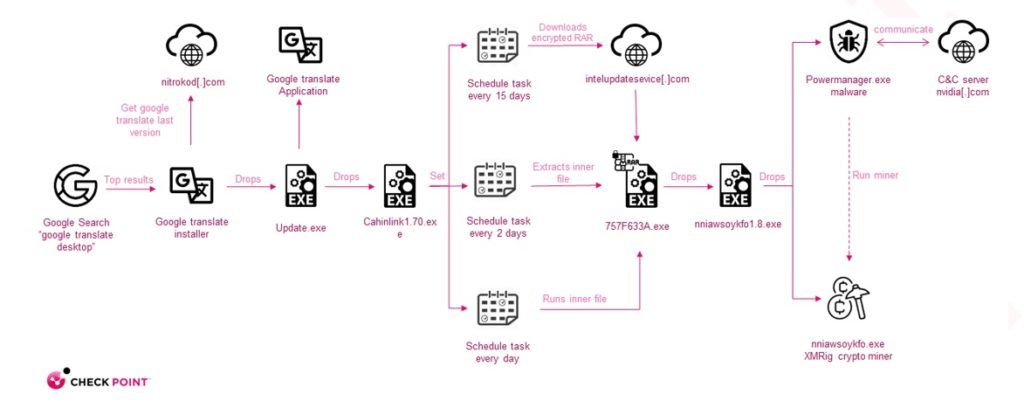
Researchers spotted a Turkish-based crypto miner malware campaign, tracked as Nitrokod, which infected systems across 11 countries. Check Point researchers discovered a Turkish based crypto miner malware campaign, dubbed Nitrokod, which infected machines across 11 countries The threat actors dropped the malware from popular software available on dozens of free software websites, including Softpedia and […]
 Pierluigi Paganini
August 29, 2022
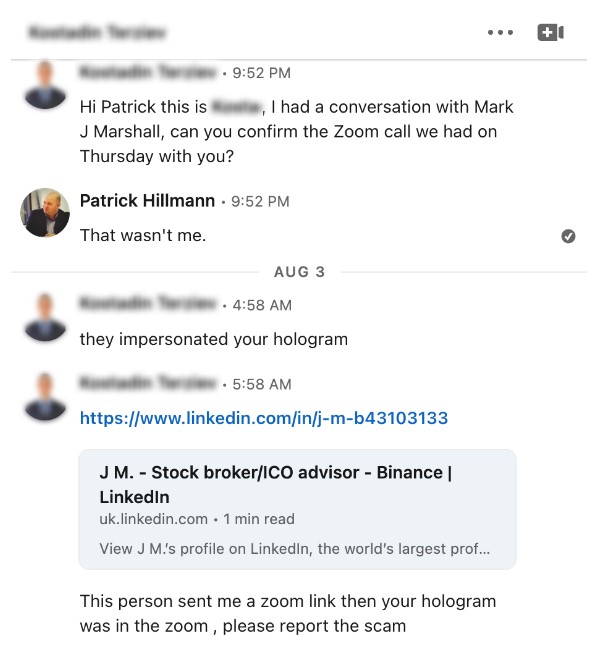
Scammers used a deepfake AI hologram of the Binance chief communications officer for fraudulent activities. Patrick Hillmann, chief communications officer of Binance, confirmed that scammers used his Deepfake AI hologram to trick users into online meetings and target the projects of clients of the company. Hillmann explained in a blog post that the attack was […]
 Pierluigi Paganini
August 29, 2022
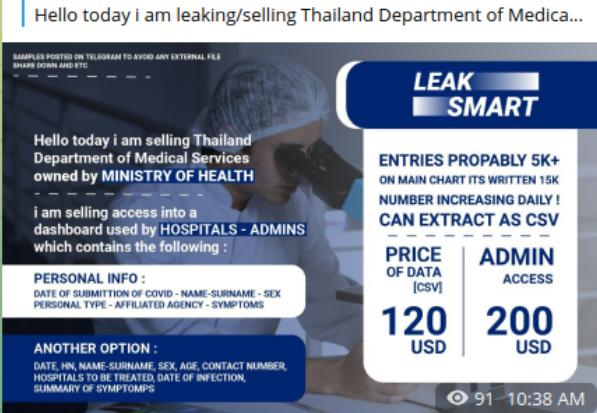
Researchers discovered leaked PII stolen from Thailand’s Department of Medical Sciences containing information about citizens with COVID-19. Resecurity, a California-based cybersecurity company protecting Fortune 500, has identified leaked PII stolen from Thailand’s Department of Medical Sciences containing information about citizens with COVID-19 symptoms. The incident was uncovered last week and shared with Thai CERT. The […]
 Pierluigi Paganini
August 28, 2022
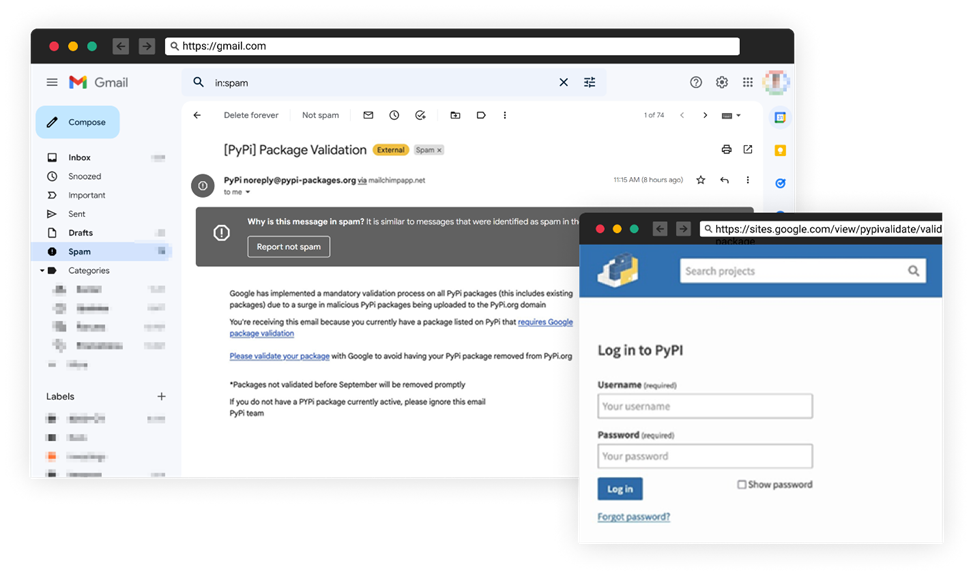
The Python Package Index (PyPI) warns of an ongoing phishing campaign to steal developer credentials and distribute malicious updates. The Python Package Index, PyPI, this week warned of an ongoing phishing campaign that aims to steal developer credentials and inject malicious updates to the packages in the repository. “Today we received reports of a phishing […]
 Pierluigi Paganini
August 28, 2022
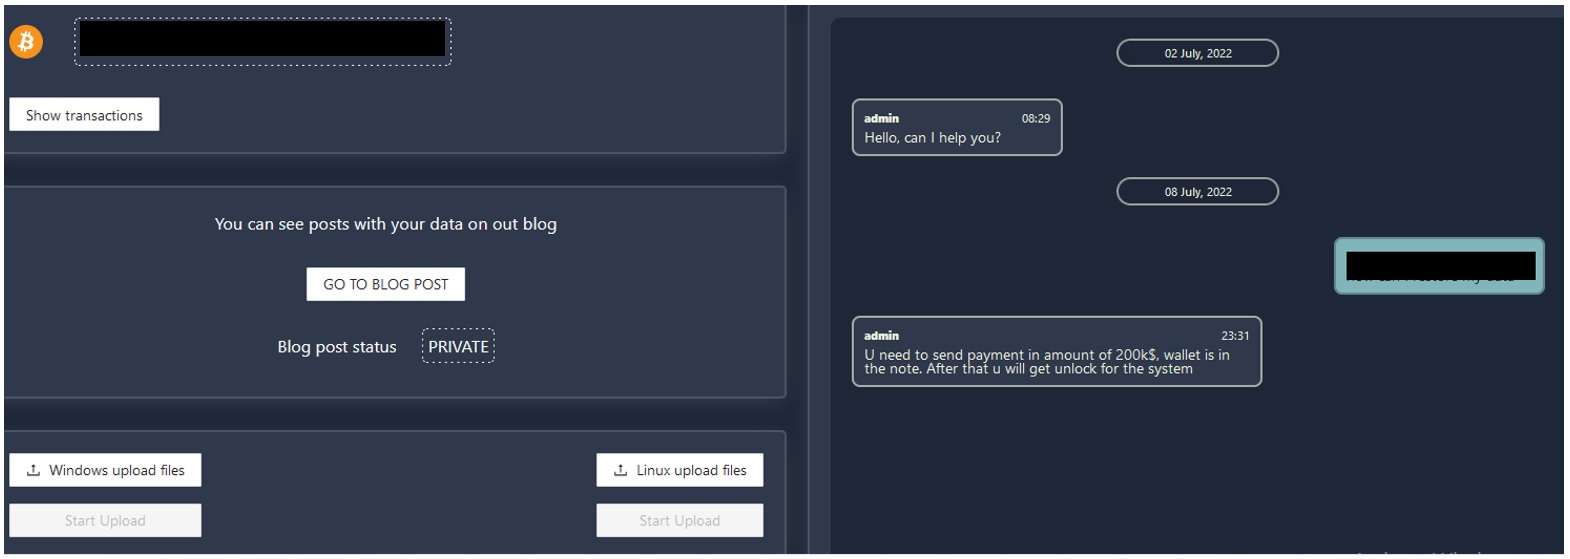
Trend Micro researchers warn of a new ransomware family called Agenda, which has been used in attacks on organizations in Asia and Africa. Trend Micro researchers recently discovered a new piece of targeted ransomware, tracked as Agenda, that was written in the Go programming language. The ransomware was employed in a targeted attack against one of […]
 Pierluigi Paganini
August 26, 2022
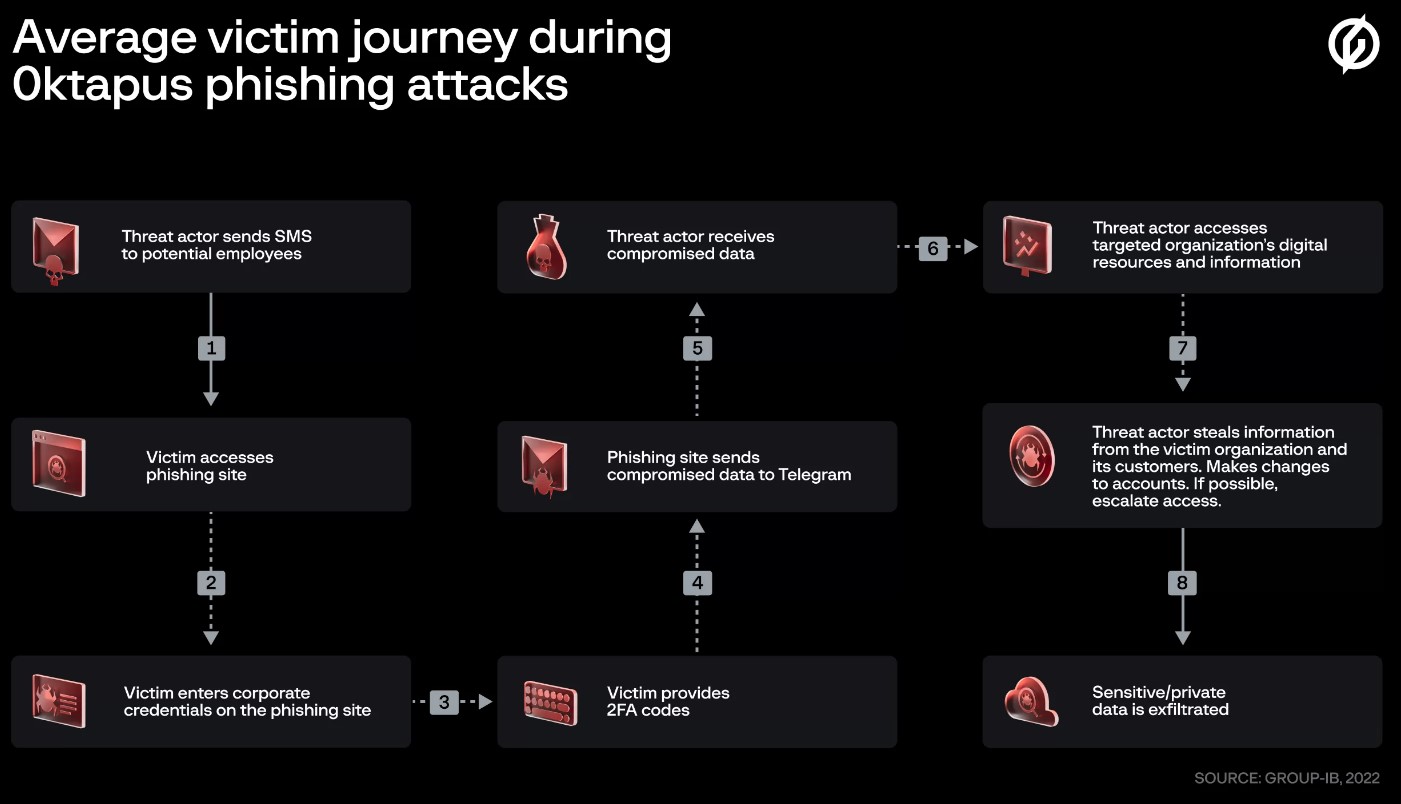
The threat actors behind Twilio and Cloudflare attacks have been linked to a phishing campaign that targeted other 136 organizations. The threat actors behind the attacks on Twilio and Cloudflare have been linked to a large-scale phishing campaign that targeted 136 organizations, security firm Group-IB reported. Most of the victims are organizations providing IT, software development, and cloud services. The campaign, codenamed 0ktapus, […]
 Pierluigi Paganini
August 25, 2022
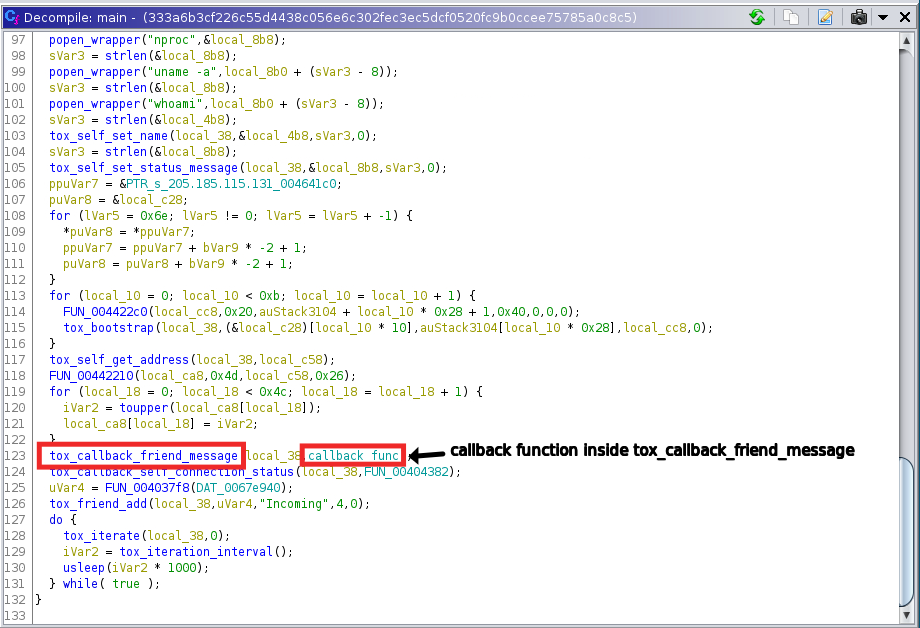
Threat actors are using the Tox peer-to-peer instant messaging service as a command-and-control server, Uptycs researchers reported. Tox is a peer-to-peer serverless instant messaging services that uses NaCl for encryption and decryption. Uptycs researchers reported that threat actors have started using the Tox peer-to-peer instant messaging service as a command-and-control server. Tox has been used in […]
 Pierluigi Paganini
August 24, 2022
The streaming media platform Plex is urging its users to reset passwords after threat actors gained access to its database. Plex is an American streaming media service and a client–server media player platform. The company disclosed a data breach after threat actors have access to a limited subset of data stored in a compromised database. Exposed data includes emails, usernames, and […]
 Pierluigi Paganini
August 24, 2022
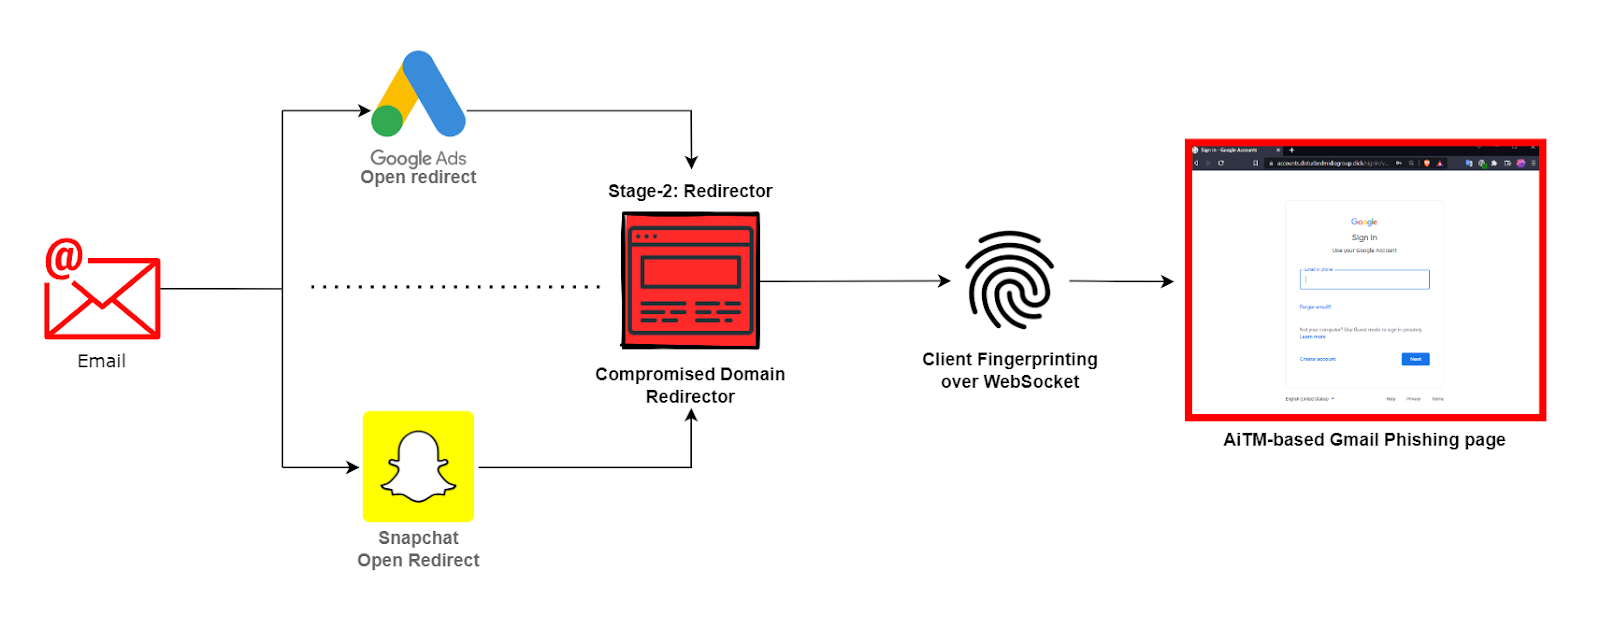
The threat actors behind a large-scale adversary-in-the-middle (AiTM) phishing campaign now target Google G Suite users The threat actors behind a large-scale adversary-in-the-middle (AiTM) phishing campaign targeting enterprise users of Microsoft email services were spotted targeting Google G Suite users. In AiTM phishing, threat actors set up a proxy server between a target user and the website the user […]
 Pierluigi Paganini
August 24, 2022
A French hospital, the Center Hospitalier Sud Francilien (CHSF), suffered a cyberattack on Sunday and was forced to refer patients to other structures. The Center Hospitalier Sud Francilien (CHSF), a hospital southeast of Paris, has suffered a ransomware attack over the weekend. The attack disrupted the emergency services and surgeries and forced the hospital to refer patients […]