 Pierluigi Paganini
 May 26, 2020
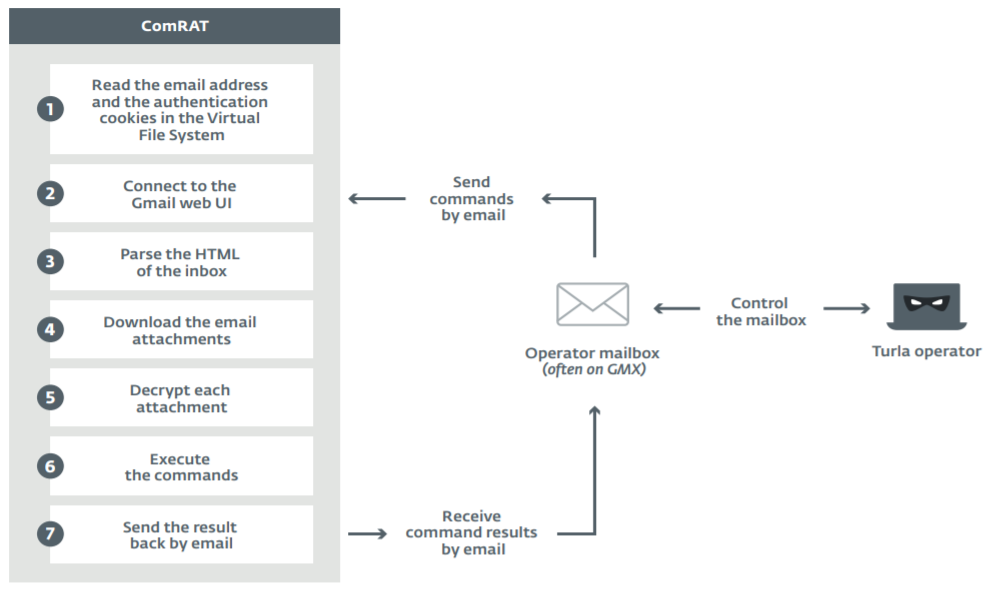
Researchers uncovered a new advanced variant of Turla’s ComRAT backdoor that leverages Gmail’s web interface as C2 infrastructure. Cybersecurity researchers discovered a new version of the ComRAT backdoor, also known as Agent.BTZ, which is a malware that was employed in past campaigns attributed to the Turla APT group. Earlier versions of Agent.BTZ were used to […]
 Pierluigi Paganini
May 09, 2020
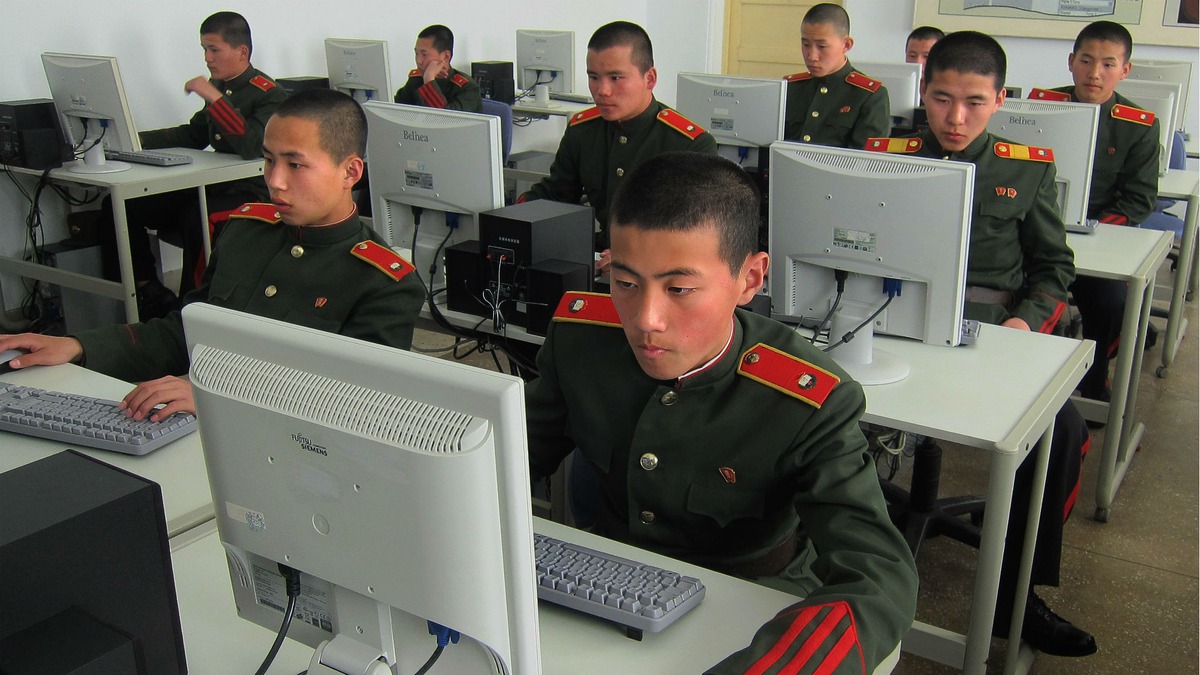
North Korea-linked Lazarus APT group employed a Mac variant of the Dacls Remote Access Trojan (RAT) in recent attacks. North Korea-linked Lazarus APT already used at least two macOS malware in previous attacks, now researchers from Malwarebytes have identified a new Mac variant of the Linux-based Dacls RAT. The activity of the Lazarus APT group (aka HIDDEN COBRA) […]
 Pierluigi Paganini
April 26, 2020
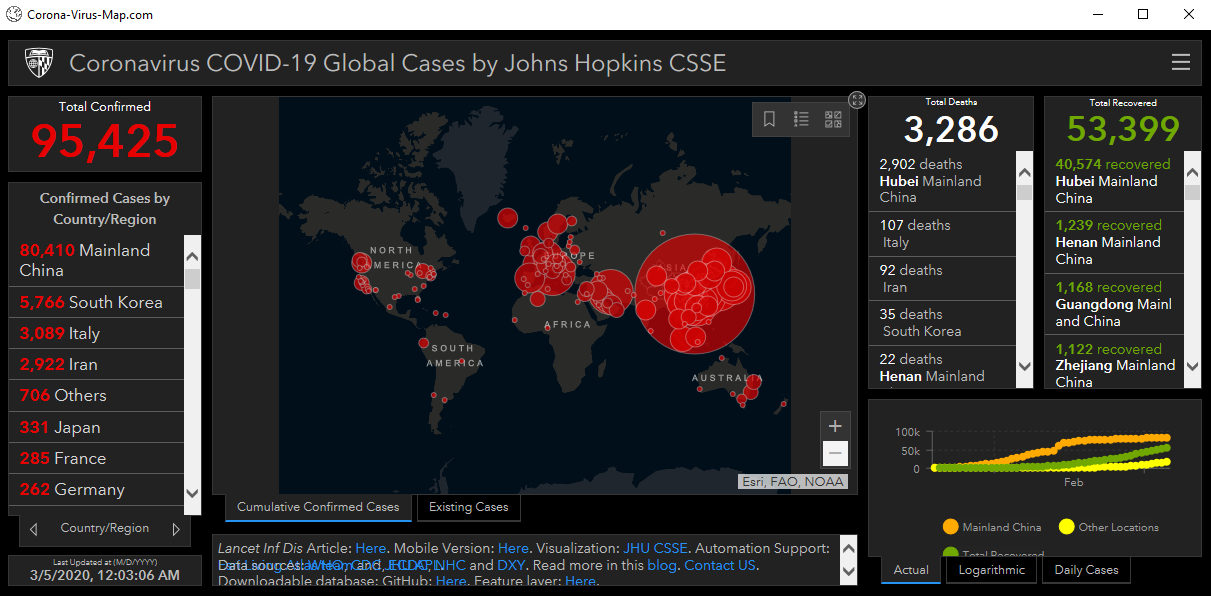
This post includes the details of the Coronavirus-themed attacks launched from April 19 to April 25, 2020. Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERShttps://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform Threat actors exploit the interest in the Coronavirus outbreak while infections increase worldwide, experts are observing new campaigns on a daily bases. Below […]
 Pierluigi Paganini
April 23, 2020
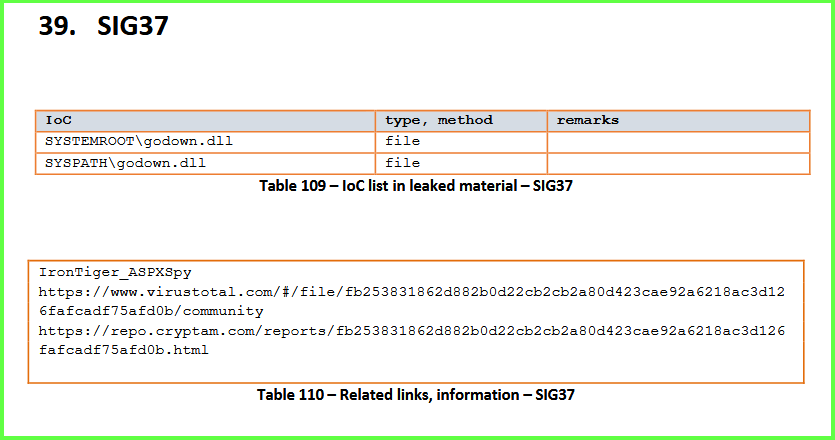
A security expert uncovered an old APT operation, tracked Nazar, by analyzing the NSA hacking tools included in the dump leaked by Shadow Brokers in 2017. Juan Andres Guerrero-Saade, a former Kaspersky and Google researcher, uncovered an old APT operation, tracked Nazar, by analyzing the NSA hacking tools included in the dump leaked by Shadow Brokers in […]
 Pierluigi Paganini
April 22, 2020
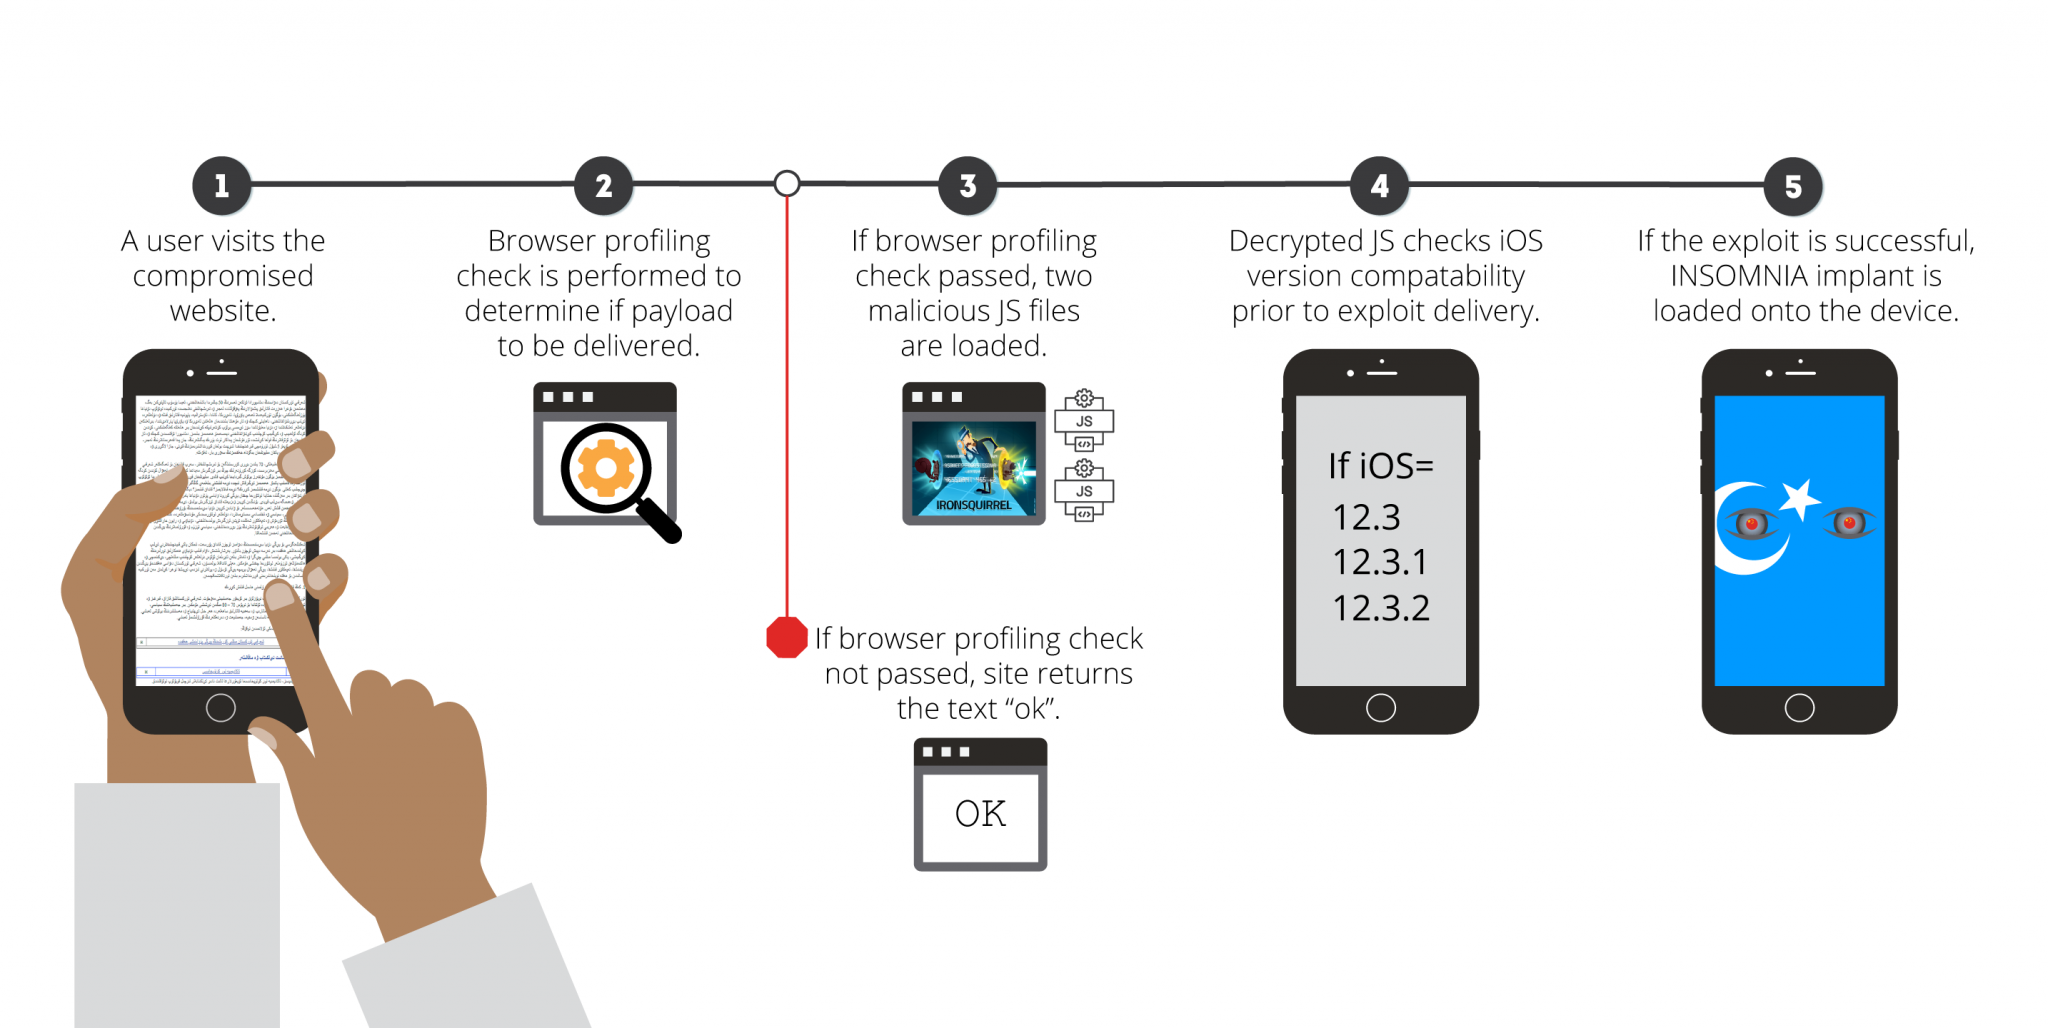
Security researchers from Volexity discovered a new Insomnia iOS exploit that was being used to spy on China’s Uyghur minority. The Uyghur group is a Turkic minority ethnic group originating from and culturally affiliated with the general region of Central and East Asia. “The Uyghurs are recognized by the Chinese government only as a regional […]
 Pierluigi Paganini
April 22, 2020
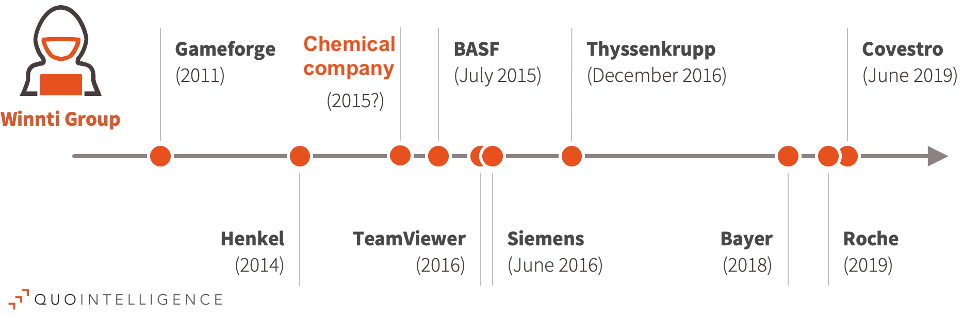
China-linked Winnti cyberespionage group targets South Korean video gaming company Gravity, QuoIntelligence (QuoINT) firm reported. Security experts from QuoIntelligence (QuoINT) firm reported that China-linked Winnti cyberespionage group targets South Korean video gaming company Gravity. The Winnti group was first spotted by Kaspersky in 2013, but according to the researchers the gang has been active since 2007. […]
 Pierluigi Paganini
April 15, 2020
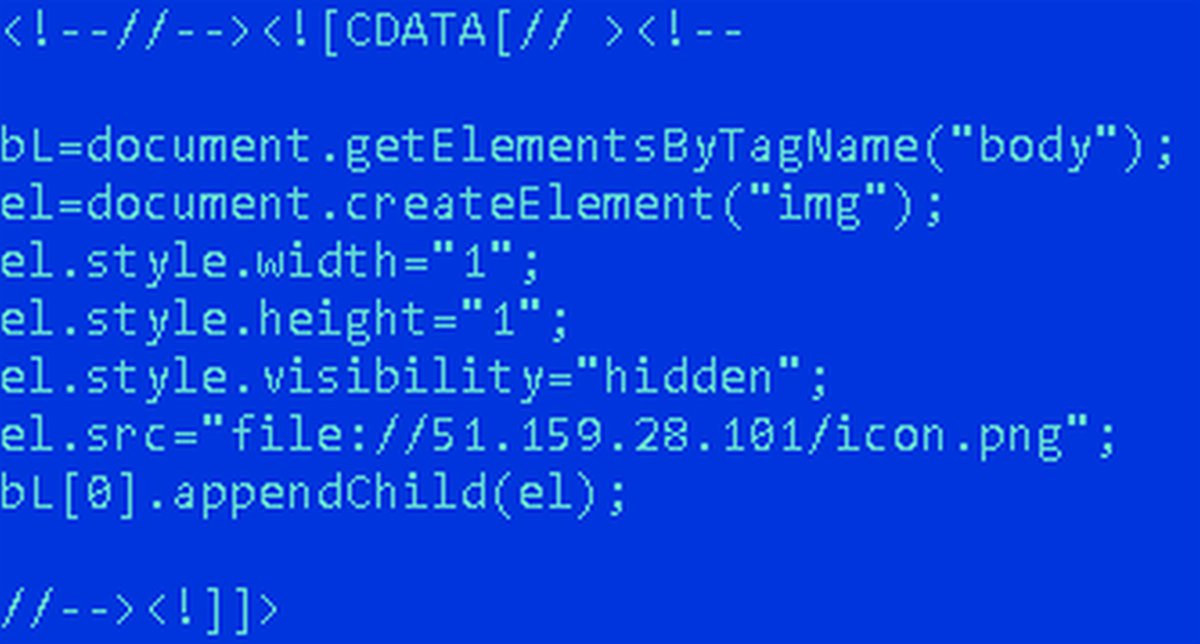
Security researchers from ESET revealed that the infamous Russian hacker group known as Energetic Bear is behind the hack of two San Francisco International Airport (SFO) websites. Researchers from ESET believe that the attacks against two San Francisco International Airport (SFO) websites were carried out by the Russian cyber-espionage group known as Energetic Bear (aka […]
 Pierluigi Paganini
April 06, 2020
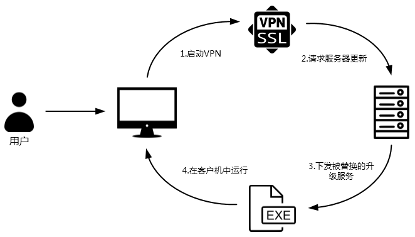
DarkHotel nation-state actor is exploiting a VPN zero-day to breach Chinese government agencies in Beijing and Shanghai Chinese security-firm Qihoo 360 has uncovered a hacking campaign conducted by a DarkHotel APT group (APT-C-06) aimed at Chinese government agencies in Beijing and Shanghai. State-sponsored hackers used a zero-day vulnerability in Sangfor SSL VPN servers to gain access […]
 Pierluigi Paganini
March 31, 2020
Holy Water – An APT group compromised a server hosting Web pages belonging mainly to religious figures and charities to carry out watering hole attacks. On December 4, 2019, Kaspersky experts discovered a watering hole attack, tracked Holy Water, aimed at an Asian religious and ethnic group. The campaign has been active since at least […]
 Pierluigi Paganini
March 31, 2020
For the third time in a few weeks, the FBI has issued an alert about supply chain attacks carried out by nation-state actors using the Kwampirs malware. The FBI has issued an alert about supply chain attacks using the Kwampirs malware as part of a hacking campaign carried out on a global scale by state-sponsored […]