 Pierluigi Paganini
 February 01, 2022
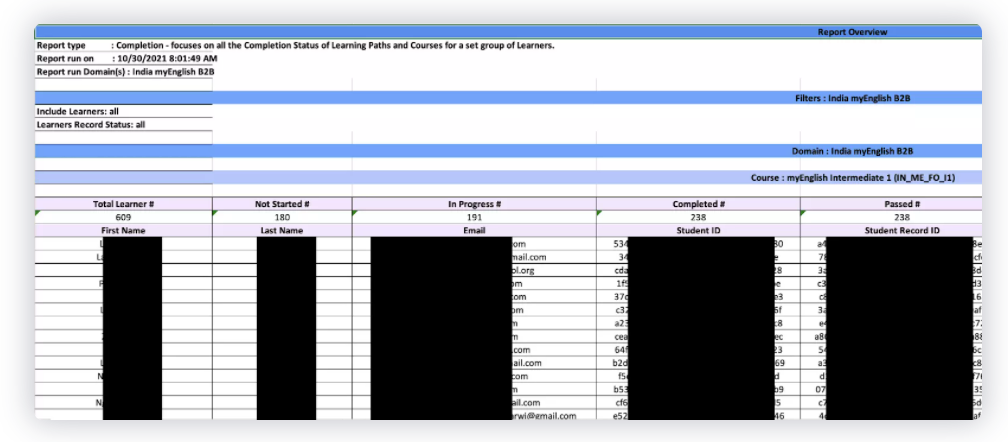
Personal information belonging to British Council students was exposed online via an unsecured repository. The British Council is a British organisation specialising in international cultural and educational opportunities. It operates in over 100 countries: promoting a wider knowledge of the United Kingdom and the English language; encouraging cultural, scientific, technological and educational co-operation with the […]
 Pierluigi Paganini
February 01, 2022
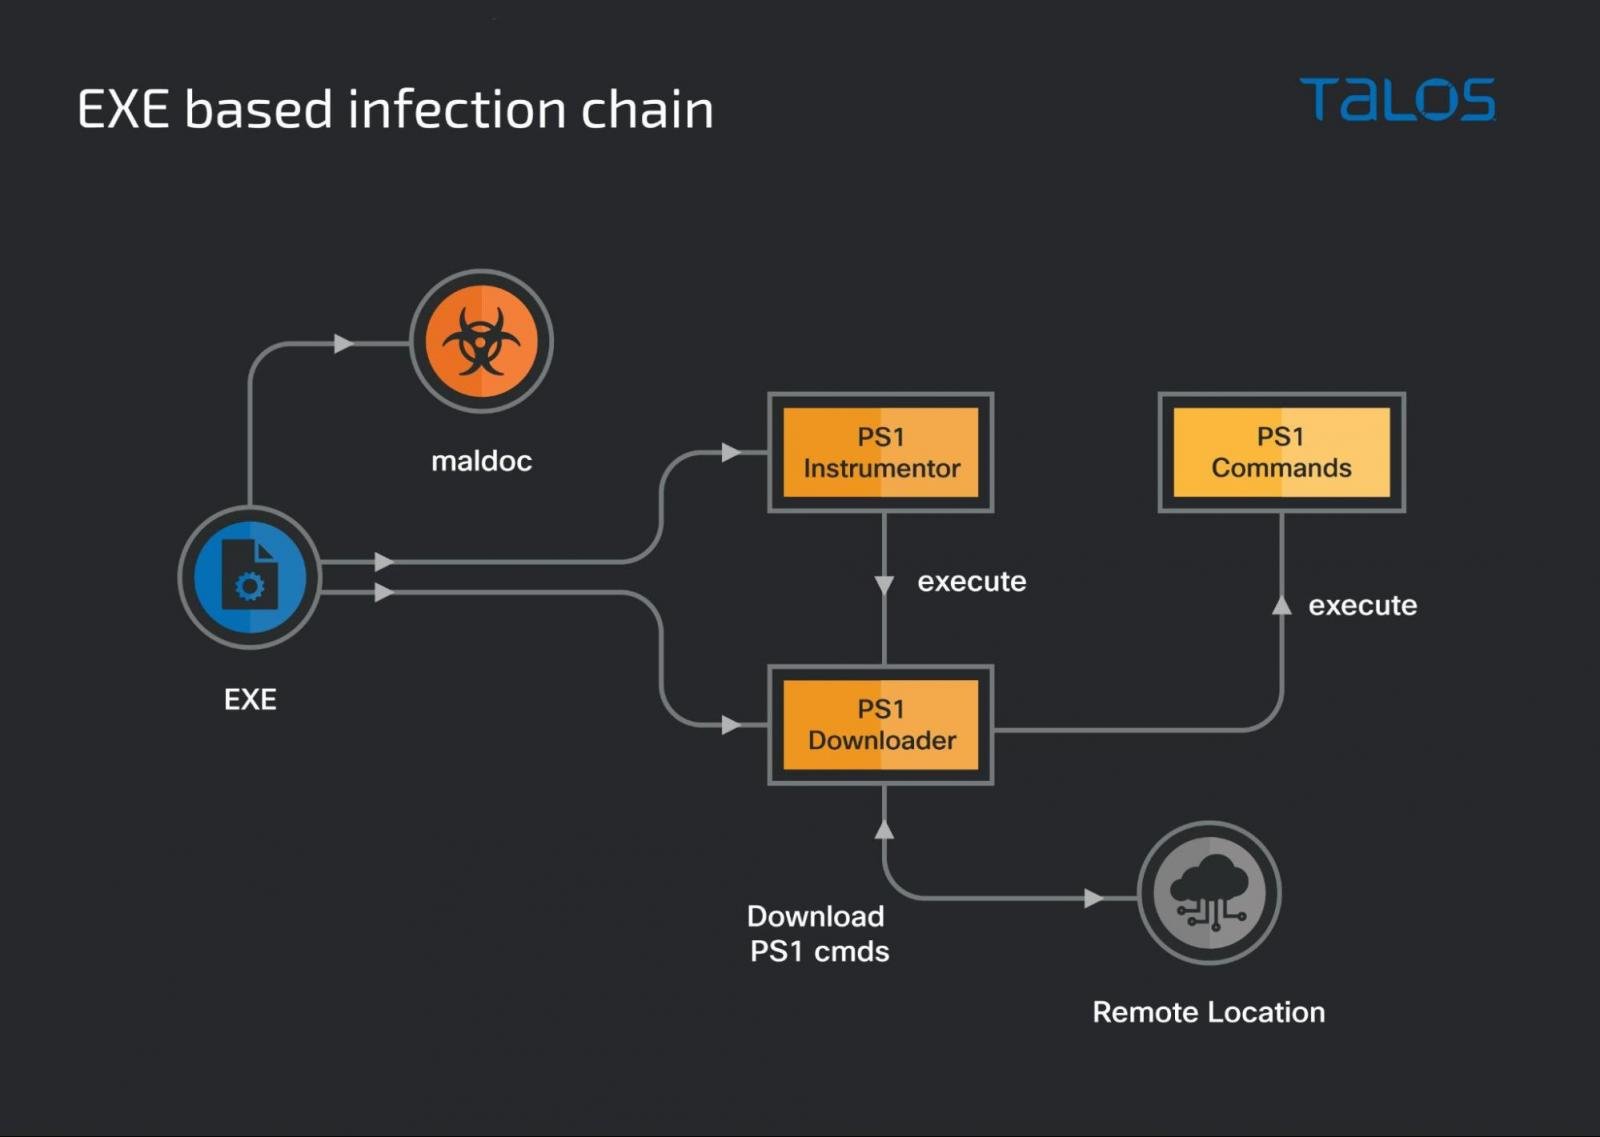
The Iran-linked MuddyWater APT group is targeting private Turkish organizations and governmental institutions. Researchers from Cisco Talos have uncovered a cyber espionage campaign carried out by the Iran-linked MuddyWater APT group (aka SeedWorm and TEMP.Zagros) and targeting private Turkish organizations and governmental institutions. The first MuddyWater campaign was observed in late 2017 when targeted entities in the Middle East. The experts called the […]
 Pierluigi Paganini
January 31, 2022
The US CISA added eight more flaws to its Known Exploited Vulnerabilities Catalog that are known to be used in attacks in the wild. The US Cybersecurity & Infrastructure Security Agency (CISA) has added eight more flaws to the Known Exploited Vulnerabilities Catalog. The ‘Known Exploited Vulnerabilities Catalog‘ is a list of known vulnerabilities that […]
 Pierluigi Paganini
January 31, 2022
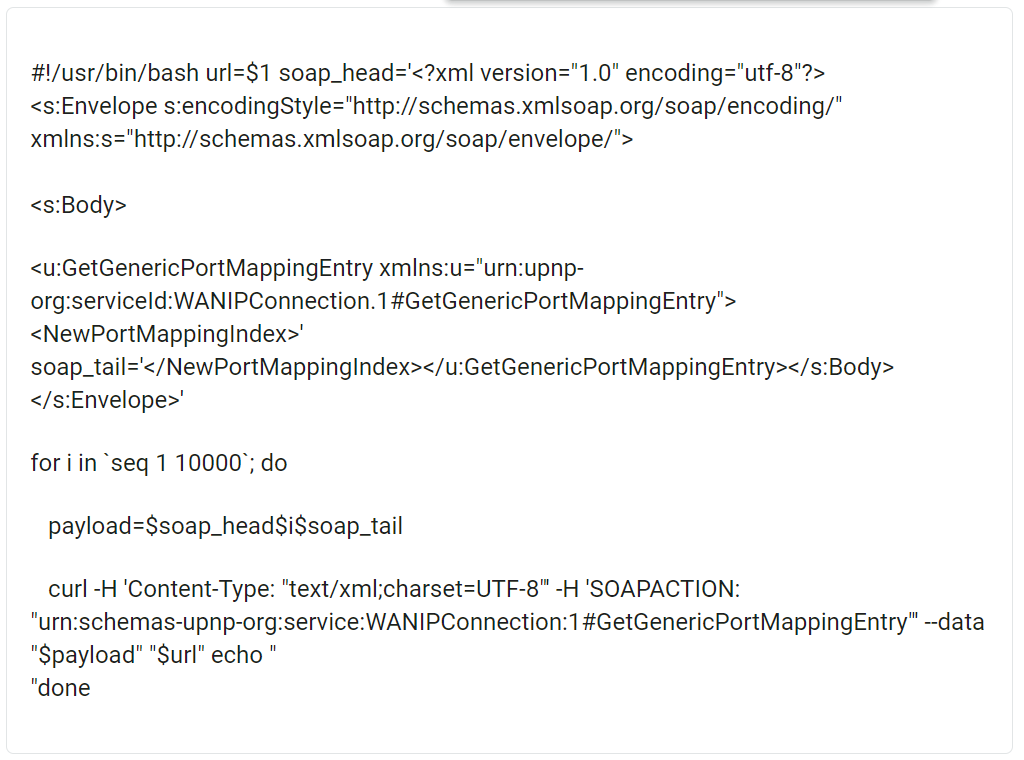
A hacking campaign, tracked as Eternal Silence, is abusing UPnP to compromise routers and use them to carry out malicious activities. Researchers from Akamai have spotted a malicious campaign, tracked as ‘Eternal Silence,’ that is abusing Universal Plug and Play (UPnP) to turn routers into a proxy server used to carry out a broad range […]
 Pierluigi Paganini
January 31, 2022
The administrator of the DeepDotWeb (DDW) has received a sentence of 97 months in prison for money laundering. Tal Prihar (37), an Israeli national who operated DeepDotWeb (DDW), was sentenced to 97 months in prison and was ordered to forfeit $8,414,173. DeepDotWeb (DDW) was a website that connected internet users with Darknet marketplaces, where they […]
 Pierluigi Paganini
January 31, 2022
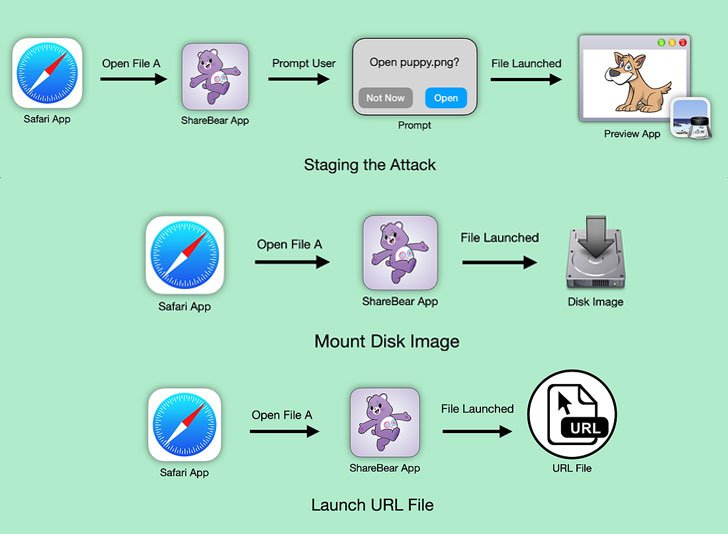
Apple paid +$100K bounty for a macOS series of flaws that can allow threat actors to take over the microphone and camera. Apple last year addressed multiple macOS vulnerabilities discovered by the security researcher Ryan Pickren in the Safari browser that could allow threat actors to access users’ online accounts, microphone, and webcam. Pickren received […]
 Pierluigi Paganini
January 31, 2022
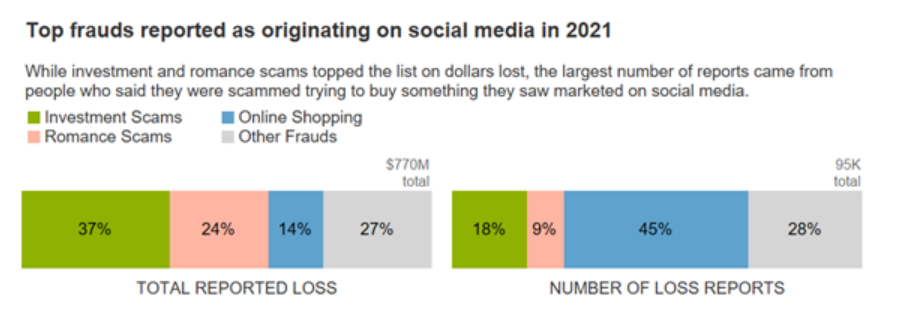
A report from the US Federal Trade Commission (FTC) revealed that in 2021 Americans lost $770 million from social media frauds The US Federal Trade Commission (FTC) revealed that in 2021 Americans lost $770 million from social media frauds. These data are the result of the increased exposure of netizens through social media. The US […]
 Pierluigi Paganini
January 30, 2022
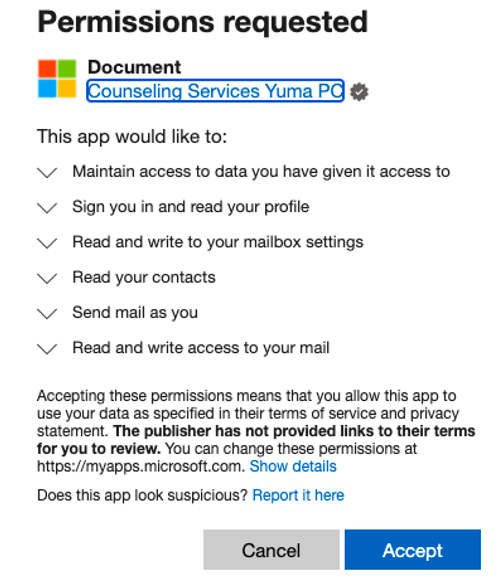
A new hacking campaign, tracked as ‘OiVaVoii’, is targeting company executives with malicious OAuth apps. Researchers from Proofpoint have uncovered a new campaign named ‘OiVaVoii’ that is targeting company executives, former board members, Presidents and managers with bogus OAuth apps and cleverly-crafted lures sent from compromised Office 365 accounts. Microsoft has blocked many of the […]
 Pierluigi Paganini
January 30, 2022
A researcher disclosed an exploit for a Windows local privilege elevation issue (CVE-2022-21882) that allows anyone to gain admin privileges in Windows 10. The security researchers RyeLv has publicly released an exploit for a Windows local privilege elevation flaw (CVE-2022-21882) that allows anyone to gain admin privileges in Windows 10. The Win32k elevation of privilege […]
 Pierluigi Paganini
January 30, 2022
A new round of the weekly Security Affairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. QNAP force-installs update against the recent wave of DeadBolt ransomware infections US FCC bans […]
Artificial Intelligence / September 29, 2026
Artificial Intelligence / September 28, 2026