



 Pierluigi Paganini
 August 14, 2026
Trump authorizes vetted US cybersecurity firms to conduct government-approved cyber operations against transnational criminal networks. President Trump signed a national security memorandum on August 13 establishing a formal program that allows vetted private US cybersecurity companies to conduct offensive cyber operations against transnational criminal organizations under government direction and oversight. The program, managed by the […]
 Pierluigi Paganini
August 13, 2026
Hackers began targeting a critical Adobe Commerce flaw that could let unauthenticated attackers hijack customer accounts and access private data. Hackers began targeting CVE-2026-71362 (CVSS score of 9.1), a critical Adobe Commerce flaw, shortly after its public disclosure. The vulnerability allows unauthenticated attackers to switch customer sessions, hijack accounts and access private data. Cybersecurity firm […]
 Pierluigi Paganini
August 13, 2026
Attackers are exploiting SharePoint flaw CVE-2026-55040 after a public PoC was released, allowing unauthenticated users to impersonate administrators. Attackers started exploiting CVE-2026-55040 (CVSS score of 9.1), a critical SharePoint authentication bypass patched in July, within days of Rapid7 releasing a public proof-of-concept on August 12. The vulnerability allows an unauthenticated attacker impersonate any SharePoint user […]
 Pierluigi Paganini
August 13, 2026
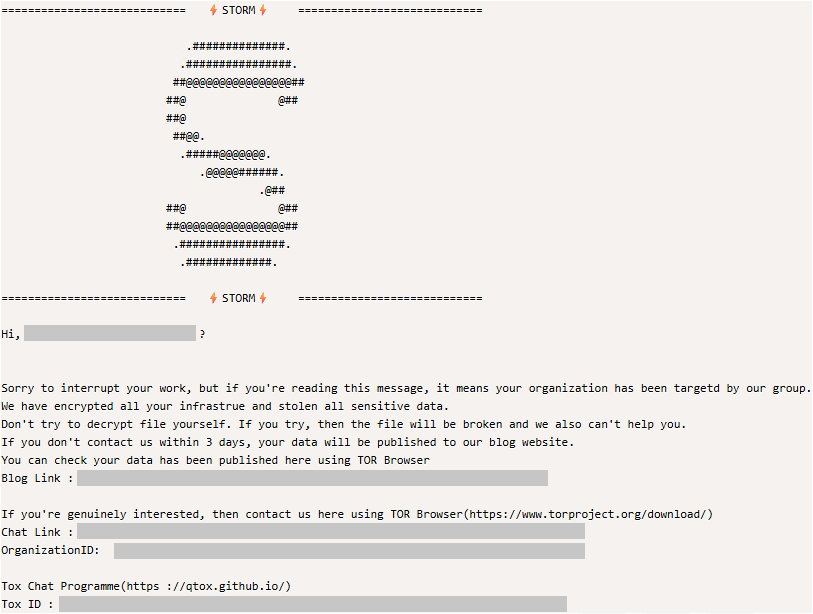
Microsoft says China-linked Storm-1175 is using a new ransomware called StormEncryptor, replacing Medusa in its latest attacks. Microsoft says China-linked, financially motivated threat actor Storm-1175 has begun using a new ransomware strain called StormEncryptor. The group previously relied on Medusa ransomware. StormEncryptor is written in C++ and encrypts files and adds the .encrypted extension, then […]
 Pierluigi Paganini
August 13, 2026
Lazarus targets defense professionals with fake Lockheed Martin jobs, exploiting a Windows zero-day to deploy backdoors and evade security controls. Check Point Research has uncovered a new wave of Operation Dream Job, the long-running North Korean campaign that lures defense and aerospace professionals with convincing fake job offers. This iteration is more dangerous than previous […]
 Pierluigi Paganini
August 12, 2026
CEVA Logistics suffered a cyberattack disrupting European operations, with eight warehouses affected and shipments halted at impacted sites. CEVA Logistics suffered a cyberattack on July 29 that disrupted parts of its European operations. The incident impacted impacted eight warehouses, and the company is still working to restore impacted services. CEVA Logistics operates in more than […]
 Pierluigi Paganini
August 12, 2026
China-linked hackers reportedly used eight AI agents to breach a government network, steal data and compromise accounts with minimal human oversight. Israeli cybersecurity firm Dream documented what looks like the first fully autonomous, end-to-end AI hacking operation against a government target. Over four days at the start of July, according to the Financial Times, suspected […]
 Pierluigi Paganini
August 12, 2026
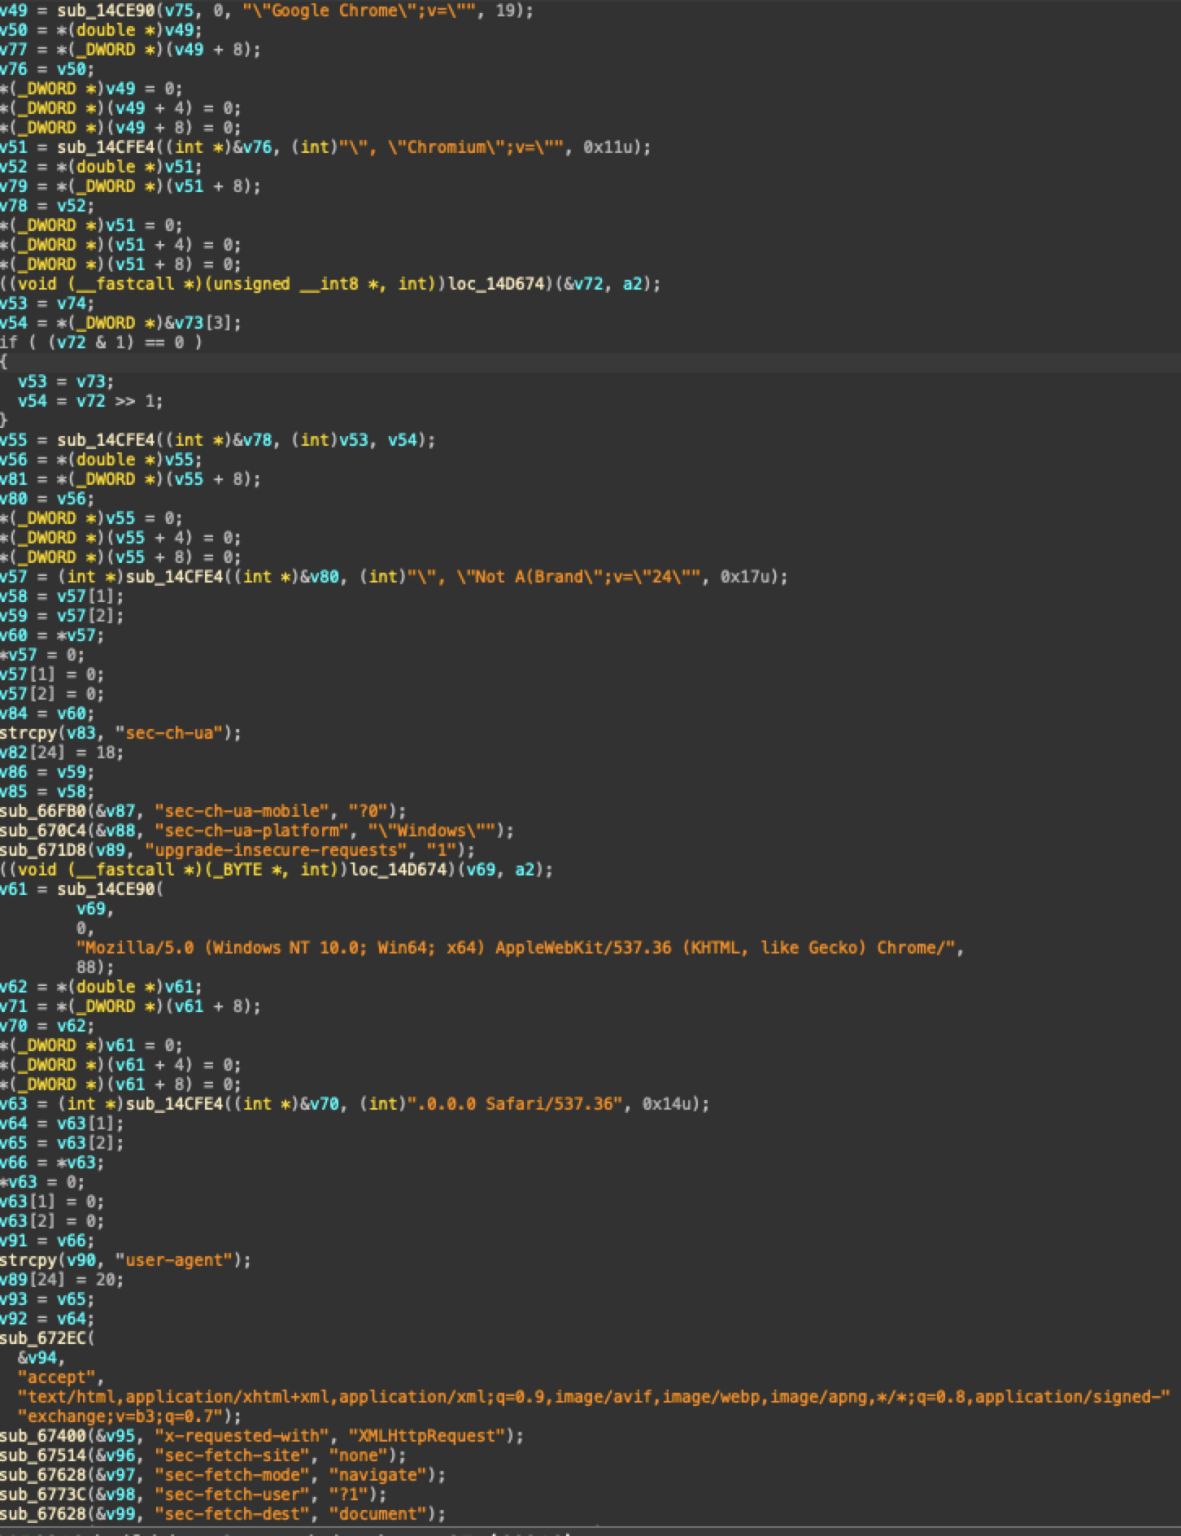
Kimwolf v7: The Android TV Botnet That Now Hides Its Traffic Behind Chrome Fingerprints and Ethereum Palo Alto Networks Unit 42 discovered Kimwolf v7 on February 3, 2026, while hunting threats following public disclosures of the botnet’s earlier activity. The new version substantially upgrades the DDoS capabilities and command infrastructure of a botnet that has […]
 Pierluigi Paganini
August 12, 2026
Chaotic Eclipse released a PoC for ShieldBreak, a Microsoft Defender zero-day that bypasses the CVE-2026-50656 patch and could enable SYSTEM-level code execution. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a PoC for ShieldBreak, a Microsoft Defender zero-day. The flaw bypasses the patch for CVE-2026-50656 (RoguePlanet), a race condition that […]
 Pierluigi Paganini
August 11, 2026
Zoom patches a zero-click flaw that could let a meeting participant execute code on another user’s computer through the annotation feature. Zoom has patched four vulnerabilities, including a critical zero-click flaw, tracked as CVE-2026-53413, in its annotation feature. CVE-2026-53413 is a memory corruption issue found by A Security that could allow a meeting participant to […]

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026





