 Pierluigi Paganini
 April 11, 2022
Easy Appointments contained a very dangerous Broken Access Control vulnerability tracked as CVE-2022-0482 that was exposing PII. Another day, another threat to your data. The recently discovered CVE-2022-0482 is a Broken Access Control vulnerability affecting Easy Appointments, a popular open-source web app written in PHP, used by thousands of sites to manage their online bookings. […]
 Pierluigi Paganini
April 09, 2022
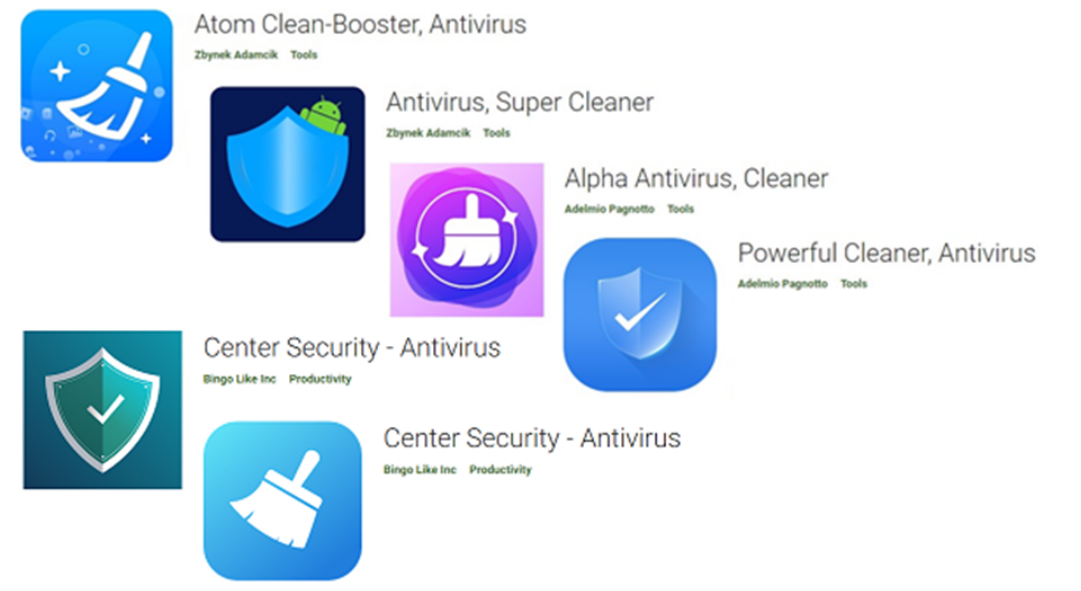
Experts discovered malicious Android apps on the Google Play Store masqueraded as antivirus solutions spreading the SharkBot Trojan. Researchers from the Check Point Research (CPR) team discovered several malicious Android apps on the official Google Play Store masqueraded as antivirus solutions that were used to deliver the SharkBot banking Trojan. Sharkbot is an information stealer steals used […]
 Pierluigi Paganini
April 08, 2022
Which are the most important cybersecurity measures that businesses can take to protect themselves in the cloud era? We are now firmly in the era of cloud data and storage. In fact, it’s become quite difficult to find a service that doesn’t rely on the cloud in some way. This ubiquity has led to increased […]
 Pierluigi Paganini
April 07, 2022
VMware fixed critical vulnerabilities in multiple products that could be exploited by remote attackers to execute arbitrary code. VMware has addressed critical remote code vulnerabilities in multiple products, including VMware’s Workspace ONE Access, VMware Identity Manager (vIDM), vRealize Lifecycle Manager, vRealize Automation, and VMware Cloud Foundation products. The virtualization giant urges its customers to address […]
 Pierluigi Paganini
April 06, 2022
Nordex Group, one of the largest manufacturers of wind turbines, was hit by a cyberattack that forced the company to shut down part of its infrastructure. Nordex Group, one of the world’s largest manufacturers of wind turbines, was the victim of a cyberattack that forced the company to take down multiple systems. The attack was […]
 Pierluigi Paganini
April 05, 2022
The U.S. CISA added the recently disclosed remote code execution (RCE) vulnerability Spring4Shell to its Known Exploited Vulnerabilities Catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the recently disclosed CVE-2022-22965 (aka Spring4Shell, CVSS score: 9.8) flaw in the Spring Framework, along with three other issues, to its Known Exploited Vulnerabilities Catalog. According to Binding Operational Directive (BOD) […]
Pierluigi Paganini
April 04, 2022
VMware released security updates to address the critical remote code execution vulnerability known as Spring4Shell. VMware has published security updates to address the critical remote code execution vulnerability known as Spring4Shell (CVE-2022-22965). According to the virtualization giant, the flaw impacts many of its cloud computing and virtualization products. The Spring4Shell issue was disclosed last week, […]
 Pierluigi Paganini
April 04, 2022
Boffins devised a new attack technique, dubbed Brokenwire, against the Combined Charging System (CCS) that could potentially disrupt charging for electric vehicles. A group of researchers from the University of Oxford and Armasuisse S+T has devised a new attack technique, dubbed Brokenwire, against the popular Combined Charging System (CCS) that could be exploited by remote […]
Pierluigi Paganini
April 04, 2022
SonarSource discovered a 15-year-old flaw in the PEAR PHP repository that could have enabled supply chain attacks. Researchers from SonarSource discovered two 15-year-old security flaws in the PEAR (PHP Extension and Application Repository) repository that could have enabled supply chain attacks. PEAR is a framework and distribution system for reusable PHP components. According to the expert, […]
 Pierluigi Paganini
April 02, 2022
GitLab has addressed a critical vulnerability, tracked as CVE-2022-1162 (CVSS score of 9.1), that could allow remote attackers to take over user accounts. The CVE-2022-1162 vulnerability is related to the set of hardcoded static passwords during OmniAuth-based registration in GitLab CE/EE. “A hardcoded password was set for accounts registered using an OmniAuth provider (e.g. OAuth, LDAP, […]