 Pierluigi Paganini
 December 29, 2025
Korean Air employee discloses a data breach after a hack of its catering and duty-free supplier, KC&D, affecting thousands of staff. Korean Air suffered a data breach after its in-flight catering supplier Korean Air Catering & Duty-Free (KC&D) was hacked, exposing personal data of ~30,000 employees of Korean Air employees. Korean Air is South Korea’s […]
 Pierluigi Paganini
December 29, 2025
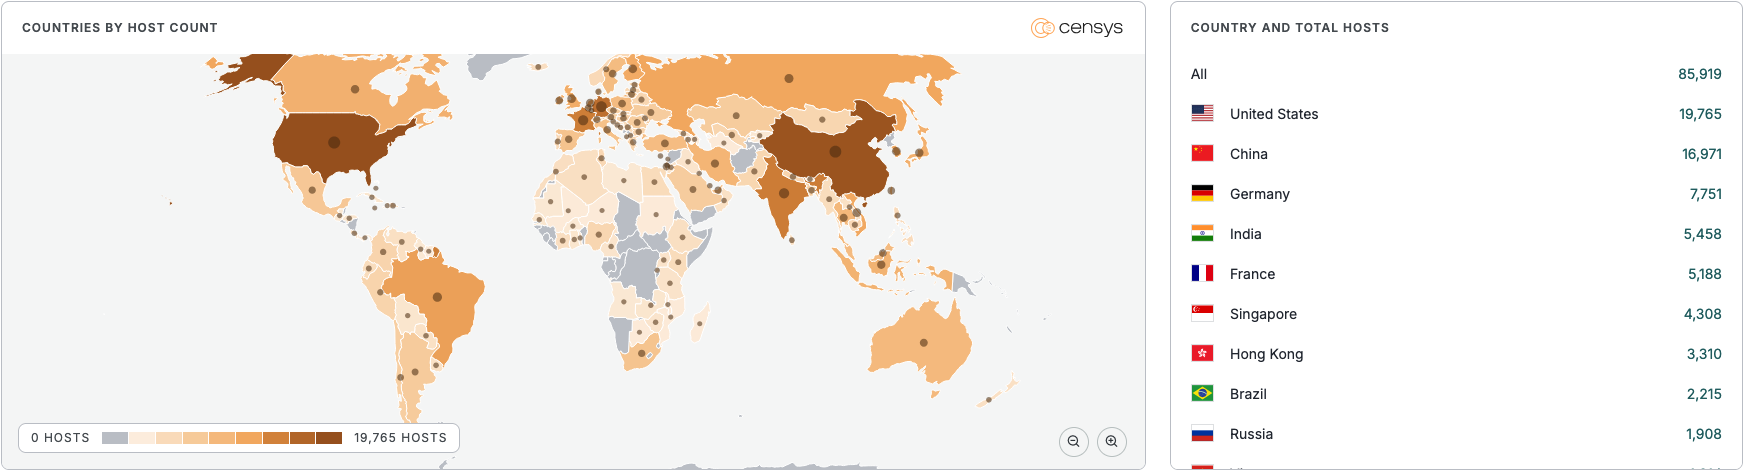
A recently disclosed MongoDB flaw (MongoBleed) is under active exploitation, with over 87,000 potentially vulnerable instances exposed worldwide. A newly disclosed MongoDB vulnerability, tracked as CVE-2025-14847 (aka MongoBleed, CVSS score of 8.7), is being actively exploited, with more than 87,000 potentially vulnerable instances identified worldwide. Cybersecurity researcher Joe Desimone published a proof-of-concept exploit for this vulnerability […]
 Pierluigi Paganini
December 29, 2025
China-linked APT Evasive Panda used DNS poisoning to deliver the MgBot backdoor in targeted cyber-espionage attacks in Türkiye, China, and India. Kaspersky researchers spotted the China-linked APT group Evasive Panda (aka Daggerfly, Bronze Highland, and StormBamboo) running a targeted cyber-espionage campaign using DNS poisoning to deliver the MgBot backdoor against victims in Türkiye, China, and […]
 Pierluigi Paganini
December 28, 2025
Stolen vault backups from the 2022 LastPass breach are still being cracked, allowing attackers to steal crypto as late as 2025. The blockchain intelligence firm TRM Labs warns that encrypted vault backups stolen in the 2022 LastPass breach are still being cracked using weak master passwords, enabling crypto theft as late as 2025. In 2022, […]
 Pierluigi Paganini
December 28, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Choose Your Fighter: A New Stage in the Evolution of Android SMS Stealers in Uzbekistan From Linear to Complex: An Upgrade in RansomHouse Encryption Prince of Persia: A Decade of Iranian Nation-State APT Campaign […]
 Pierluigi Paganini
December 27, 2025
A critical flaw in LangChain Core could allow attackers to steal sensitive secrets and manipulate LLM responses via prompt injection. LangChain Core (langchain-core) is a key Python package in the LangChain ecosystem that provides core interfaces and model-agnostic tools for building LLM-based applications. A critical vulnerability, tracked as CVE-2025-68664 (CVSS score of 9.3), affects the […]
 Pierluigi Paganini
December 26, 2025
Pro-Russian hacking group Noname057 claimed responsibility for the cyberattack that recently disrupted La Poste’s digital banking and online services. This week, the French national postal service La Poste confirmed a major cyber incident had knocked its information systems offline, disrupting digital banking and online services for millions of customers. On social media, La Poste said […]
 Pierluigi Paganini
December 25, 2025
Fortinet reported active exploitation of a five-year-old FortiOS SSL VPN flaw, abused in the wild under specific configurations. Fortinet researchers observed “recent abuse” of a five-year-old security vulnerability, tracked as CVE-2020-12812 (CVSS score: 5.2), in FortiOS SSL VPN. The vulnerability is exploited in attacks in the wild under certain configurations. CVE-2020-12812 is an improper authentication flaw […]
 Pierluigi Paganini
December 25, 2025
MongoDB addressed a high-severity vulnerability that can be exploited to achieve remote code execution on vulnerable servers. MongoDB addressed a high-severity vulnerability, tracked as CVE-2025-14847 (CVSS score 8.7), an unauthenticated, remote attacker can exploit the issue to execute arbitrary code on vulnerable servers. “An client-side exploit of the Server’s zlib implementation can return uninitialized heap […]
 Pierluigi Paganini
December 24, 2025
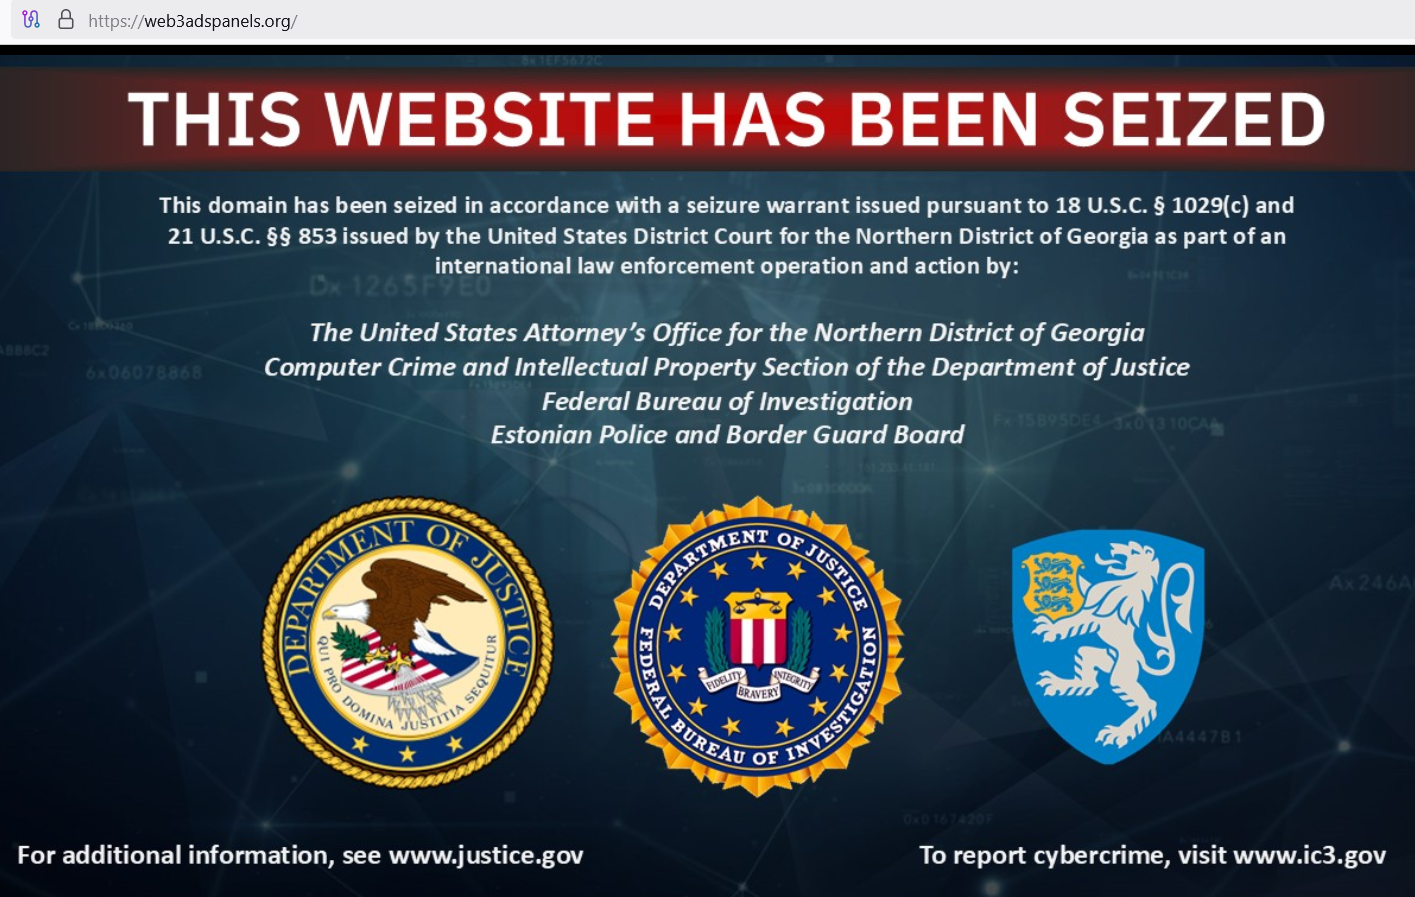
The U.S. seized the ‘web3adspanels.org’ domain and database used by cybercriminals to store stolen bank login credentials. The FBI seized the domain web3adspanels[.]org and its database after cybercriminals used it to store bank login credentials stolen from U.S. victims. A criminal group ran fake ads on Google and Bing that mimicked real bank advertisements. Victims […]
Breaking News / November 10, 2026