


 Pierluigi Paganini
 July 18, 2026
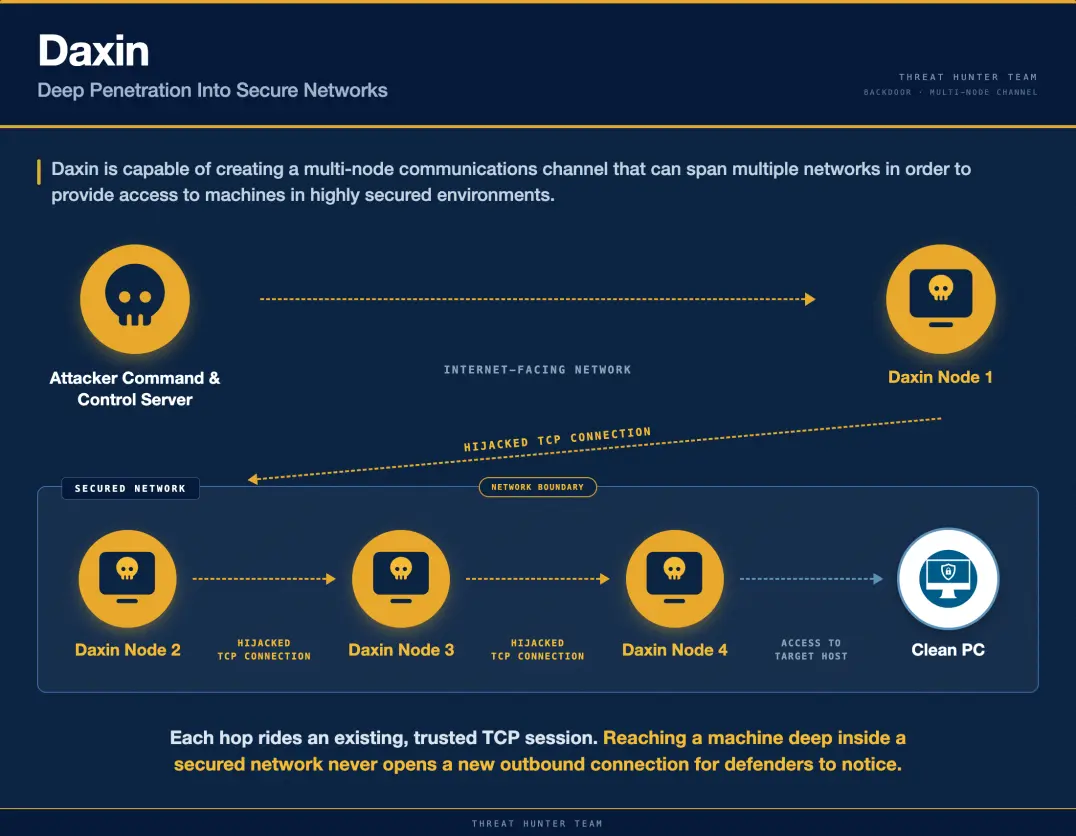
Researchers found China’s Daxin rootkit and a new Stupig backdoor on a Taiwan firm’s network, suggesting a stealthy intrusion dating back to 2013. Symantec’s Threat Hunter Team found Daxin running on a compromised host at a Taiwan-based subsidiary of a multinational high-tech manufacturer in 2026. Daxin is a Windows kernel-mode rootkit that Symantec first documented […]
 Pierluigi Paganini
July 18, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet FortiSandbox and Microsoft SharePoint flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Fortinet FortiSandbox and Microsoft SharePoint flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the KeV catalog: This week, Microsoft’s July 2026 […]
 Pierluigi Paganini
July 17, 2026
Ernst & Young (EY) disclosed a data breach after attackers compromised a third-party IT support system containing client documents and tax information. Ernst & Young (EY) is disclosed a data breach linked to a compromised third-party support ticket system used by its IT teams. The platform stored support requests that may have included documents containing […]
 Pierluigi Paganini
July 17, 2026
A cyberattack hit one of Japan’s largest food companies, Nichirei, disrupting logistics and shipments. The company is gradually restoring operations. Nichirei is one of Japan’s largest food companies, best known for its frozen food business. Founded in 1942 and headquartered in Tokyo, it operates globally through dozens of subsidiaries. The food giant confirmed that the […]
 Pierluigi Paganini
July 17, 2026
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
July 16, 2026
Two members of the Scattered Spider cybercrime group received jail sentences in the UK for the 2024 cyberattack on Transport for London. A UK court sentenced two Scattered Spider members, Thalha Jubair (20) and Owen Flowers (18), for their role in the 2024 cyberattack on Transport for London (TfL). Transport for London (TfL) is a local […]
 Pierluigi Paganini
July 16, 2026
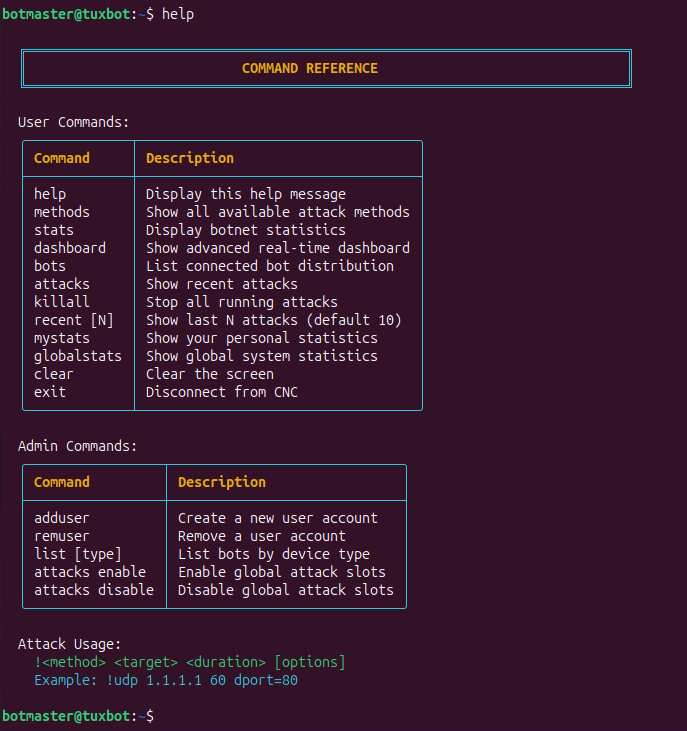
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 16, 2026
Zoom warns of a critical Windows flaw, tracked as CVE-2026-53412, that could let attackers take over accounts without authentication. Zoom has fixed a critical Windows vulnerability, tracked as CVE-2026-53412 (CVSS score of 9.8) that could allow unauthenticated attackers to hijack user accounts. The flaw affects older versions of Workplace, the Windows VDI Client, and the […]
 Pierluigi Paganini
July 15, 2026
US and allies warn of Russian APT groups targeting routers and network devices to compromise critical infrastructure worldwide. The US and allied governments warn that Russian state-sponsored APT groups are scanning and exploiting poorly secured network devices, especially routers, to access critical infrastructure. Groups linked to FSB Center 16, including Berserk Bear, Energetic Bear, Ghost […]
 Pierluigi Paganini
July 15, 2026
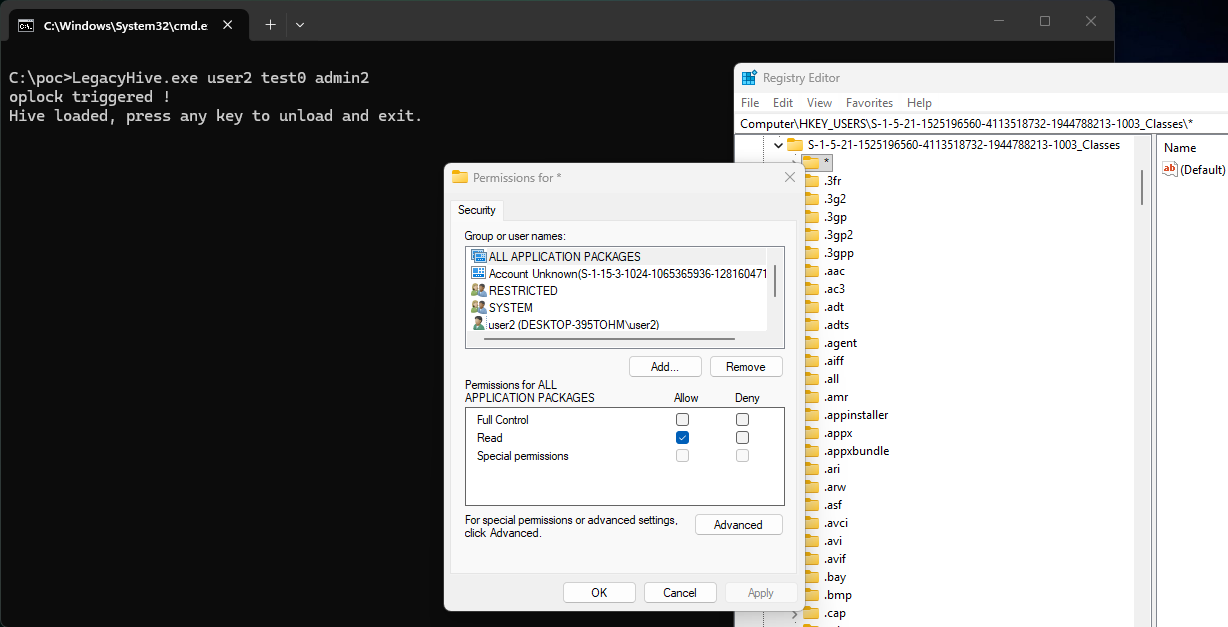
LegacyHive PoC exposes a Windows Privilege Escalation flaw affecting fully patched Windows desktop and server systems. Just hours after Microsoft’s July 2026 Patch Tuesday, security researcher Nightmare Eclipse, also known as Chaotic Eclipse, published a new Windows zero-day proof-of-concept called LegacyHive. This time, the target is the Windows User Profile Service (ProfSvc), and unlike the […]


Artificial Intelligence / September 14, 2026

