 Pierluigi Paganini
 May 24, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. CVE-2026-9082: Drupal’s Highly Critical SQL Injection Flaw Is Already Under Active Attack Why pure extortion is […]
 Pierluigi Paganini
May 23, 2026
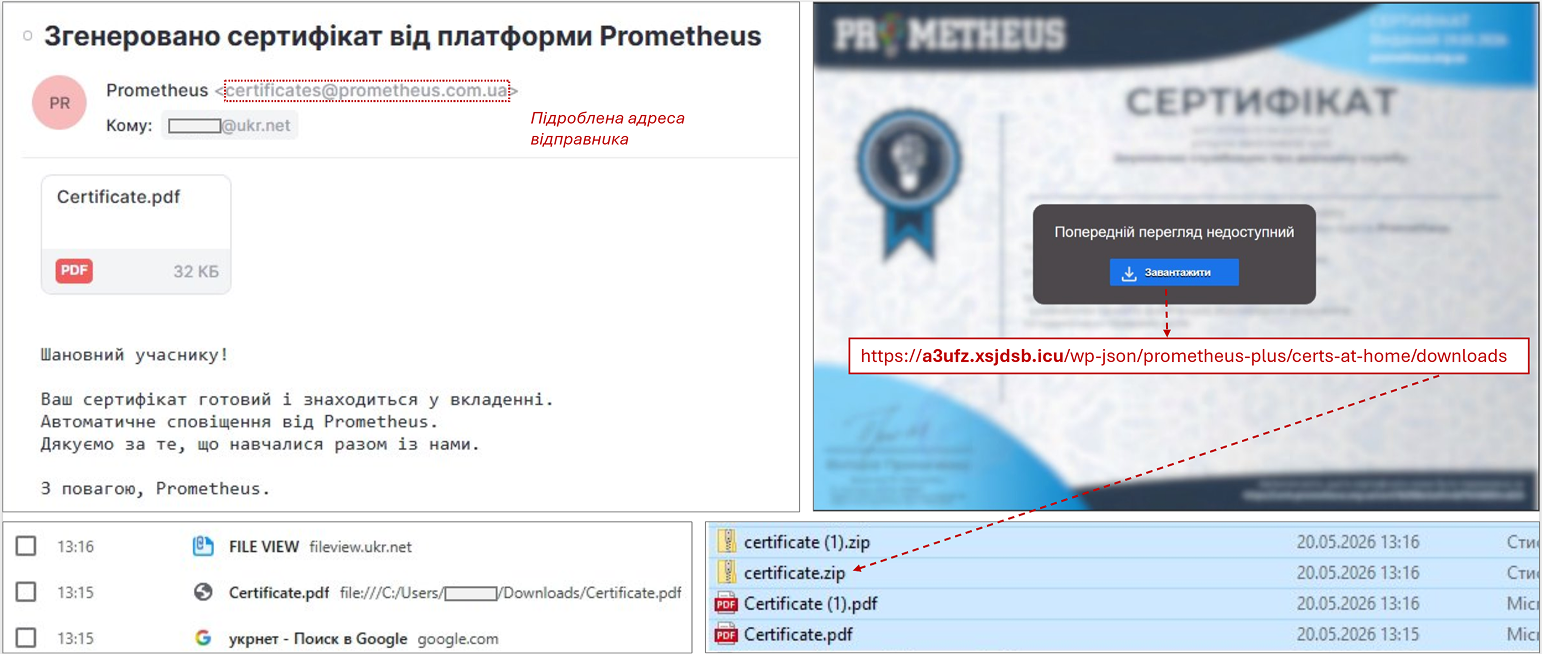
Ghostwriter targeted Ukrainian government agencies with phishing emails delivering malware and Cobalt Strike payloads. The Belarus-nexus APT group Ghostwriter (also tracked as UAC-0057 and UNC1151) has resurfaced with a new phishing campaign targeting Ukrainian government organizations. This time the lure is Prometheus, a legitimate Ukrainian online learning platform that many government employees actually use. Using […]
 Pierluigi Paganini
May 22, 2026
Canadian authorities arrested a 23-year-old Ottawa man accused of running the Kimwolf DDoS botnet. The US is now seeking extradition. US authorities have charged 23-year-old Jacob Butler (aka “Dort”), an Ottawa resident, for allegedly operating the recently disrupted Kimwolf botnet. Authorities arrested the suspect in Canada, he could face up to 10 years in prison […]
 Pierluigi Paganini
May 22, 2026
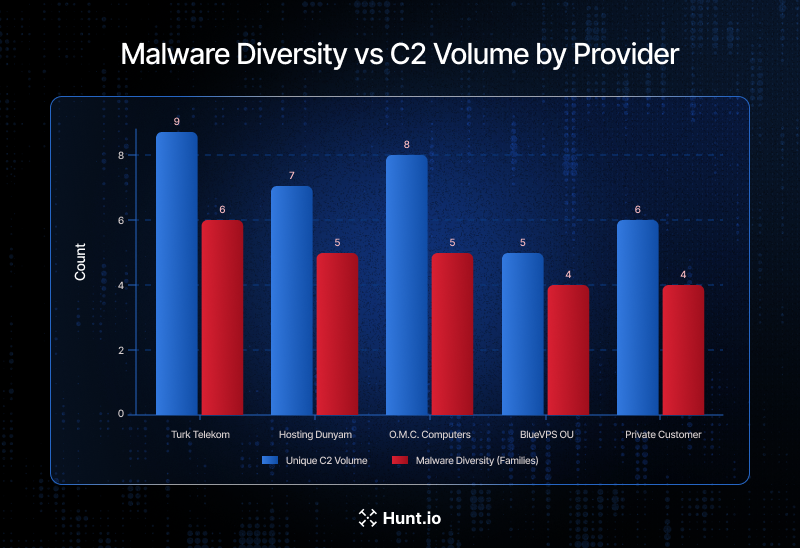
Hunt.io mapped 1,350+ C2 servers across the Middle East, revealing how a small group of providers quietly supports major malware activity. For years, threat intelligence focused mostly on malware families, phishing domains, and individual indicators. But a new report from Hunt.io shows why defenders may need to pay closer attention to something more boring, hosting […]
 Pierluigi Paganini
May 20, 2026
One employee installed a trojanized VS Code extension. Result: ~3,800 GitHub internal repositories exfiltrated. TeamPCP claims credit, wants $50K. There is something almost ironic about GitHub, the platform that hosts the code for most of the world’s software, getting breached through a trojanized plugin for a code editor. But that is exactly what happened, and […]
 Pierluigi Paganini
May 19, 2026
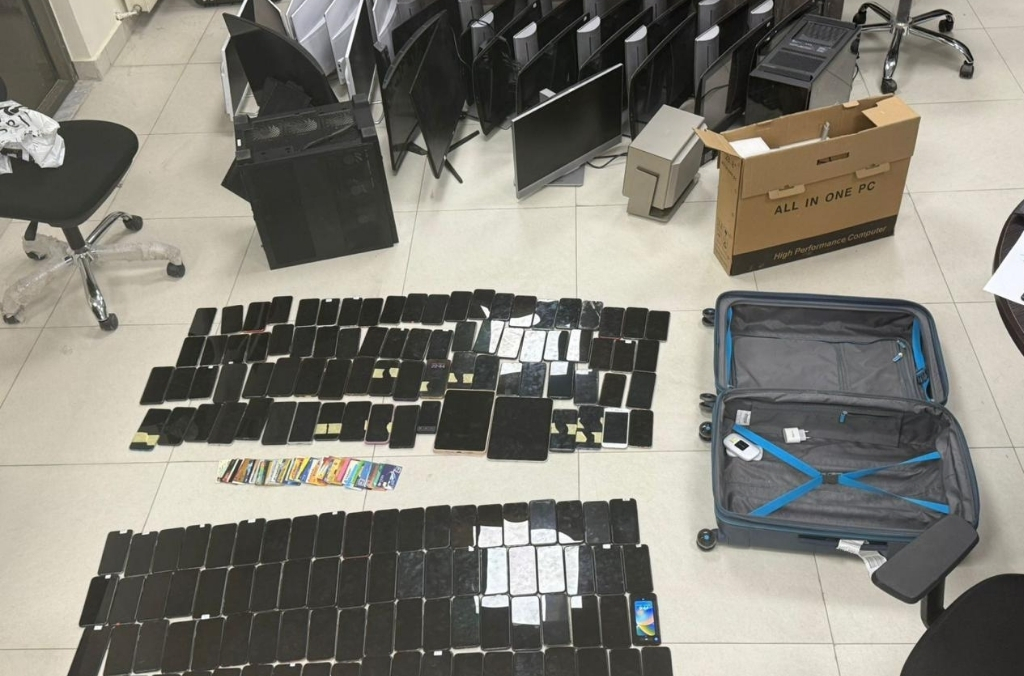
INTERPOL led Operation Ramz in MENA, resulting in 201 arrests and 382 suspects tied to cybercrime networks. INTERPOL coordinated Operation Ramz across the Middle East and North Africa, leading to 201 arrests and identifying 382 additional suspects. ” A first-of-its-kind cybercrime operation in the MENA region has led to the arrest of 201 individuals, with a […]
 Pierluigi Paganini
May 19, 2026
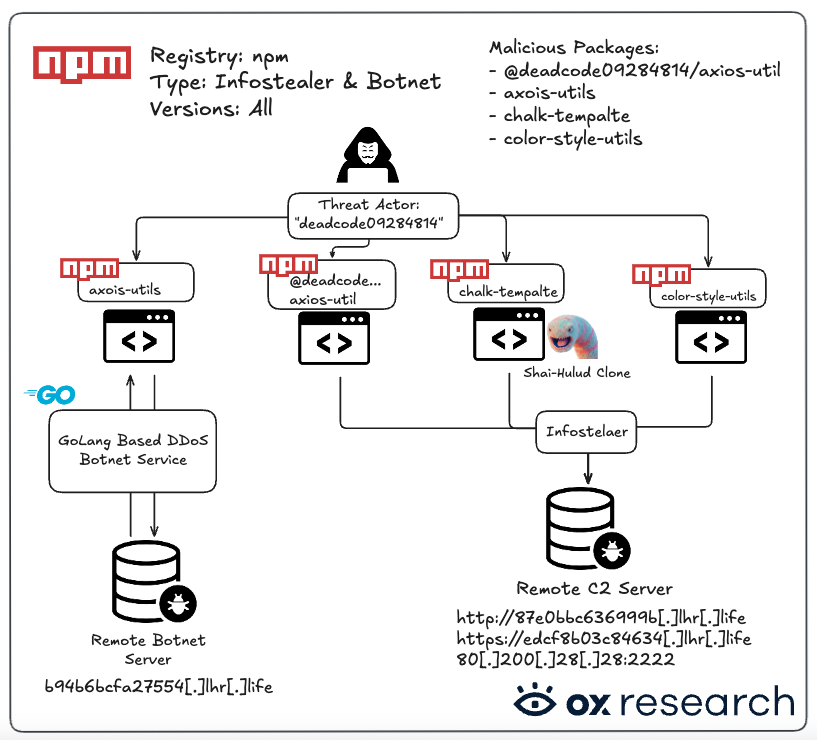
Shai-Hulud worm copycats are already attacking NPM developers after its source code leaked, enabling fast supply chain exploitation. The first copycats of the Shai-Hulud worm have already started showing up online, only a few days after the malware’s source code was dumped on GitHub. Researchers had warned this would happen almost immediately, and they were […]
 Pierluigi Paganini
May 18, 2026
Grafana confirmed a GitHub token breach that exposed source code, but said no customer data or systems were affected. Grafana Labs confirmed a security incident after the extortion group Coinbase Cartel listed it on a leak site and claimed data theft on May 15. The breach was triggered by a compromised token that gave attackers […]
 Pierluigi Paganini
May 18, 2026
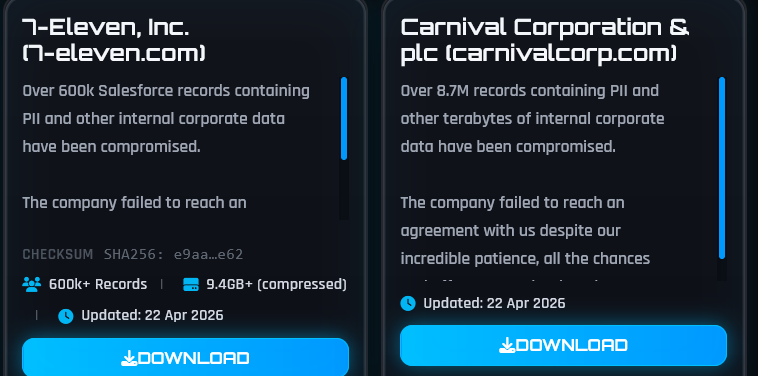
7-Eleven confirmed a breach after ShinyHunters claimed theft of over 600,000 Salesforce records and franchisee data. 7-Eleven has confirmed a data breach after the ShinyHunters hacking group claimed it stole more than 600,000 Salesforce records containing personal and corporate information. “Over 600k Salesforce records containing PII and other internal corporate data have been compromised.” The […]
 Pierluigi Paganini
May 17, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter JDownloader site hacked to replace installers with Python RAT malware New TrickMo Variant: Device Take Over malware targeting Banking, Fintech, Wallet & Auth apps Threat Actor Mr_Rot13 Actively Exploits CVE-2026-41940 for Backdoor Deployment Operation […]