 Pierluigi Paganini
 May 17, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Attackers exploit Funnel Builder bug to inject e-skimmers into e-stores Pwn2Own Berlin 2026, Day Three: DEVCORE […]
 Pierluigi Paganini
May 17, 2026
Attackers are exploiting a critical flaw in the WordPress Funnel Builder plugin to inject skimming code into WooCommerce checkout pages. A critical vulnerability in the WordPress Funnel Builder plugin is being actively exploited to inject malicious JavaScript into WooCommerce checkout pages, according to Sansec researchers. Funnel Builder by FunnelKit is a checkout and upsell plugin […]
 Pierluigi Paganini
May 16, 2026
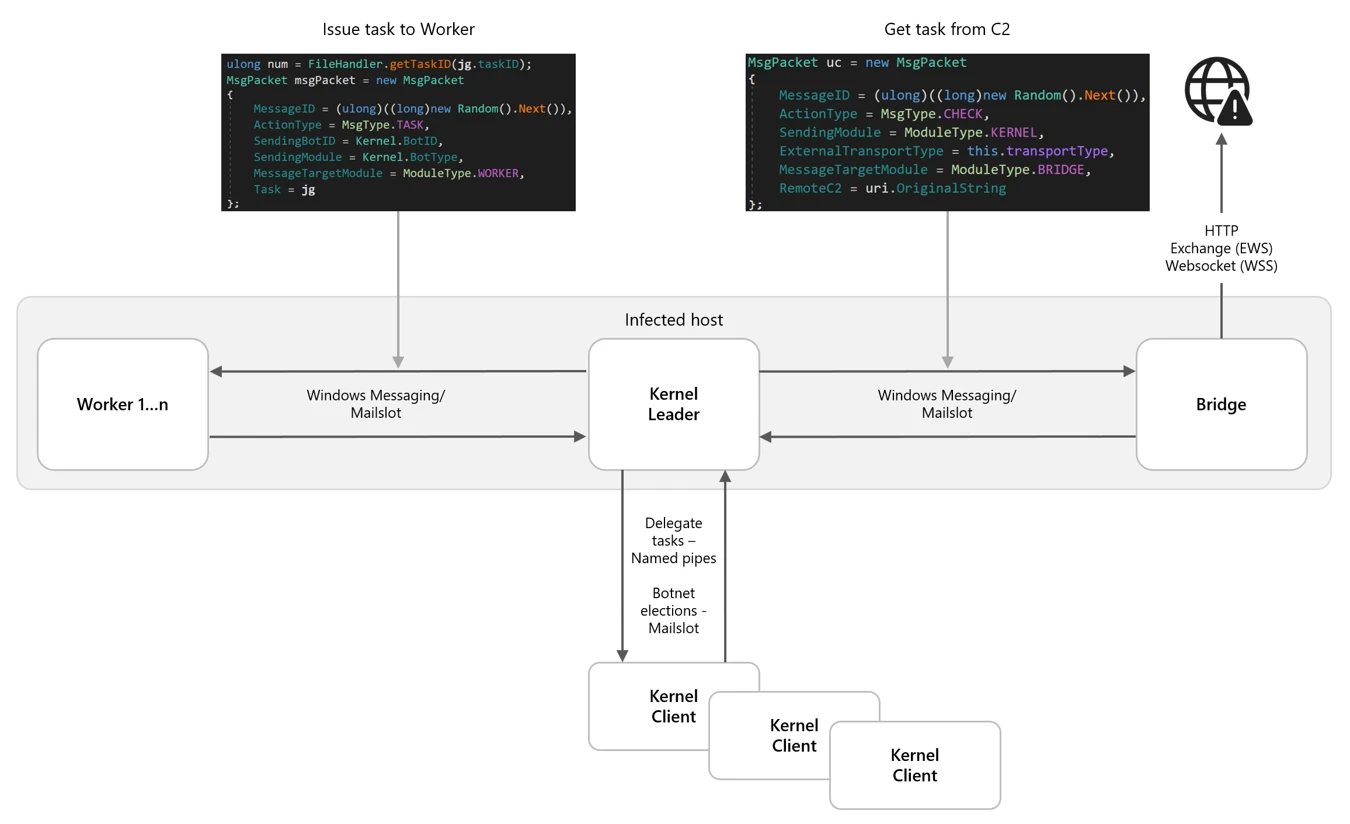
Russia-linked APT group Turla turned its Kazuar malware into a stealthy P2P botnet for long-term access to compromised systems. Russia-linked APT group Turla upgraded its Kazuar backdoor into a modular peer-to-peer botnet designed for stealth and persistent access to infected systems. Microsoft researchers say the malware allows attackers to maintain long-term control while making detection […]
 Pierluigi Paganini
May 16, 2026
OpenAI said the TanStack supply chain attack compromised two employee devices and exposed credentials from code repositories. OpenAI confirmed that the recent TanStack supply chain attack compromised two employee devices and exposed credential material stored in internal source code repositories. The incident began after the TeamPCP hacking group abused weaknesses in the package publishing process […]
 Pierluigi Paganini
May 12, 2026
Attackers are exploiting cPanel flaw CVE-2026-41940 to install the Filemanager backdoor and gain unauthorized admin access. Cybercriminals are actively exploiting the critical cPanel vulnerability CVE-2026-41940 (CVSS score of 9.3) to deploy a backdoor called Filemanager on compromised servers. cPanel is a widely used web hosting control panel that lets users manage websites and servers through a […]
 Pierluigi Paganini
May 12, 2026
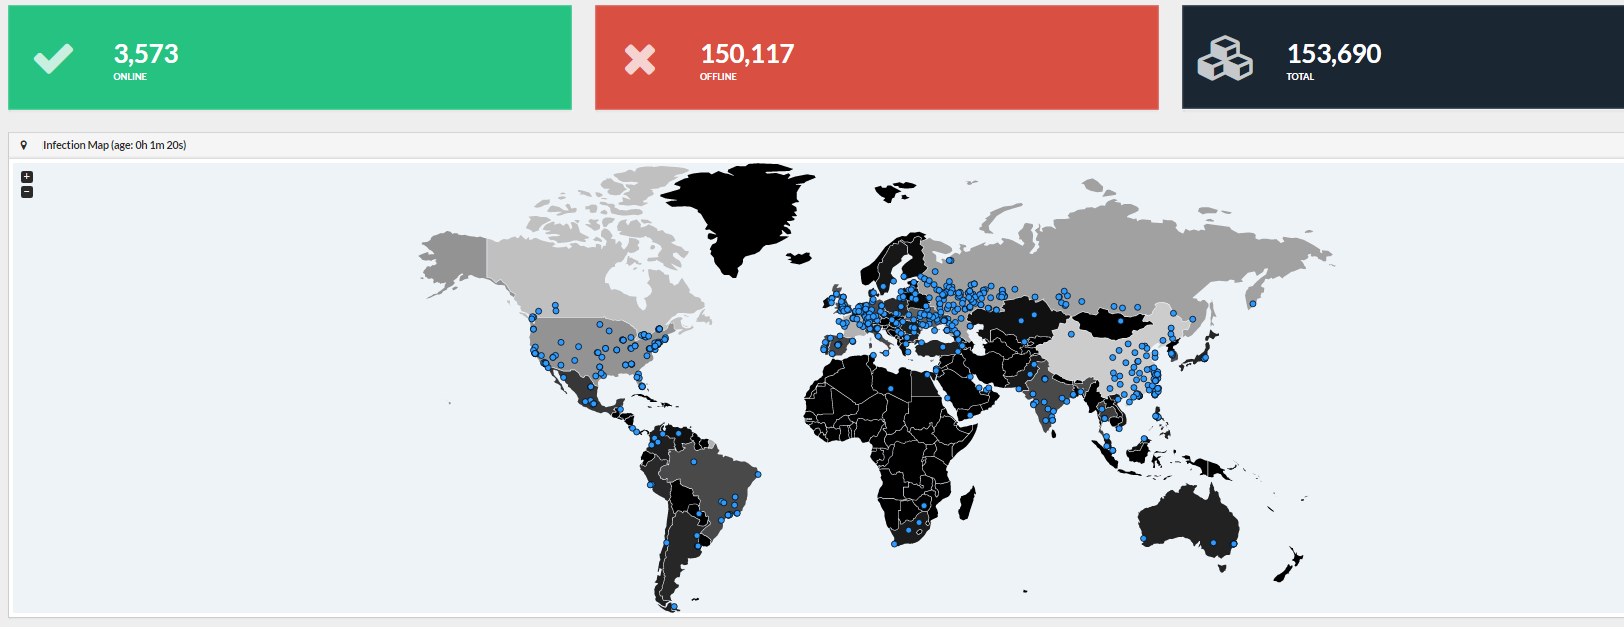
WannaCry showed how unpatched flaws and leaked cyber tools can cripple global systems, reshaping cybersecurity defenses worldwide. In memory of the day the digital world was shaken, but learned to fight back. The WannaCry ransomware attack represents one of the most significant events in recent cybersecurity history, not only for its global scale but also […]
 Pierluigi Paganini
May 12, 2026
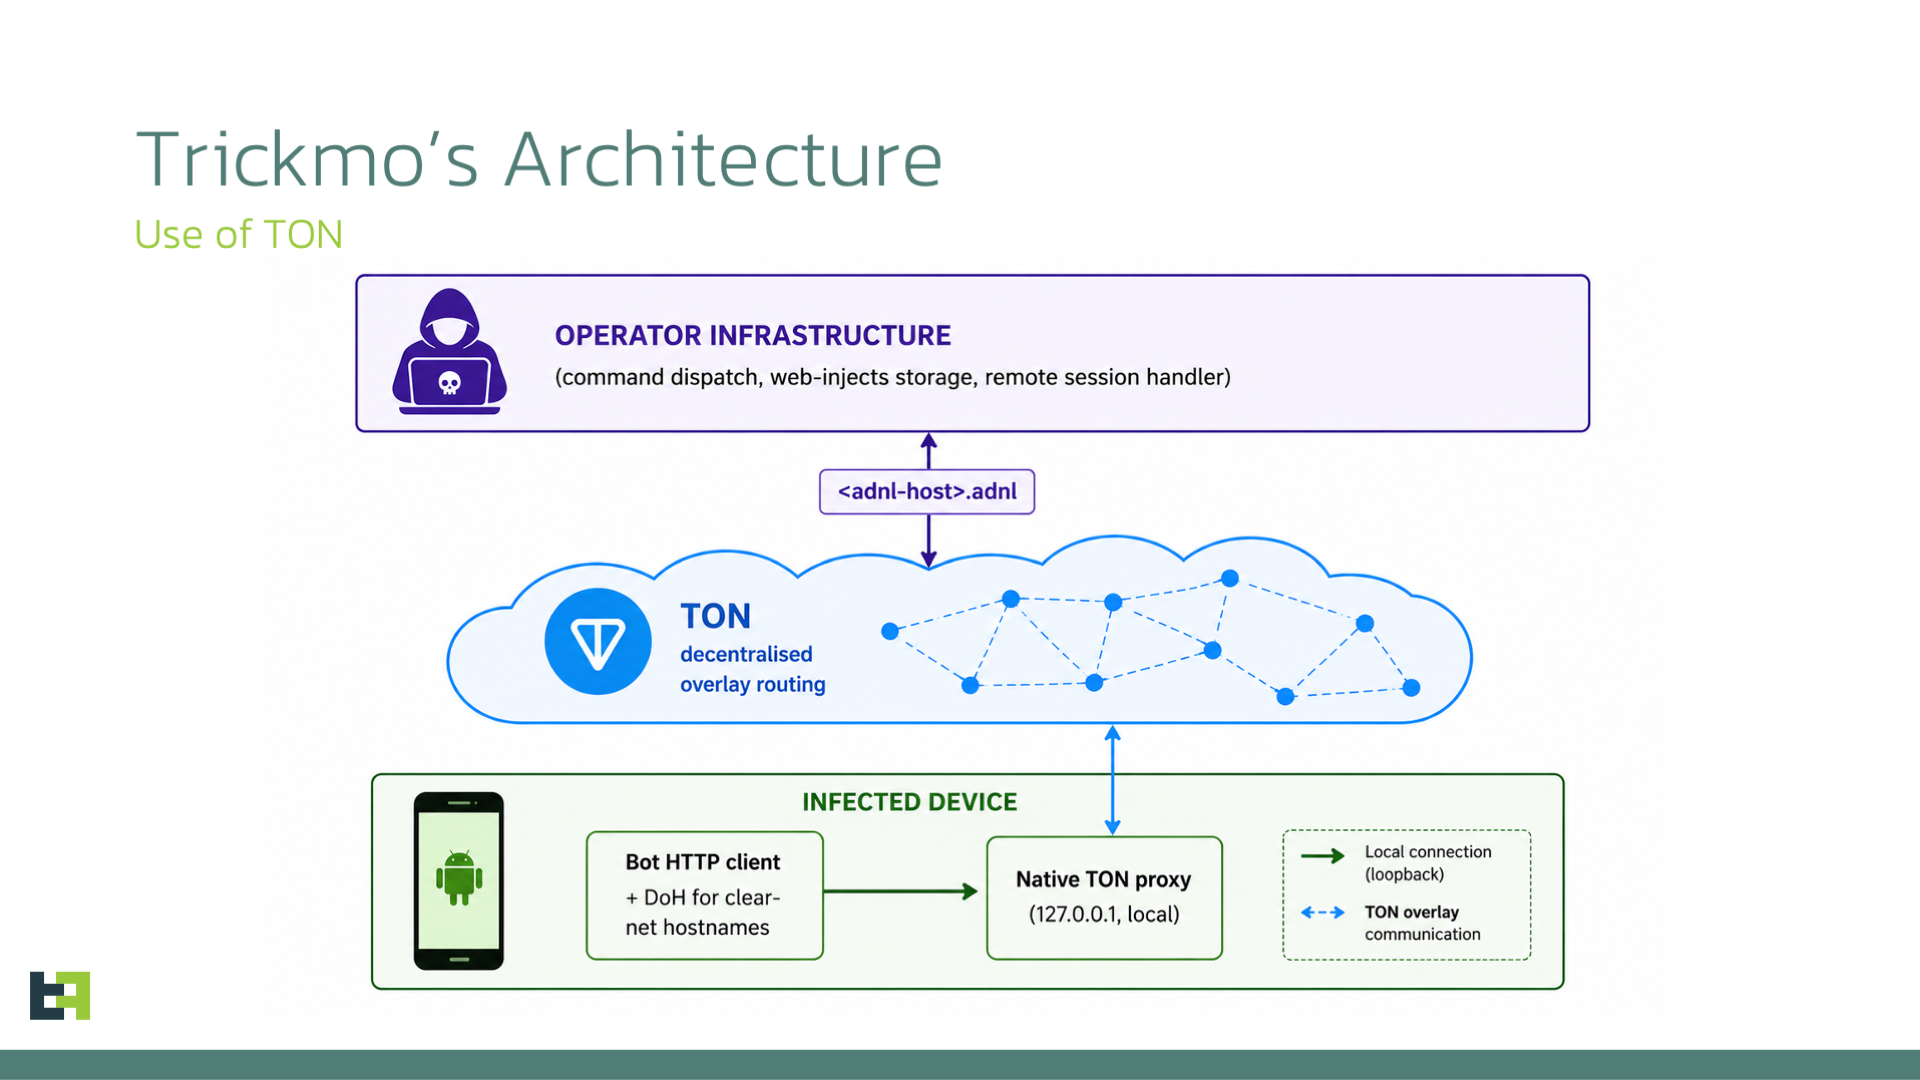
ThreatFabric found a new TrickMo Android trojan focused on stealth and persistence, moving its command-and-control traffic to the TON network. Security researchers at ThreatFabric have recently identified a new version of TrickMo, a dangerous Android banking trojan that shows how malware operators are focusing less on flashy new features and more on improving stealth, flexibility, […]
 Pierluigi Paganini
May 11, 2026
Google says hackers now use AI to create exploits, automate attacks, evade defenses, and target AI supply chains at scale. Artificial intelligence is rapidly changing the cyber threat landscape, and a new report from the Google Cloud Threat Intelligence team highlights how attackers already use AI to improve vulnerability exploitation and gain initial access to […]
Pierluigi Paganini
May 10, 2026
cPanel fixed three flaws that could allow file reads, code execution, and privilege escalation. No active exploitation has been reported yet. cPanel has released security updates to fix three vulnerabilities affecting cPanel & WHM that could allow attackers to read files, execute code, or escalate privileges on vulnerable systems. Below are the descriptions for these […]
 Pierluigi Paganini
May 10, 2026
JDownloader website was hacked to distribute malicious Windows and Linux installers carrying a Python RAT between May 6–7, 2026. JDownloader official website was compromised in a supply chain attack that replaced legitimate Windows and Linux installers with malicious files between May 6 and May 7, 2026. JDownloader is a free, open-source download management application designed […]