 Pierluigi Paganini
 April 16, 2026
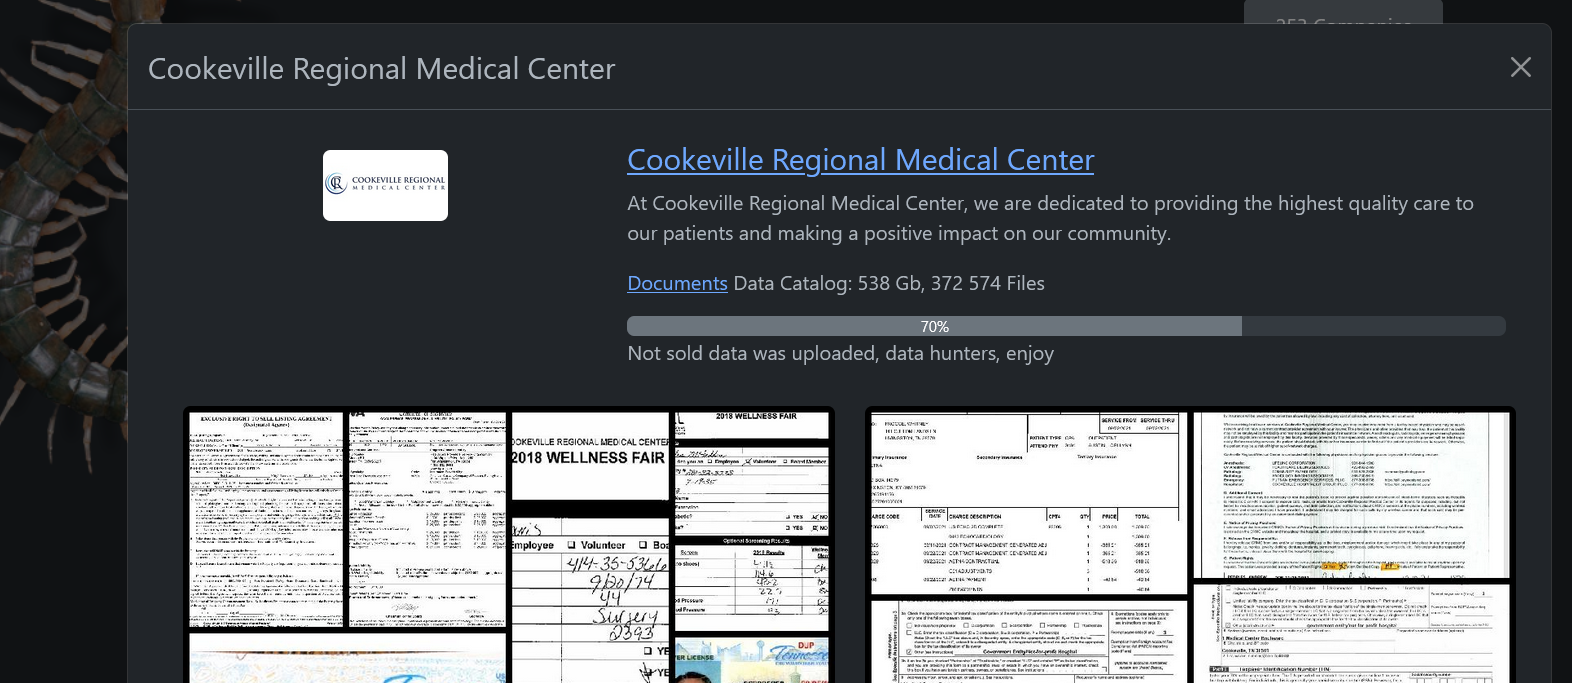
A ransomware attack on Cookeville Regional Medical Center hospital (Tennessee) exposed data of 337,000 people after hackers stole 500GB of sensitive information from its systems. A ransomware attack on Cookeville Regional Medical Center (CRMC) in Tennessee led to a major data breach affecting about 337,000 people. The attack, carried out by the Rhysida group, involved […]
 Pierluigi Paganini
April 16, 2026
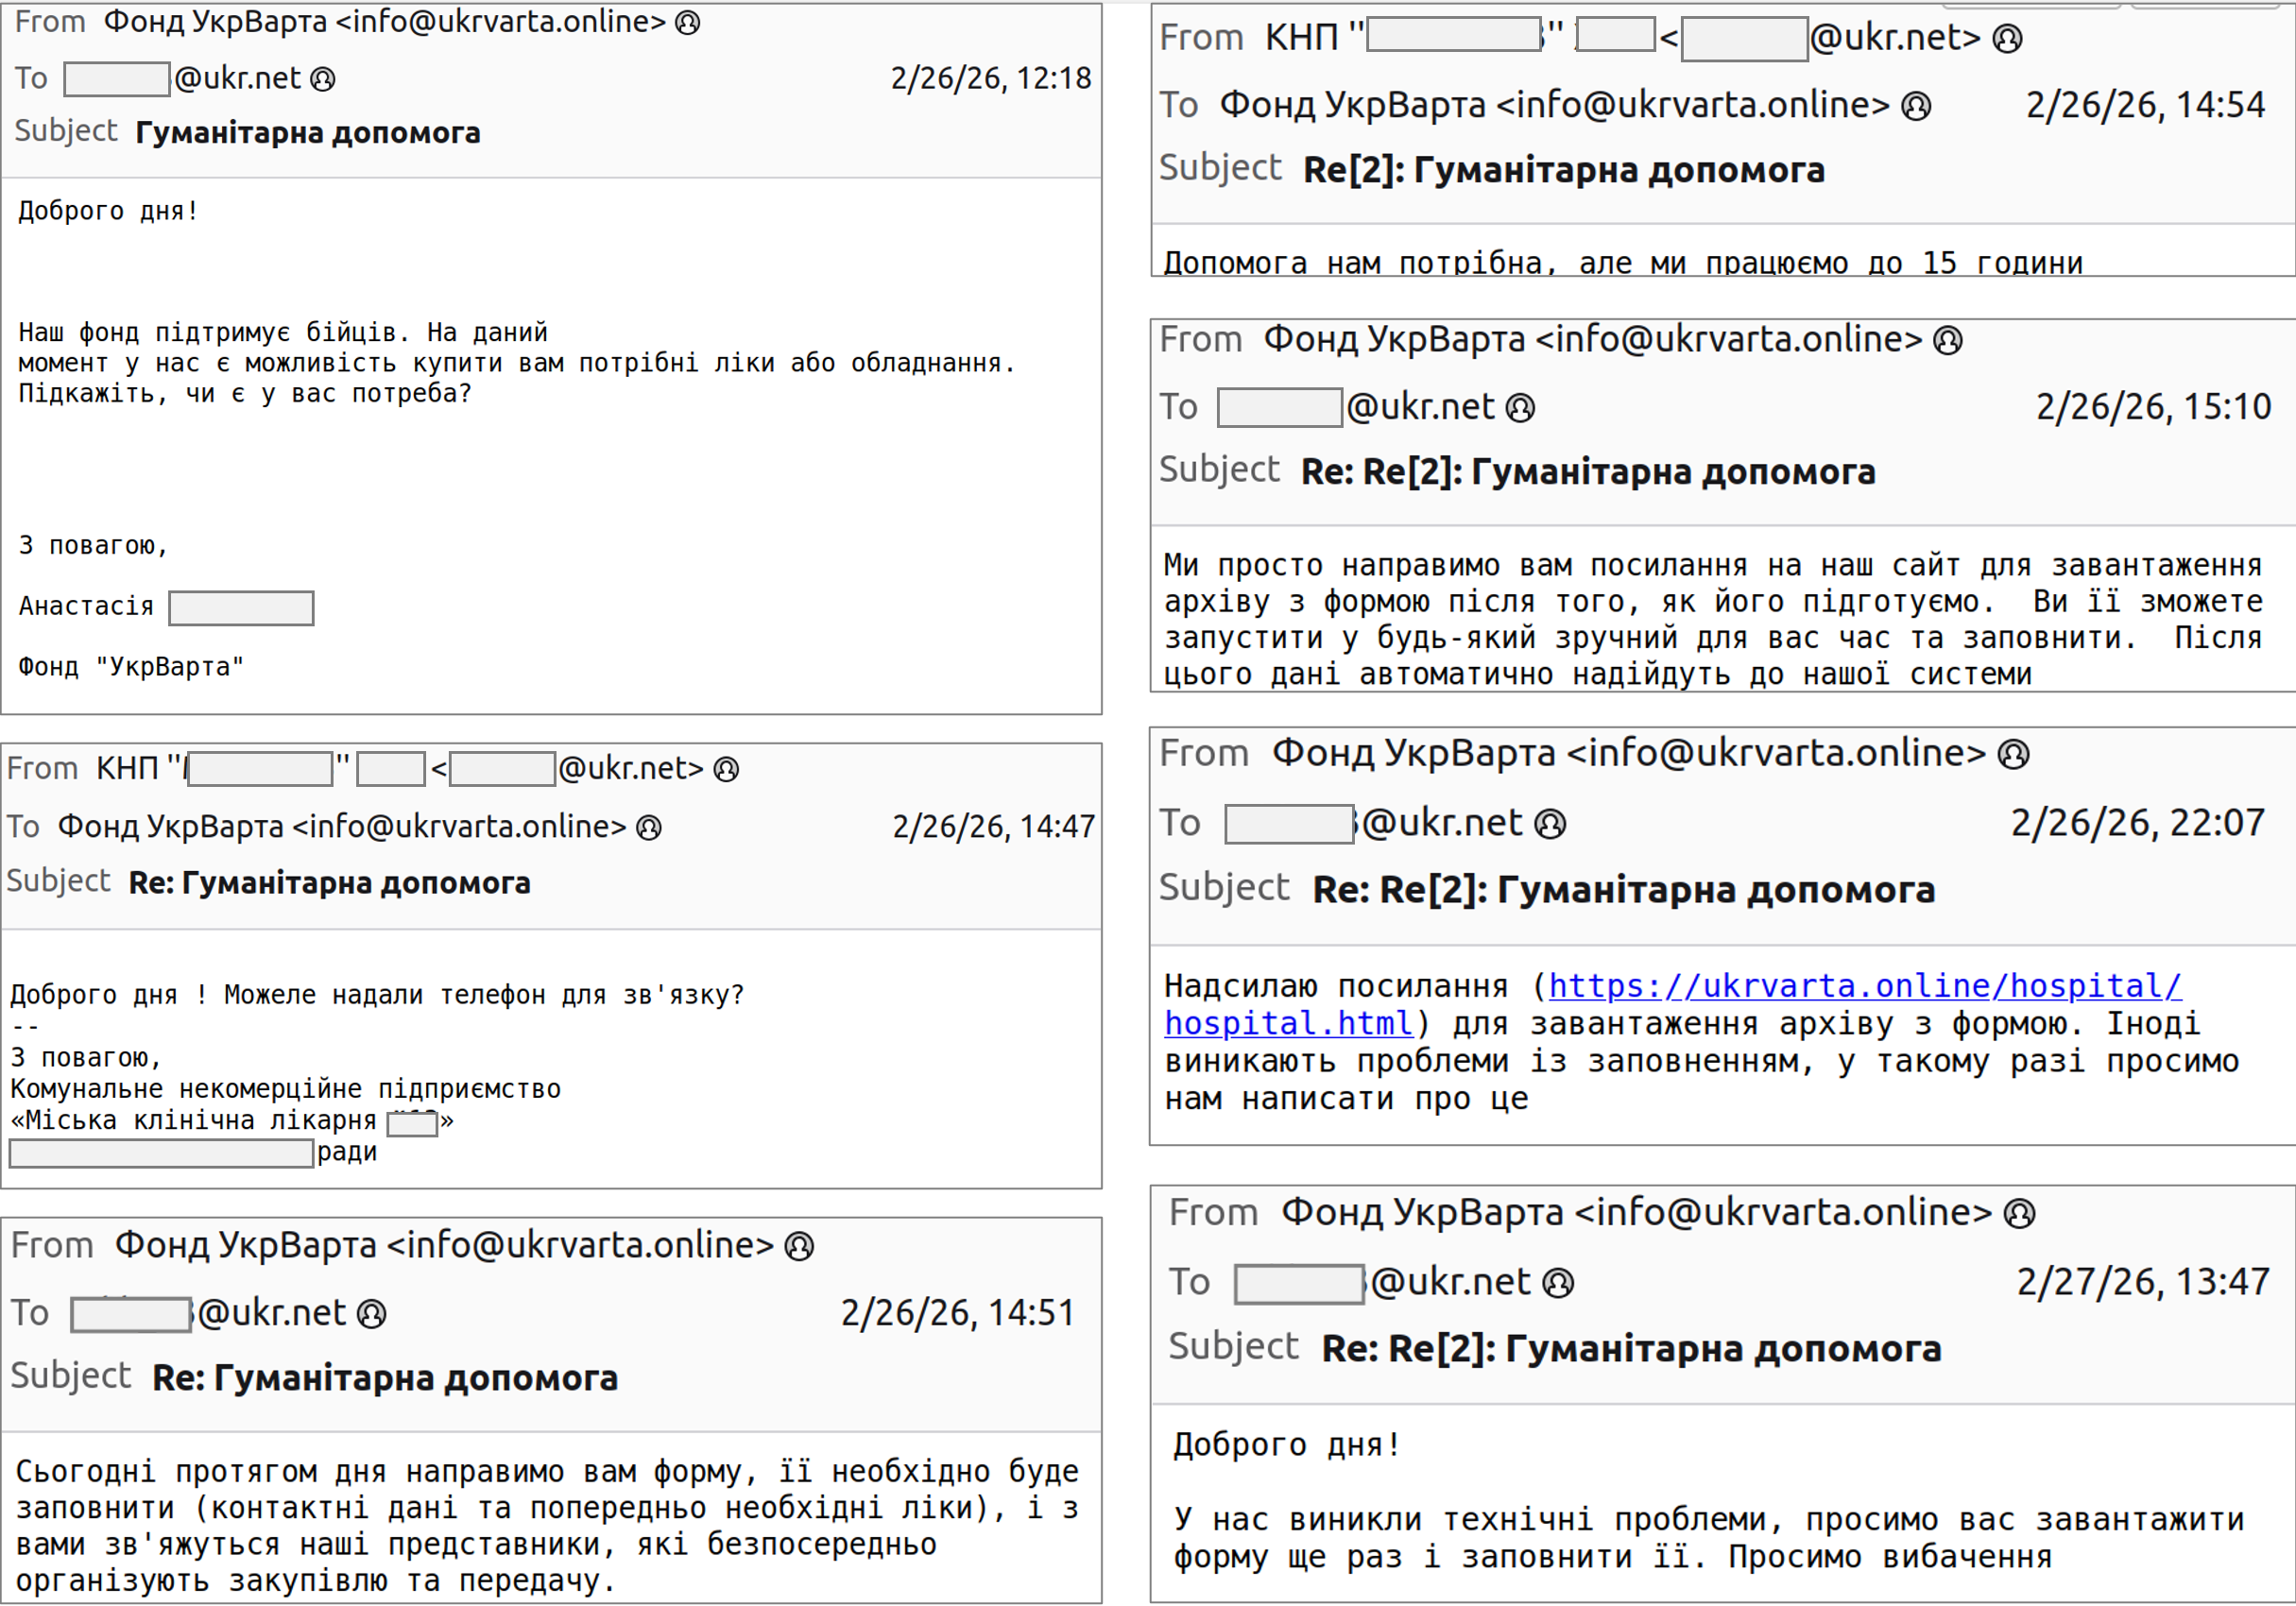
CERT-UA reports UAC-0247 targeting Ukrainian clinics and government bodies with malware stealing data from Chromium browsers and WhatsApp. CERT-UA has revealed a cyber campaign by the threat actor UAC-0247 targeting Ukrainian government entities and municipal healthcare facilities, including clinics and emergency hospitals. The operation between March and April 2026, used malware designed to steal sensitive […]
 Pierluigi Paganini
April 15, 2026
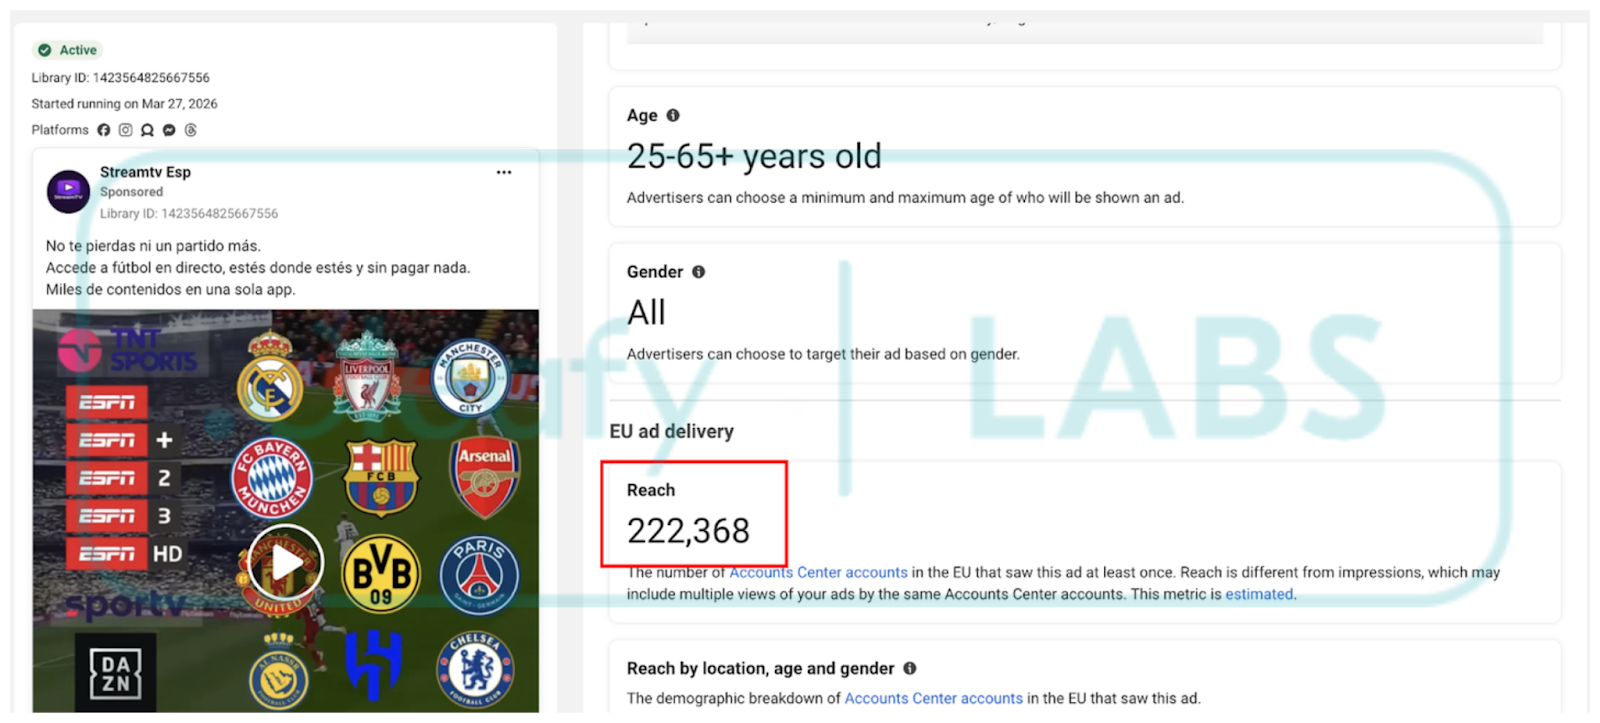
Mirax, a new Android RAT, spread via Meta ads, infected 220,000 users and turns devices into SOCKS5 proxies, giving attackers full remote control. Mirax is a new Android remote access trojan spreading through ads on Meta platforms, targeting mainly Spanish-speaking users and reaching over 220,000 accounts. The malicious code lets attackers fully control infected devices […]
 Pierluigi Paganini
April 14, 2026
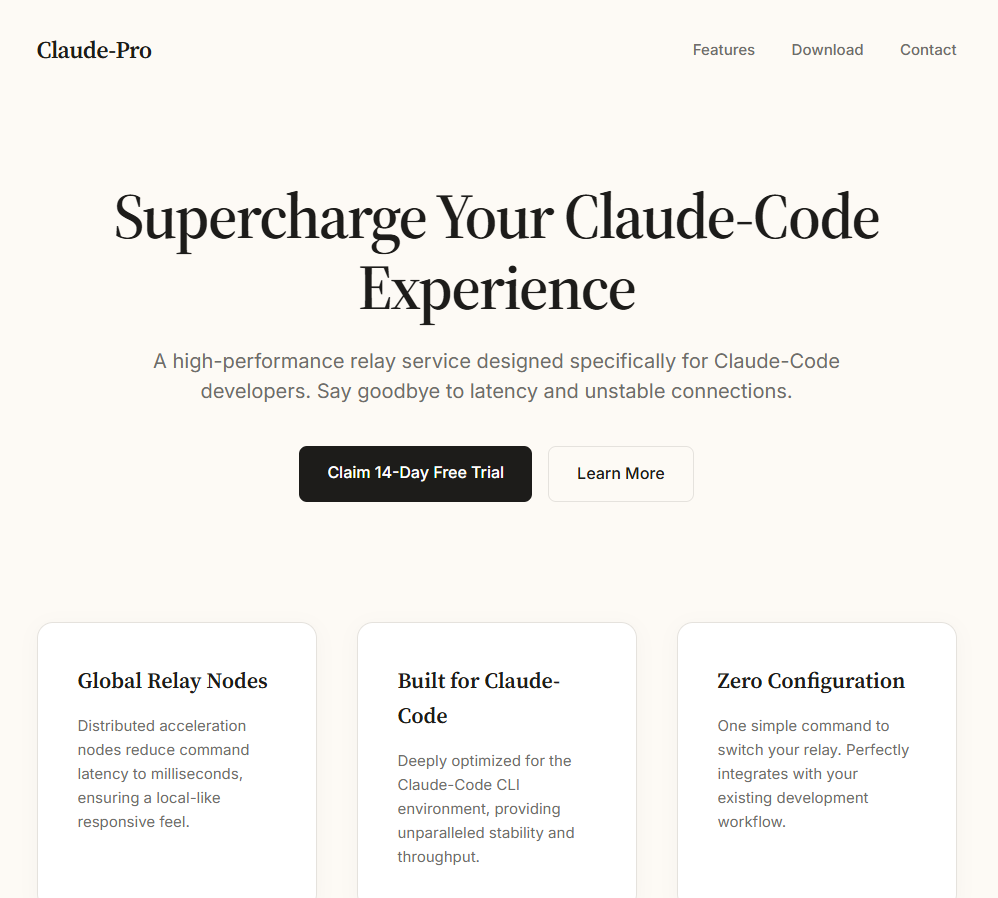
Fake Claude website impersonates Anthropic and delivers PlugX RAT via ZIP download using DLL sideloading. A fake website impersonating Anthropic’s Claude service was found distributing the PlugX remote access trojan, according to Malwarebytes. The rogue site abuses the chatbot’s popularity to trick users into downloading a ZIP archive presented as a “pro version” installer. The […]
 Pierluigi Paganini
April 13, 2026
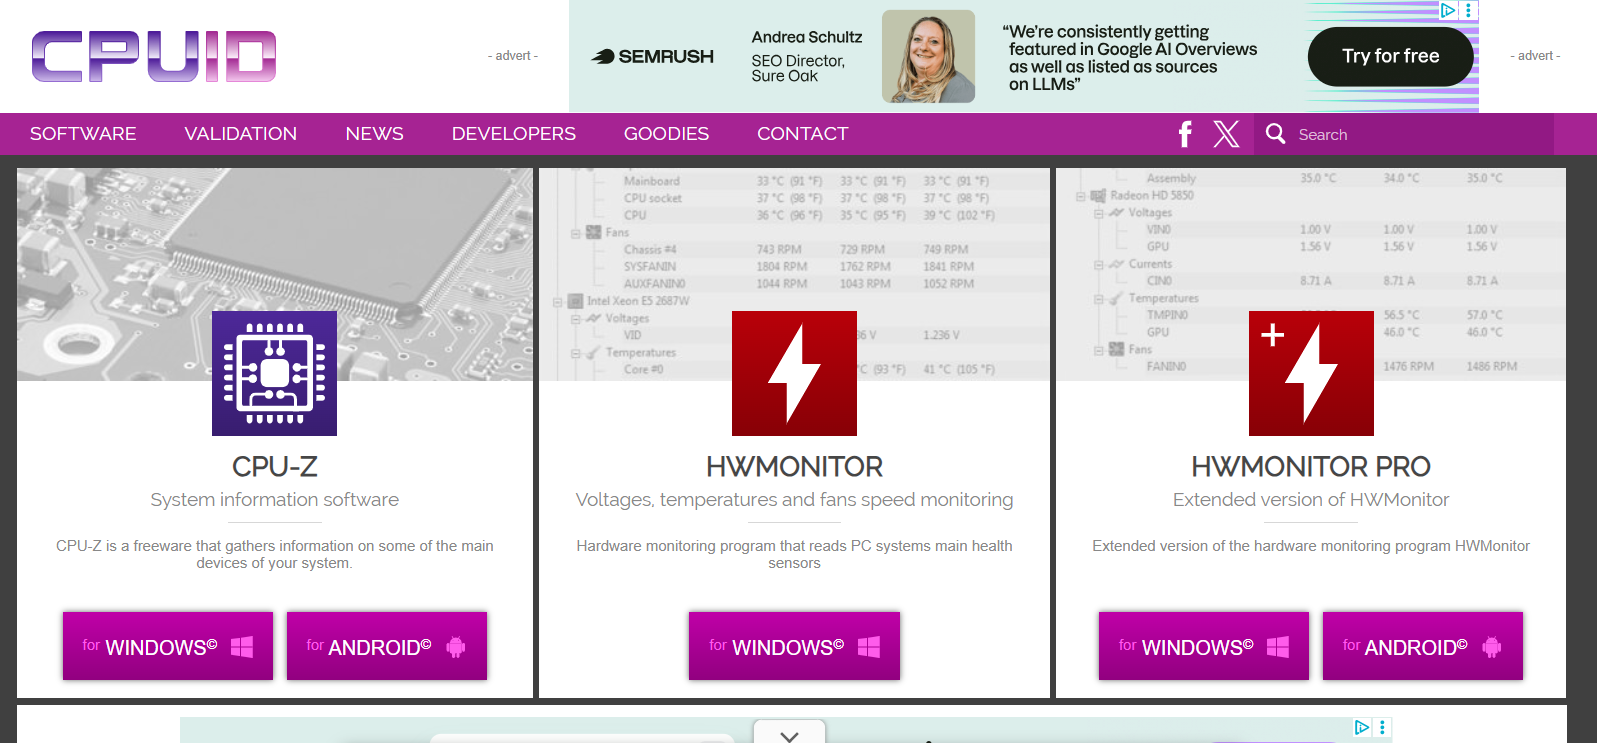
Threat actors compromised the CPUID website and spread STX RAT through fake CPU-Z and HWMonitor downloads. Attackers breached the website CPUID and replaced download links for CPU-Z and HWMonitor with malicious files for several hours. Users who downloaded them got infected with the STX RAT, giving attackers remote access to their systems. The short attack […]
 Pierluigi Paganini
April 12, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Thirty-Six Malicious npm Strapi Packages Deploy Redis RCE, Database Theft, and Persistent C2 Malicious LNK Files Distributing a Python-Based Backdoor and Changes in Distribution Techniques (Kimsuky Group) Hackers Are Attempting to Turn ComfyUI Servers Into a […]
 Pierluigi Paganini
April 12, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Censys finds 5,219 devices exposed to attacks by Iranian APTs, majority in U.S. GlassWorm evolves with […]
 Pierluigi Paganini
April 11, 2026
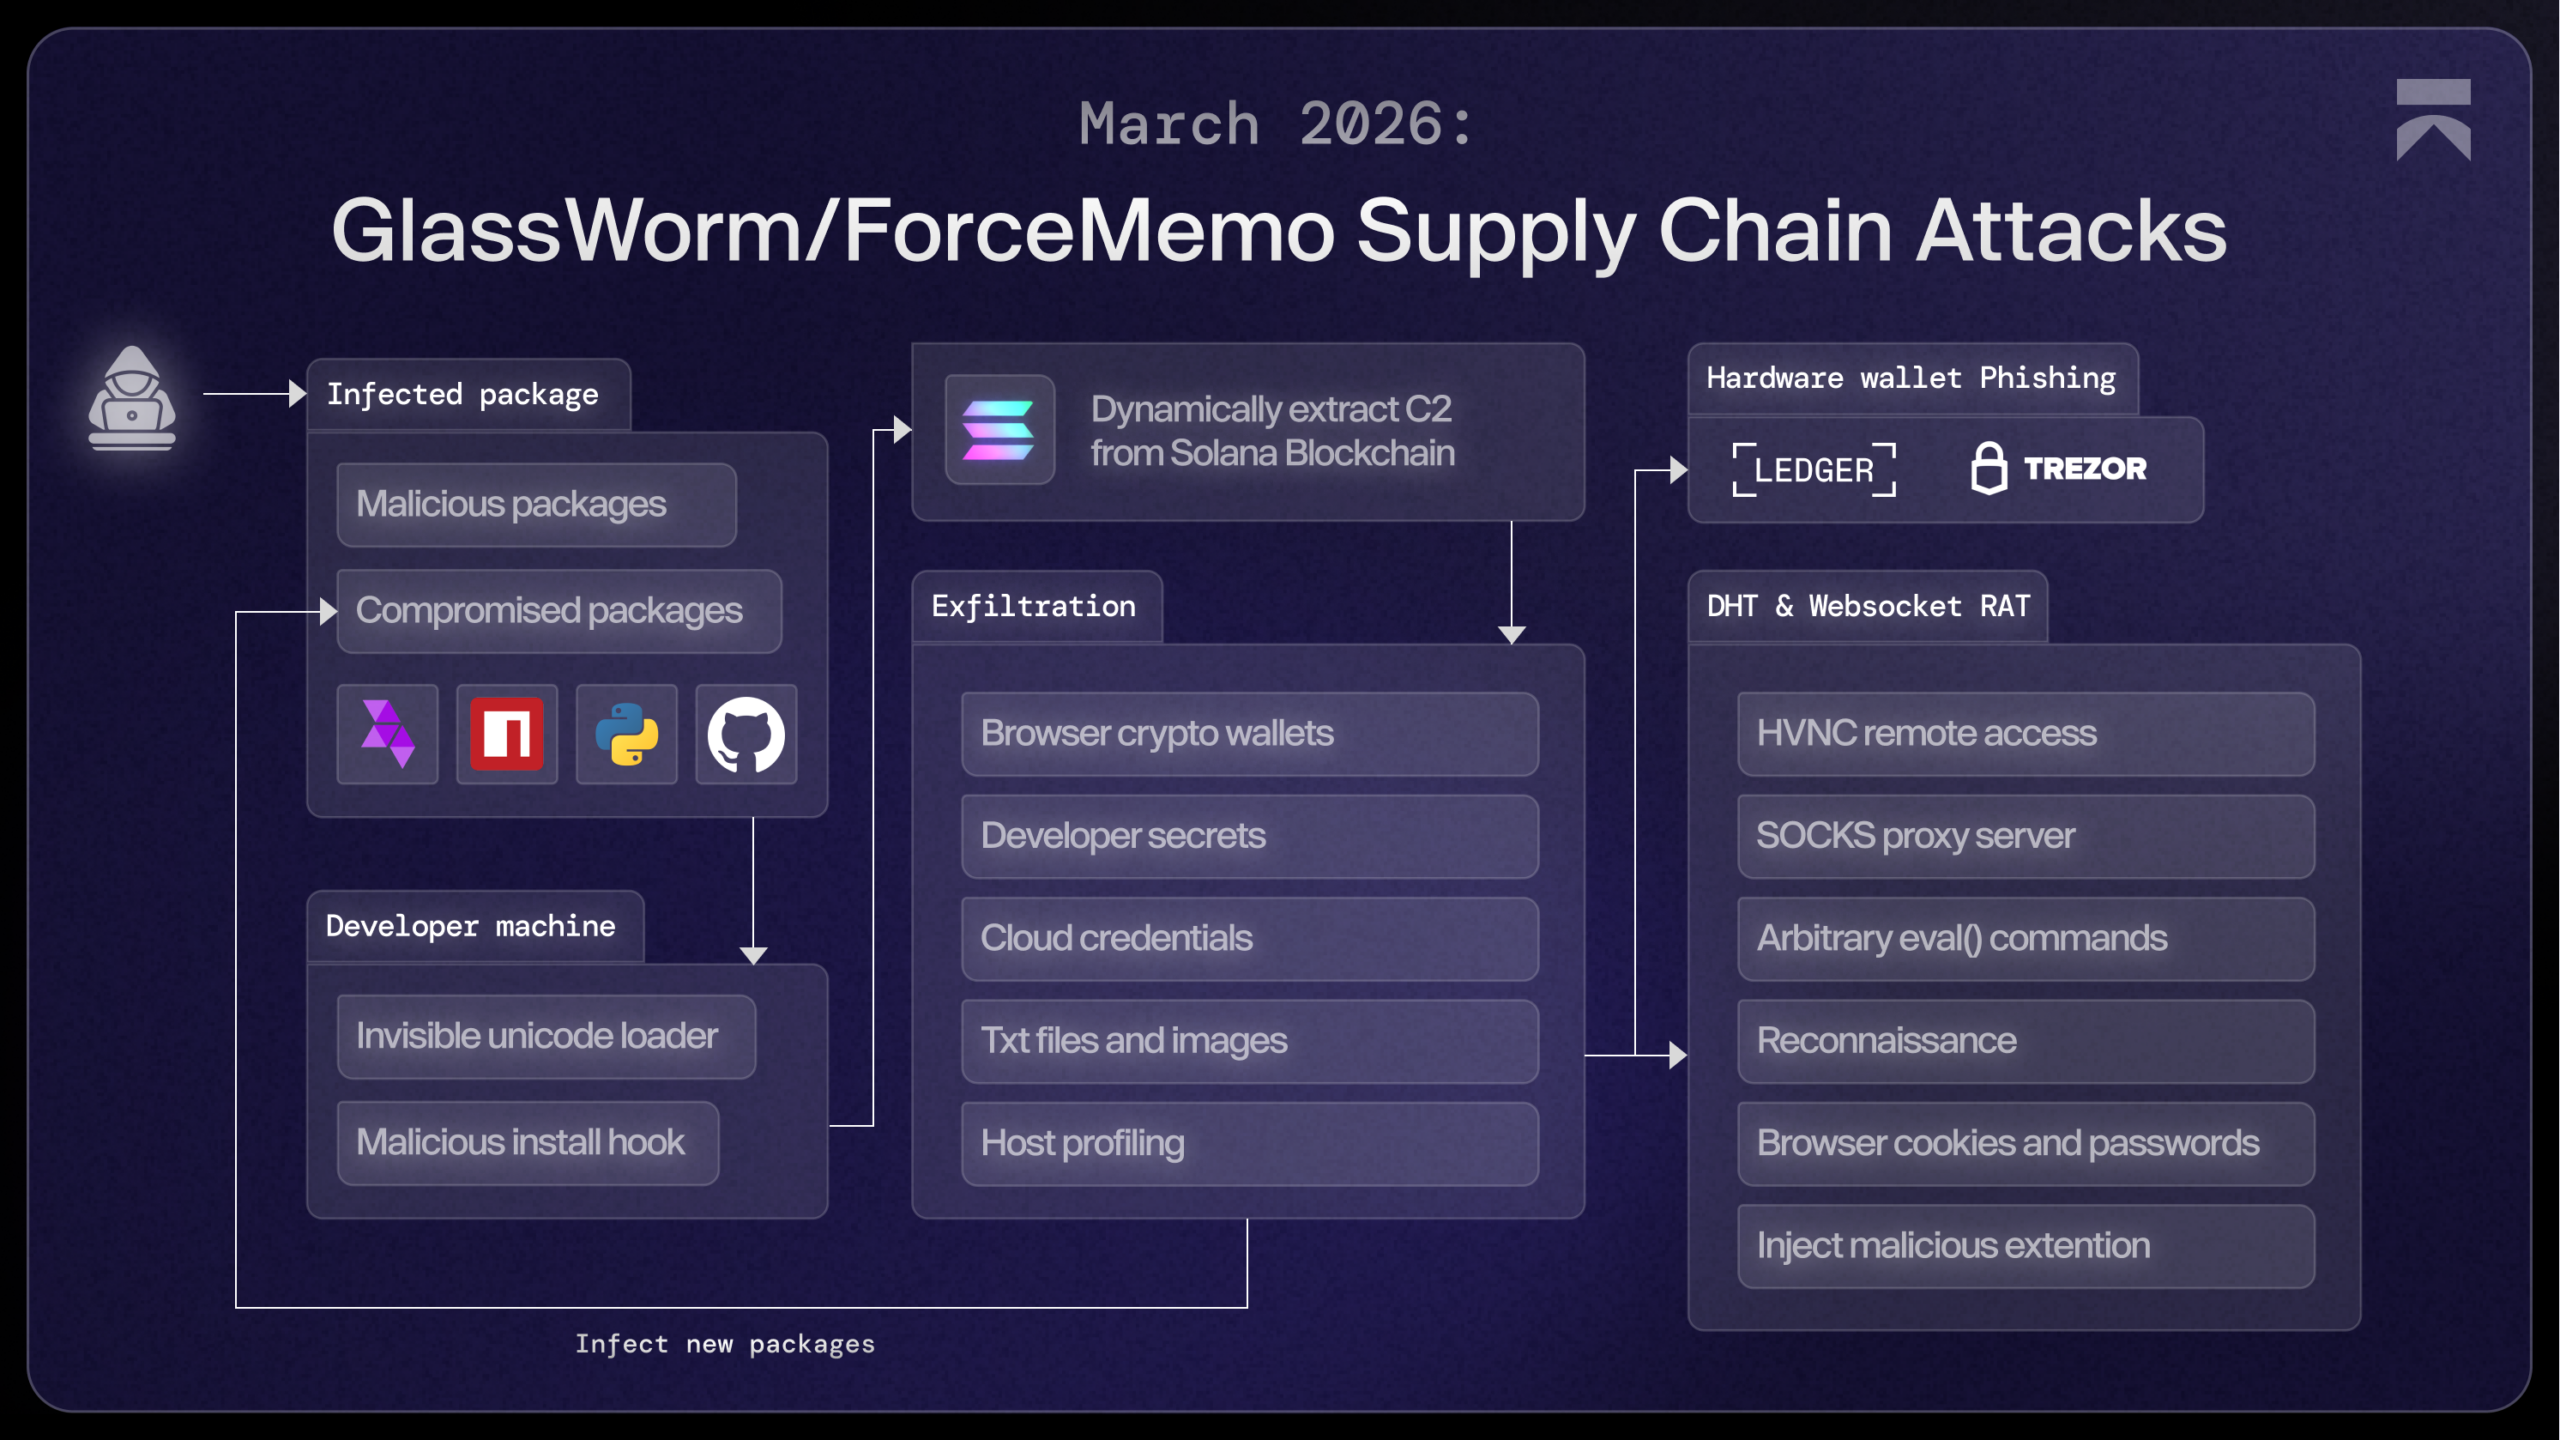
The GlassWorm campaign uses a Zig-based dropper hidden in a fake IDE extension to infect developer tools and compromise systems. The GlassWorm campaign, active since 2025, has evolved from malicious npm packages to large-scale supply chain attacks across GitHub, npm, and VS Code, even deploying RATs via fake browser extensions. In its latest iteration, threat […]
 Pierluigi Paganini
April 10, 2026
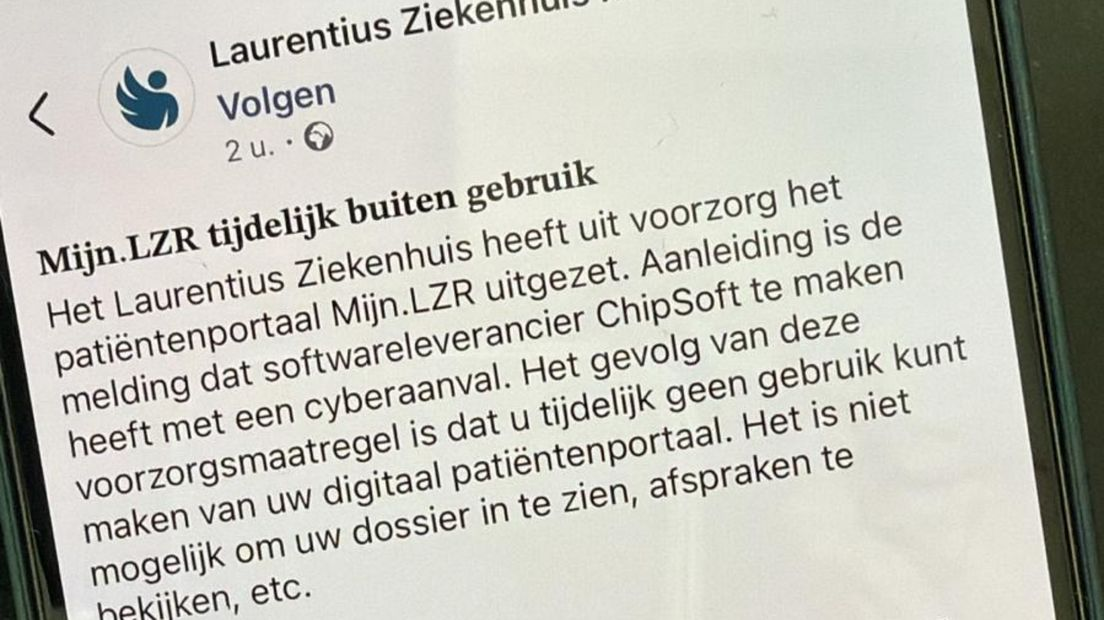
Dutch healthcare IT firm ChipSoft suffered a ransomware attack, forcing services and its HiX platform offline, impacting hospitals and patients. ChipSoft, a major Dutch provider of EHR systems, was hit by a ransomware attack that forced it to take its website and digital services offline, disrupting access for hospitals, healthcare providers, and patients. EHR (Electronic […]
 Pierluigi Paganini
April 10, 2026
LucidRook is Lua malware used in phishing attacks on NGOs and universities in Taiwan, linked to UAT-10362, spread via password-protected emails. LucidRook is a new Lua-based malware used in targeted phishing attacks against NGOs and universities in Taiwan. Cisco Talos links it to a skilled group tracked as UAT-10362. In Oct 2025, attackers used password-protected […]