 Pierluigi Paganini
 April 03, 2018
Researchers John Mason with the help of TheBestVPN.com the ethical hacker File Descriptor from Cure53 tested 15 VPN services and 10 of them were causing DNS leaks through their Chrome browser extensions. Intro Google Chrome has a feature called DNS Prefetching(https://www.chromium.org/developers/design-documents/dns-prefetching) which is an attempt to resolve domain names before a user tries to follow a link. It’s a solution to reduce latency delays […]
 Pierluigi Paganini
April 02, 2018
MITRE is evaluating a new service dubbed ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) for APT detection. MITRE is going to offer a new service based on its ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) framework to evaluate products based on their ability in detecting advanced persistent threats. “MITRE’s Adversarial Tactics, Techniques, and Common Knowledge (ATT&CK™) is a […]
 Pierluigi Paganini
April 02, 2018
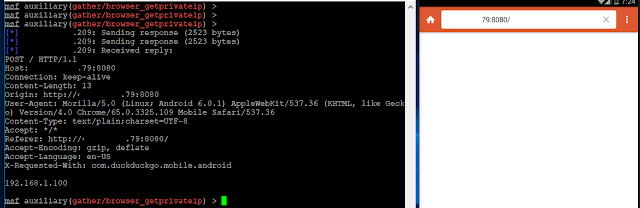
The security researcher Dhiraj Mishra (@mishradhiraj_) has studied how VPNs & Privacy Browsers leak users’ IPs via WebRTC Hi Internet, You might have heard about VPN’s & Privacy Browsers leaking users’ IPs via WebRTC [1] [2] Summary: Got CVE-2018-6849 reserved, wrote a Metasploit Module for this issue which uses WebRTC and collects the leak private IP address, however this module may […]
 Pierluigi Paganini
April 01, 2018
The Philippine central bank has thrown an alert to local financial institutions following a cyber attack against the SWIFT servers at the Malaysian central bank. The Philippine central bank has thrown an alert to local financial institutions following a cyber attack against the Malaysian central bank. According to Malaysian governor, the hackers attempted to steal money through fraudulent wire […]
 Pierluigi Paganini
April 01, 2018
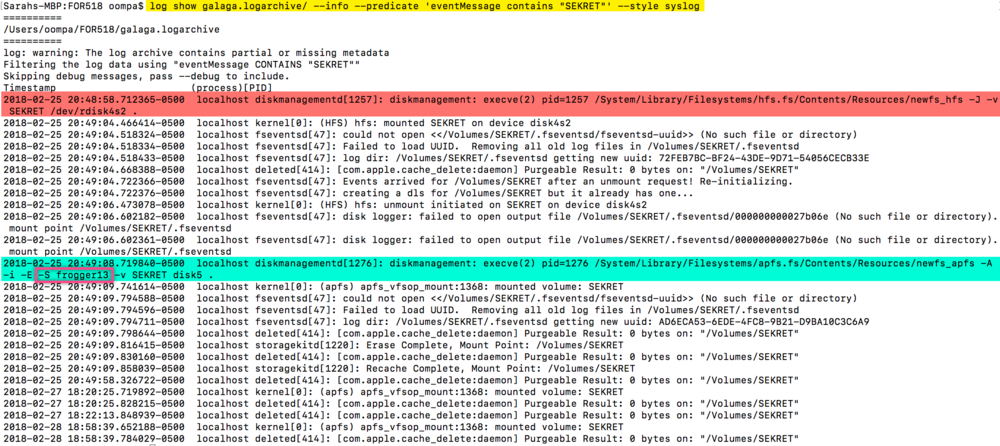
A security expert discovered severe security issues in APFS file system for macOS High Sierra that expose passwords of encrypted external drives in plain text. A vulnerability in APFS file system for macOS High Sierra operating system has been discovered by forensic analyst Sarah Edwards. According to Edwards, the flaw exposes passwords of encrypted external drives in plain text. […]
 Pierluigi Paganini
March 31, 2018
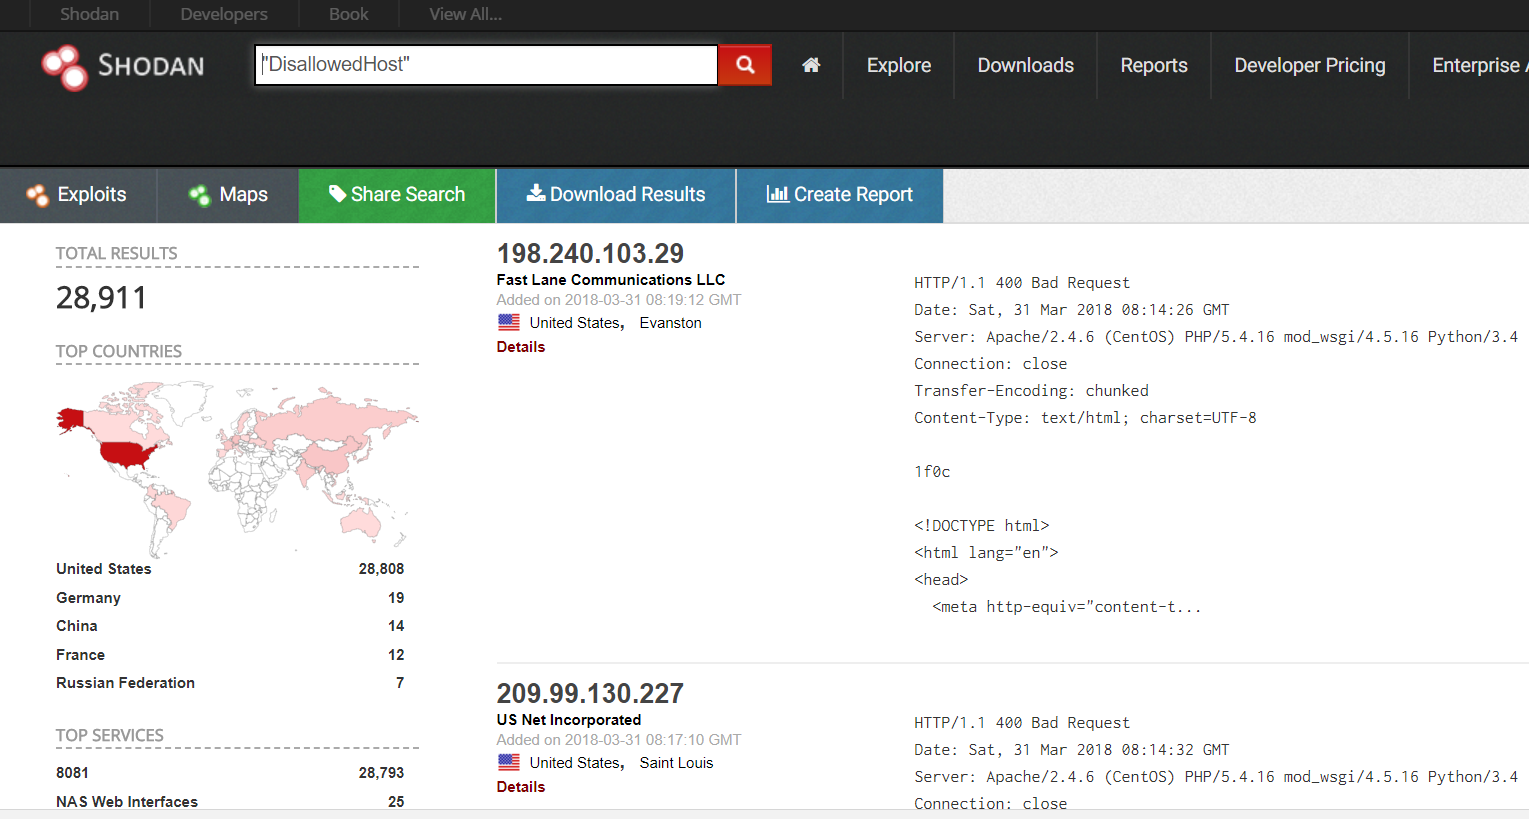
The security researcher Fábio Castro discovered tens of thousands of Django apps that expose sensitive data because developers forget to disable the debug mode. Security researchers have discovered misconfigured Django applications that are exposing sensitive information, including passwords, API keys, or AWS access tokens. Django is a very popular high-level Python Web framework that allows rapid development of Python-based web applications. The […]
 Pierluigi Paganini
March 31, 2018
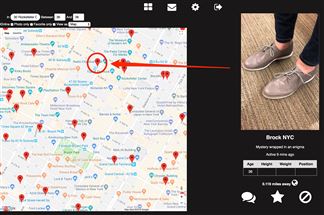
According to an NBC report, the Grindr gay-dating app was affected by 2 security issues (now patched) that could expose the information of its more than 3 million daily users. Every day we read of a new data breach, in some cases, exposed data could have a severe impact on the victim. According to an NBC report, the Grindr […]
 Pierluigi Paganini
March 30, 2018
A ransomware infected systems at the Uttar Haryana Bijli Vitran Nigam power company in India, crooks demanded 10 million Rupees to get the data back. The Uttar Haryana Bijli Vitran Nigam power company in India was hacked last week, attackers breached into its computer systems and stole the billing data of their customers. The hackers demanded 10 million Rupees to […]
 Pierluigi Paganini
March 29, 2018
The Drupal development team has fixed the drupalgeddon2 vulnerability that could be exploited by an attacker to take over a website. A few days ago, Drupal Security Team confirmed that a “highly critical” vulnerability, tracked as CVE-2018-7600, affects Drupal 7 and 8 core and announced the availability of security updates on March 28th. The vulnerability was discovered […]
 Pierluigi Paganini
March 29, 2018
This week Cisco patched three critical vulnerabilities affecting its operating system IOS XE, two of them are remote code execution flaws that could be exploited by an attacker to gain full control over vulnerable systems. Cisco March 2018 Semiannual Cisco IOS and IOS XE Software Security Advisory Bundled Publication addressed 22 vulnerabilities, 3 of them rated as […]
Security / October 08, 2026