 Pierluigi Paganini
 September 30, 2019
After 2 years of waiting, MalwareMustDie returns with an excellent page of malware analysis of a new IoT malware: Linux/AirDropBot. Yes, I have to confess, it was hard to wait all this time, but the reward it was worth it: unixfreaxjp is return, with a new, great page of reverse engeeniring published on the MalwareMustDie […]
 Pierluigi Paganini
September 30, 2019
Experts recently analyzed an information-stealing malware tracked as Arcane Stealer V that is very cheap and easy to buy in the Dark Web. In July 2019, researchers at Fidelis Threat Research Team (TRT) analyzed a sample of Arcane Stealer V, a .net information-stealing malware that is easy to acquire in the dark web. The author […]
 Pierluigi Paganini
September 29, 2019
A new round of the weekly newsletter arrived! The best news of the week with Security Affairs Hi folk, let me inform you that I suspended the newsletter service, anyway I’ll continue to provide you a list of published posts every week through the blog. Once again thank you! 0patch will provide micropatches for Windows […]
 Pierluigi Paganini
September 29, 2019
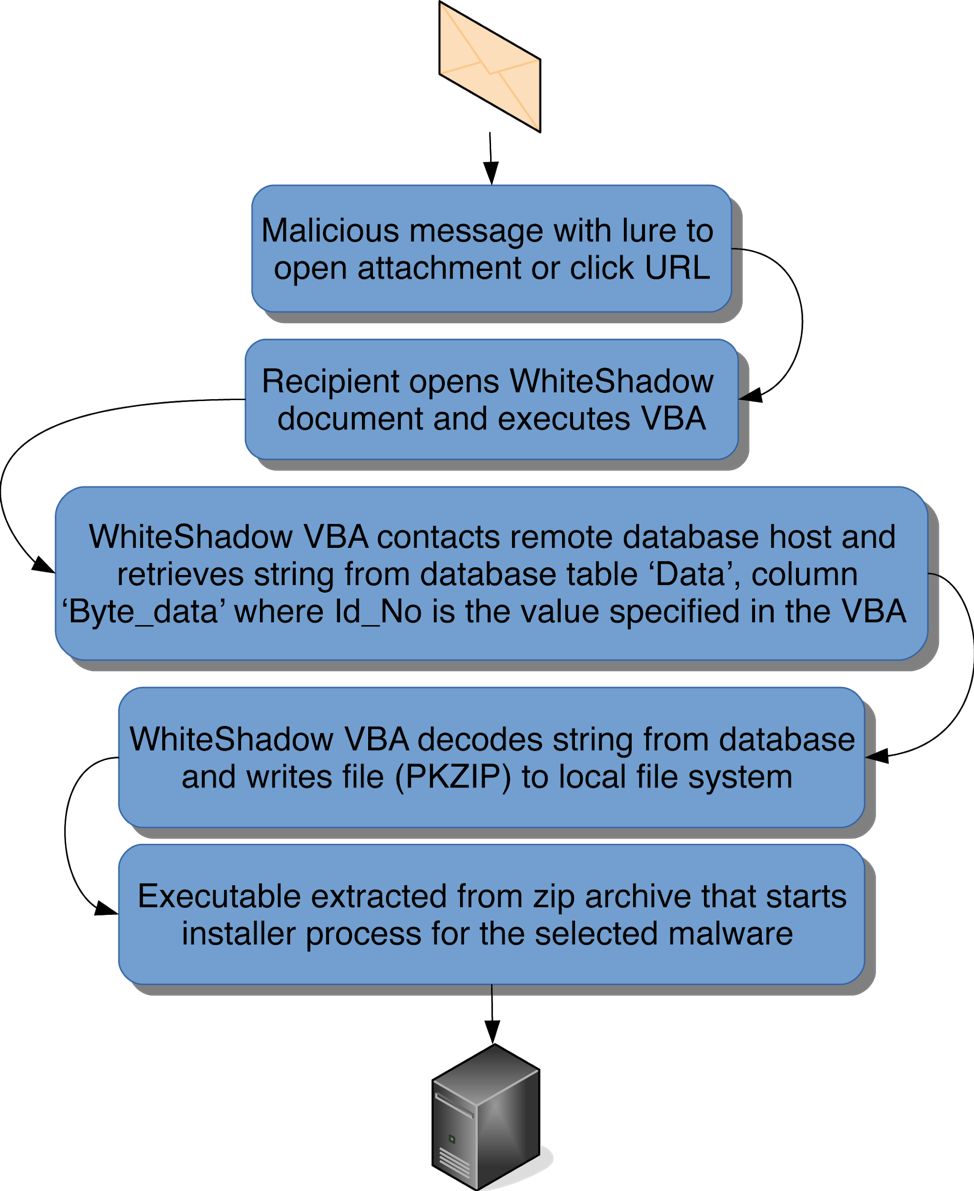
Researchers at Proofpoint have spotted a piece of downloader, dubbed WhiteShadow, that leverages Microsoft SQL queries to pull and deliver malicious payloads. In August, malware researchers at Proofpoint spotted a new downloader which is being used to deliver a variety of malware via Microsoft SQL queries. The experts detected new Microsoft Office macros, which collectively […]
 Pierluigi Paganini
September 29, 2019
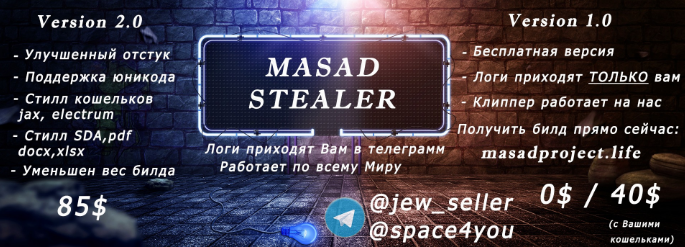
Experts at Juniper Threat Labs have discovered a new piece of malware dubbed Masad Stealer that exfiltrates cryptocurrency wallet files via Telegram. Security researchers at the Juniper Threat Labs discovered a strain of malware dubbed Masad Stealer that is actively distributed. The malware could steals files, browser information, and cryptocurrency wallet data and send them […]
 Pierluigi Paganini
September 28, 2019
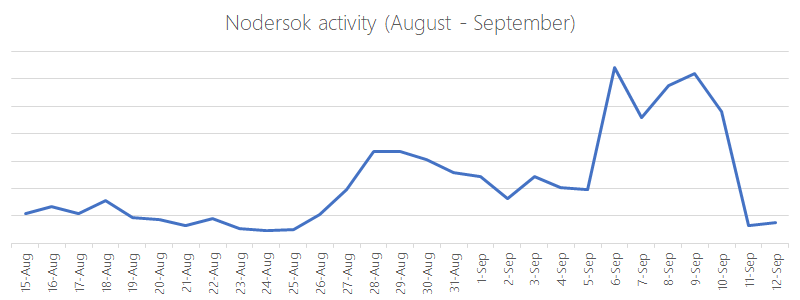
Microsoft researchers observed a campaign delivering malware, dubbed Nodersok, relying on advanced techniques and elusive network infrastructure. Microsoft experts observed a malware campaign, tracked as Nodersok, relying on advanced techniques and elusive network infrastructure. Microsoft uncovered the campaign in mid-July when noticed patterns in the anomalous usage of MSHTA.exe. Nodersok abuse of legitimate tools also […]
 Pierluigi Paganini
September 28, 2019
A series of cyber attacks hit the defense contractors Rheinmetall AG and Defence Construction Canada (DCC) causing the disruption of their information technology systems. This month a series of cyber attack hit defense contractors Rheinmetall AG and Defence Construction Canada (DCC) disrupting their information technology systems. German Rheinmetall AG is a market leader in the supply of military technology, in […]
 Pierluigi Paganini
September 27, 2019
IBM researchers observed one of the Magecart groups using a malicious code to inject into commercial-grade layer 7 L7 routers. IBM X-Force Incident Response and Intelligence Services (IRIS) experts observed that one of the Magecart groups, tracked as MG5, is using malware to inject into commercial-grade L7 routers. The experts believe the hackers are likely […]
 Pierluigi Paganini
September 27, 2019
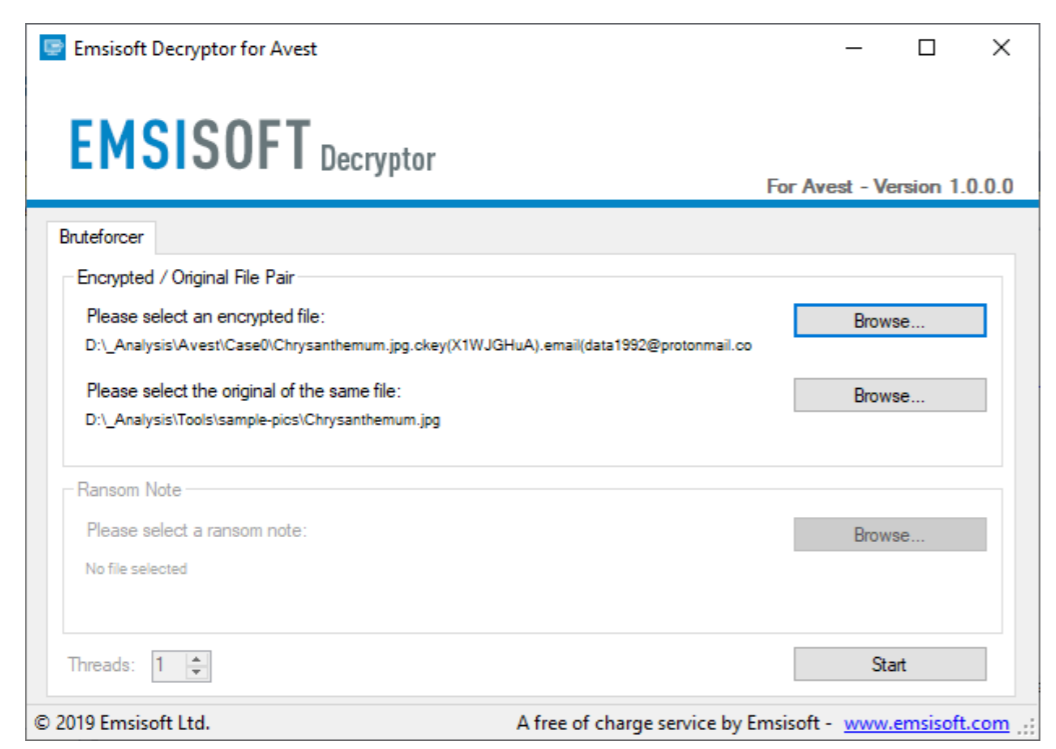
Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days after the release of WannaCryFake decryptor. Emsisoft security firm has released a new free decryption tool for the Avest ransomware, a few days ago the researchers also released a free decryptor for the WannaCryFake ransomware. The Avest ransomware […]
 Pierluigi Paganini
September 26, 2019
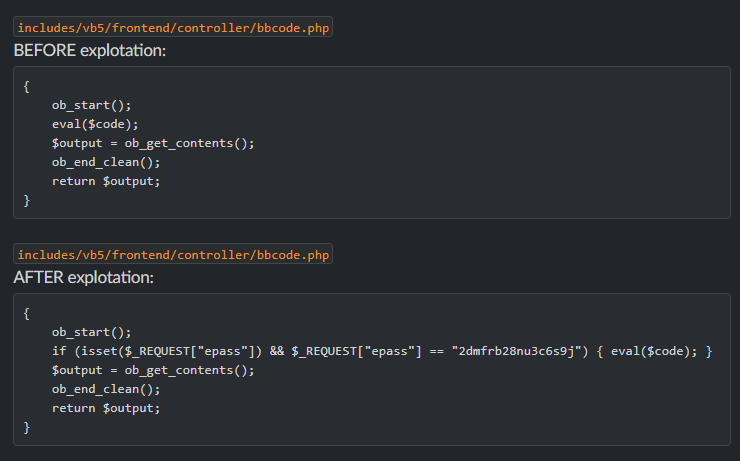
Security expert Troy Mursch of Bad Packets reported that a botnet is exploiting the recently disclosed vBulletin exploit to block other attackers from also using it. The security expert Troy Mursch observed a botnet that it utilizing the recently disclosed vBulletin exploit to secure vulnerable servers to avoid that can be compromised by other threat actors. […]