 Pierluigi Paganini
 November 30, 2021
A threat actor named WIRTE targets government, diplomatic entities, military organizations, law firms, and financial institutions in Middle East. Cybersecurity researchers from Kaspersky have detailed the activity of a threat actor named WIRTE that is targeting government, diplomatic entities, military organizations, law firms, and financial institutions in Middle East since early 2019. The activity of […]
 Pierluigi Paganini
November 28, 2021
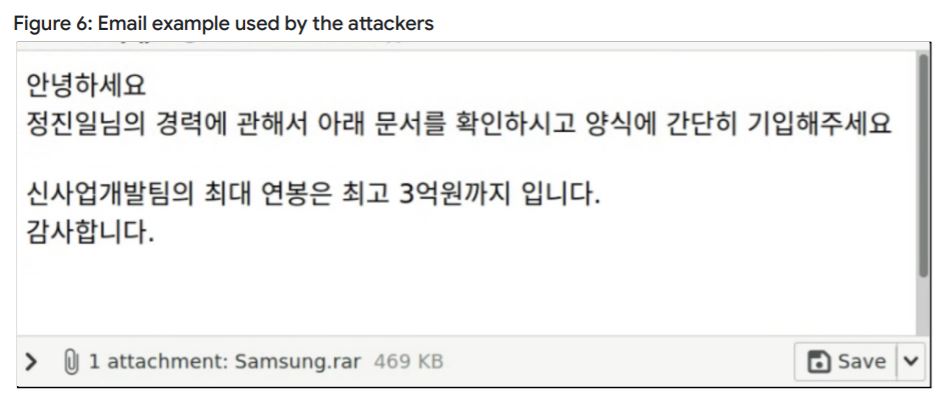
North Korea-linked threat actors posed as Samsung recruiters in a spear-phishing campaign aimed at employees at South Korean security firms. North Korea-linked APT group posed as Samsung recruiters is a spear-phishing campaign that targeted South Korean security companies that sell anti-malware solutions, Google TAG researchers reported. According to the Google Threat Horizons report, the state-sponsored […]
 Pierluigi Paganini
November 26, 2021
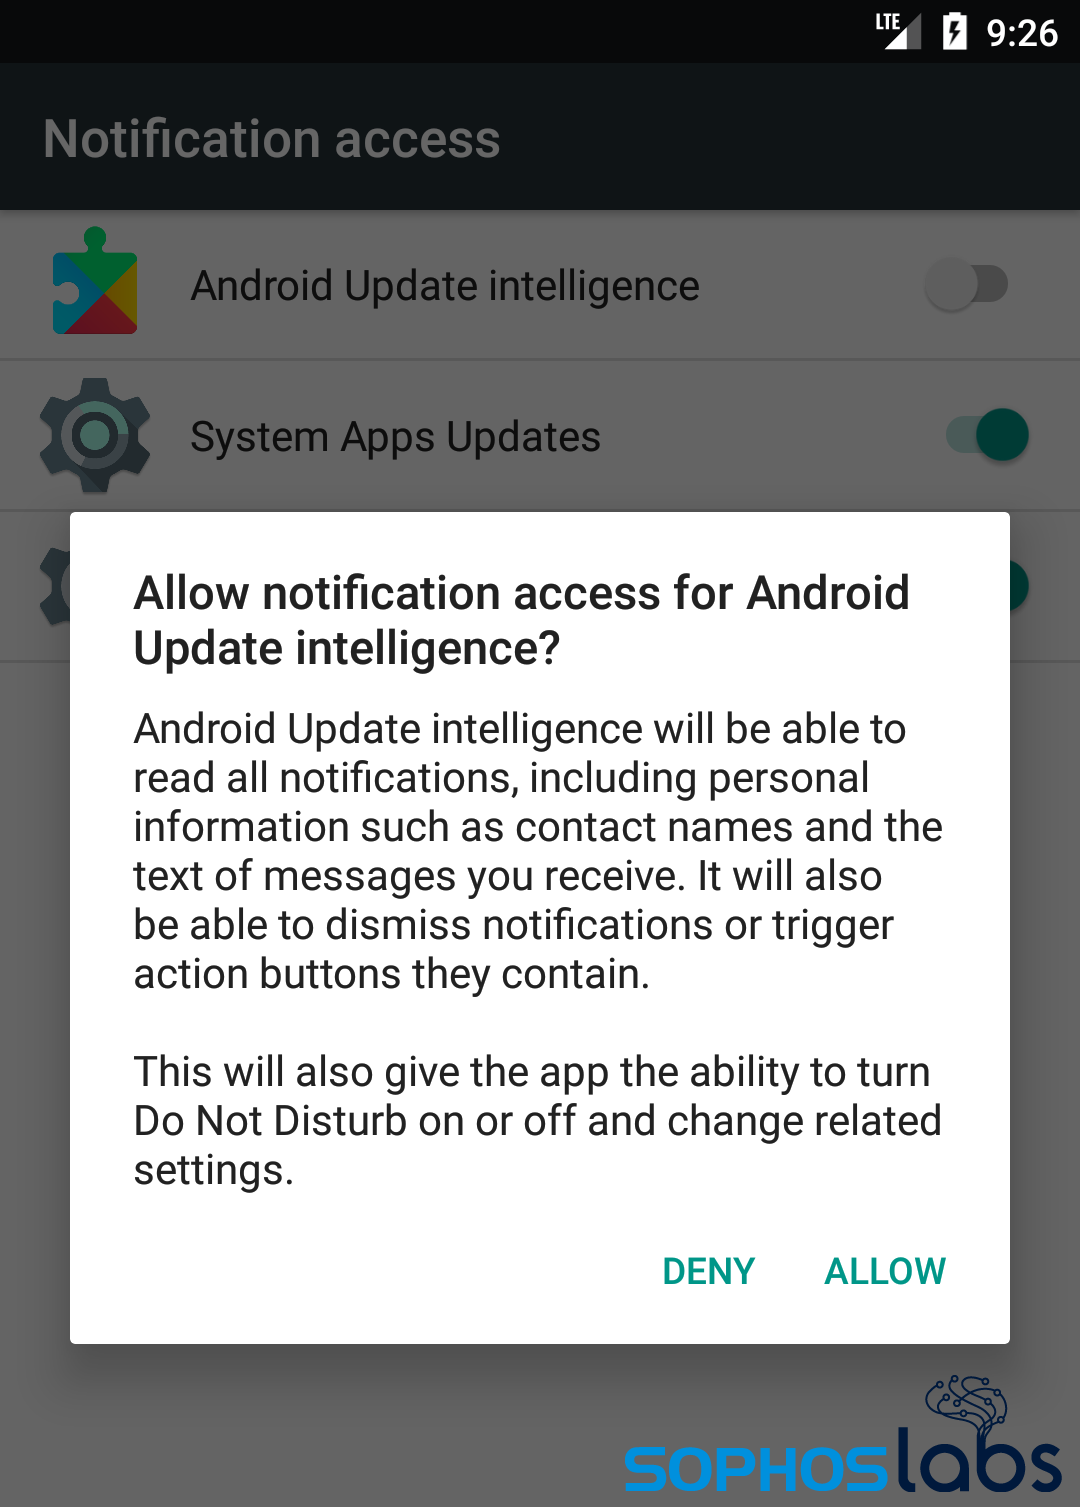
A threat actor, tracked as APT C-23, is using new powerful Android spyware in attacks aimed at targets in the Middle East. The APT C-23 cyberespionage group (also known as GnatSpy, FrozenCell, or VAMP) continues to target entities in the Middle East with enhanced Android spyware masqueraded as seemingly harmless app updates (i.e. AndroidUpdate,, Telegram). The […]
 Pierluigi Paganini
November 17, 2021
The researchers at Microsoft Threat Intelligence Center (MSTIC) are warning of increasingly sophisticated operations carried out by Iranian threat actors. The Microsoft Threat Intelligence Center (MSTIC) shared the results of their analysis on the evolution of Iran-linked threat actors at the CyberWarCon 2021. Over the past 12 months, MSTIC experts observed increasingly sophisticated attacks orchestrated […]
 Pierluigi Paganini
November 15, 2021
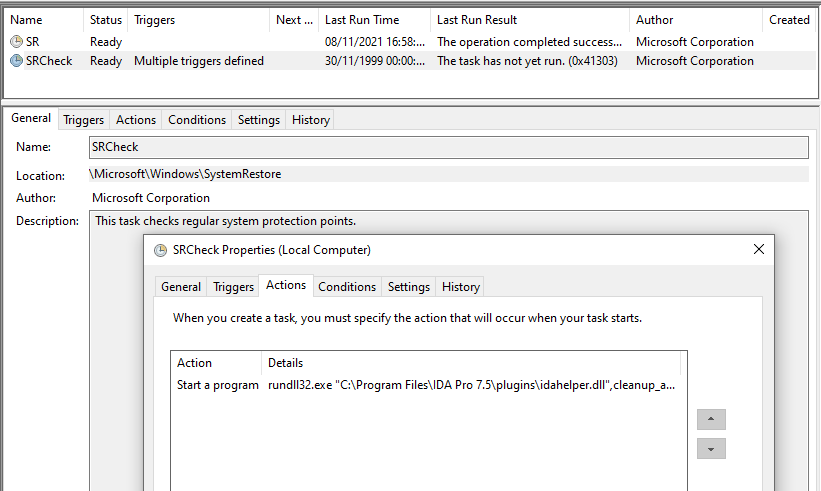
North Korea-linked APT Lazarus targets security researchers using a trojanized pirated version of the popular IDA Pro reverse engineering software. ESET researchers reported that the North Korea-linked Lazarus APT group is targeting cyber security community with a trojanized pirated version of the popular IDA Pro reverse engineering software. Threat actors bundled the IDA Pro 7.5 […]
 Pierluigi Paganini
November 05, 2021
Ukraine’s premier law enforcement and counterintelligence revealed the real identities of five FSB members behind the Gamaredon cyberespionage group. Ukraine’s premier law enforcement and counterintelligence disclosed the real identities of five alleged members of the Russia-linked APT group Gamaredon (aka Primitive Bear, Armageddon, Winterflounder, or Iron Tilden) that are suspected to be components of the […]
 Pierluigi Paganini
November 01, 2021
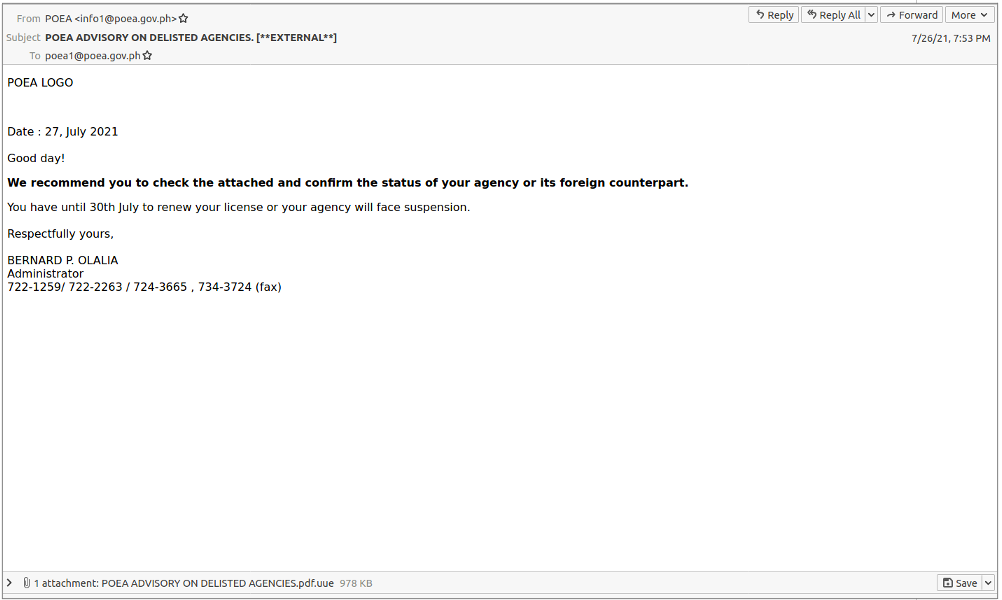
Meet Balikbayan Foxes: a threat group impersonating the Philippine gov’t Experts uncovered a new threat actor, tracked as Balikbayan Foxes, that is impersonating the Philippine government to spread malware. Researchers from Proofpoint have uncovered a new threat actor, dubbed Balikbayan Foxes (TA2722) that is impersonating the Philippine health, labor, and customs organizations as well as […]
 Pierluigi Paganini
October 27, 2021
North Korea-linked Lazarus APT group is extending its operations and started targeting the IT supply chain on new targets. North Korea-linked Lazarus APT group is now targeting also IT supply chain, researchers from Kaspersky Lab warns. The activity of the Lazarus APT group surged in 2014 and 2015, its members used mostly custom-tailored malware in their attacks. […]
 Pierluigi Paganini
October 11, 2021
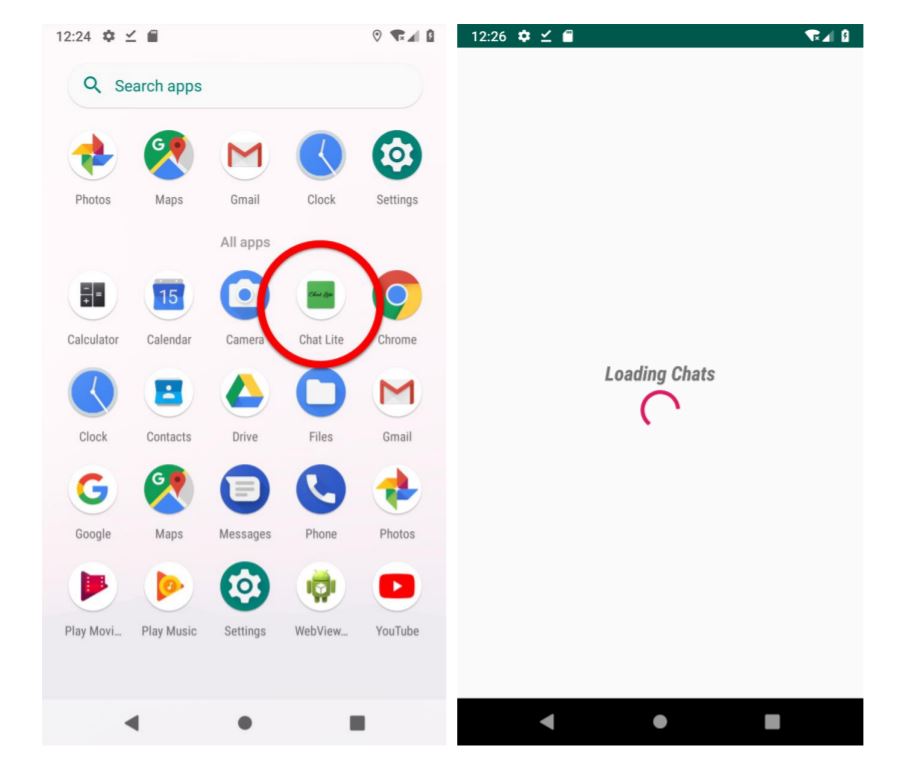
Donot Team targeted a Togolese human rights advocate with a mobile spyware that has been allegedly developed by an Indian firm. Researchers from Amnesty International have uncovered a cyberespionage campaign tracked as ‘Donot Team‘ (aka APT-C-35), which was orchestrated by threat actors in India and Pakistan. Experts believe the attackers used a spyware developed by […]
 Pierluigi Paganini
October 10, 2021
A new round of the weekly Security Affairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the international press subscribe here. Previously undetected FontOnLake Linux malware used in targeted attacks Google addresses four high-severity flaws in Chrome Security […]