 Pierluigi Paganini
 April 10, 2019
Palo Alto Networks researchers discovered a new variant of the Mirai malware that is targeting more processor architectures than previous ones. Mirai botnet continues to be one of the most dangerous malware in the threat landscape, experts at Palo Alto Networks discovered a new variant that targets more processor architectures than before. Mirai malware first […]
 Pierluigi Paganini
March 19, 2019
PaloAlto Networks researchers discovered a new variant of the infamous Mirai botnet is targeting IoT devices belonging to businesses. Researchers at PaloAlto Networks spotted a new variant of the infamous Mirai botnet is targeting IoT devices belonging to businesses. Mirai malware first appeared in the wild in 2016 when the expert MalwareMustDie discovered it in massive attacks […]
 Pierluigi Paganini
February 24, 2019
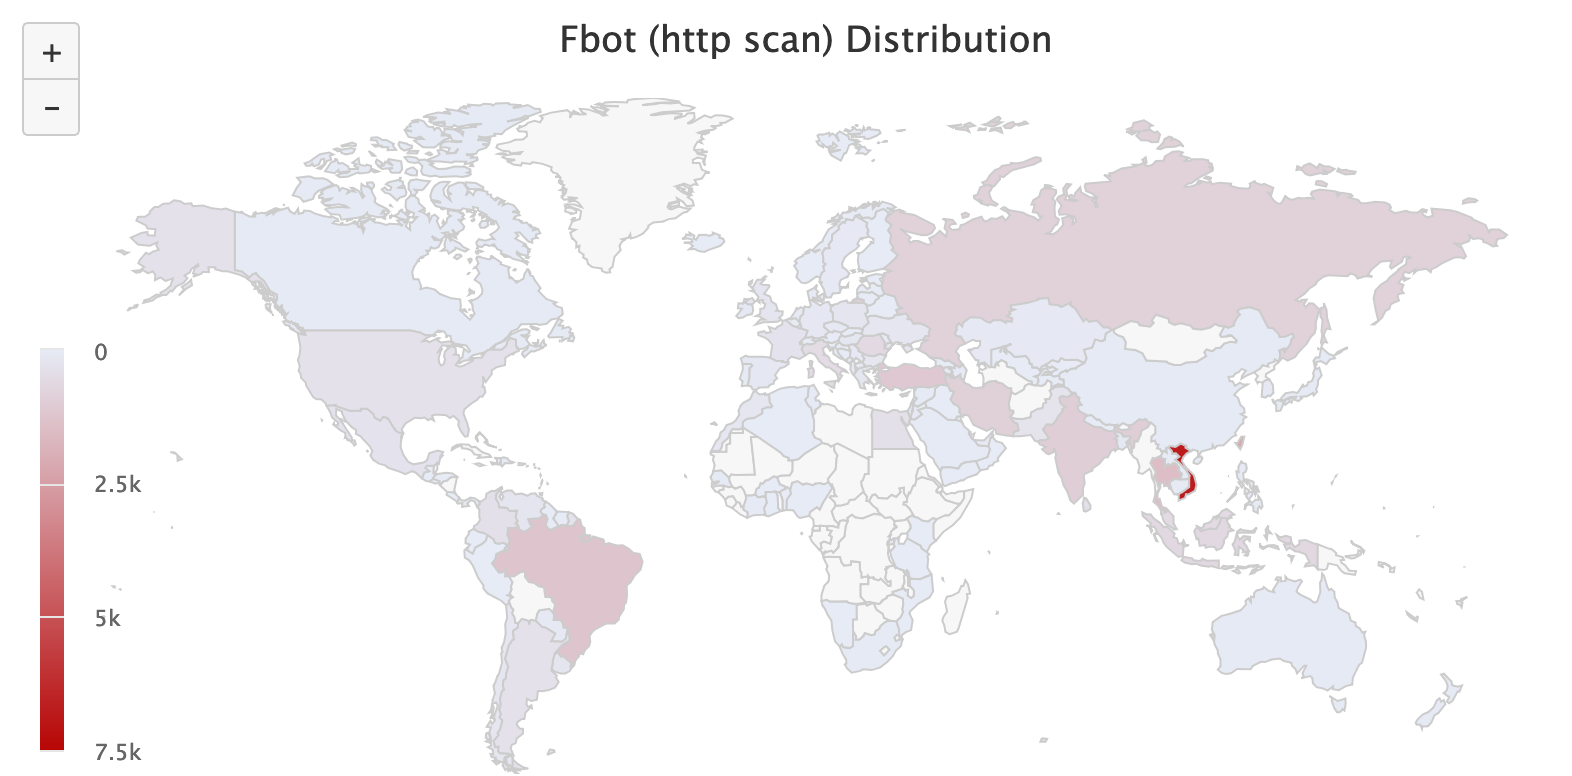
Experts at 360Netlab observed the Fbot bot infecting a large number of HiSilicon DVR/NVR Soc devices. Since February 16, 2019, security experts at 360Netlab observed a large number of HiSilicon DVR/NVR Soc devices were infected with an updated version of the Fbot bot. The Fbot malware was first discovered by 360Netlab researchers, according to the […]
 Pierluigi Paganini
January 11, 2019
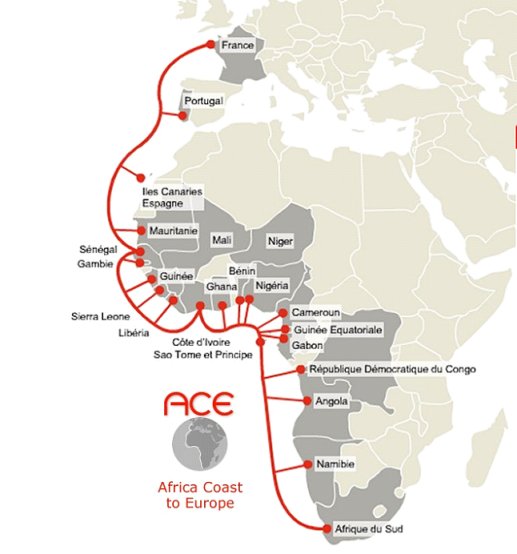
The British hacker Daniel Kaye has been sentenced to 32 months in prison for the cyberattack on Liberian telecom firms. The British hacker Daniel Kaye (29) has been sentenced to 32 months in prison for the 2016 attack that took down telecommunications services in Liberia. Kaye pleaded guilty in December to two charges under the Computer Misuse […]
 Pierluigi Paganini
December 21, 2018
2018 was the year of the Internet of Things (IoT), massive attacks and various botnets hit smart devices, These are 5 IoT Security Predictions for 2019 Insights from VDOO’s leadership 2018 was the year of the Internet of Things (IoT) – massive attacks and various botnets, a leap in regulation and standards, and increased adoption […]
 Pierluigi Paganini
December 09, 2018
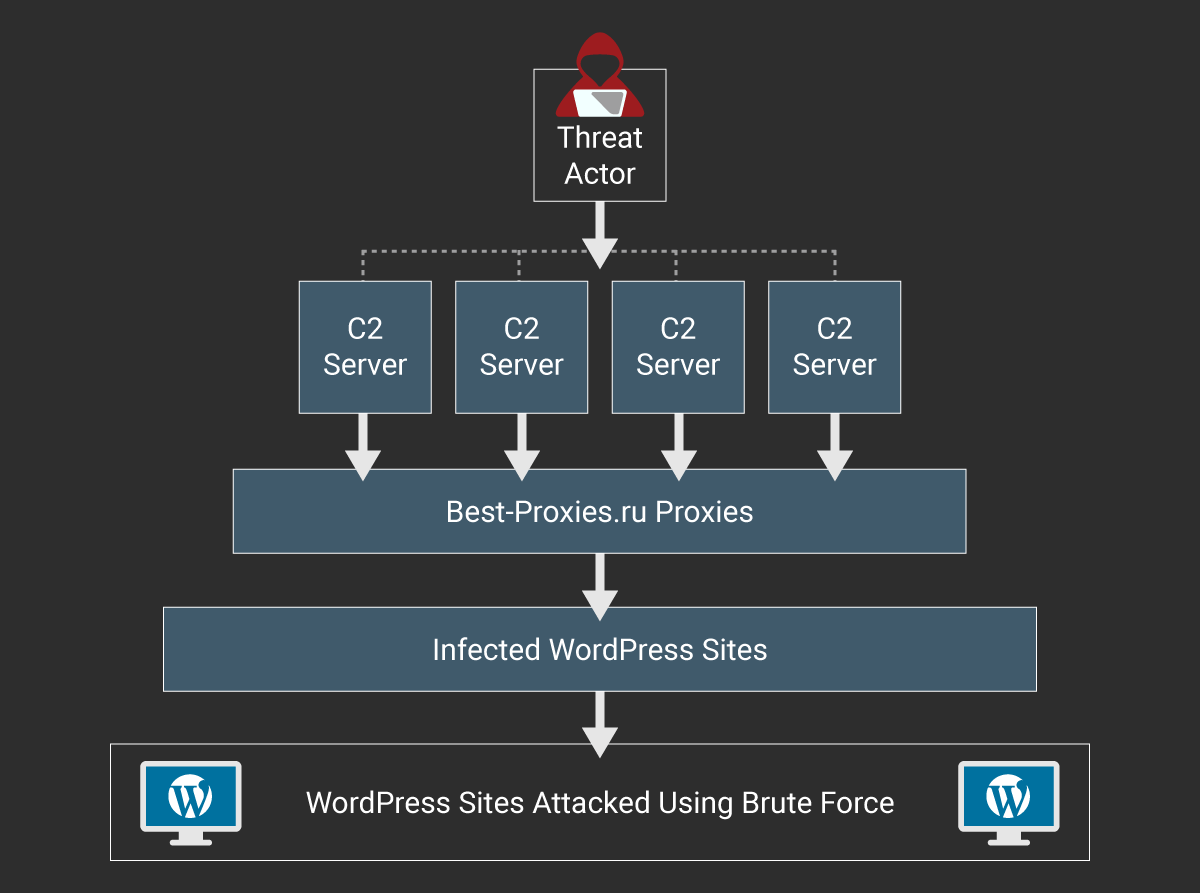
Experts from security firm Wordfence discovered a Botnet of 20,000 WordPress Sites Infecting other WordPress installs. Experts from security firm Wordfence uncovered a botnet composed of over 20,000 WordPress sites that is being used to compromise other websites running on the popular CMS and recruit them. “The threat actors (hackers) use a group of four command […]
 Pierluigi Paganini
December 01, 2018
Over 270,000 connected devices run vulnerable implementations of UPnP, threat actors are attempting to recruit them in a multi-purpose botnet. In April, Akamai reported that threat actors compromised 65,000 home routers by exploiting vulnerabilities in Universal Plug’N’Play (UPnP), experts tracked the botnet as UPnProxy. Now the company provided an update to its initial analysis revealing […]
 Pierluigi Paganini
November 22, 2018
Security experts from Netscout Asert discovered more than ten Mirai bot variants attempting to exploit a recently disclosed flaw in Hadoop YARN on Intel servers. These Mirai variants are the first one that doesn’t target Internet of Things devices, the bot was specifically developed to target Linux servers. The Hadoop YARN is vulnerability is a command injection […]
 Pierluigi Paganini
November 09, 2018
Security researchers at 360 Netlab have discovered a new spam botnet, dubbed BCMPUPnP_Hunter, that likely already infected around 400,000 machines to date. Security experts from 360 Netlab security firm have recently discovered a new spam botnet, dubbed BCMPUPnP_Hunter, that mainly targets routers that have the BroadCom UPnP feature enabled. The BCMPUPnP_Hunter was first spotted in September, but researchers […]
 Pierluigi Paganini
November 06, 2018
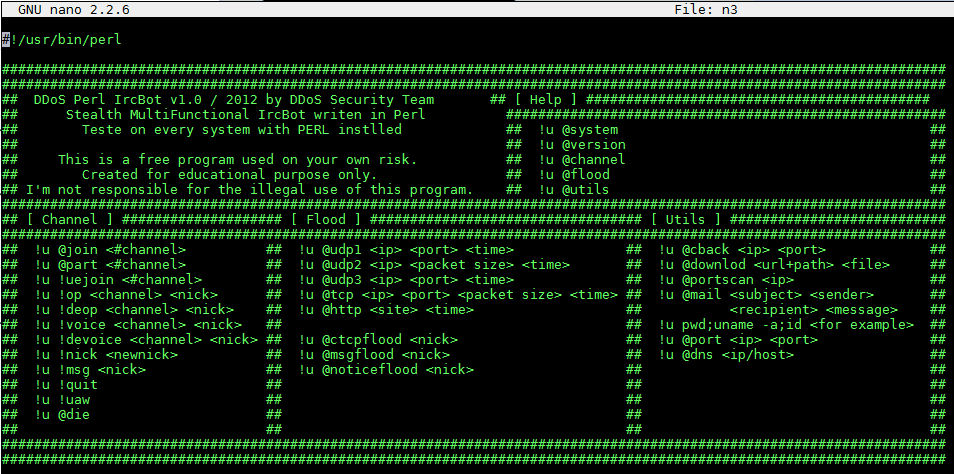
Security experts at Trend Micro have spotted an IRC bot dubbed Shellbot that was built using Perl Shellbot. The malware was distributed by a threat group called Outlaw, it was able to target Linux and Android devices, and also Windows systems. “We uncovered an operation of a hacking group, which we’re naming “Outlaw” (translation derived from the Romanian word haiduc, […]

Hacking / October 29, 2026