 Pierluigi Paganini
 September 21, 2026
Ireland’s DPC fined Google €403 million over GDPR violations involving location data, transparency, retention and user control. Ireland’s Data Protection Commission (DPC) just fined Google €403 million, and the case behind it goes back six years, to a set of complaints that never really went away. The DPC launched the investigation in February 2020 after […]
 Pierluigi Paganini
September 21, 2026
Hackers targeted two Colorado water utilities, changing OT settings and disabling alarms, but causing no impact on water services or safety. Foreign hackers targeted the operational technology (OT) systems of two small private water utilities in Colorado in late August, apparently trying to disrupt operations. Local authorities haven’t identified the affected utilities or the attackers. […]
 Pierluigi Paganini
September 21, 2026
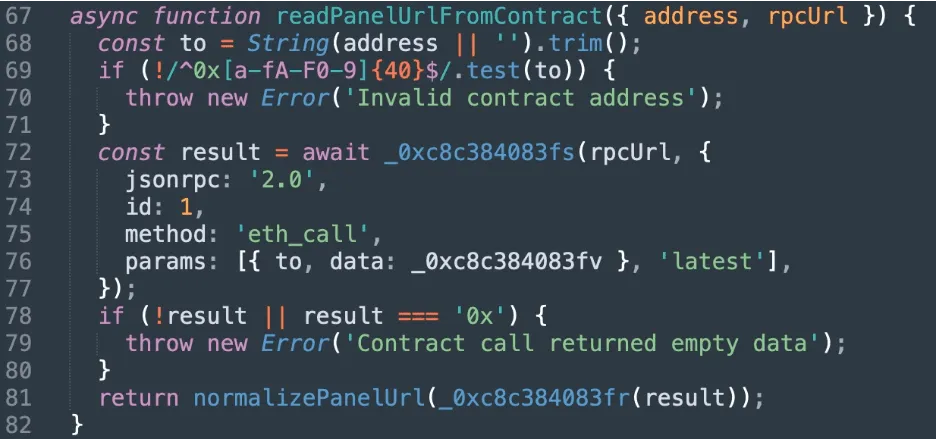
Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint’s Adversary Pursuit Group was chasing a ClickFix campaign spreading an unknown RAT namend ChainScript. The malicious code is a previously undocumented Node.js remote access trojan that hides its command server on a public blockchain. The […]
 Pierluigi Paganini
September 21, 2026
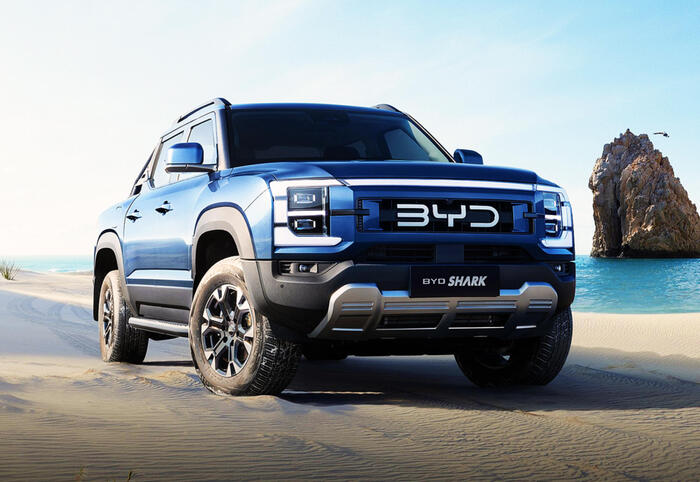
A BYD Shark 6 was remotely hacked, exposing vehicle controls, location tracking and cabin audio, raising serious connected-car security concerns. A journalist drove a BYD Shark 6 down a country road outside Canberra while a hacker sitting on the shoulder killed the headlights with a keystroke. That’s not a hypothetical. It’s what happened during a […]
 Pierluigi Paganini
September 21, 2026
AI agents are becoming the new attack surface, exposed to poisoned skills, prompt injection, jailbreaks and attacks through connected tools. I read the AI security research published in a single month, February 2026, and when you put it all together, it’s not a list of curiosities. It’s a field guide to a new attack surface. […]
 Pierluigi Paganini
September 21, 2026
A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist. A Guardian investigation has surfaced a 2017 document signed off by then City of London police commissioner Ian Dyson, who also held the title of senior information risk owner for the entire country. That […]
 Pierluigi Paganini
September 20, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [1, 2] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Below are detailed descriptions of the flaws: At the time of this writing, there are currently no details on how the […]
 Pierluigi Paganini
September 20, 2026
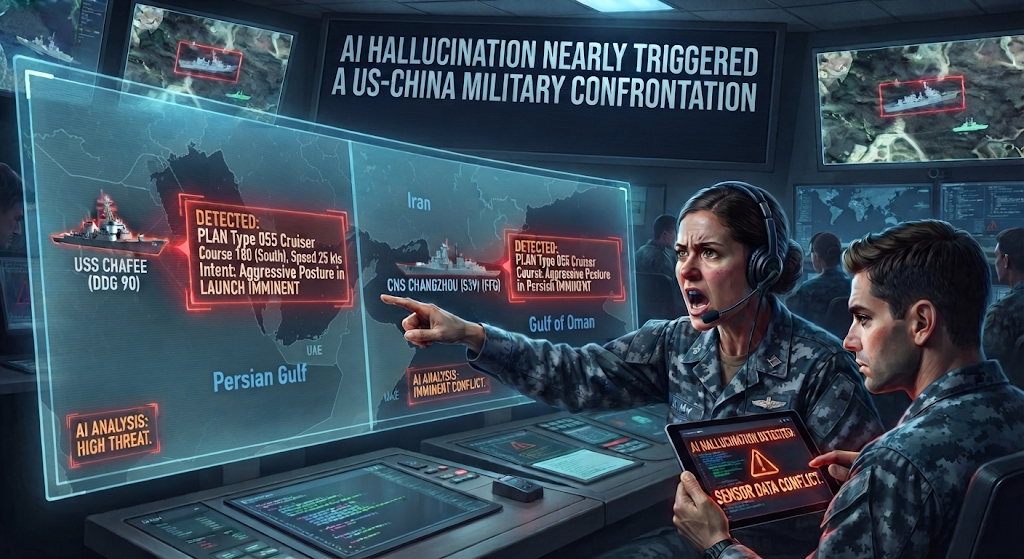
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The […]
 Pierluigi Paganini
September 20, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gray Rabbits and the Tale of a One-Click Backdoor Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot […]
 Pierluigi Paganini
September 20, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Google Gemini also Broke Out of Its Test Environment AI Helps Hackers Hijack OpenAI Staff Accounts Through […]