


 Pierluigi Paganini
 August 21, 2026
GitLab flaw CVE-2026-19478 is now under active exploitation, allowing unauthenticated attackers to modify or delete public projects. WatchTowr researchers warn of active exploitation of critical GitLab flaw CVE-2026-19478 (CVSS score of 9.4). This week, GitLab pushed out an emergency patch to address this flaw, which could let an attacker with zero credentials remotely modify or […]
 Pierluigi Paganini
August 21, 2026
CERT Polska confirmed active exploitation of CVE-2026-73570, a critical unauthenticated RCE in Zimbra Collaboration Suite patched on July 20. CERT Polska, Poland’s national computer emergency response team, confirmed this week that threat actors are actively exploiting a critical vulnerability in Zimbra Collaboration Suite tracked as CVE-2026-73570. The flaw allows unauthenticated remote code execution and was […]
 Pierluigi Paganini
August 21, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds TrueConf Server flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: TrueConf Server is an on-premises video conferencing and unified communications platform developed by TrueConf. Organizations can deploy it on their […]
 Pierluigi Paganini
August 21, 2026
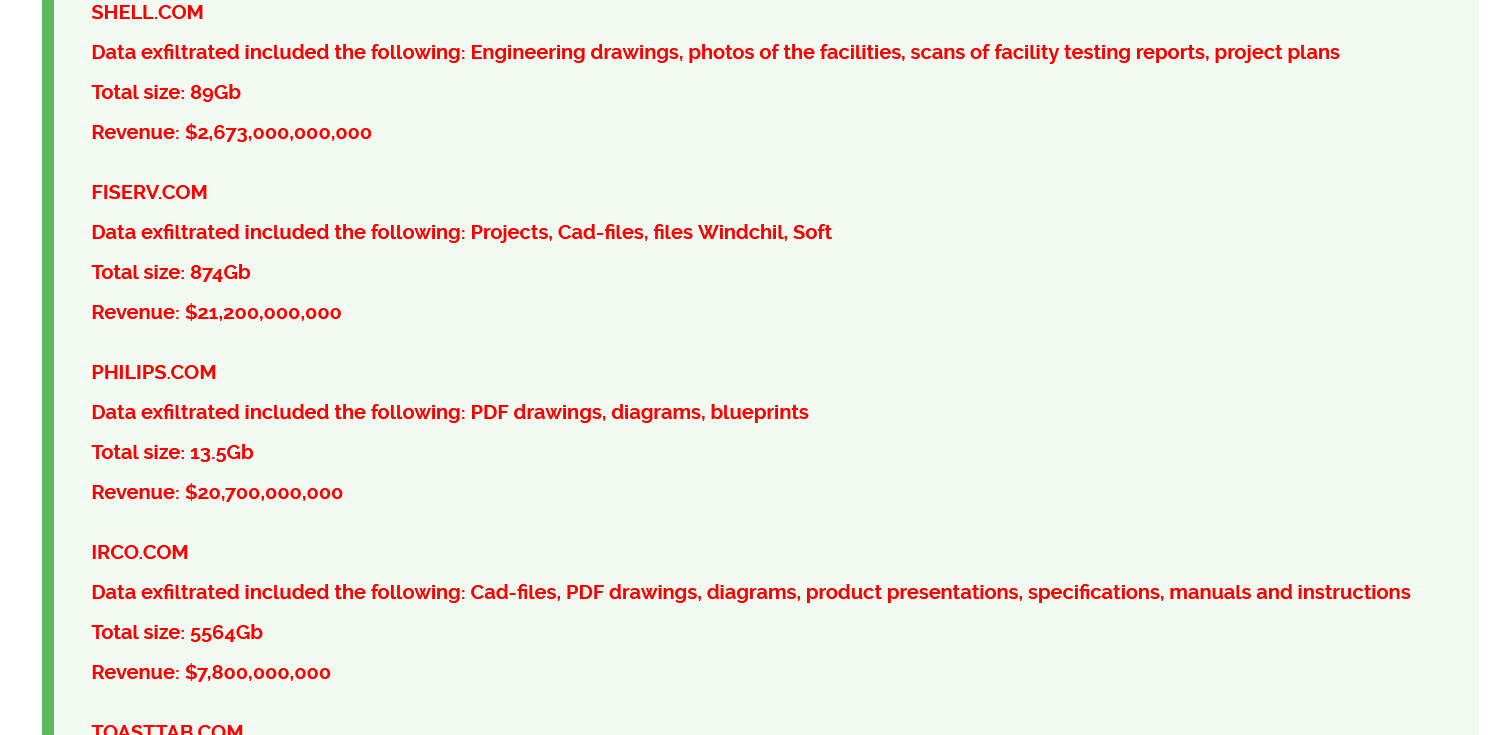
Cl0p claims over 40 organizations fell victim to attacks exploiting a PTC Windchill and FlexPLM vulnerability. Cl0p is using a familiar strategy again: exploit one flaw in enterprise software to attack many companies, then publish the victims’ names if they refuse to pay. The group claims it has targeted more than 40 organizations through a […]
 Pierluigi Paganini
August 20, 2026
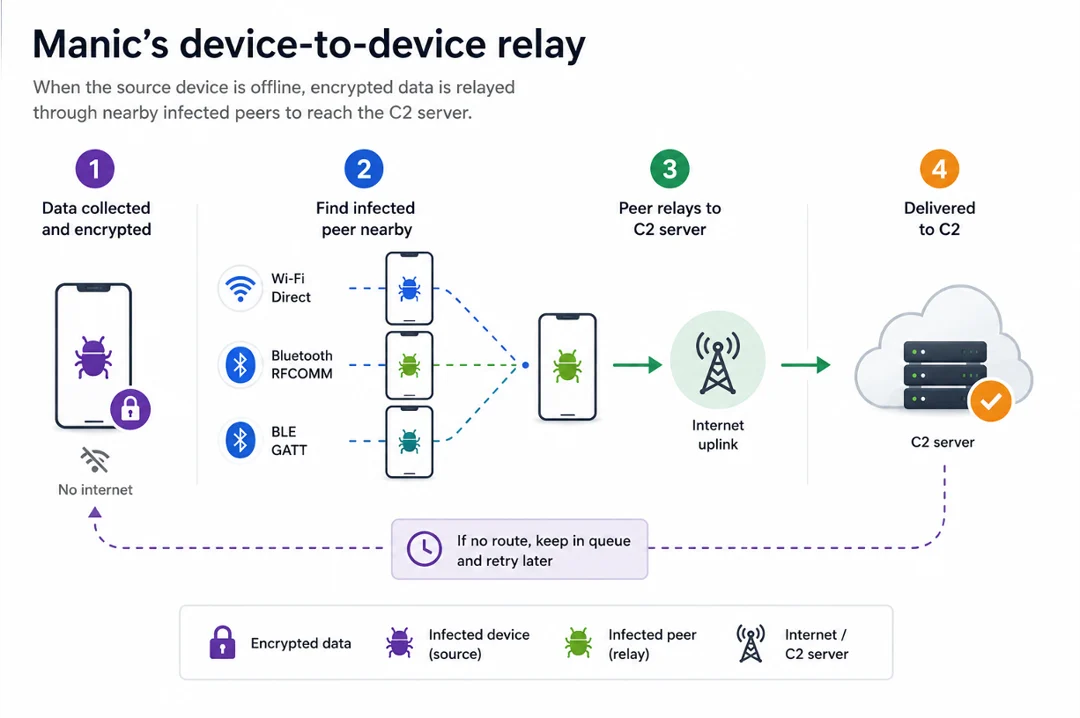
Manic Android malware combines banking fraud and spyware, using a Bluetooth relay to steal data even when devices are offline. ThreatFabric’s Mobile Threat Intelligence team has identified a new Android malware, dubbed Manic, which has been active in the wild since at least February 2026. The researchers state that the malware is still under development […]
 Pierluigi Paganini
August 20, 2026
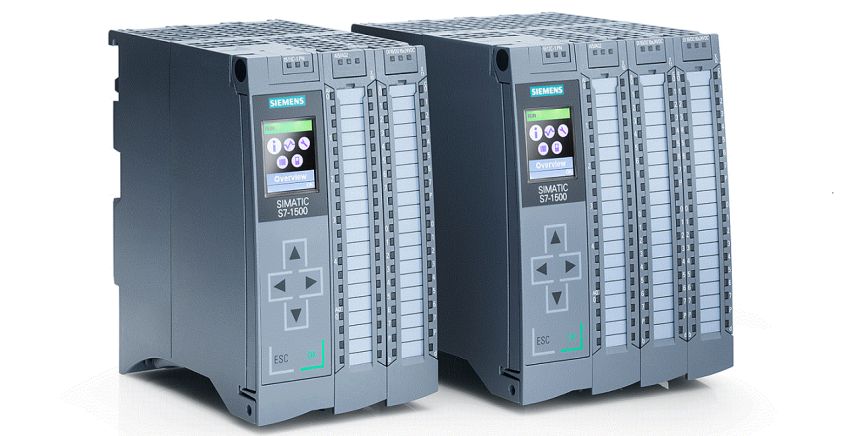
NSA, CISA, FBI, DOE, and EPA warn of active AI-assisted attacks against Siemens S7 PLCs across US critical infrastructure sectors. Five U.S. federal agencies issued a joint advisory this week warning of an active hacking campaign against Siemens S7 Series programmable logic controllers. The advisory, CISA AA26-231A, is co-signed by NSA, FBI, DOE, and EPA […]
Pierluigi Paganini
August 20, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds an MLflow vulnerability to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Progress LoadMaster vulnerability, tracked as CVE-2026-64849 (CVSS score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-64849 is a critical server-side request forgery (SSRF) vulnerability in MLflow, a […]
 Pierluigi Paganini
August 20, 2026
The US charged 17 Iranians over a years-long hacking campaign that stole 31TB from universities, companies and government agencies worldwide. Eight years after the original indictment first went public, US prosecutors just added eight more names to the list. The Justice Department unsealed a superseding indictment this week charging 17 members of the Mabna Institute, […]
 Pierluigi Paganini
August 20, 2026
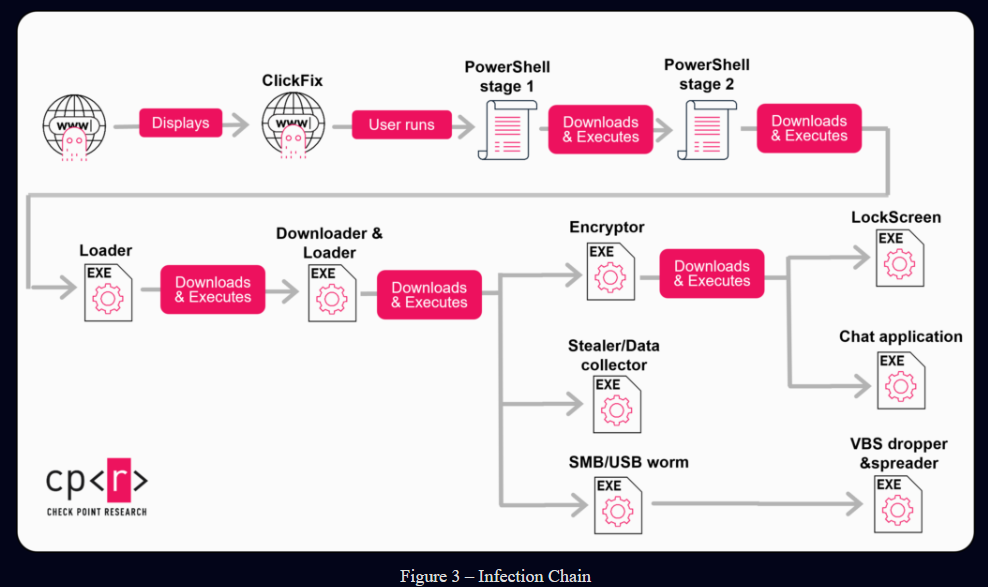
StopAndProtect turned nearly 2,000 hacked WordPress sites into a criminal network for malware delivery, data theft, surveillance and ransomware. Check Point Research uncovered a cybercrime operation, dubbed StopAndProtect, that has turned thousands of hacked WordPress websites into a shared platform for malware delivery, data theft, surveillance and ransomware. The operation is a good reminder that […]
 Pierluigi Paganini
August 19, 2026
An exposed operator directory reveals how one actor compromised 14,000+ Dahua cameras across Ukraine and Russia, no password needed for most. A researcher discovered an exposed directory containing the tools of an attacker who compromised more than 14,000 Dahua cameras between June 17 and July 22, 2026, mainly in Ukraine and Russia. Hunt.io reconstructed the […]

Security / September 18, 2026

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026




