 Pierluigi Paganini
 May 30, 2018
The Department of Homeland Security (DHS) and the FBI issued a joint Technical alert on two strain on malware, the Joanap backdoor Trojan and Brambul Server Message Block worm, associated with the HIDDEN COBRA North Korea-linked APT group. The US-CERT alert reads: “Working with U.S. government partners, DHS and FBI identified Internet Protocol (IP) addresses and other indicators […]
 Pierluigi Paganini
May 30, 2018
Researchers at IBM X-Force Research team discovered a new Delphi-based banking Trojan dubbed MnuBot that leverages Microsoft SQL Server for communication with the command and control (C&C). The MnuBot Trojan implements a two-stage attack flow, it is composed of two main components that are tasked for the two stages. In the first stage, the malware searches for a file […]
 Pierluigi Paganini
May 29, 2018
Group-IB has released a new report on Cobalt group’s attacks against banks and financial sector organizations worldwide after the arrest of its leader. Threat intelligence firm Group-IB published an interesting report titiled “Cobalt: Evolution and Joint Operations” on the joint operations of Cobalt and Anunak (Carbanak) groups after the arrest of the leader in March 2018. Researchers reported that […]
 Pierluigi Paganini
May 28, 2018
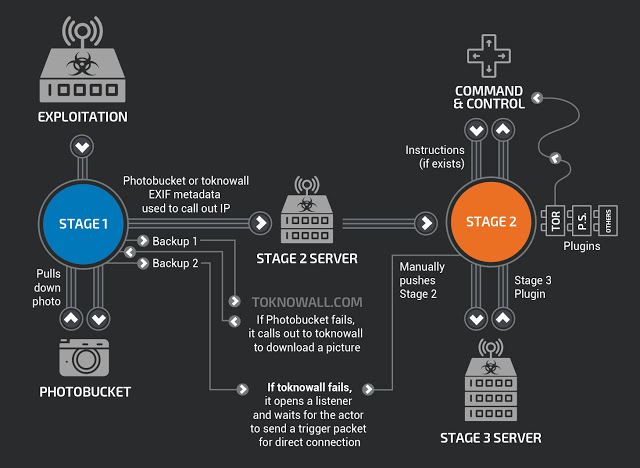
Researchers and the FBI are working together to take down the dreaded VPNFilter botnet composed of hundreds of thousands of compromised devices. For several months, there have been rumors and vague warnings about highly skilled adversaries targeting critical infrastructure. Last week we learned some details about the warning, why you might be impacted and how […]
 Pierluigi Paganini
May 28, 2018
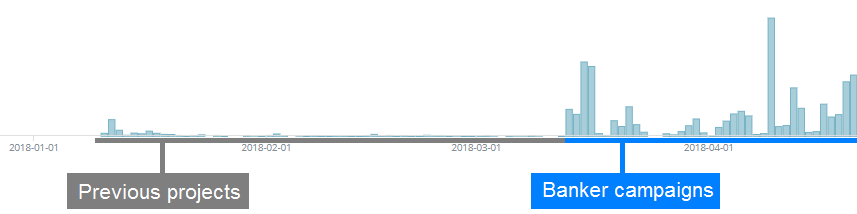
Security experts at ESET have spotted a new strain of banking trojan named BackSwap Trojan that implements new techniques to steal money from bank customers. The new techniques allow the malware to bypass anti-malware solutions and security features implemented by browsers to prevent Man-In-The-Browser attacks. Banking malware use to inject malicious code into the web page, […]
 Pierluigi Paganini
May 28, 2018
The cybersecurity experts Marco Ramilli analyzed a new sample of malware dubbed MalHide that implements a quite new attack path to use the compromised system as eMail relay in order to hide the attacker networks. Today I’d like to share an interesting (at least to me) analysis on a given sample. I have called this sample MalHide but […]
 Pierluigi Paganini
May 28, 2018
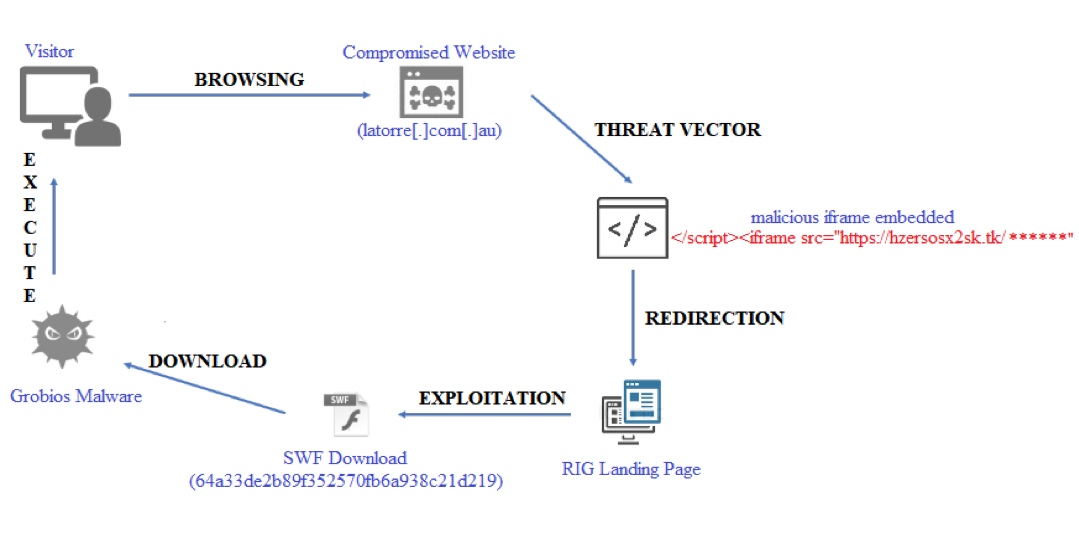
Malware researchers from FireEye recently noticed an interesting ongoing activity involving the infamous RIG Exploit Kit (EK) to deliver the Grobios Trojan. Security experts highlighted several times the decline of the exploit kit activity after the disappearance of the Angler and Nuclear exploit kits in 2016. Anyway, researchers at FireEye periodically observe significant developments in this […]
 Pierluigi Paganini
May 26, 2018
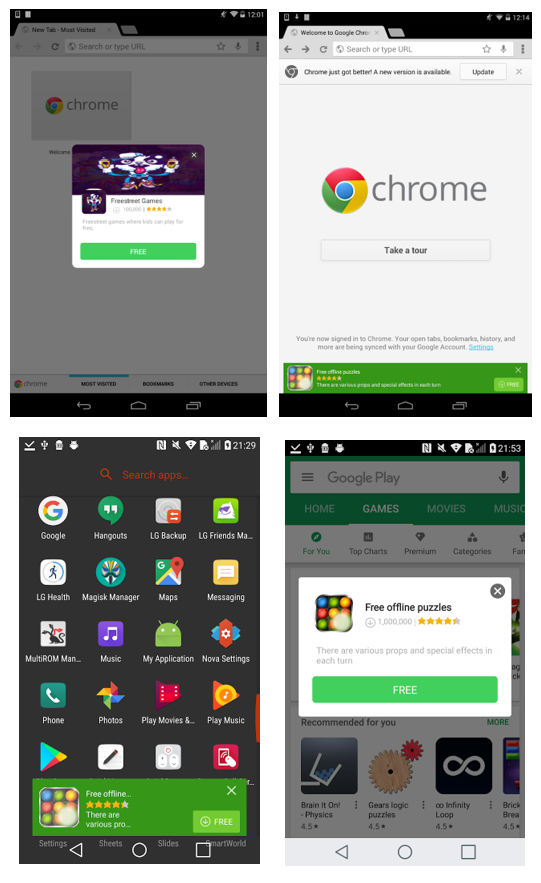
Researchers from Avast the antivirus firm are investigating the discovery of pre-installed malware found in 141 low-cost Android devices in over 90 countries. Security experts from Antivirus firm Avast have discovered a new case of pre-installed malware on low-cost Android devices, crooks injected the malicious code in the firmware of 141 models. The operation is […]
 Pierluigi Paganini
May 25, 2018
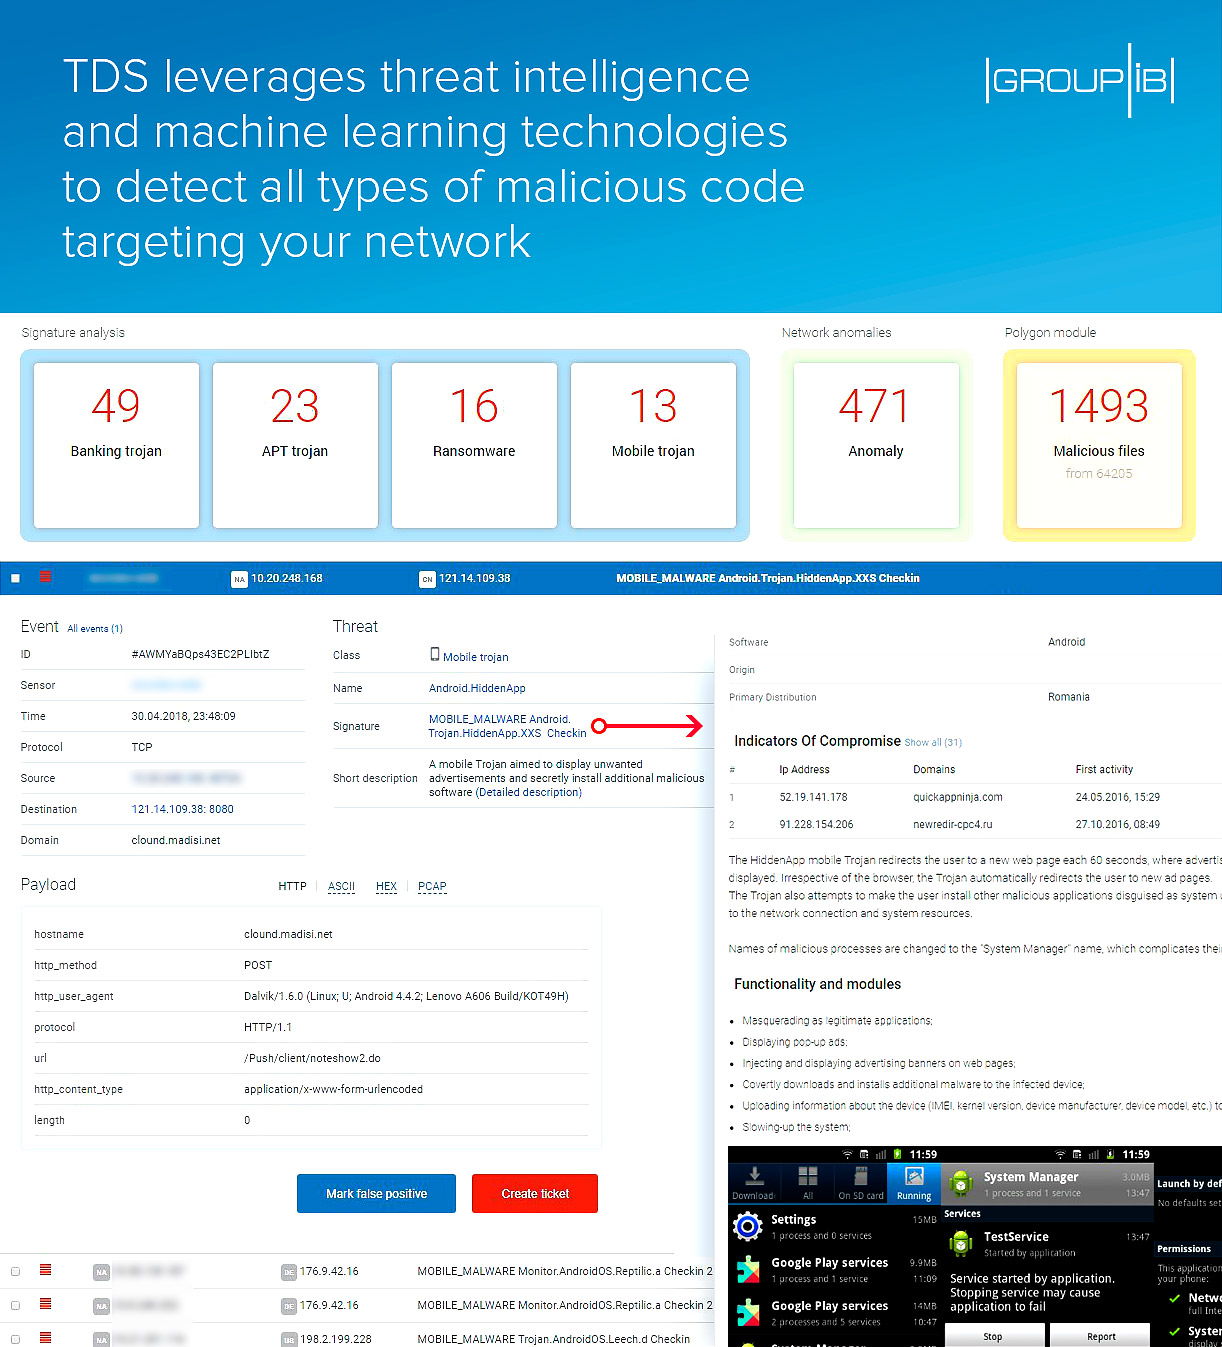
Moscow, May 24, 2018 – law enforcement, with support from Group-IB, has arrested a 32-year-old hacker, accused of stealing funds from Russian banks’ customers using Android mobile malware. At the height of their activity, victims reportedly lost between 1,500 to 8,000 dollars daily and levered cryptocurrency for laundering. Group-IB’s analysis reviewed the tools and techniques […]
 Pierluigi Paganini
May 24, 2018
In the past weeks, many Mac users have been infected with a new strain of Monero miner, the infections confirm the rise of this kind of malware. According to researchers at Malwarebytes, many Mac users in the past weeks have been infected with a new strain of Monero miner. The owners of the infected Mac systems […]