 Pierluigi Paganini
 February 24, 2021
Ukraine ‘s government attributes a cyberattack on the government document management system to a Russia-linked APT group. The Ukraine ‘s government blames a Russia-linked APT group for an attack on a government document management system, the System of Electronic Interaction of Executive Bodies (SEI EB). According to Ukrainian officials, the hackers aimed at disseminating malicious […]
 Pierluigi Paganini
February 17, 2021
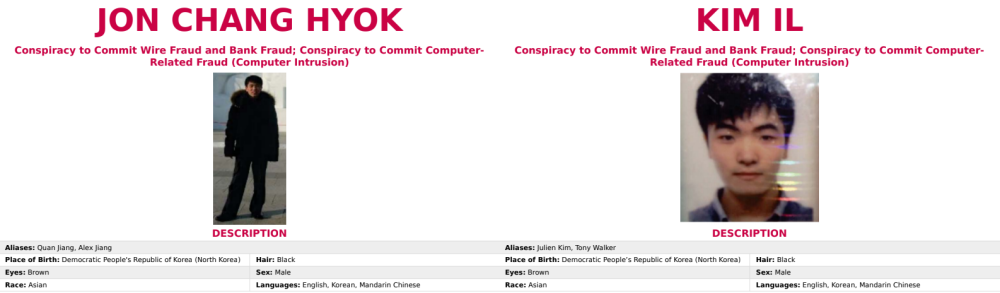
The US DOJ charged three members of the North Korea-linked Lazarus Advanced Persistent Threat (APT) group. The U.S. Justice Department indicted three North Korean military intelligence officials, members of the Lazarus APT group, for their involvement in cyber-attacks, including the theft of $1.3 billion in money and crypto-currency from organizations around the globe. The indictment […]
 Pierluigi Paganini
February 16, 2021
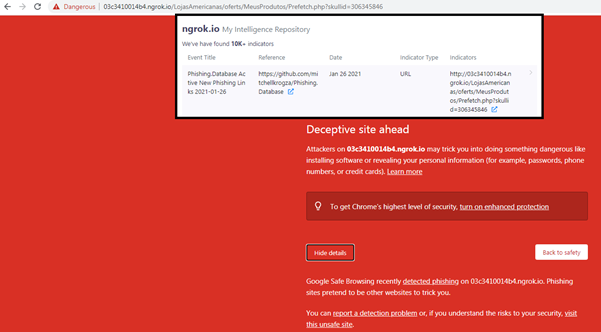
Researchers from threat intelligence Cyble have discovered threat actors abusing the Ngrok platform in a fresh phishing campaign. Researchers at the threat intelligence firm Cyble discovered a new wave of phishing attacks targeting multiple organizations that are abusing the ngrok platform, a secure and introspectable tunnel to the localhost. ngrok is a cross-platform application used to […]
 Pierluigi Paganini
February 15, 2021
French agency ANSSI attributes a series of attacks targeting Centreon servers to the Russia-linked Sandworm APT group. The French security agency ANSSI is warning of a series of attacks targeting Centreon monitoring software used by multiple French organizations and attributes them to the Russia-linked Sandworm APT group. The first attack spotted by ANSSI experts dates back […]
 Pierluigi Paganini
February 15, 2021
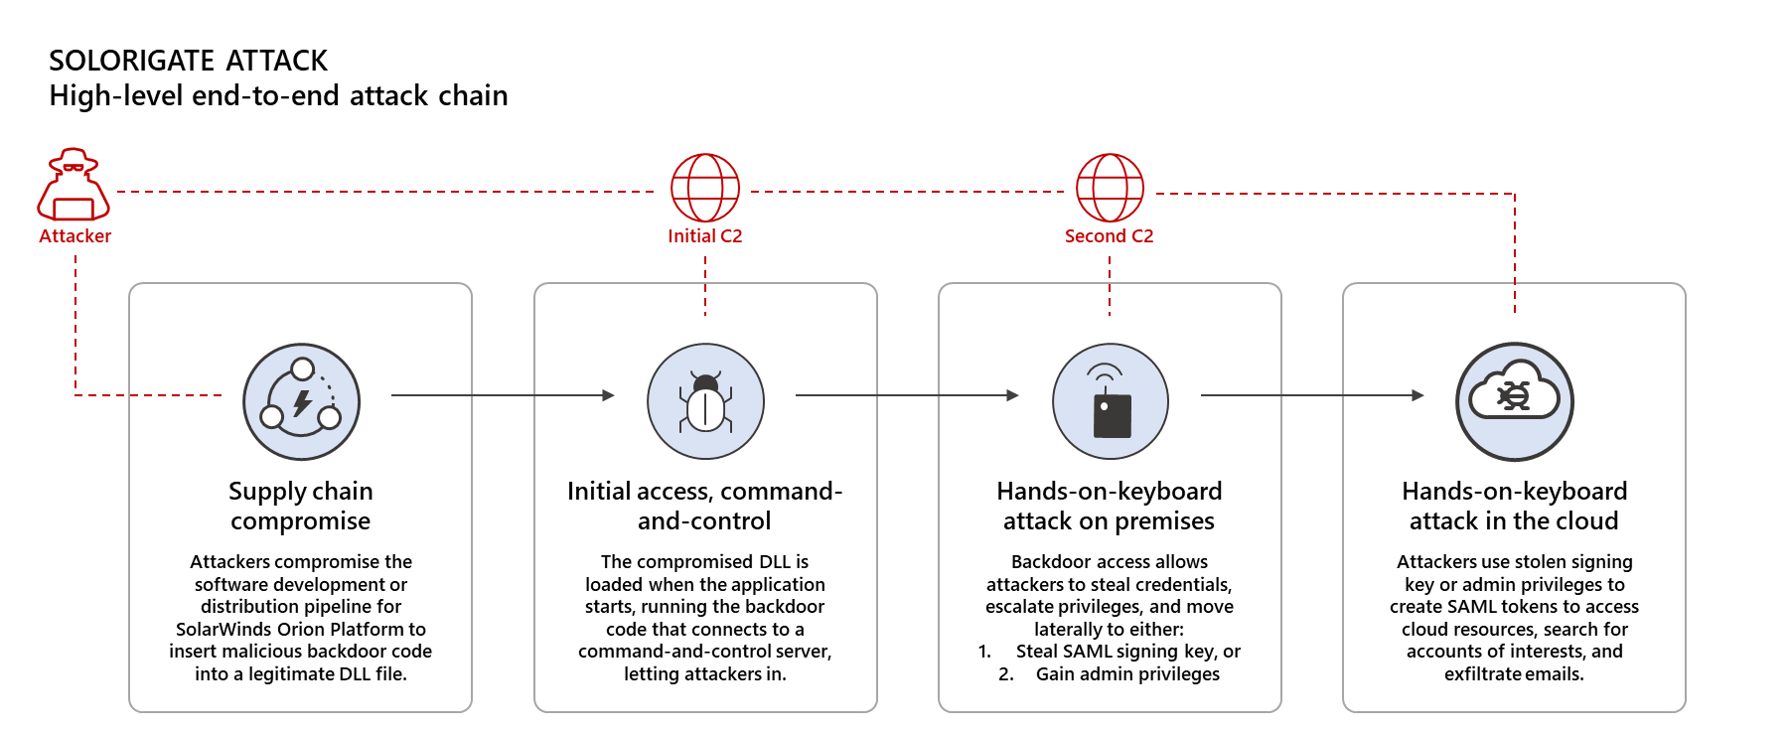
Microsoft says it found 1,000-plus developers’ fingerprints on the SolarWinds attack Microsoft’s analysis of the SolarWinds supply chain attack revealed that the code used by the threat actors was the work of a thousand developers. Microsoft president Brad Smith provided further details about the investigation of the SolarWinds supply chain attack, the company’s analysis of […]
 Pierluigi Paganini
February 08, 2021
Iran-linked APT group Domestic Kitten, also tracked as APT-C-50, has been conducting widespread surveillance targeting over 1,000 individuals. Domestic Kitten, also tracked as APT-C-50, is an Iran-linked APT group that has been active at least since 2018. In 2018, researchers at security firm CheckPoint uncovered an extensive surveillance operation conducted by Domestic Kitten aimed at […]
 Pierluigi Paganini
January 29, 2021
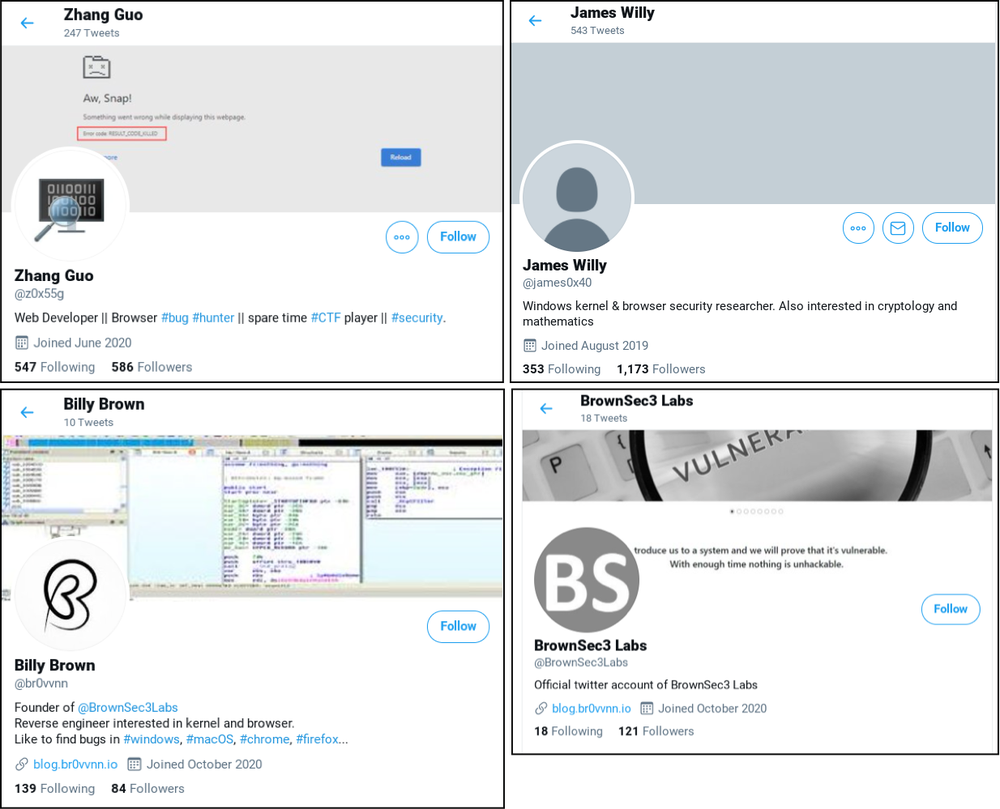
Microsoft, like Google TAG, observed a cyber espionage campaign aimed at vulnerability researchers that attributed to North Korea-linked Zinc APT group. Researchers from Microsoft monitored a cyber espionage campaign aimed at vulnerability researchers and attributed the attacks to North Korea-linked Zinc APT group. “In recent months, Microsoft has detected cyberattacks targeting security researchers by an […]
 Pierluigi Paganini
January 28, 2021
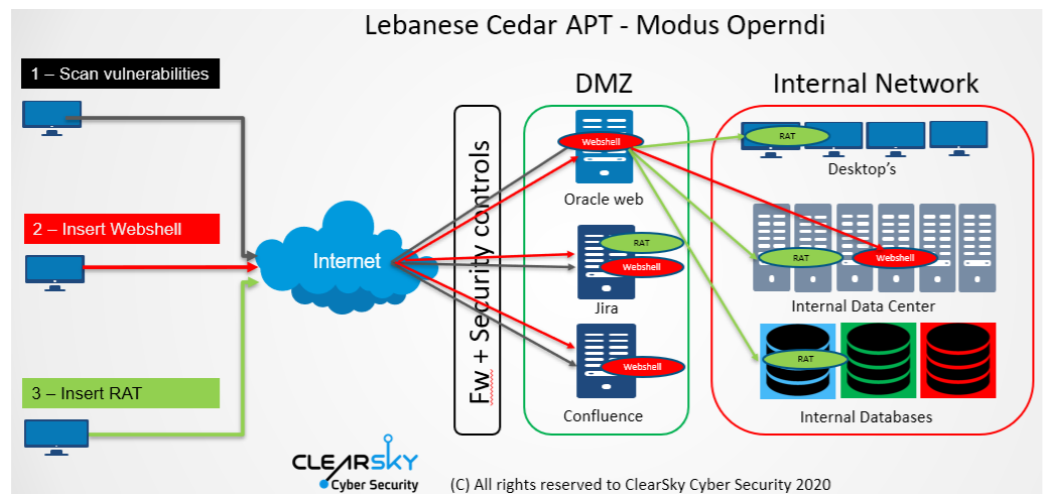
Clearsky researchers linked the Lebanese Cedar APT group to a cyber espionage campaign that targeted companies around the world. Clearsky researchers linked the Lebanese Cedar group (aka Volatile Cedar) to a cyber espionage campaign that targeted companies around the world. The APT group has been active since 2012, experts linked the group to the Hezbollah […]
Pierluigi Paganini
January 26, 2021
Google TAG is warning that North Korea-linked hackers targeting security researchers through social media. Google Threat Analysis Group (TAG) is warning that North Korea-linked hackers targeting security researchers through social media. According to the Google team that focuses on nation-state attacks, a North Korea-linked APT group has targeted experts that are working on the research […]
 Pierluigi Paganini
January 20, 2021
Cybersecurity firm FireEye has released a report that sheds the light on the SolarWinds attack and the way hackers breached its networks. Cybersecurity firm FireEye has released a report that sheds the light on the SolarWinds attack and the way hackers breached its networks. The experts explained how the UNC2452 and other threat actors breached […]