 Pierluigi Paganini
 June 21, 2018
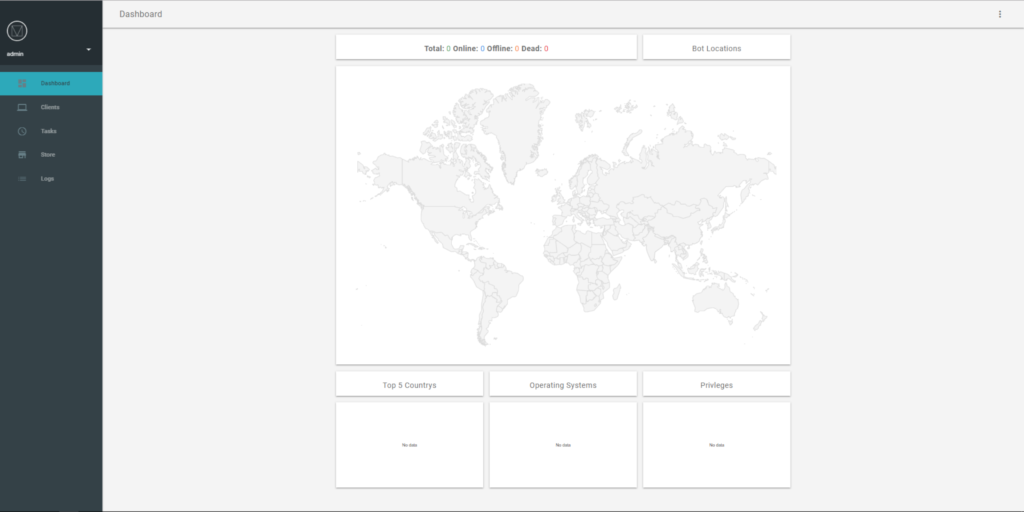
Researchers at Netscout Arbor have discovered a malware downloader advertised on underground forums as a paid open beta product, its name is Kardon Loader. Researchers from Netscout Arbor have discovered a downloader advertised on underground forums dubbed Kardon Loader, it allows customers to build a malware distribution network or a botshop. Advs for Kardon Loader were first discovered on April 21, 2018, the author […]
 Pierluigi Paganini
June 17, 2018
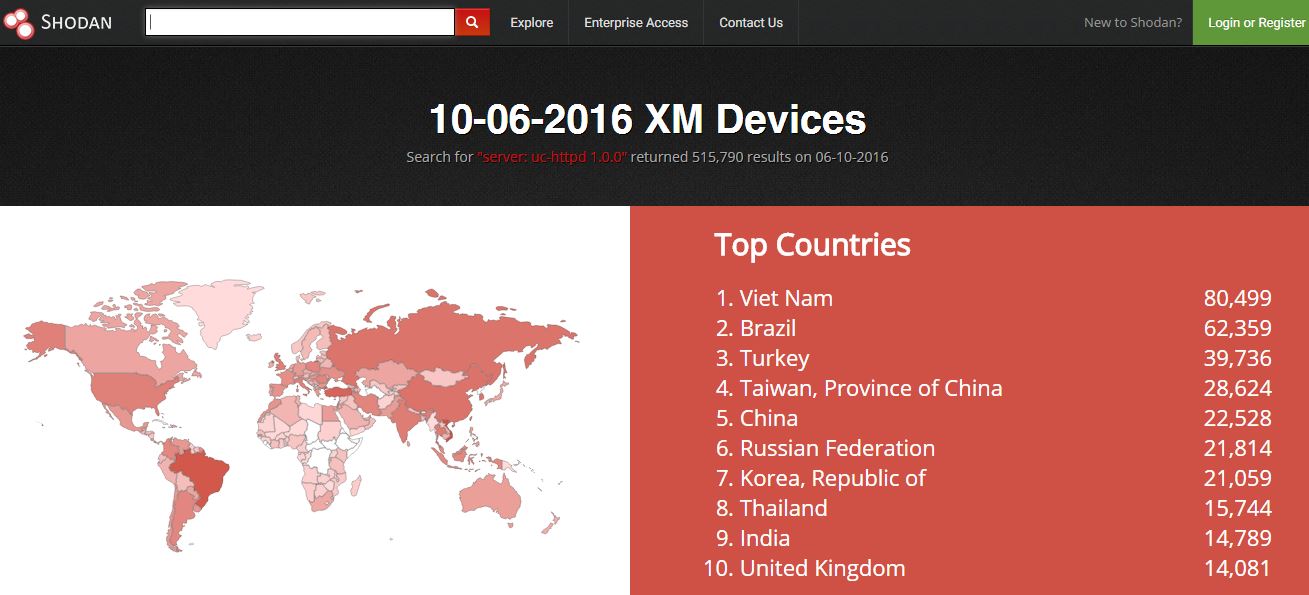
This week, security experts observed a surge in port 8000 scan activity, researchers at Qihoo 360 Netlab determined that the unusual activity was associated with Satori IoT botnet. Experts from Qihoo 360 Netlab discovered that the author of the Satori botnet have integrated a the proof-of-concept (PoC) code for the XionMai web server software package after it was […]
 Pierluigi Paganini
June 13, 2018
A security researcher from Vertek Corporation reported to Bleeping Computer that over 43 million email addresses have been leaked from the command and control server of a spam botnet. An expert from Vertek Corporation spotted the C&C server while investigating a recent malware campaign distributing a version of the Trik trojan. The malicious code was used as a first-stage malware […]
 Pierluigi Paganini
June 07, 2018
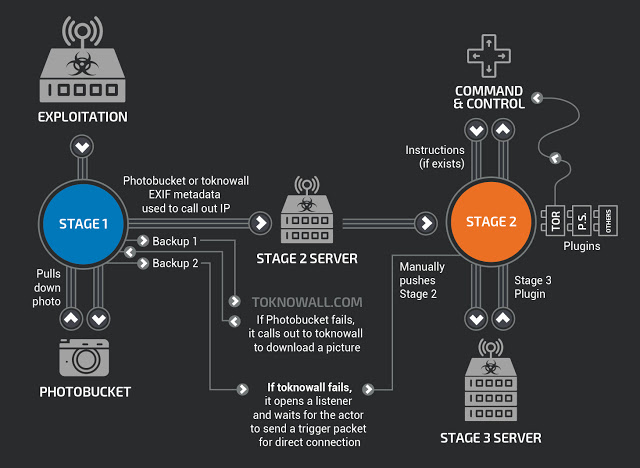
The VPNFilter botnet now targeting new devices from other vendors, including ASUS, D-Link, Huawei, Ubiquiti, UPVEL, and ZTE. The VPNFilter botnet is worse than initially thought, according to a new report published by Cisco Talos Intelligence group, the malicious code is now targeting ASUS, D-Link, Huawei, Ubiquiti, UPVEL, and ZTE “First, we have determined that additional devices are […]
 Pierluigi Paganini
June 07, 2018
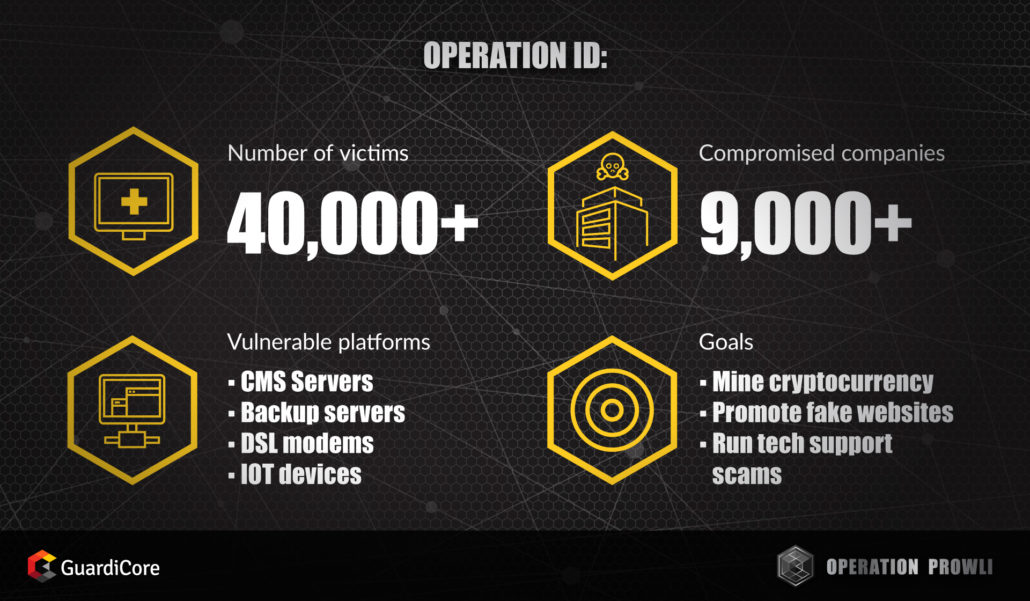
Crooks have infected over 40,000 web servers, modems, and other IoT devices with the Prowli malware as part of a cryptocurrency mining campaign and to redirect victims to malicious sites. The Prowli malware was spotted by researchers at GuardiCore, attackers composed the huge botnet by exploiting known vulnerabilities and brute-force attacks. This campaign, dubbed Operation Prowli, […]
 Pierluigi Paganini
June 03, 2018
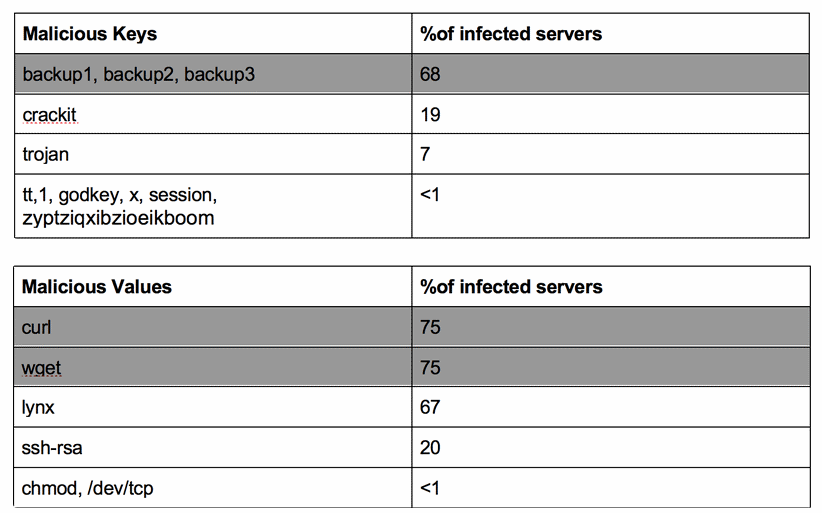
According to the security experts at Imperva firm, three open Redis servers out of four are infected with malware. The discovery is the result of analysis conducted by running Redis-based honeypot servers for some months. Since their initial report on the RedisWannaMine attack that propagates through open Redis and Windows servers, the experts from Imperva have discovered a new […]
 Pierluigi Paganini
June 01, 2018
Cybercriminals continue to improve the infamous Mirai botnet by adding new exploits and functionalities, experts warn new dangerous variant will appear in the wild. According to Netscout’s Arbor Security Engineering and Response Team (ASERT), cybercriminals continue to improve the dreaded Mirai IoT botnet by adding new exploits and functionalities. The time to market of new Mirai botnet […]
 Pierluigi Paganini
May 28, 2018
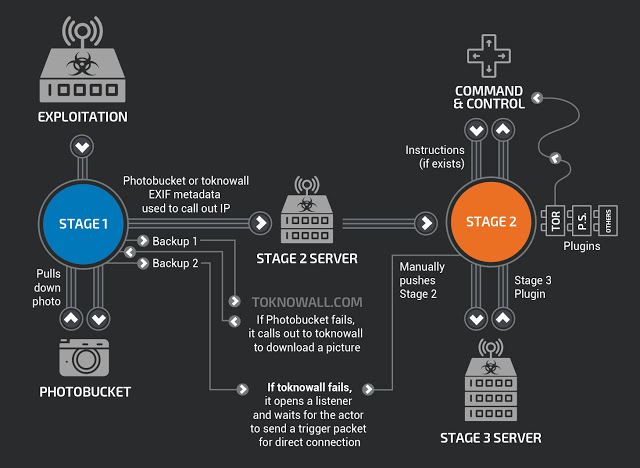
Researchers and the FBI are working together to take down the dreaded VPNFilter botnet composed of hundreds of thousands of compromised devices. For several months, there have been rumors and vague warnings about highly skilled adversaries targeting critical infrastructure. Last week we learned some details about the warning, why you might be impacted and how […]
Pierluigi Paganini
May 24, 2018
The Justice Department announced an effort to disrupt the VPNFilter botnet of hundreds of thousands of infected home and office (SOHO) routers and other networked devices under the control of a Russia-linked APT group. Yesterday Talos and other security firm revealed the discovery of a huge botnet tracked as VPNFilter composed of more than 500,000 compromised routers and […]
Pierluigi Paganini
May 23, 2018
Security firm Talos along with other cybersecurity firms and law enforcement agencies have uncovered a huge botnet dubbed VPNFilter, composed of more than 500,000 compromised routers and network-attached storage (NAS) devices. The experts believe the VPNFilter was developed by Russia and the associated malware appears to be very sophisticated, at the time they discovered more than 500,000 compromised devices across […]

Hacking / October 29, 2026