 Pierluigi Paganini
 June 16, 2017
A study conducted by the security firm Rapid7 revealed that millions of devices remain exposed to cyber attacks via SMB, Telnet, RDP, and other types of improper configurations. Rapid7 published the second report National Exposure Index that provides Internet service providers (ISPs) worldwide information about the global exposure of devices. The researchers scanned the Internet for improperly configured services, […]
 Pierluigi Paganini
May 22, 2017
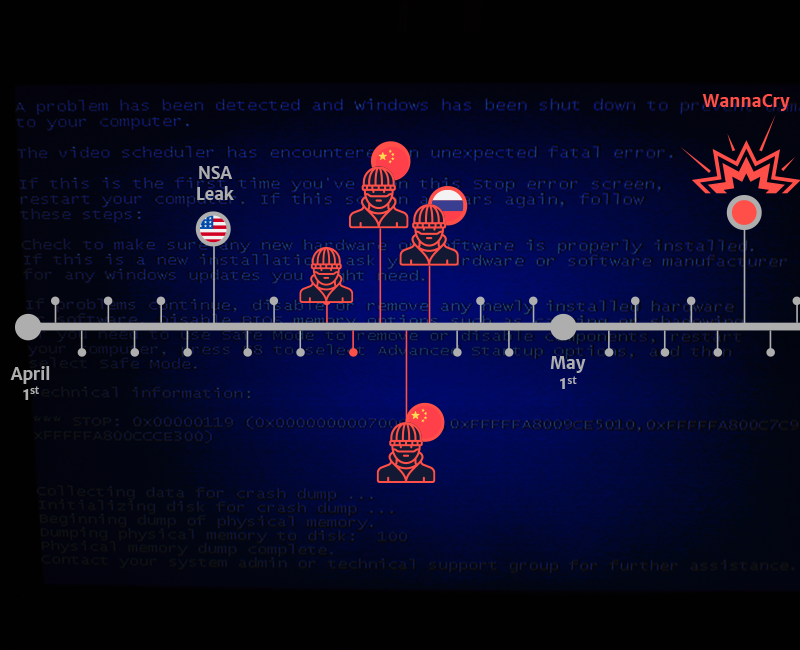
At least 3 different groups have been leveraging the NSA EternalBlue exploit weeks before the WannaCry attacks, here’s the evidence. In the last days, security experts discovered numerous attacks that have been leveraging the same EternalBlue exploit used by the notorious WannaCry ransomware. The Shadow Brokers hacker group revealed the exploit for the SMB vulnerability in April, but […]
 Pierluigi Paganini
May 20, 2017
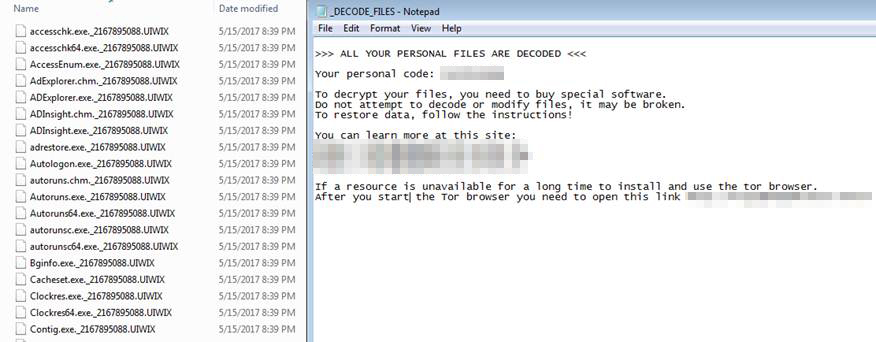
Security experts discovered a new ransomware family, dubbed UIWIX, that uses the NSA-linked EternalBlue exploit for distribution The effects of the militarization of the cyberspace are dangerous and unpredictable. A malicious code developed by a government could create serious problems for the Internet users, the recent WannaCry massive attack demonstrates it that used the EternalBlue Exploit to […]
 Pierluigi Paganini
May 17, 2017
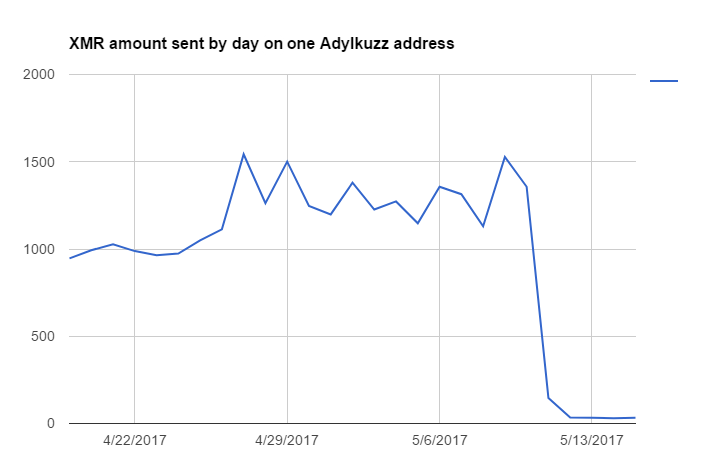
Security experts at ProofPoint security discovered that many machines can’t be infected by WannaCry because they have been already infected by Adylkuzz. The recent WannaCry ransomware attack wasn’t the first to use the NSA-linked EternalBlue and DoublePulsar hacking tools. Proofpoint researchers have discovered that the cryptocurrency miner Adylkuzz, was the first threat that used the EternalBlue exploit to trigger […]
 Pierluigi Paganini
May 12, 2017
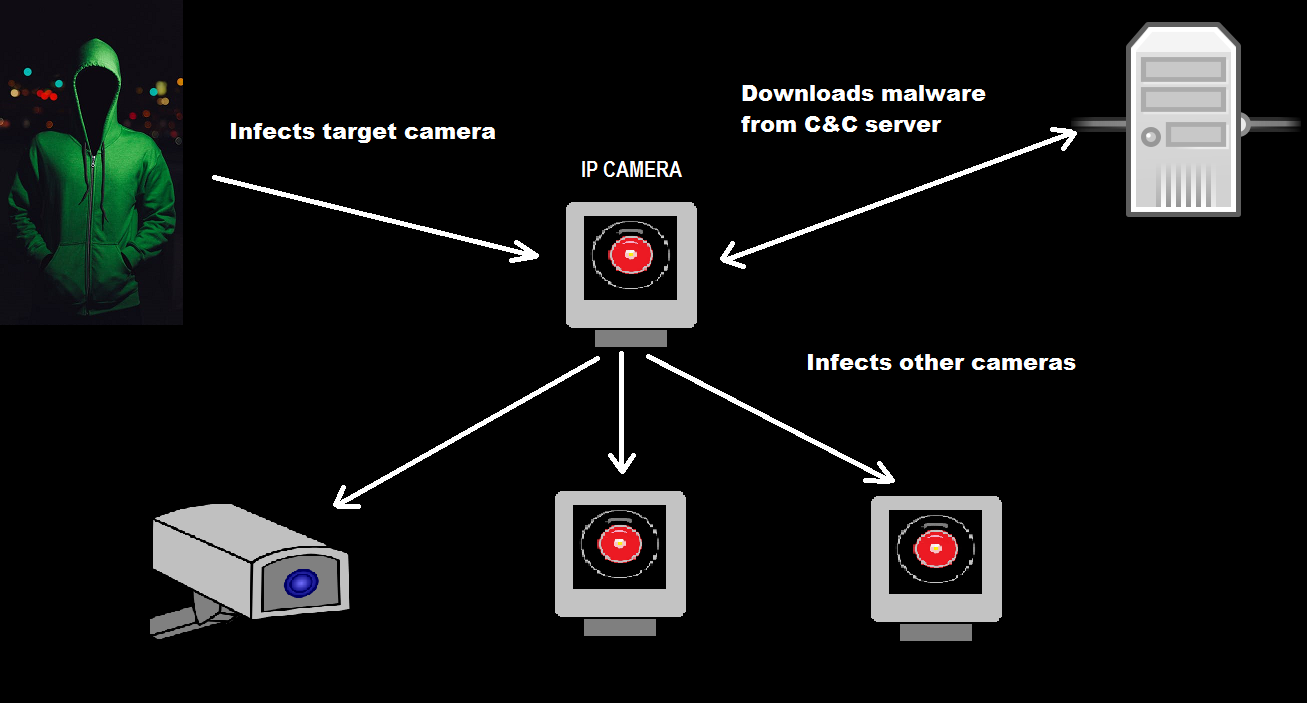
Trend Micro has discovered a new attack on internet-based IP cameras and recorders powered by a new Internet of Things (IOT) bot dubbed PERSIRAI. Trend Micro has discovered a new attack on internet-based IP cameras and recorders. The new Internet of Things (IOT) attack called ELF_PERSIRAI has also been back-tracked to an Iranian research institute […]
 Pierluigi Paganini
May 03, 2017
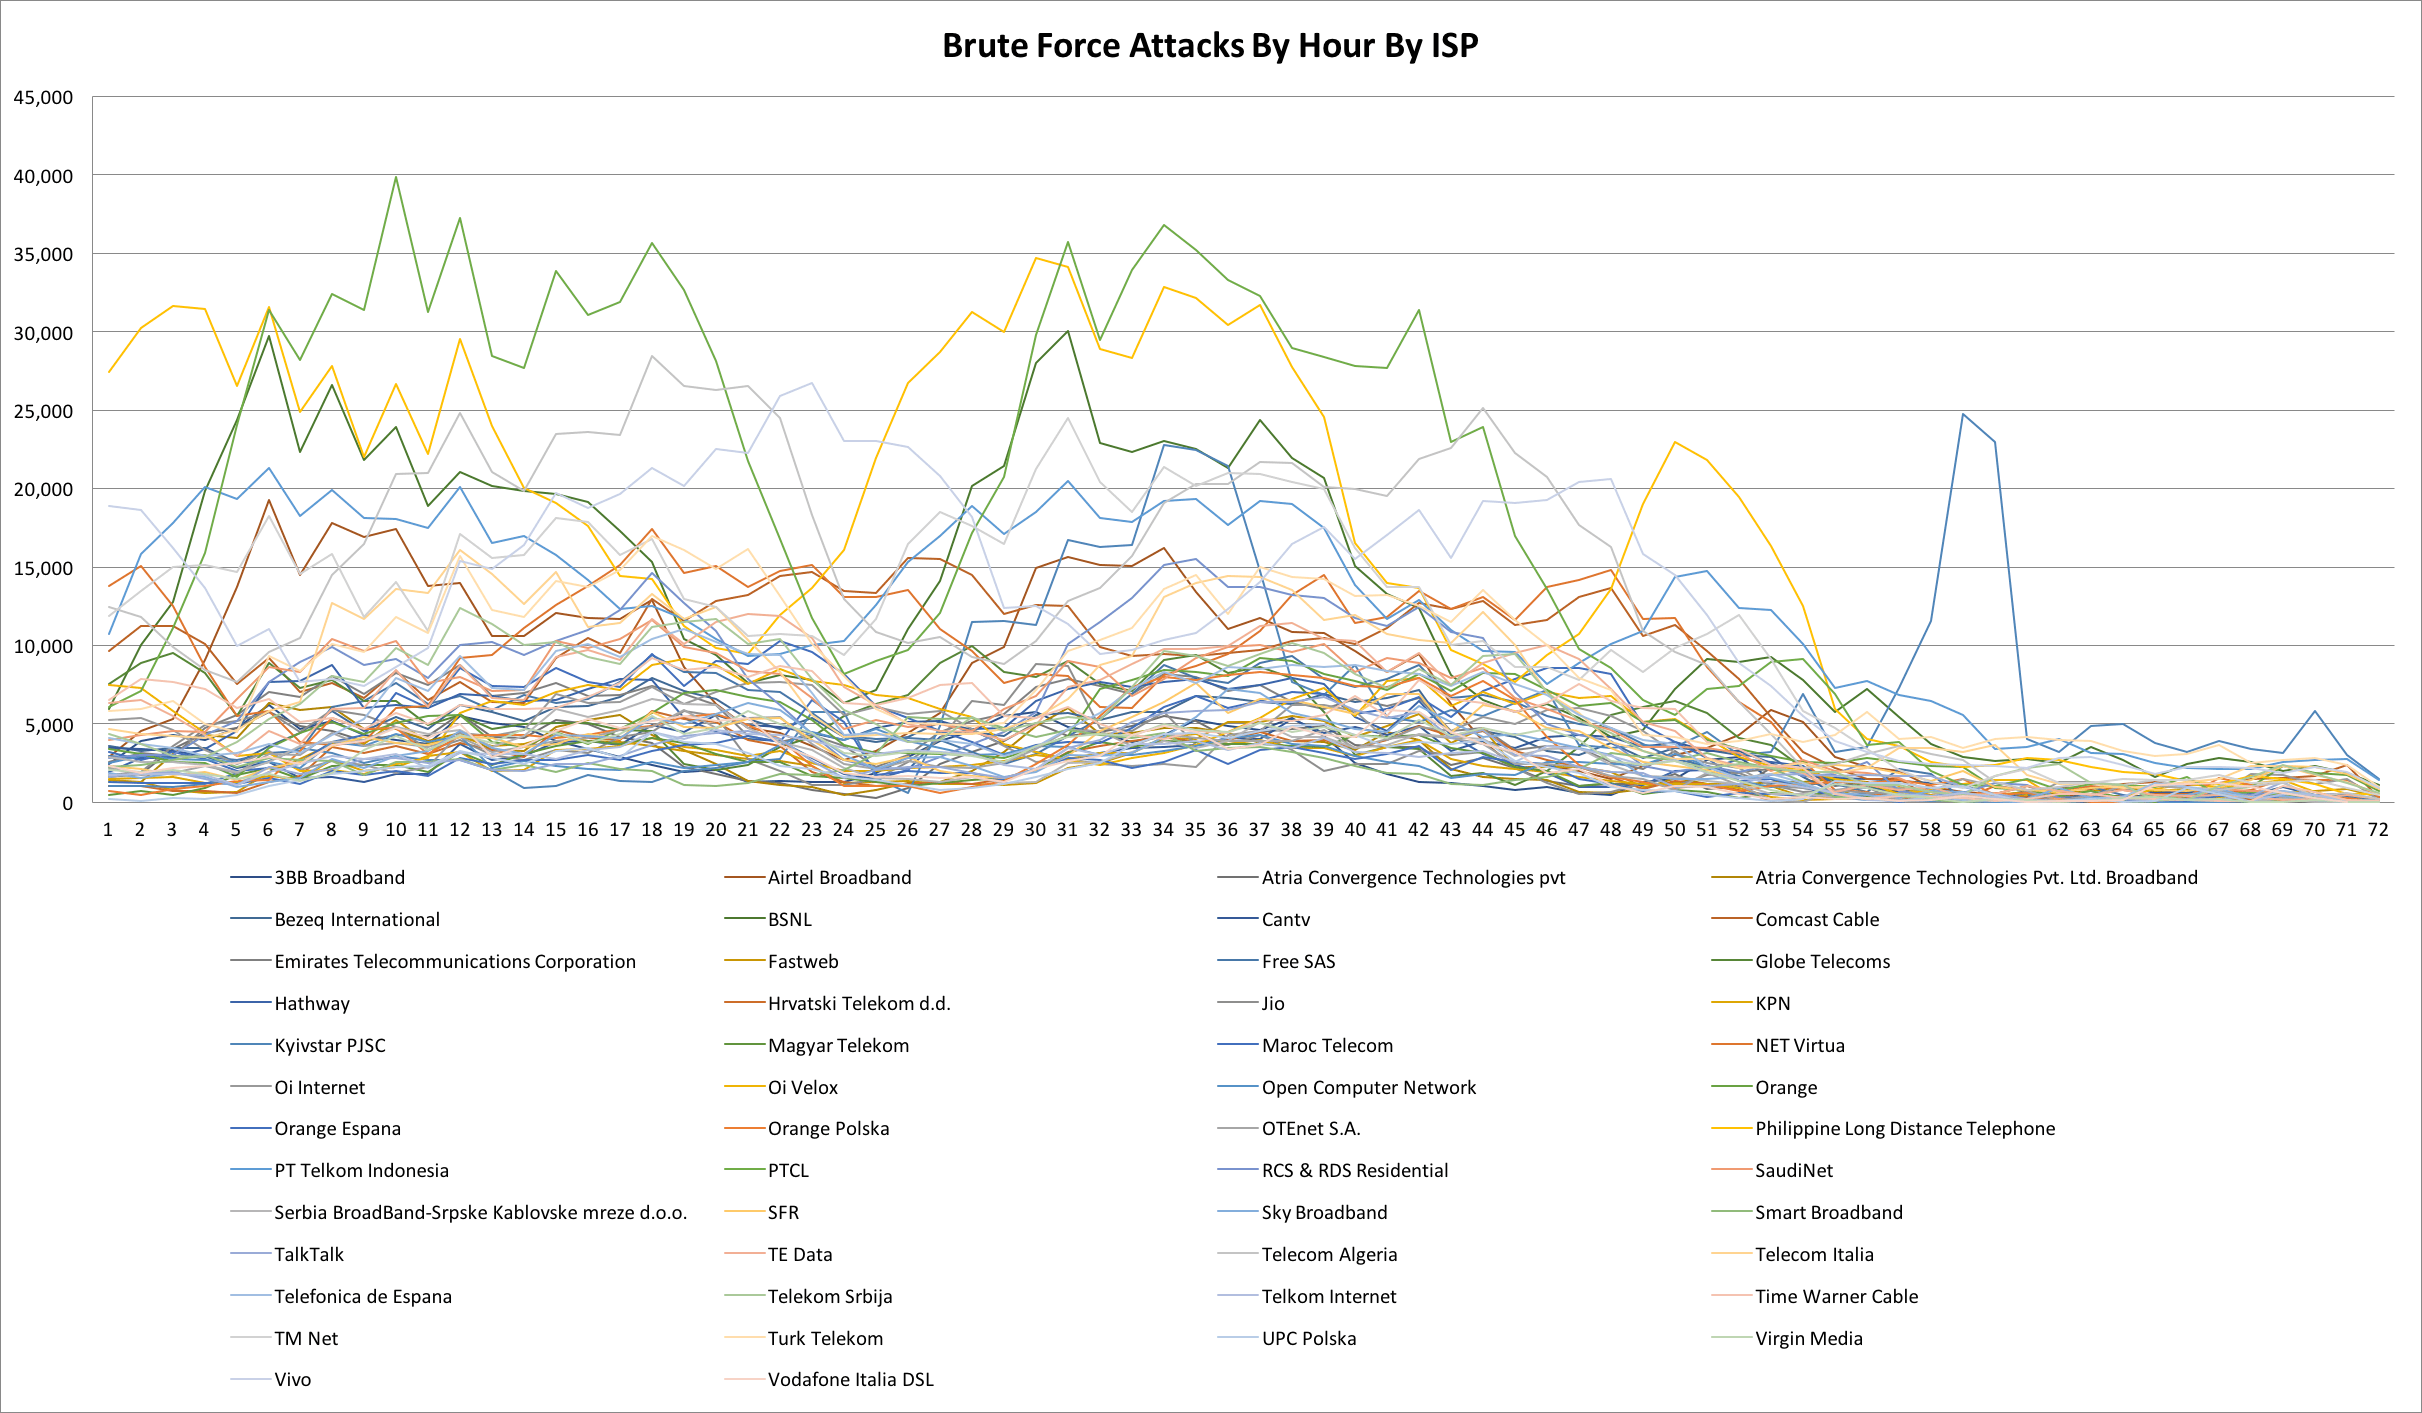
Experts from security firm WordFence reported a rapid reduction of WordPress attacks originating from hundreds of ISPs worldwide. Experts at the security firm Wordfence a few weeks ago reported that tens of thousands of flawed routers from dozens of ISPs worldwide were recruited in a botnet used to power several types of attacks against WordPress […]
 Pierluigi Paganini
May 02, 2017
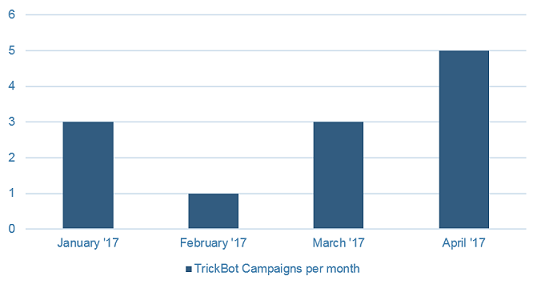
According to a new analysis conducted by the IBM’s X-Force security team, a new wave of attacks powered by the TrickBot banking Trojan have been targeting private banks in the UK, Australia, and Germany. The researchers observed new redirection attacks focused on new brands, including private banks, private wealth management firms, investment banking, and a retirement insurance and […]
 Pierluigi Paganini
April 26, 2017
The Interpol located and shut down nearly 9,000 Command and control servers located in Asia and hacked with a WordPress plug-in exploit. An investigation conducted by the Interpol resulted in the identification of nearly 9,000 command and control servers located in Asia. The law enforcement body operated with the support of private partners, including Kaspersky Lab, Cyber Defense Institute, […]
 Pierluigi Paganini
April 08, 2017
Experts observed a new threat targeting WordPress install, the Sathurbot botnet attempts to bruteforce WordPress accounts. Once compromised a WordPress website, the Sathurbot botnet uses it to spread the malware. The Sathurbot leverages torrents as a delivery mechanism, once a website is compromised it is used to host fake movie and software torrents. When victims search for […]
 Pierluigi Paganini
March 09, 2017
The researcher Pierre Kim revealed that more than 185,000 vulnerable Wi-Fi-connected cameras are exposed to the Internet, ready to be hacked. According to the security advisory published by Pierre Kim via Full Disclosure, more than 185,000 vulnerable Wi-Fi-connected cameras are exposed to the Internet, a gift for crooks and hackers. The devices are affected by the following […]

Hacking / October 29, 2026