


 Pierluigi Paganini
 March 02, 2026
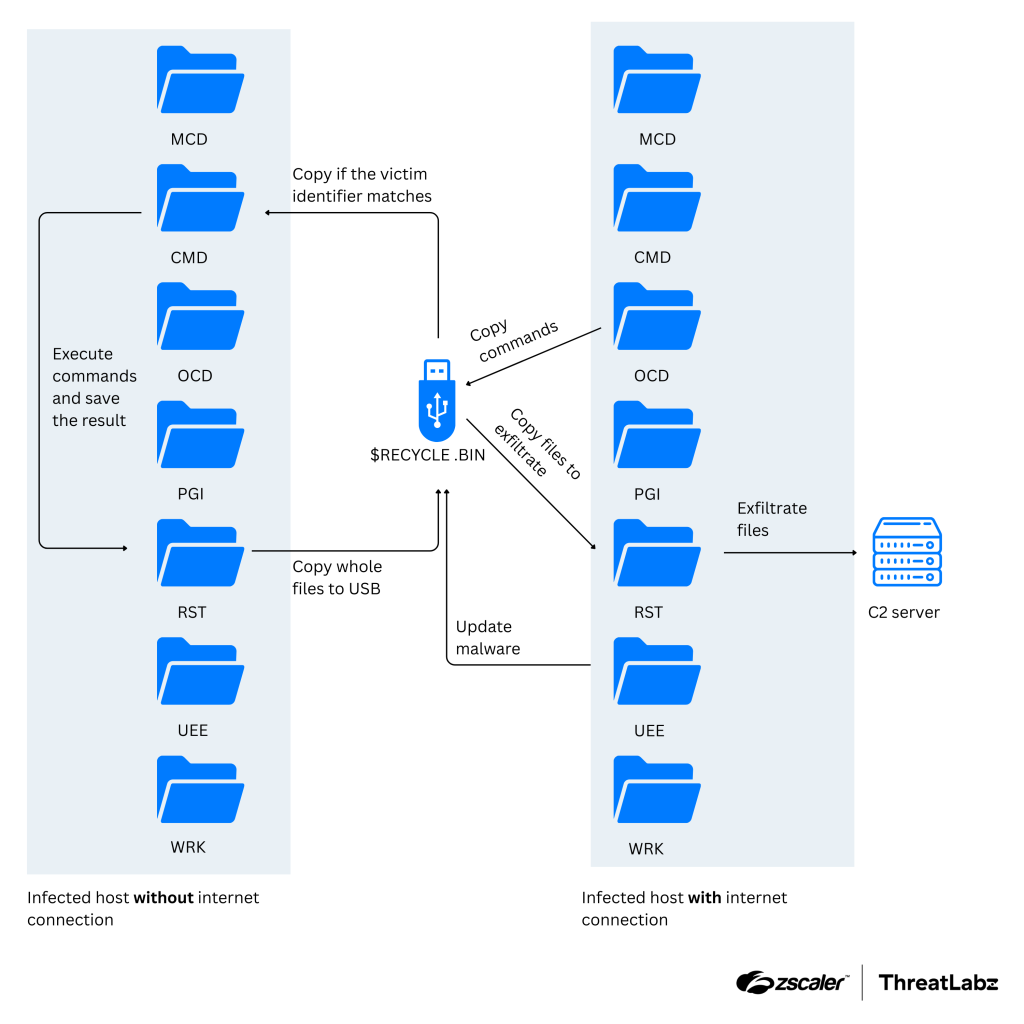
North Korea-linked APT 37 used Zoho WorkDrive and USB malware to breach air-gapped networks in the Ruby Jumper campaign. North Korean group ScarCruft (aka APT37, Reaper, and Group123) deployed new tools in a campaign dubbed Ruby Jumper, using a backdoor that leverages Zoho WorkDrive for C2 and a USB-based implant to breach air-gapped systems. Zscaler ThreatLabz […]
 Pierluigi Paganini
March 02, 2026
“ClawJacked” flaw let malicious sites hijack OpenClaw AI agents to steal data; patch released in version 2026.2.26. A high-severity vulnerability called ClawJacked in OpenClaw allowed malicious websites to brute-force and take control of local AI agent instances. Oasis Security discovered the flaw, which enabled silent data theft. OpenClaw addressed the issue with version 2026.2.26, released […]
 Pierluigi Paganini
March 01, 2026
Hackers abused Claude Code to build exploits and steal 150GB of data in a cyberattack targeting Mexican government systems. Hackers abused Anthropic’s Claude Code AI assistant to develop exploits, create custom tools, and automatically exfiltrate more than 150GB of data in an attack on Mexican government systems, the Israeli cybersecurity firm Gambit Security reports. The […]
 Pierluigi Paganini
February 28, 2026
A data breach at Canadian Tire exposed personal data from over 38 million accounts, including contact details and encrypted passwords. More than 38 million accounts were affected by an October 2025 data breach at Canadian retail giant Canadian Tire (CTC). The incident marks one of the largest retail data breaches in Canada, raising concerns about […]
 Pierluigi Paganini
February 27, 2026
AI accelerates incident response by correlating alerts and generating reports in minutes, helping teams scale beyond manual limits. Incident response has always been a race against the clock. It starts ticking the moment an alert is triggered, and each minute thereafter can lead to lost revenue, regulatory exposure, reputational damage, or customer churn. Traditionally, incident […]
 Pierluigi Paganini
February 27, 2026
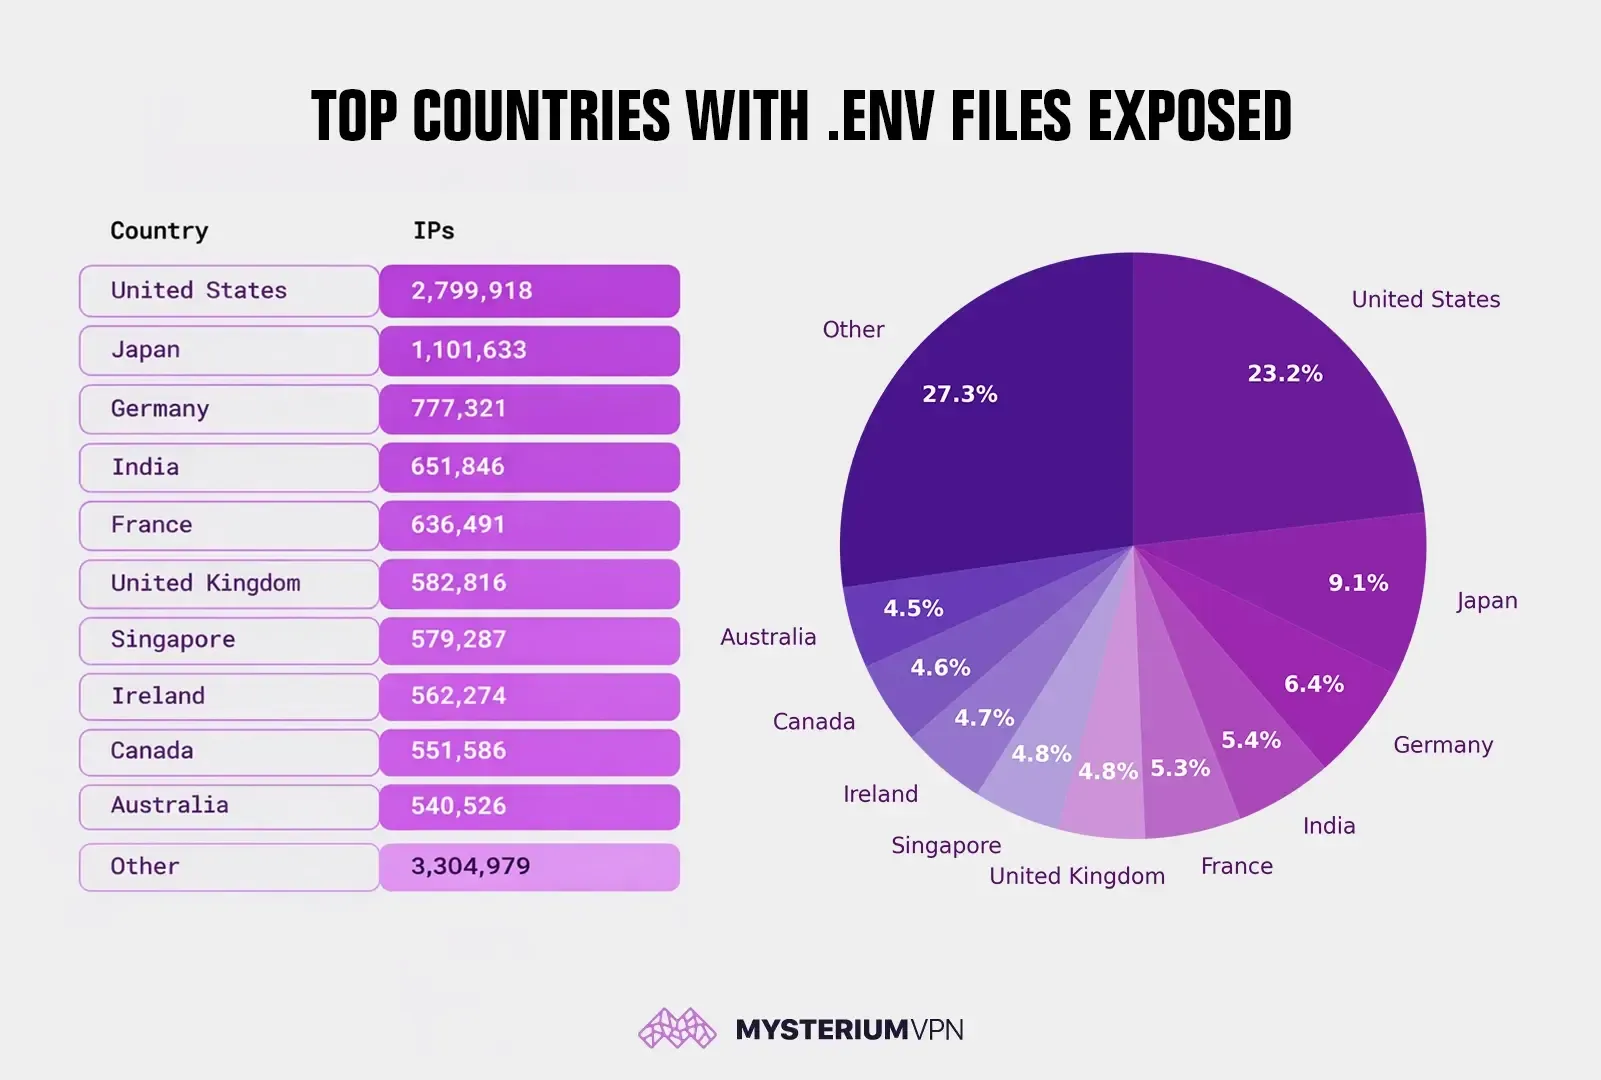
Mysterium VPN found 12M IPs exposing .env files, leaking credentials and revealing widespread security misconfigurations worldwide. Configuration mistakes rarely trigger alarms. A forgotten deny rule, an overlooked server setting, or a full project folder uploaded to production can quietly expose a company’s most sensitive secrets. In many cases, those secrets live inside simple environment files […]
 Pierluigi Paganini
February 27, 2026
European DIY platform ManoMano suffered a data breach via a third-party provider, exposing personal data of 38 million customers. European DIY e-commerce platform ManoMano disclosed a major data breach affecting 38 million customers. Hackers accessed personal information by compromising a third-party service provider, prompting notifications and potential security measures for impacted users across multiple countries. […]
 Pierluigi Paganini
February 26, 2026
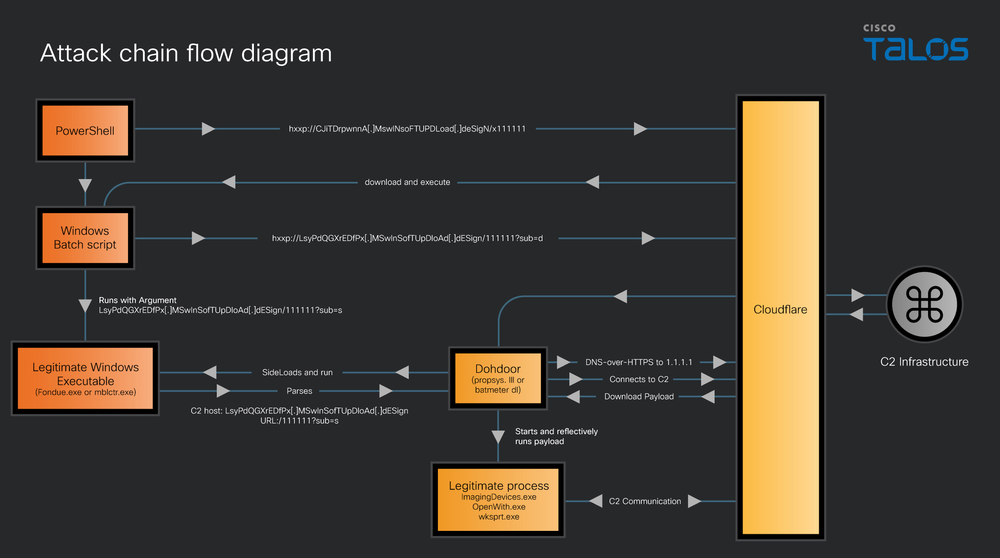
UAT-10027 campaign is targeting U.S. education and healthcare sectors to deploy a new Dohdoor backdoor. Cisco Talos has identified a new threat cluster, tracked as UAT-10027, targeting U.S. education and healthcare organizations since at least December 2025 to deploy a previously unseen backdoor named Dohdoor. Initial access likely occurs through phishing, triggering a PowerShell script […]
 Pierluigi Paganini
February 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco SD-WAN flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added two Cisco SD-WAN flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the catalog: This week, Cisco warned of a critical Cisco SD-WAN vulnerability, tracked […]
 Pierluigi Paganini
February 26, 2026
Cisco SD-WAN vulnerability CVE-2026-20127 has been exploited since 2023 to gain unauthenticated admin access. A critical Cisco SD-WAN vulnerability, tracked as CVE-2026-20127 (CVSS score of 10.0), has been actively exploited since 2023. The flaw affects Catalyst SD-WAN Controller and Manager and allows remote, unauthenticated attackers to bypass authentication and gain full administrative access by sending […]






