 Pierluigi Paganini
 June 18, 2013
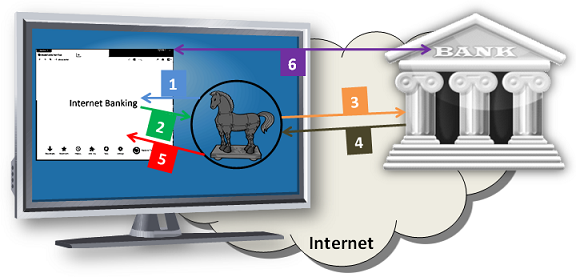
Security firm Trusteer detected a new variant of Zeus Trojan that steals funds and recruits Money Mules proposing jobs ads to the victims using Man-in-the-Browser (MitB) techniques. Zeus Trojan is becoming even more complex, its evolution is unpredictable due to the intense activity in the underground on its source code. Various forums in the underground offer customization […]
 Pierluigi Paganini
June 12, 2013
Is RBN (Russian Business Network) really linked to Facebook Zeus variant? Exclusive interview with WhiteHat who has investigated on the malware. RBN or ordinary crime, Zeus is appearing in new forms and using new infection channels but according some security analysts behind new a variant there could be the support of members of dangerous criminal organization RBN. As […]
 Pierluigi Paganini
May 17, 2013
Group-IB researchers have detected a new botnet named Kangoo that infected more than 150 000 machines mainly targeting Australian banks. Group-IB researchers have detected a new botnet named Kangoo that infected more than 150 000 machines, specialists dubbed it «Kangoo» due the presence of a kangaroo logo on the WEB-interface of the C&C administrative panel. The botnet mainly […]
 Pierluigi Paganini
May 11, 2013
The biggest Bank robbery realized by a gang of hackers, a global network of cyber criminals operating in 26 countries stole $45 million hacking into a database of prepaid debit cards. The news on the biggest bank robbery with a cyber attack against ATMs in the history is conquering the Network, US law enforcement has […]
 Pierluigi Paganini
April 25, 2013
Public offer of Zeus FaaS service on Facebook My readers know very well the dynamic of cybercrime enterprise and in particular of the growing interest in monetization malicious codes such as malware, ransomware and more in general botnets. One of the most targeted sector is banking, the evolution of banking services, their introduction on mobile platforms made attractive targets for cyber criminals, one […]
 Pierluigi Paganini
April 23, 2013
In the last months of 2012 a group of hackers known as “Izz ad-Din al-Qassam Cyber Fighters” conducted a series of attacks against principal banking and financial institutions including the U.S. Bancorp, JPMorgan Chase&co, Bank of America, PNC Financial Fervices Group, and SunTrust Banks. Security experts noted that the hackers adopted an anomalous strategy for the […]
 Pierluigi Paganini
February 17, 2013
Zeus malware is considered the most popular and prolific malicious code for banking, it is one of the privilege agent by cybercrime the use to sell various customized version in the underground to conduct sophisticated frauds. Security community has found it in different occasion and anyway it was a surprice, the malware has evolved in […]
 Pierluigi Paganini
February 04, 2013
In the last weeks we discussed on the efficiency of exploit kits, malicious tool kits that allow to the attackers to exploit a huge quantity of vulnerabilities in victims systems. These products are largely diffused in the underground where is possible to find different tools usable for various purpose, most precious are those kit that […]
 Pierluigi Paganini
January 28, 2013
The capillary diffusion of mobile devices, the lack of security systems on these platforms and low level of awareness on principal cyber threats made them a privileged target for cybercrime. We have assisted in the recent year to an explosion of malware designed to hit principal mobile OSs, in a recent report Sophos security firm […]
 Pierluigi Paganini
January 26, 2013
The news is sensational US authorities blamed 3 individuals of a large scale malware-based attack against banking world, the trojan infected at least one million computers stealing millions of dollars. The three are the Russian Nikita Kuzmin (25 year old), Latvian resident Deniss Calovskis (27 year old) and Romanian Mihai Ionut Paunescu (28 year old) […]