Pierluigi Paganini
 December 30, 2025
China-linked APT Mustang Panda used a signed kernel-mode rootkit driver to load shellcode and deploy its ToneShell backdoor. China-linked APT Mustang Panda (aka Hive0154, HoneyMyte, Camaro Dragon, RedDelta or Bronze President) was observed using a signed kernel-mode rootkit driver with embedded shellcode to deploy its ToneShell backdoor. Mustang Panda has been active since at least 2012, targeting American and European entities such as […]
 Pierluigi Paganini
December 30, 2025
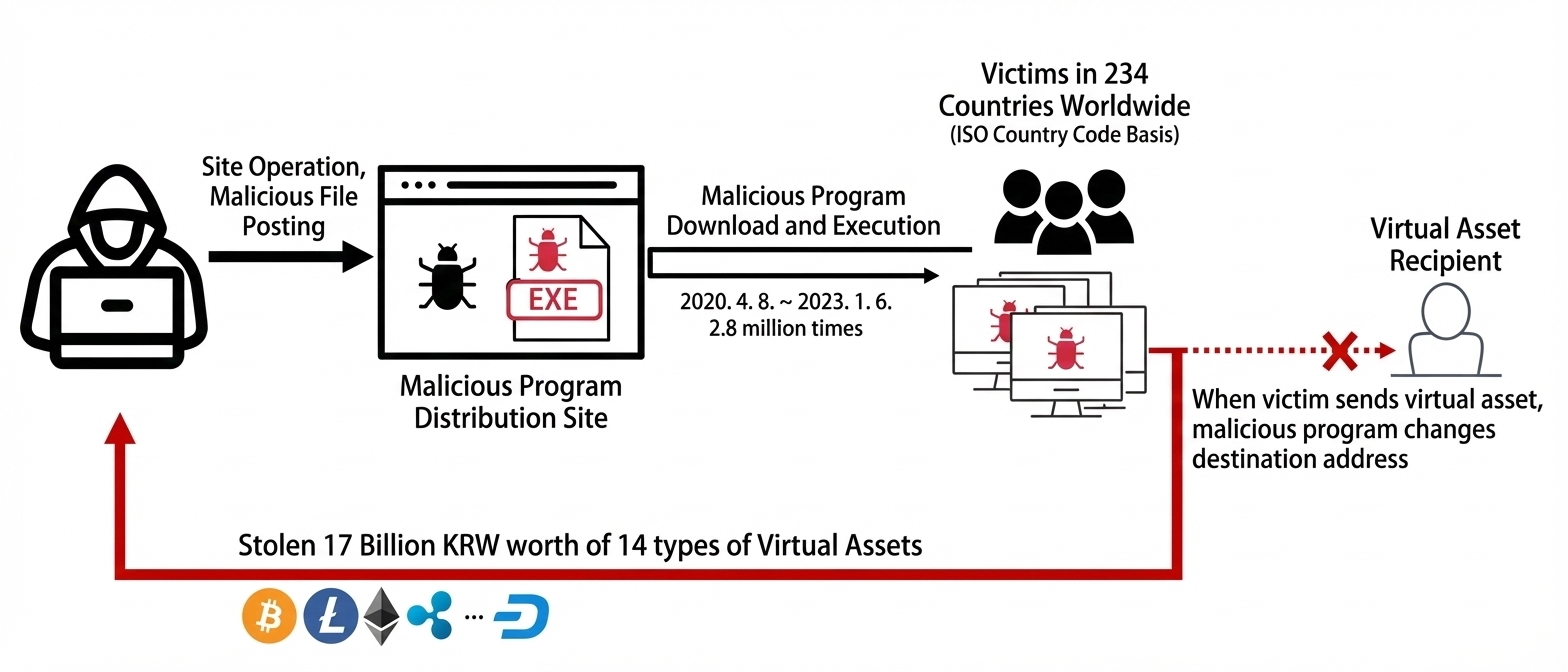
A Lithuanian national was arrested for allegedly spreading KMSAuto malware that stole clipboard data and infected 2.8 million Windows and Office systems. A Lithuanian man (29) was arrested for allegedly spreading KMSAuto-based clipboard-stealing malware that infected about 2.8 million Windows and Office systems. The man was extradited from Georgia to South Korea under Interpol coordination. […]
 Pierluigi Paganini
December 29, 2025
A ransomware attack hit Romania’s Oltenia Energy Complex on December 26, knocking out IT systems at the country’s largest coal power producer. A ransomware attack disrupted Oltenia Energy Complex, Romania’s largest coal-based power producer, shutting down its IT systems on December 26. The Oltenia Energy Complex (CE Oltenia) is Romania’s leading state-controlled lignite mining and […]
Pierluigi Paganini
December 29, 2025
China-linked APT Evasive Panda used DNS poisoning to deliver the MgBot backdoor in targeted cyber-espionage attacks in Türkiye, China, and India. Kaspersky researchers spotted the China-linked APT group Evasive Panda (aka Daggerfly, Bronze Highland, and StormBamboo) running a targeted cyber-espionage campaign using DNS poisoning to deliver the MgBot backdoor against victims in Türkiye, China, and […]
 Pierluigi Paganini
December 28, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Choose Your Fighter: A New Stage in the Evolution of Android SMS Stealers in Uzbekistan From Linear to Complex: An Upgrade in RansomHouse Encryption Prince of Persia: A Decade of Iranian Nation-State APT Campaign […]
 Pierluigi Paganini
December 27, 2025
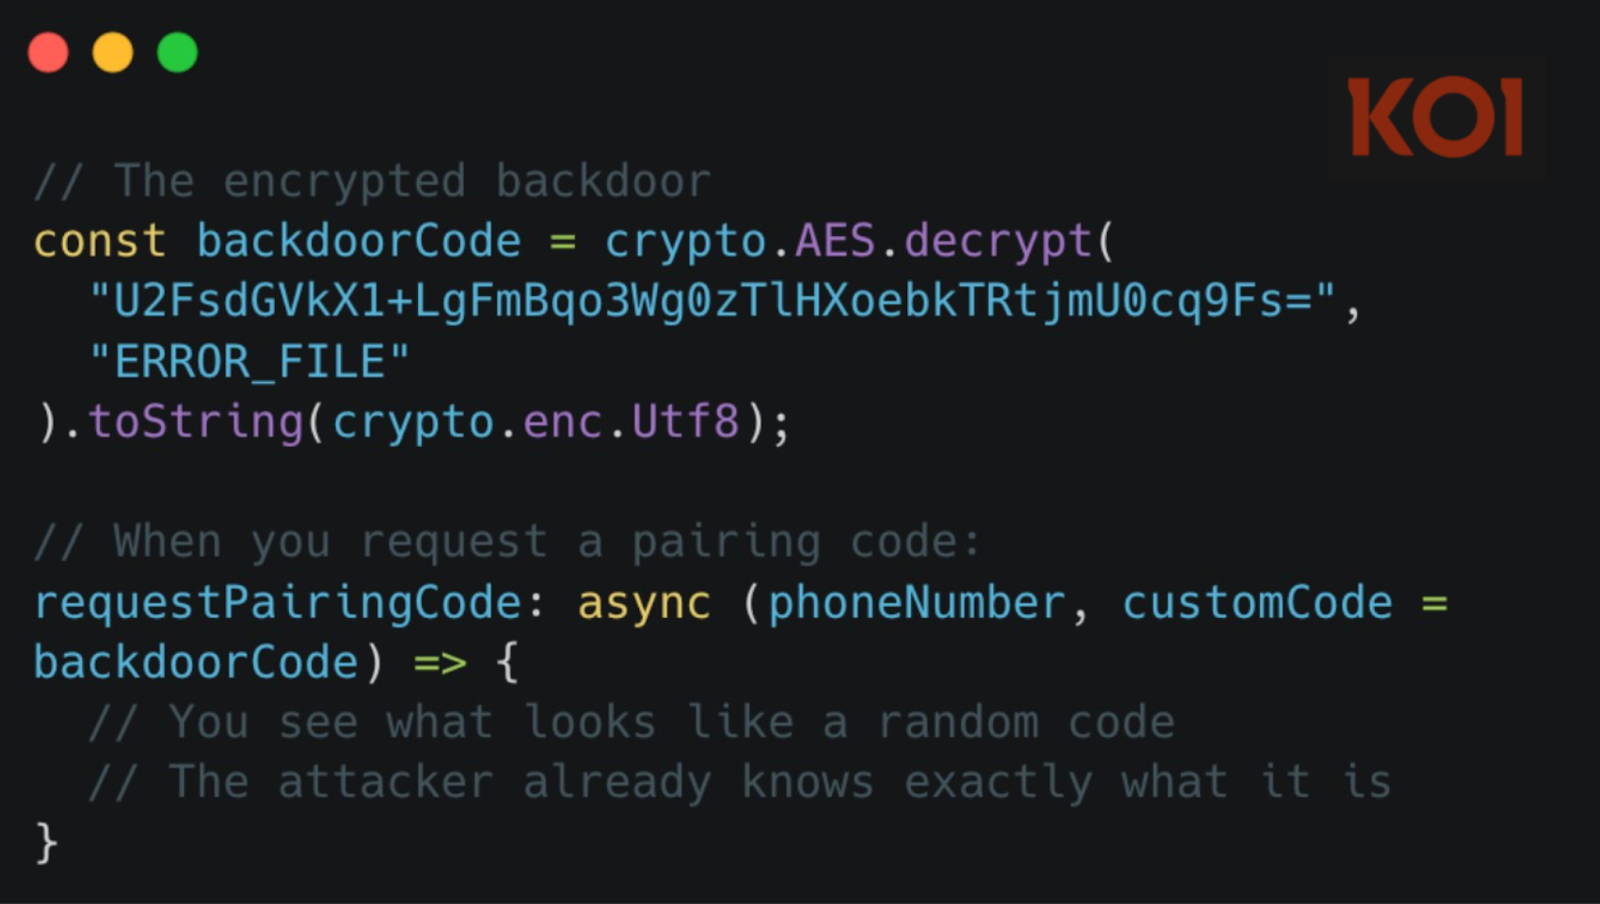
An NPM package with over 56,000 downloads stole WhatsApp credentials, hid its activity, and installed a backdoor. Koi Security researchers warned that the NPM package ‘Lotusbail’, a WhatsApp Web API library and fork of ‘Baileys’, has been stealing users’ credentials and data. The package has been available for six months and has had over 56,000 […]
Pierluigi Paganini
December 22, 2025
Romania’s national water management authority, Romanian Waters, was hit by a ransomware attack over the weekend. Romanian Waters (Administrația Națională Apele Române), the country’s water management authority, suffered a ransomware attack over the weekend. According to the National Cyber Security Directorate (DNSC), the incident affected around 1,000 computer systems across the central organization and 10 […]
 Pierluigi Paganini
December 22, 2025
Ukrainian Artem Stryzhak (35) pleaded guilty in the U.S. for Nefilim ransomware attacks; he was arrested in Spain in 2024, extradited in April 2025. A 35-year-old Ukrainian, Artem Aleksandrovych Stryzhak (35), pleaded guilty in the U.S. for Nefilim ransomware attacks. The Ukrainian citizen was arrested in Spain in 2024 and extradited to the US in […]
Pierluigi Paganini
December 21, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter CyberVolk | A Deep Dive into the Hacktivists, Tools and Ransomware Fueling Pro-Russian Cyber Attacks Operation MoneyMount-ISO — Deploying Phantom Stealer via ISO-Mounted Executables Inside GhostPoster: How a PNG Icon Infected 50,000 Firefox Users […]
 Pierluigi Paganini
December 21, 2025
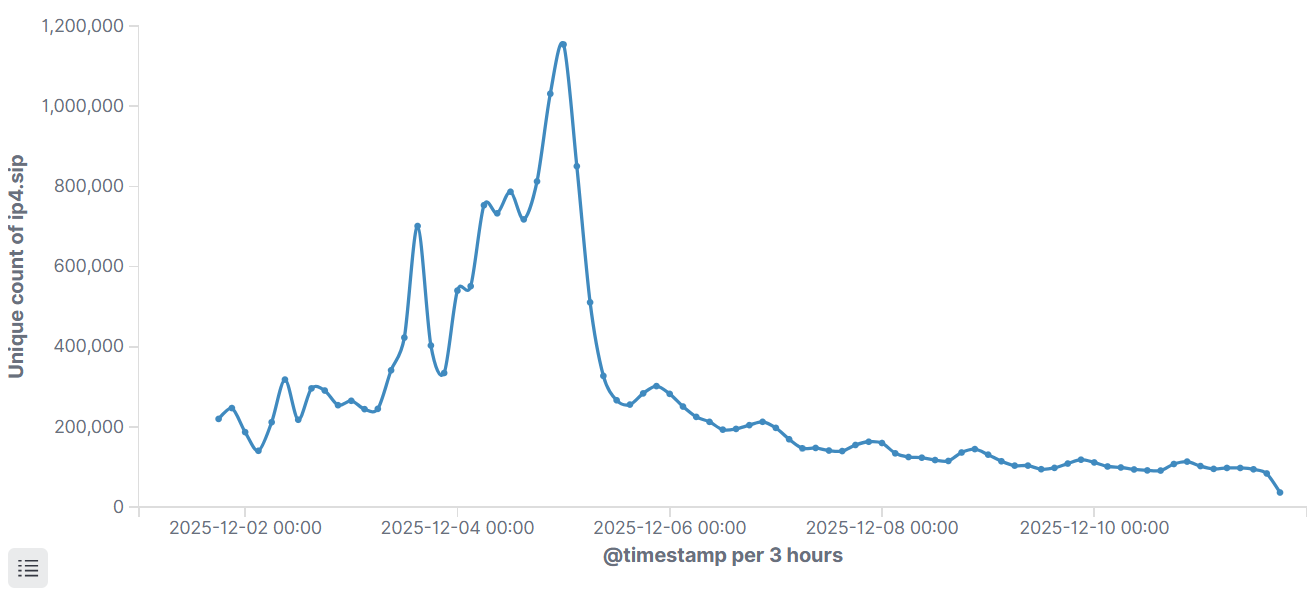
The Kimwolf Android botnet has infected 1.8M+ devices, launching massive DDoS attacks and boosting its C&C domain, says XLab. Kimwolf is a newly discovered Android botnet linked to the Aisuru botnet that has infected over 1.8 million devices and issued more than 1.7 billion DDoS attack commands, according to XLab. On October 24, 2025, XLab […]