 Pierluigi Paganini
 August 09, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Fake Xeno Roblox Cheats Deliver Powerful Java Stealer Through Discord and Forums DarkSword’s Panel Sprawl: How One Body Hash Unravels a Six-Panel, Two-Codebase Operator Cluster Distributed npm Package Cluster Delivers Cross-Platform RAT Targeting Alibaba […]
 Pierluigi Paganini
August 09, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Palo Alto Networks Faces China Cybersecurity Review Amid Rising Tech Tensions Metabase Zero-Day Exploited in the Wild, […]
 Pierluigi Paganini
August 08, 2026
China opened a cybersecurity review of Palo Alto Networks, citing national security concerns but giving no details about the reasons behind the probe. China’s Cyberspace Administration (CAC) announced that it’s launching a cybersecurity review of products Palo Alto Networks sells in the country. The announcement itself runs to a few sentences of formal Chinese, citing […]
 Pierluigi Paganini
August 08, 2026
Attackers exploited a CVSS 10 Metabase zero-day to gain admin access and steal sensitive data. Framework confirmed it was among the victims. Metabase just confirmed something no analytics vendor wants to write: attackers found and used an unpatched, maximum-severity flaw against Metabase Cloud before anyone on the defense side knew it existed. The company’s own […]
 Pierluigi Paganini
August 08, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a Progress LoadMaster vulnerability to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Progress LoadMaster vulnerability, tracked as CVE-2026-8037 (CVSS score of 9.6), to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability is an OS Command Injection Remote Code Execution issue […]
 Pierluigi Paganini
August 08, 2026
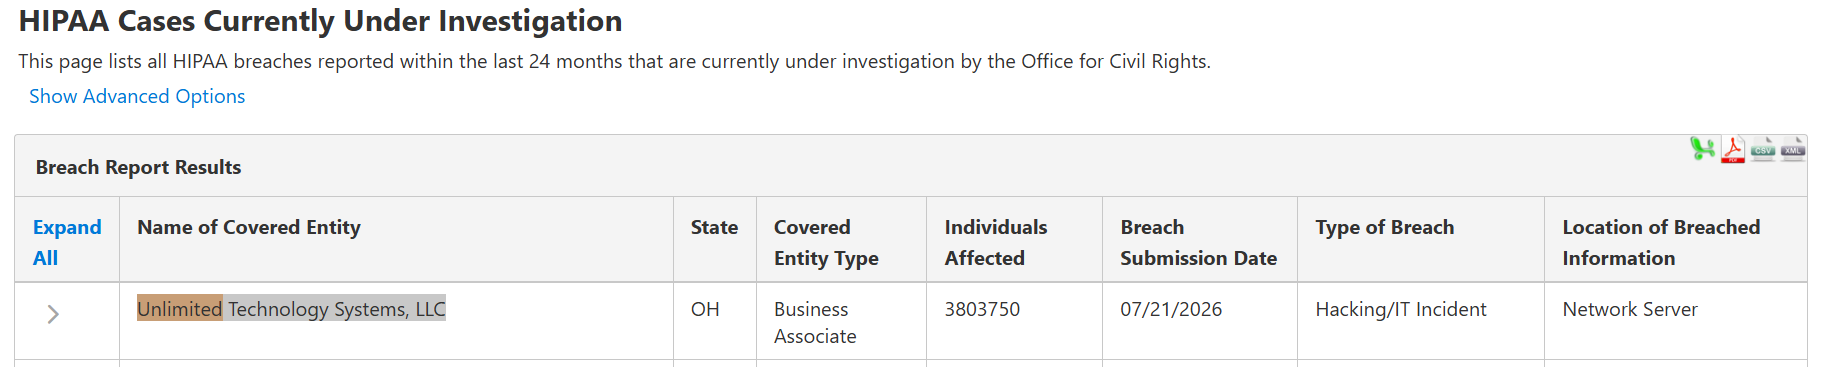
Hackers stole personal, medical, and insurance data of 3.8 million people from Unlimited Technology Systems’ data center. Unlimited Technology Systems disclosed a data breach affecting more than 3.8 million people after hackers accessed one of its commercial data centers between October 5 and 10, 2025. Unlimited Technology Systems is a U.S.-based healthcare technology company headquartered […]
 Pierluigi Paganini
August 07, 2026
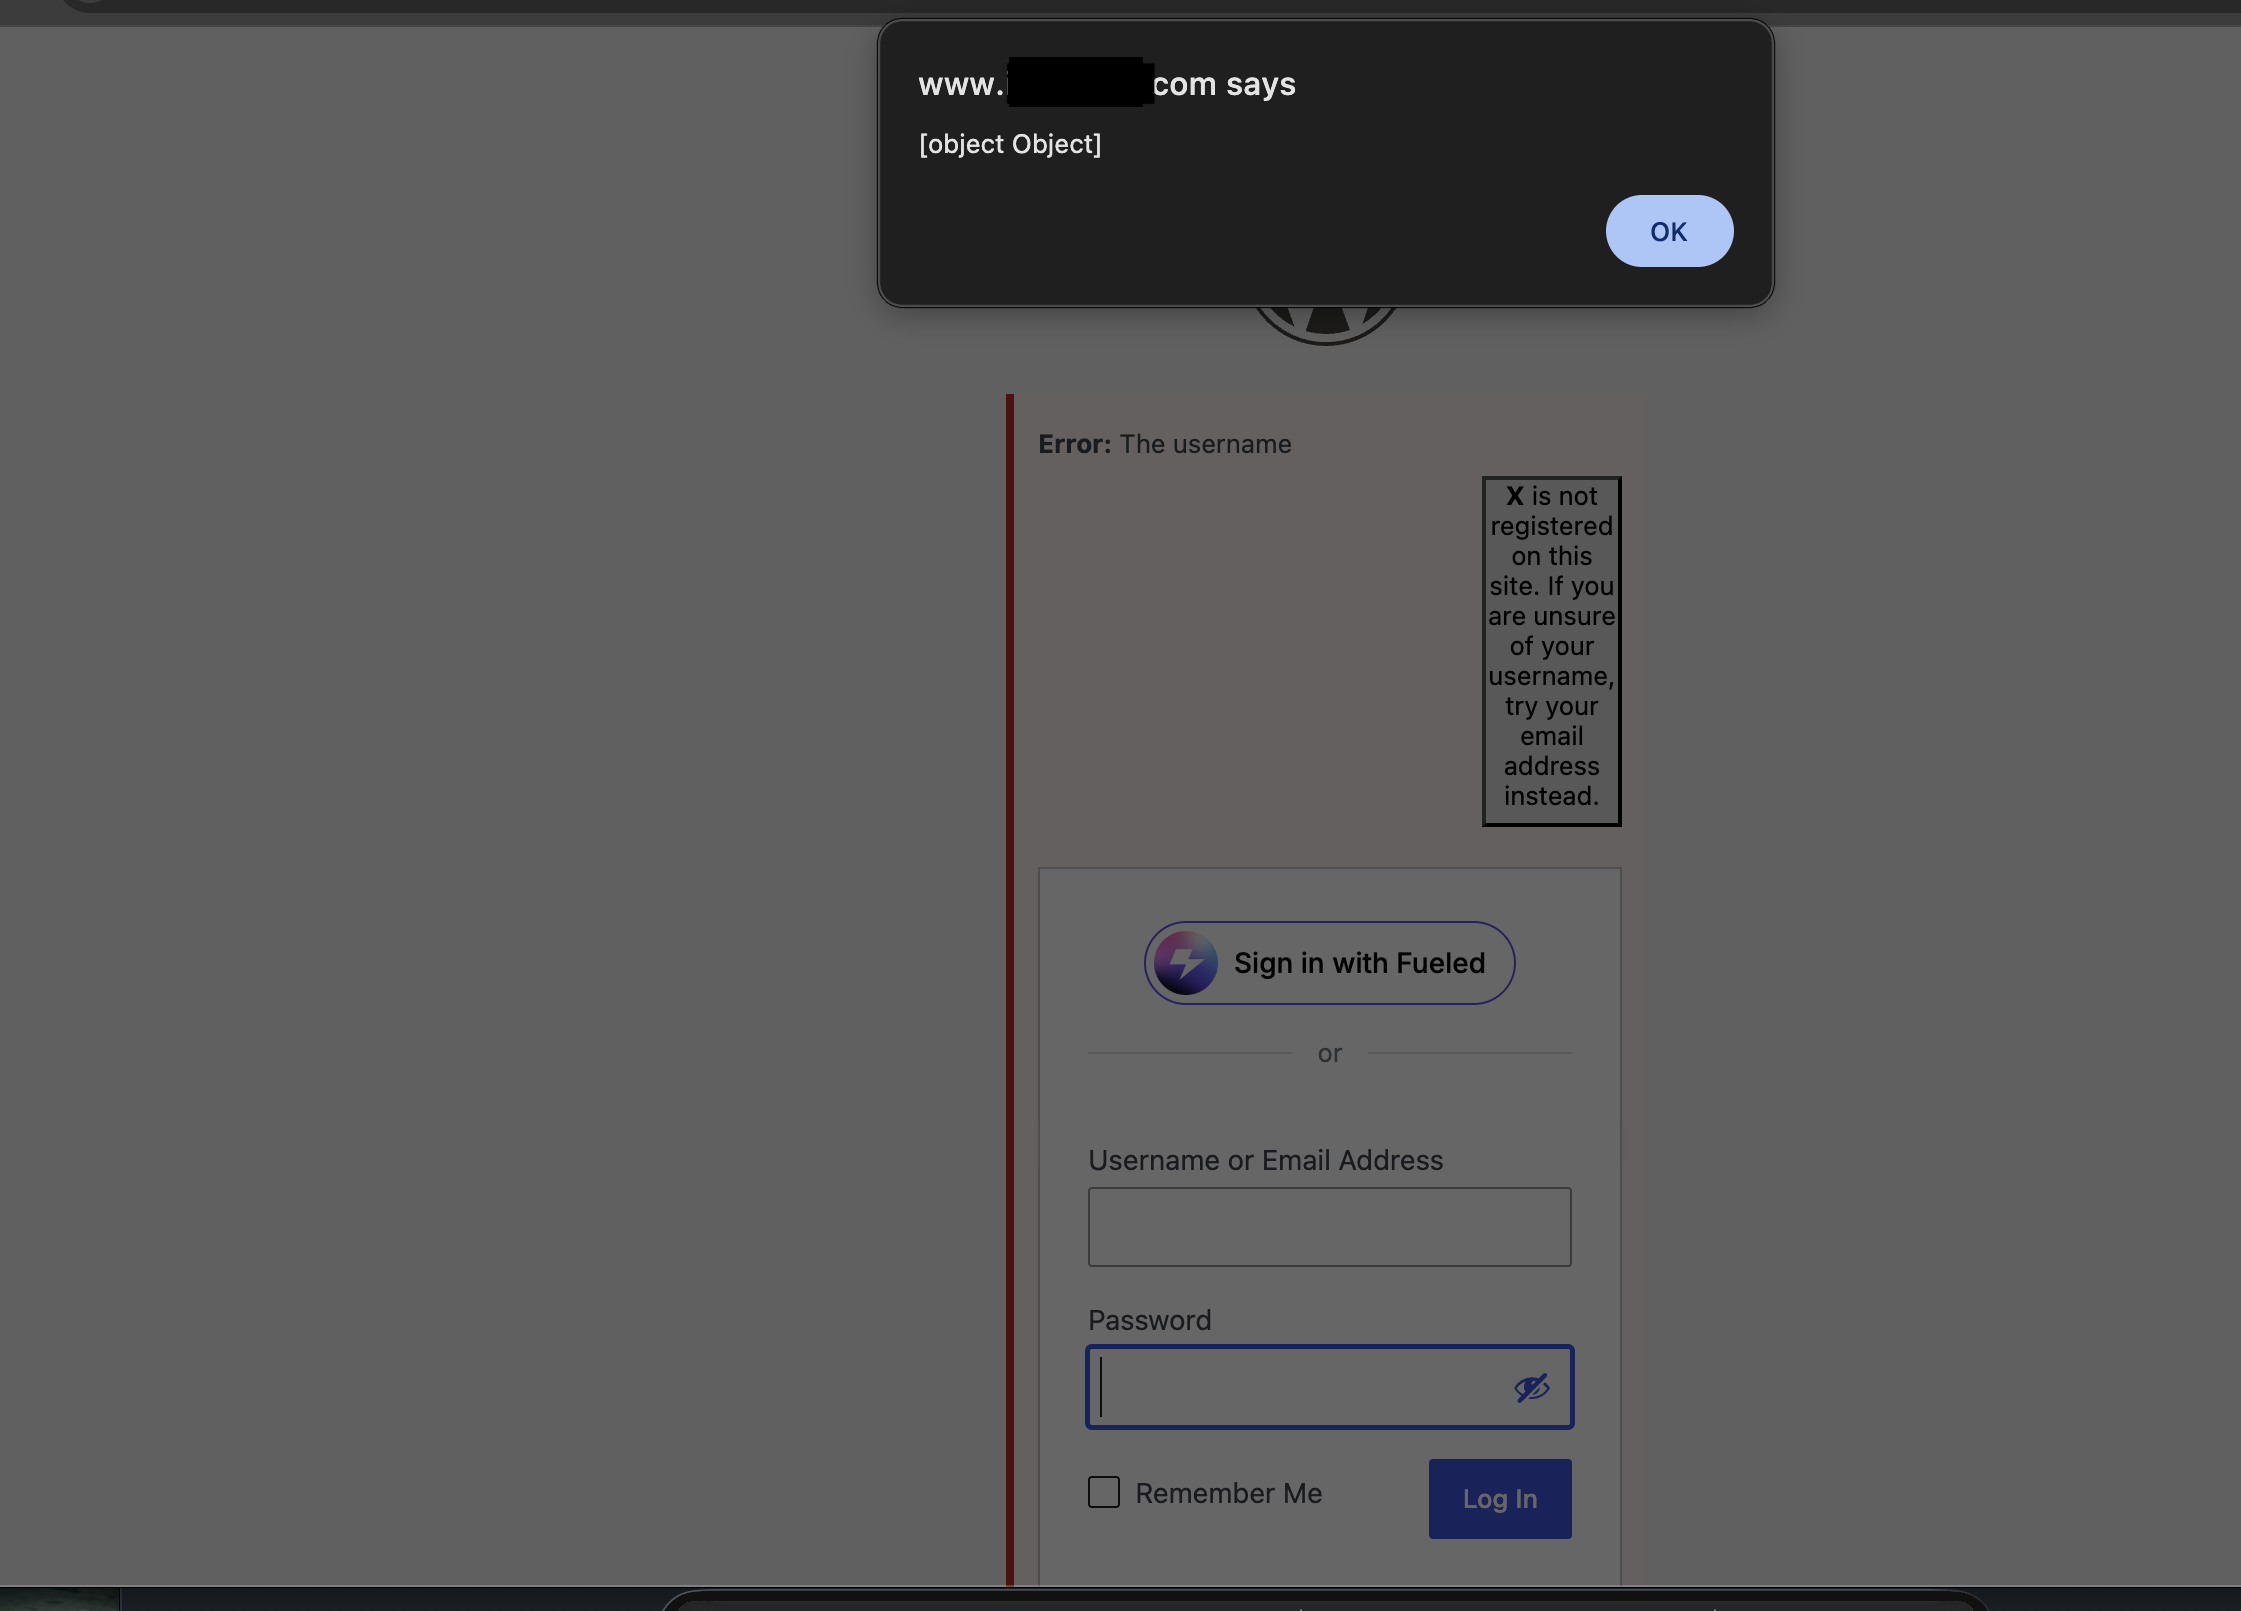
WordPress XSS2Shell flaw enables admin takeover and remote code execution. Users should update to patched versions. Researchers at Pwn just published a report on a vulnerability chain they’re calling XSS2Shell, and the entry point is quite simple: type a username that doesn’t exist, and WordPress echoes it back with a tiny formatting flaw baked into […]
 Pierluigi Paganini
August 07, 2026
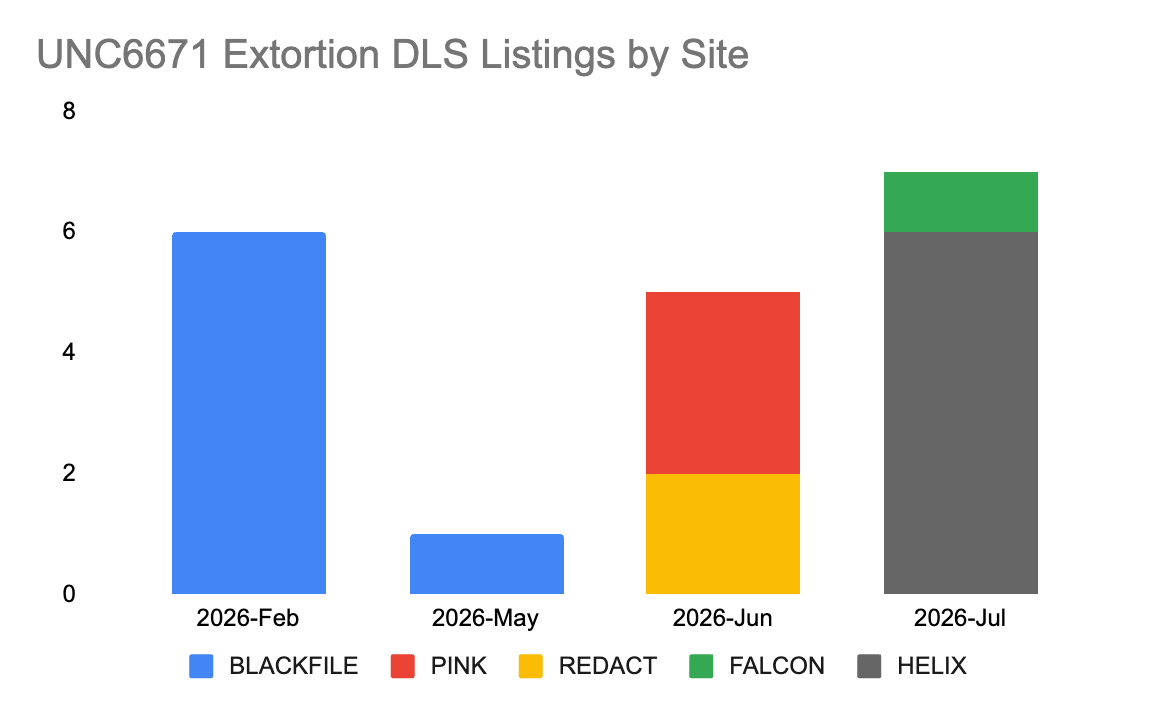
Hackers used fake IT help desks to steal MFA credentials, targeting over 200 firms, including major financial companies. A hacking campaign operating under names including Redact, Pink, Falcon, and Helix has built credential-stealing websites targeting employees at Blackstone, Bridgewater Associates, Apollo Global Management, Bain Capital, KKR, TPG, CME Group, Clearlake Capital, and Moody’s, among dozens […]
 Pierluigi Paganini
August 07, 2026
Meta was ordered to pay $567M after a judge ruled its platforms harmed children, bringing New Mexico penalties to $942M. Meta ‘s child-safety legal bill just got another half-billion dollars heavier. A New Mexico state judge ruled that company’s platforms constitute a “public nuisance,” the BBC reports, ordering $567 million into a fund meant to […]
 Pierluigi Paganini
August 07, 2026
A hidden backdoor in 20 router models lets remote servers execute commands as root, putting affected devices at risk of takeover. Jacob Baines had a router on his desk that kept trying to call home, and it wasn’t supposed to. VulnCheck researchers found a backdoor baked into Zbtlink routers, and it’s not the kind of […]