 Pierluigi Paganini
 April 21, 2014
Which are the security improvements in the critical update proposed by criminal ecosystem for P2P Zeus Botnet? Fortinet experts detected and analyzed it. Security experts at Fortinet have uncovered a critical update proposed by criminal ecosystem for P2P Zeus Botnet. The first P2P Zeus variant was uncovered by Trusteer firm a couple of years ago, it was used […]
 Pierluigi Paganini
April 07, 2014
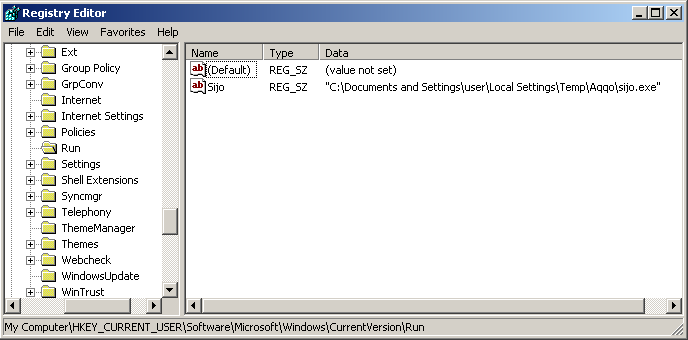
Security researchers at Comodo have detected a new Zeus trojan variant enhanced with digital signature of its source code to avoid detection. The security community is once again menaced by Zeus banking trojan, a new variant of the malicious ZeuS Trojan has been identified by researchers at Comodo AV labs. This instance presents an interesting feature, it is […]
 Pierluigi Paganini
March 27, 2014
Security experts at F-Secure have detected a new variant of Gameover ZeuS financial Trojan which is targeting recruitment websites. Zeus Trojan is probably one of the most prolific and long-lived malware, security firms have discovered in the last years numerous variant even more sophisticated. After the public release of it source code, principal security firms have […]
 Pierluigi Paganini
February 08, 2014
Security experts at AppRiver detected a traffic spam spike linked to a new malware Campaign Targeting customers of Bank of America. Bank of America is being targeted by a new malicious campaign, cybercriminals are spreading a stealthy malicious financial malware to hit the clients of the financial institution. Security experts at AppRiver recently detected and blocked a set of […]
 Pierluigi Paganini
February 04, 2014
Security experts at Malcovery firm have detected a new Zeus variant bypassing the security traditional defenses with the usage of encryption. Zeus malware is hard to die, the availability of its source code in the wild caused periodically the born of a new variant, even more resistant and sophisticated. Over the years, we saw variants […]
 Pierluigi Paganini
January 20, 2014
Financial Supervisory Service confirmed that Stolen credit card data of at least 20 million bank and credit card users in South Korea has been leaked. While US are facing with a series of clamorous data breached against principal retailers, in South Korea an employee of personal credit ratings firm Korea Credit Bureau (KCB) has been […]
 Pierluigi Paganini
December 31, 2013
Two German researchers at the last Chaos Computing Congress in Hamburg revealed how cyber thieves steal money from ATMs win infected USB Sticks. Cyber criminals are exploiting new techniques to attack ATMs (Automated Teller Machines) infecting the devices with specifically crafted malware. Security researchers discovered a new series of attacks against ATMs, the criminals cut […]
 Pierluigi Paganini
December 11, 2013
Security researchers at Kaspersky Lab have detected a 64-bit Zeus banking trojan version enhanced with communication capability on the Tor network. Is Zeus banking trojan dead? Absolutely no! Periodically security experts found new a variant that includes new features to make it more resilient and able to spread itself via social networks. Last variant was […]
 Pierluigi Paganini
December 05, 2013
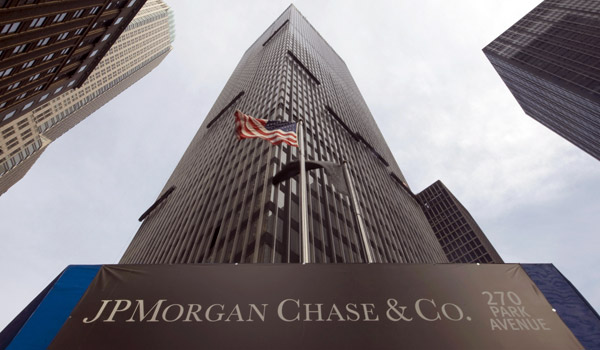
JPMorgan Chase & Co has recently announced to have suffered a cyber attack in July that exposed 465,000 card users to data loss. JPMorgan Chase & Co has announced that it was the victim of a cyber attack and warned around 465,000 of its holders of prepaid cash cards on the possible exposure of their […]
 Pierluigi Paganini
November 22, 2013
Trusteer researchers have uncovered a sneaky piece of financial malware, known as i2Ninja, being sold on a Russian cyber crime forum. A new financial malware dubbed i2Ninja menaces banking, despite it has yet to be discovered in the wild, researchers at the IBM company Trusteer have found a sneaky piece of the malicious code on […]