 Pierluigi Paganini
 March 03, 2021
Avast researchers reported that the infamous Ursnif Trojan was employed in attacks against at least 100 banks in Italy. Avast experts recently obtained information on possible victims of Ursnif malware that confirms the interest of malware operators in targeting Italian banks. Operators behind this attacks have stolen financial data and credential from targeted financial institutions. “Among the […]
 Pierluigi Paganini
February 16, 2021
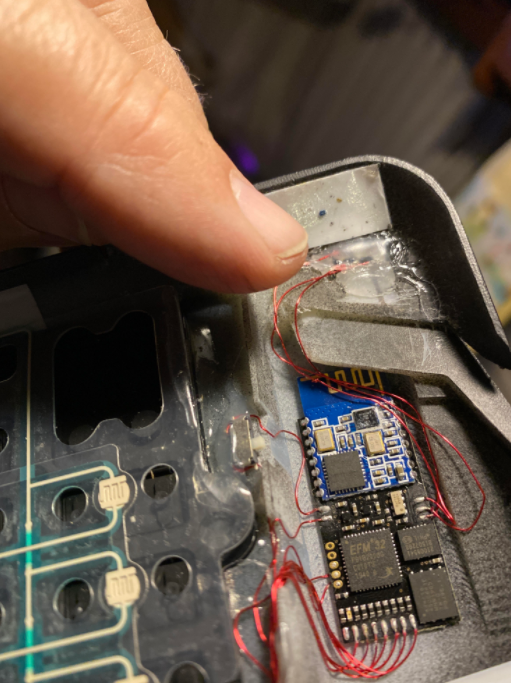
Experts discovered a new Bluetooth overlay skimmer that interferes with the ability of the terminal to read chip-based cards, forcing the use of the stripe. The popular investigator Brian Krebs reported the discovery of a new Bluetooth overlay skimmer that interfered with the terminal’s ability to read chip-based cards, forcing the use of the magnetic […]
 Pierluigi Paganini
January 02, 2021
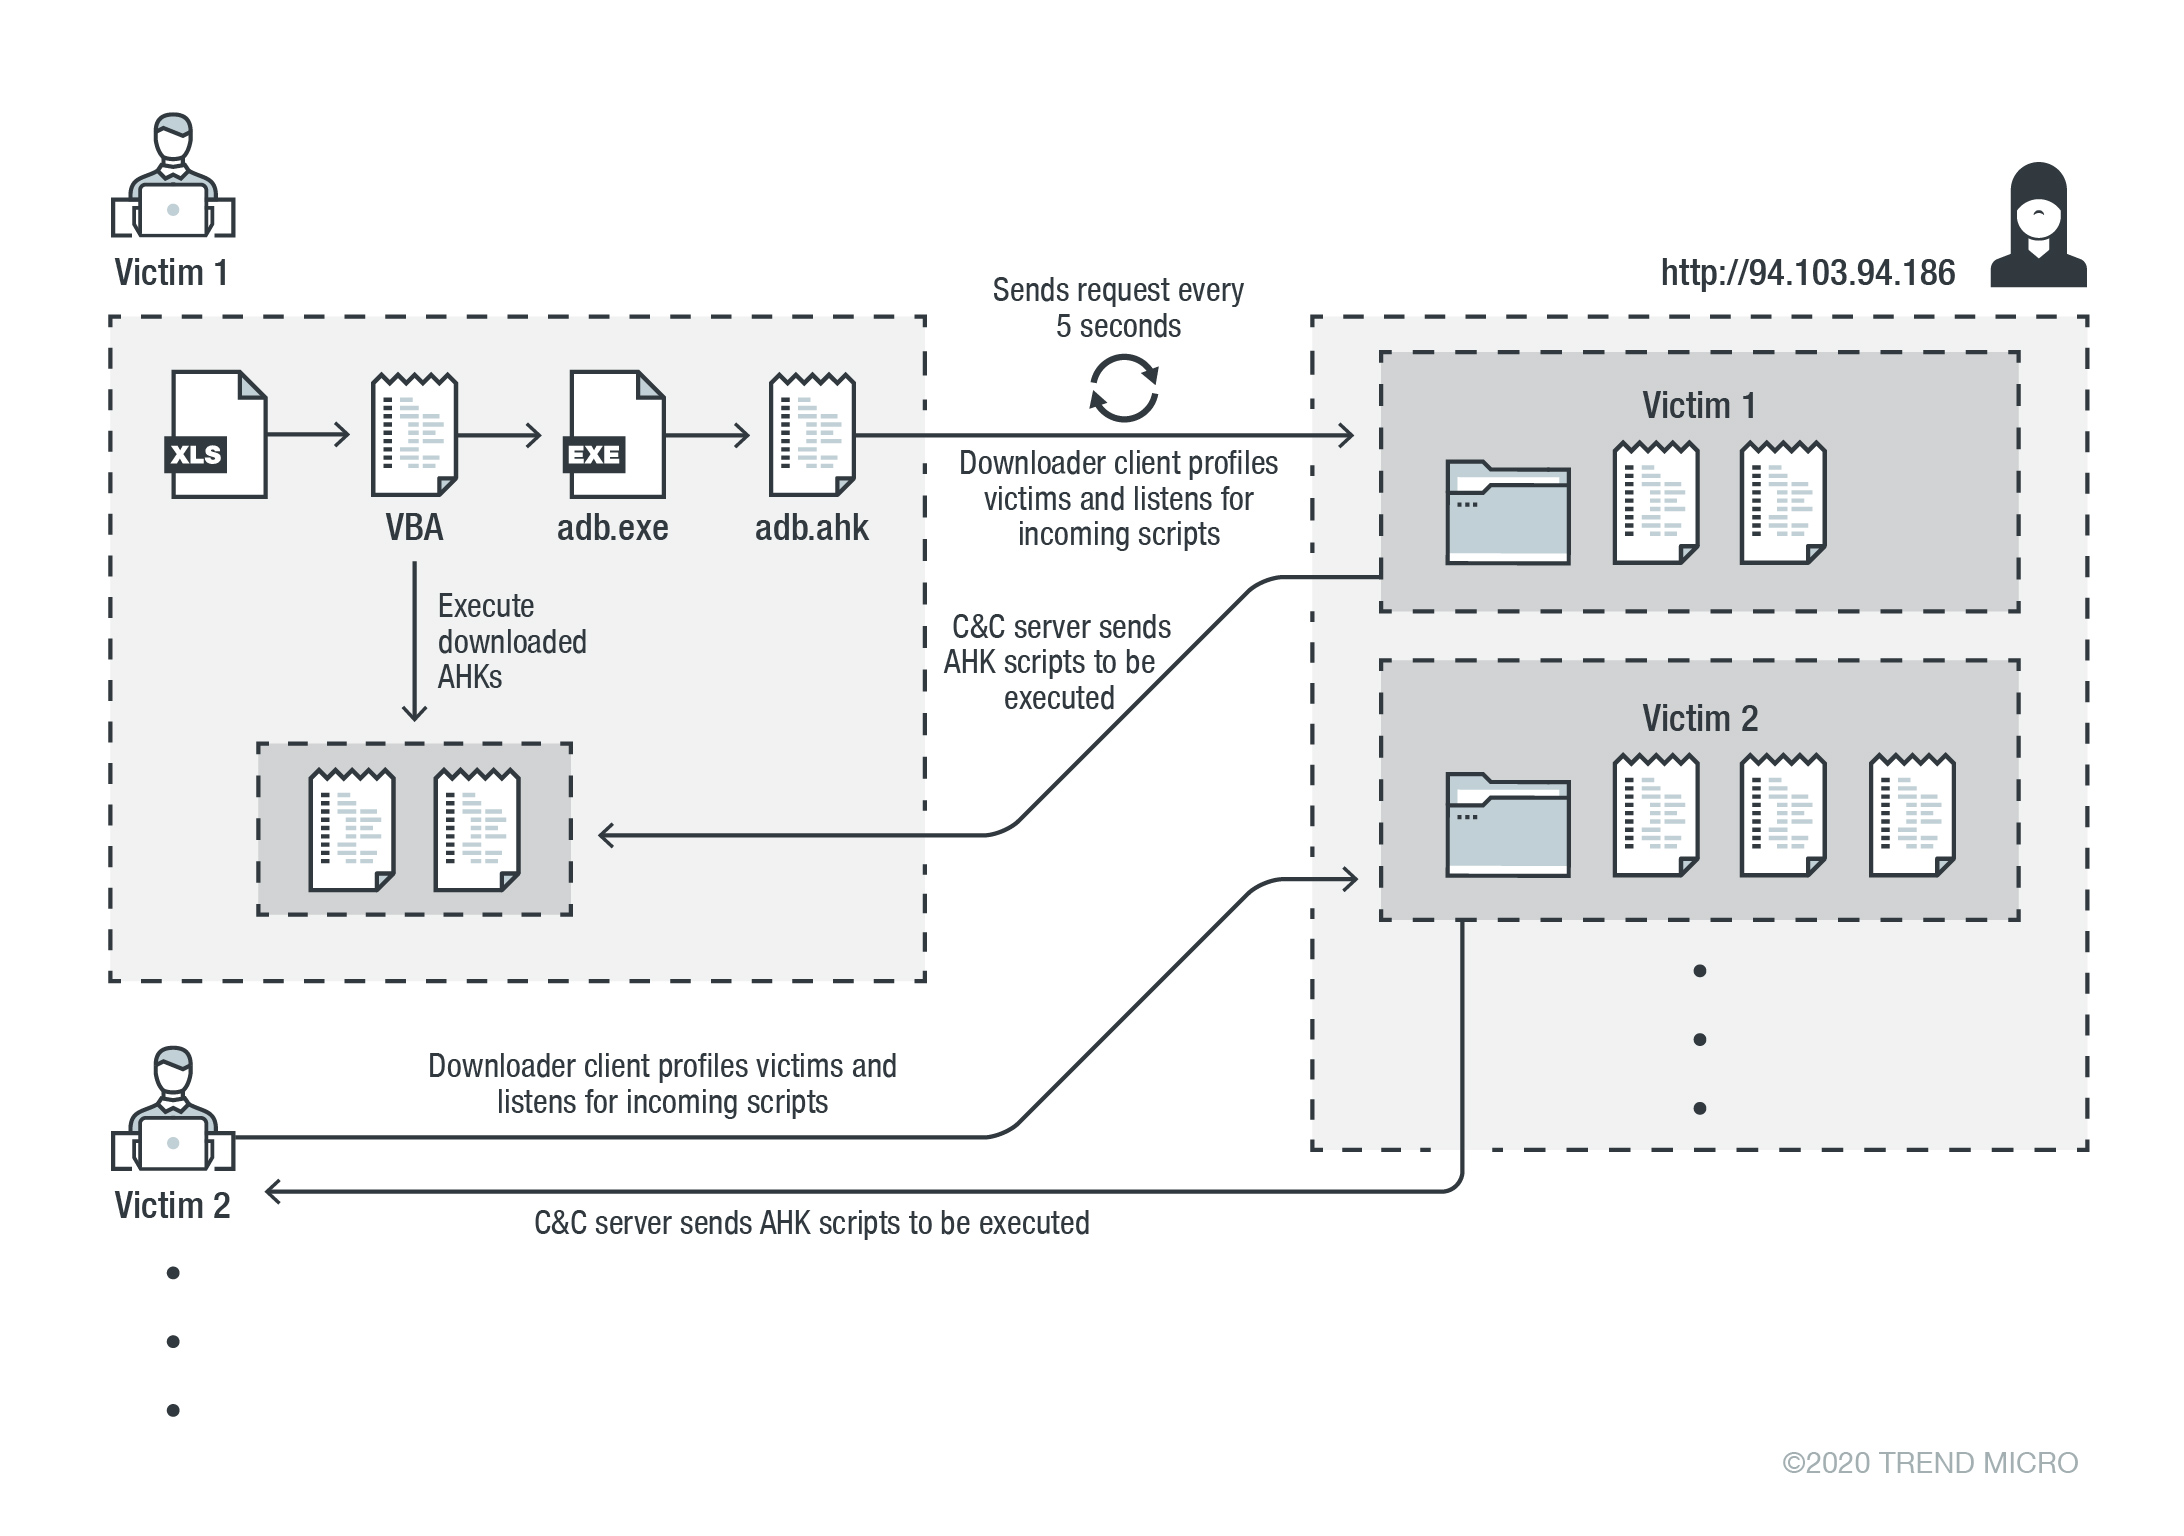
Experts spotted a new credential stealer written in AutoHotkey (AHK) scripting language that is targeting the US and Canadian bank customers. Security experts from Trend Micro have discovered a new credential stealer written in AutoHotkey (AHK) scripting language that is targeting the US and Canadian bank customers as part of an ongoing campaign that has […]
 Pierluigi Paganini
December 20, 2020
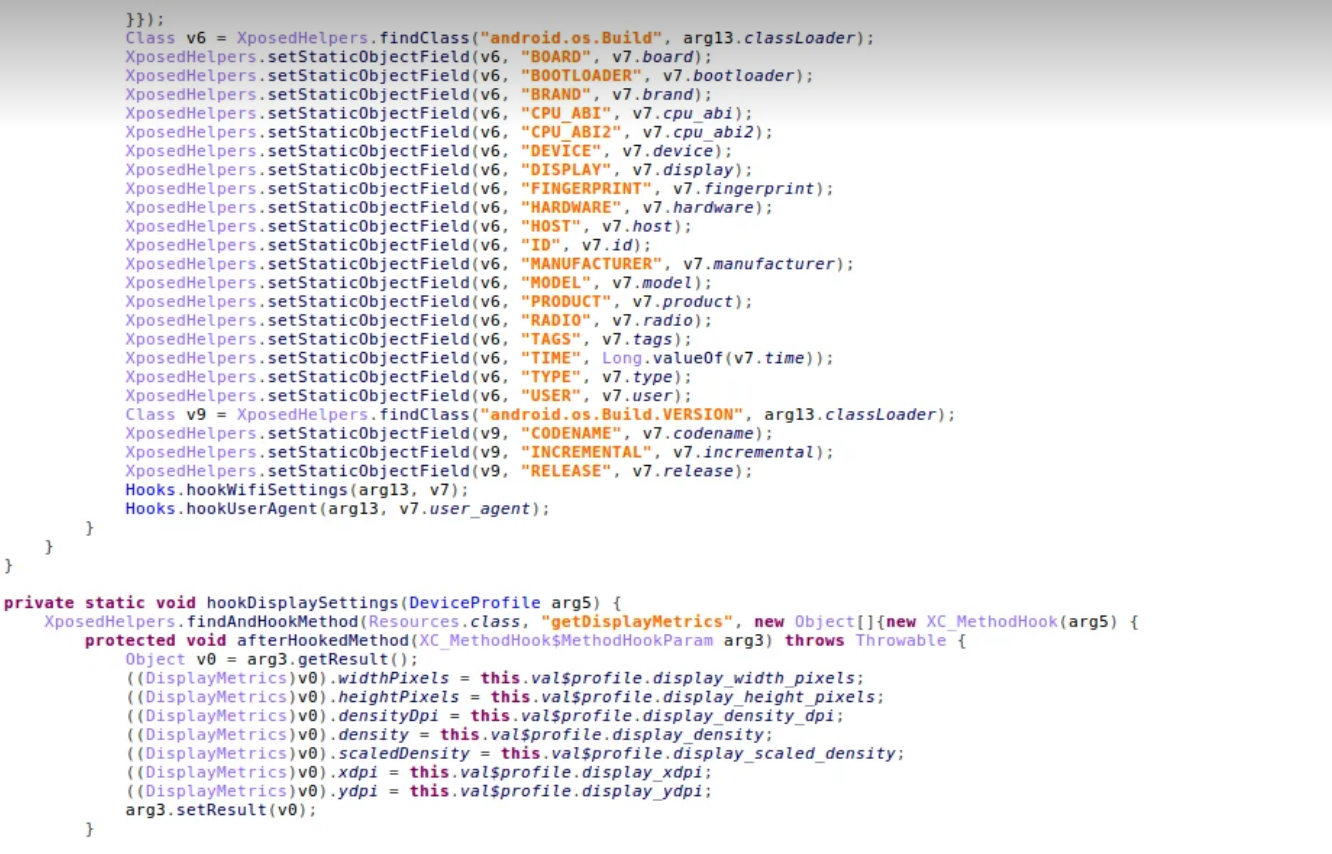
Experts uncovered a massive fraud operation that used a network of mobile device emulators to steal millions of dollars from online bank accounts. Researchers from IBM Trusteer have uncovered a massive fraud operation that leveraged a network of mobile device emulators to steal millions of dollars from online bank accounts in a few days. The […]
 Pierluigi Paganini
November 29, 2020
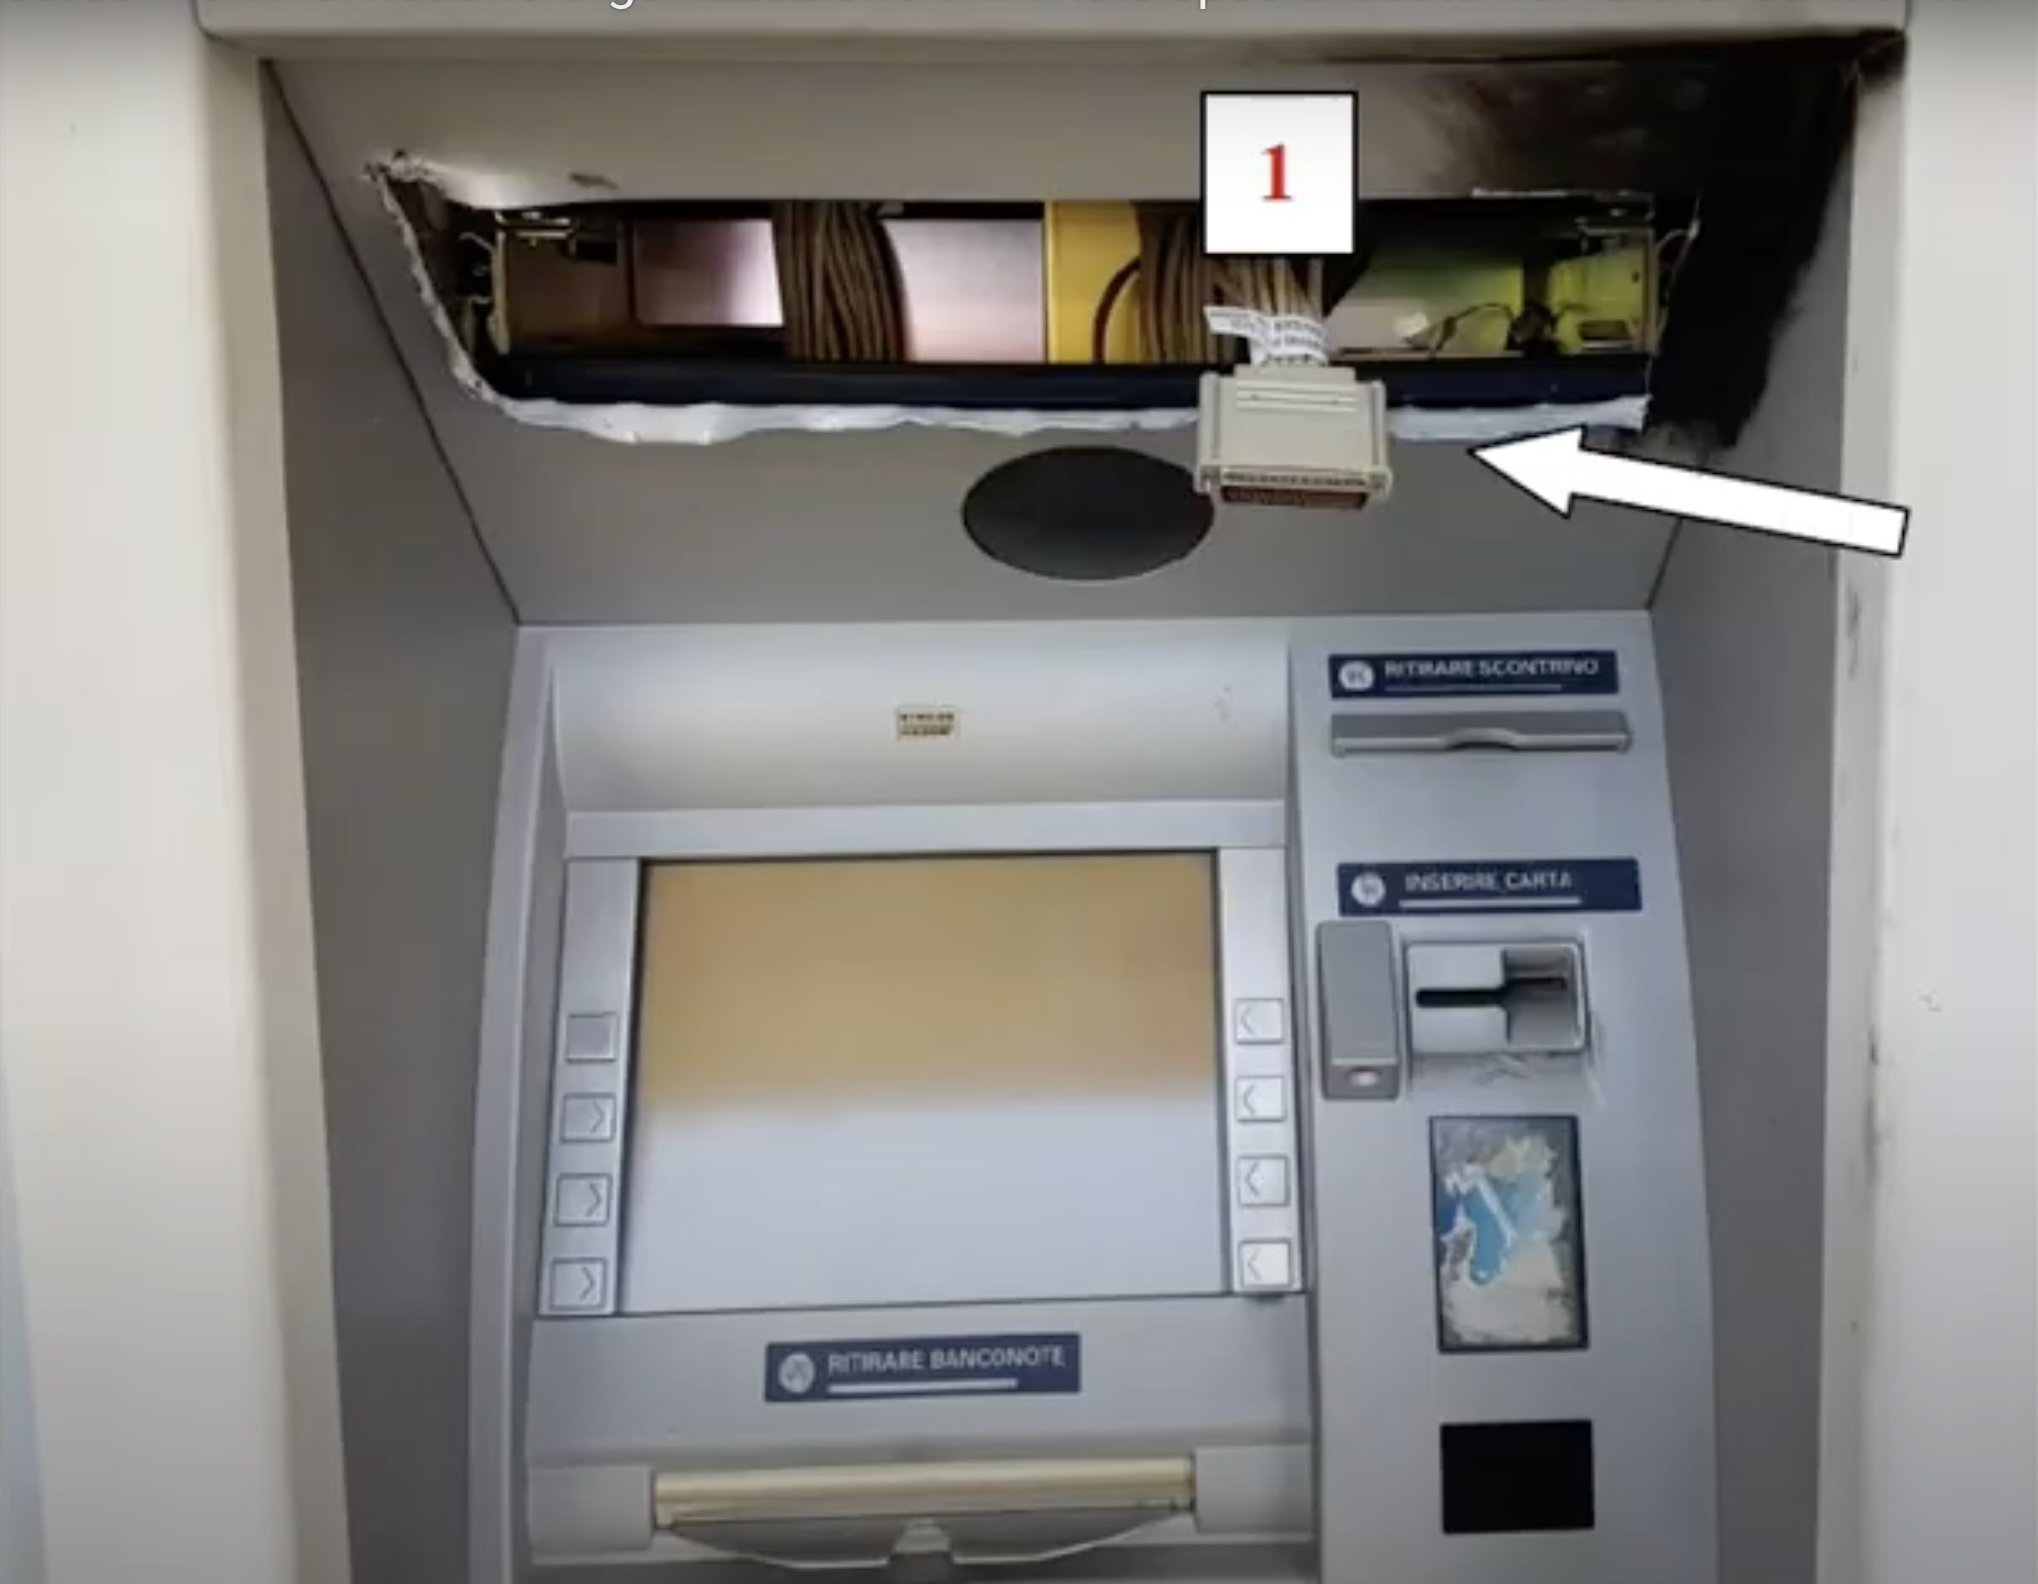
A cyber criminal organization has stolen money from at least 35 Italian ATMs with a black box attack technique. A criminal organization has stolen money from at least 35 ATMs and Post Office cash dispensers operated by Italian banks with a new black box attack technique. The Carabinieri of Monza dismantled by the gang, the […]
 Pierluigi Paganini
September 24, 2020
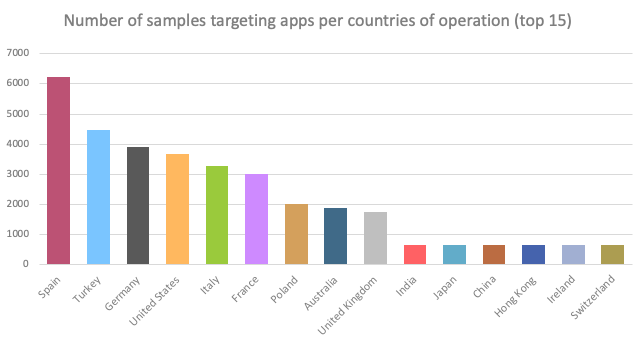
Security researchers spotted a new strain of Android malware, dubbed Alien, that implements multiple features allowing it to steal credentials from 226 apps. Researchers from ThreatFabric have discovered and analyzed a new strain of Android malware, tracked as Alien, that implements multiple features allowing it to steal credentials from 226 applications. Alien first appeared in […]
 Pierluigi Paganini
August 29, 2020
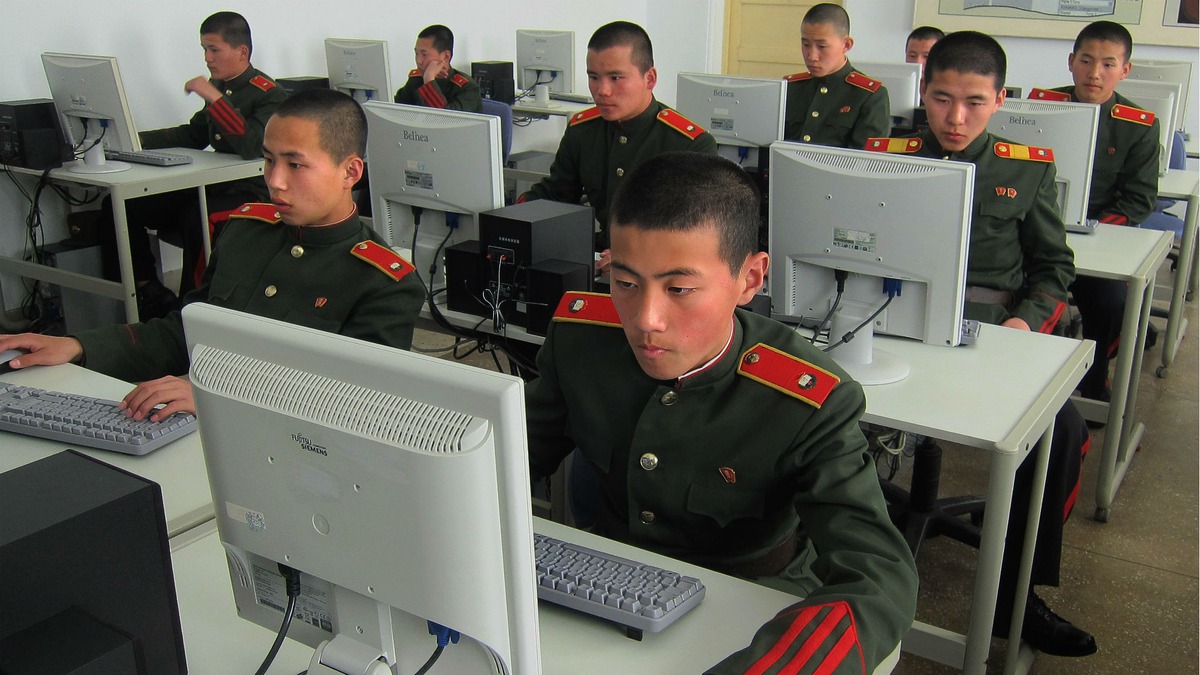
North Korea-linked APT group BeagleBoyz intensified its operations since February, US CISA, Department of the Treasury, FBI, and USCYBERCOM warn. According to a joint advisory issued by the Cybersecurity and Infrastructure Security Agency (CISA), the Department of the Treasury, the Federal Bureau of Investigation (FBI), and U.S. Cyber Command (USCYBERCOM) North Korea-linked APT group BeagleBoyz […]
 Pierluigi Paganini
August 22, 2020
The ATM manufacturer giants, Diebold Nixdorf and NCR, have released software updates to fix a flaw that could have been exploited for ‘deposit forgery’ attacks The ATM manufacturers Diebold Nixdorf and NCR have addressed a bug that could have been exploited for ‘deposit forgery’ attacks The flaws that could have allowed crooks to modify the […]
 Pierluigi Paganini
July 19, 2020
ATM maker Diebold Nixdorf is warning banks a new ATM black box attack technique that was recently employed in cyber thefts in Europe. Black box attacks are a type of jackpotting attack aimed at forcing an ATM to dispense the cash by sending a command through a “black box” device. In this attack, a black box […]
 Pierluigi Paganini
July 08, 2020
Experts found a tainted app in the Google Play store that was downloaded by more than 10,000 users and that was delivering the Cerberus banking Trojan. Researchers from AVAST have discovered a currency converter application in the Google Play store that was downloaded by more than 10,000 users and that was designed to deliver the […]
Malware / November 17, 2026