 Pierluigi Paganini
 June 05, 2018
Two months after the release of the security updates for the drupalgeddon2 flaw, experts continue to see vulnerable websites running on flawed versions of Drupal that hasn’t installed security patches. In March, the Drupal developers Jasper Mattsson discovered a “highly critical” vulnerability, tracked as CVE-2018-7600, aka drupalgeddon2, affecting Drupal 7 and 8 versions. Both Drupal 8.3.x and 8.4.x are […]
Pierluigi Paganini
May 21, 2018
Crooks are exploiting known vulnerabilities in the popular Drupal CMS such as Drupalgeddon2 and Drupalgeddon3 to deliver cryptocurrency miners, remote administration tools (RATs) and tech support scams. Security experts at Malwarebytes reported that compromised Drupal websites are used to deliver cryptocurrency miners, remote administration tools (RATs) and tech support scams. Crooks are exploiting known vulnerabilities in the […]
 Pierluigi Paganini
May 08, 2018
Recently security experts discovered two critical vulnerabilities in the Drupal CMS (CVE-2018-7600 and CVE-2018-7602), and cybercriminals promptly attempted to exploit them in the wild. The hackers started using the exploits for the above vulnerabilities to compromise drupal installs, mostly cryptocurrency mining. It has been estimated that potentially over one million Drupal websites are vulnerable to cyber attacks […]
Pierluigi Paganini
April 26, 2018
The new flaw tracked as CVE-2018-7602, is a highly critical remote code execution issue, Drupal team fixed it with the release of versions 7.59, 8.4.8 and 8.5.3. Drupal team has released updates for versions 7 and 8 of the popular content management system (CMS) to address the recently disclosed CVE-2018-7600 Drupalgeddon2 flaw. The new flaw tracked as CVE-2018-7602, is a highly […]
 Pierluigi Paganini
April 19, 2018
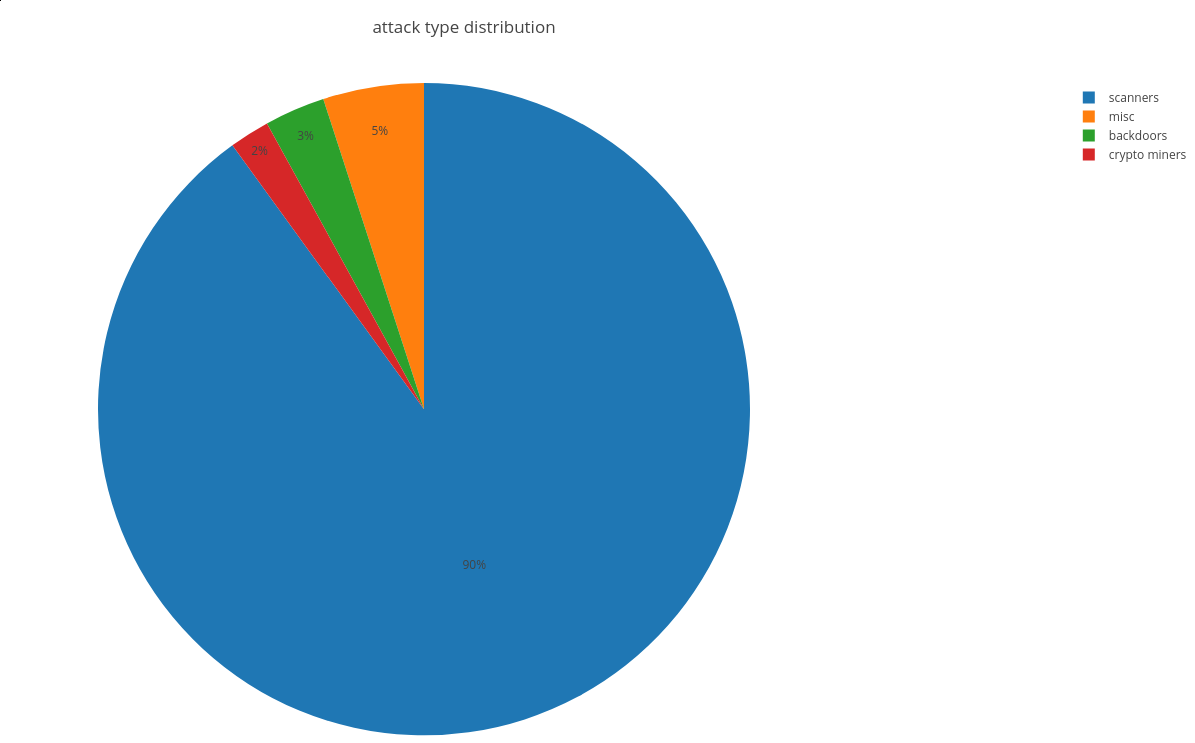
After the publication of a working Proof-Of-Concept for Drupalgeddon2 on GitHub experts started observing attackers using it to deliver backdoors and crypto miners. At the end of March, the Drupal Security Team confirmed that a “highly critical” vulnerability (dubbed Drupalgeddon2), tracked as CVE-2018-7600, was affecting Drupal 7 and 8 core and announced the availability of security updates on March 28th. The […]
Pierluigi Paganini
April 13, 2018
After the publication of a working Proof-Of-Concept for Drupalgeddon2 on GitHub for “educational or information purposes,” experts started observing bad actors attempting to exploit the flaw. At the end of March, the Drupal Security Team confirmed that a “highly critical” vulnerability (dubbed Drupalgeddon2), tracked as CVE-2018-7600, was affecting Drupal 7 and 8 core and announced the availability of security updates on […]
Pierluigi Paganini
March 29, 2018
The Drupal development team has fixed the drupalgeddon2 vulnerability that could be exploited by an attacker to take over a website. A few days ago, Drupal Security Team confirmed that a “highly critical” vulnerability, tracked as CVE-2018-7600, affects Drupal 7 and 8 core and announced the availability of security updates on March 28th. The vulnerability was discovered […]
Pierluigi Paganini
February 23, 2018
The Drupal development team addressed many vulnerabilities in both Drupal 8 and 7, including some flaws rated as “critical”. Drupal maintainers have fixed many vulnerabilities in Drupal 7 and 8, including some flaws rated as “critical.” One of the critical security vulnerabilities is related to partial cross-site scripting (XSS) prevention mechanisms that was addressed with Drupal 8.4.5 and 7.57 […]
Pierluigi Paganini
June 22, 2017
Drupal team released security updates to fix several vulnerabilities, including the critical access bypass flaw CVE-2017-6922 exploited in spam campaigns. The Drupal development team has released security updates to fix several vulnerabilities, including the critical access bypass flaw tracked as CVE-2017-6922 that has been exploited in spam campaigns. The CVE-2017-6922 flaw was fixed with the […]
Pierluigi Paganini
April 19, 2017
A critical vulnerability affects the Drupal References module that is used by hundreds of thousands of websites using the popular CMS. The Drupal security team has discovered a critical vulnerability in a third-party module named References. The Drupal team published a Security advisory on April 12 informing its users of the critical flaw. The flaw has a huge impact on […]
Data Breach / November 17, 2026
Malware / November 17, 2026