


 Pierluigi Paganini
 October 01, 2026
Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it’s not going straight to the public. It’s rolling out first to a set of trusted cyber defenders through what Google calls the Fairwind Program, which […]
 Pierluigi Paganini
October 01, 2026
Apple patched a CoreGraphics zero-day that may have been exploited in targeted attacks. A public PoC for the flaw is now available. Apple patched a zero-day vulnerability, tracked as CVE-2026-86950, in CoreGraphics that attackers may have exploited to target specific individuals. The flaw is an out-of-bounds write that can lead to arbitrary code execution when […]
 Pierluigi Paganini
October 01, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Catalyst SD-WAN Manager flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Catalyst SD-WAN Manager flaw, tracked as CVE-2026-76504 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability resides in Cisco Catalyst SD-WAN Manager’s […]
 Pierluigi Paganini
October 01, 2026
DIVD was breached through two Zammad zero-days that let an AI agent reach root in seconds, steal data and pivot to other services before being stopped. The Dutch Institute for Vulnerability Disclosure, a nonprofit organization of volunteer security researchers whose whole job is finding and responsibly disclosing vulnerabilities in other people’s software, just disclosed that […]
 Pierluigi Paganini
September 30, 2026
WatchGuard fixes 15 Fireware OS flaws, including a critical RCE bug that could give attackers root access to vulnerable Firebox appliances. WatchGuard has released security updates for Fireware OS that address 15 vulnerabilities, including a critical code injection flaw, tracked as CVE-2026-86131 (CVSS score of 9.2), that could allow an attacker to execute commands with […]
 Pierluigi Paganini
September 30, 2026
DOJ charges against Oxygen Forensics reveal the Russian-linked firm also sold forensic software to EU projects and European police forces for years. Last week’s Justice Department indictment of Oxygen Forensics looked, at first, like an American procurement scandal. CEO Lee Reiber and Russian co-founder Oleg Davydov stand accused of hiding that the company was Russian-owned […]
 Pierluigi Paganini
September 30, 2026
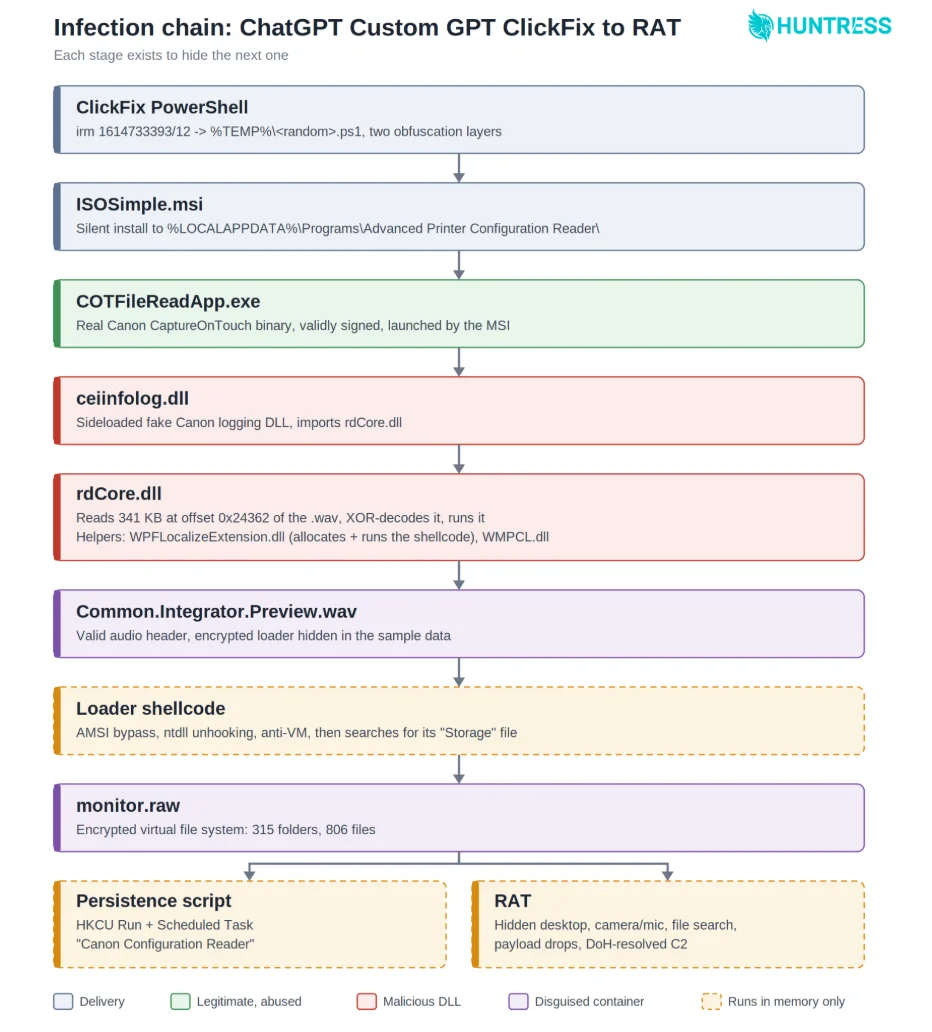
Threat actors abused fake ChatGPT Custom GPTs and ClickFix to deliver a multi-stage RAT. ChatGPT’s Custom GPT feature is the latest legitimate surface being turned into a delivery mechanism, and Huntress researchers caught it in action across at least 40 incidents. A Custom GPT (now simply called a GPT) is essentially a version of ChatGPT […]
Pierluigi Paganini
September 30, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple Multiple Products flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple Multiple Products flaw, tracked as CVE-2026-86950 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Apple has released security updates for iOS, iPadOS […]
 Pierluigi Paganini
September 30, 2026
Mandiant and GTIG detail active exploitation of a Citrix NetScaler zero-day, deploying custom web shells WHIPSHOT and SLAPSHOT for root access. Mandiant and Google Threat Intelligence Group caught active exploitation of a zero-day in Citrix NetScaler ADC and Gateway appliances in late September 2026. The bug, tracked as CVE-2026-88772 (CVSS score of 9.5), has been […]
 Pierluigi Paganini
September 29, 2026
Keio, a major Japanese railway operator, was hit by ransomware, disrupting business systems and forcing the company to shut down its network. Keio Corporation, one of Japan’s major private railway operators, was hit by a ransomware attack over the weekend, disrupting some of its business systems. The company detected a system failure early Saturday and […]






