


 Pierluigi Paganini
 October 07, 2026
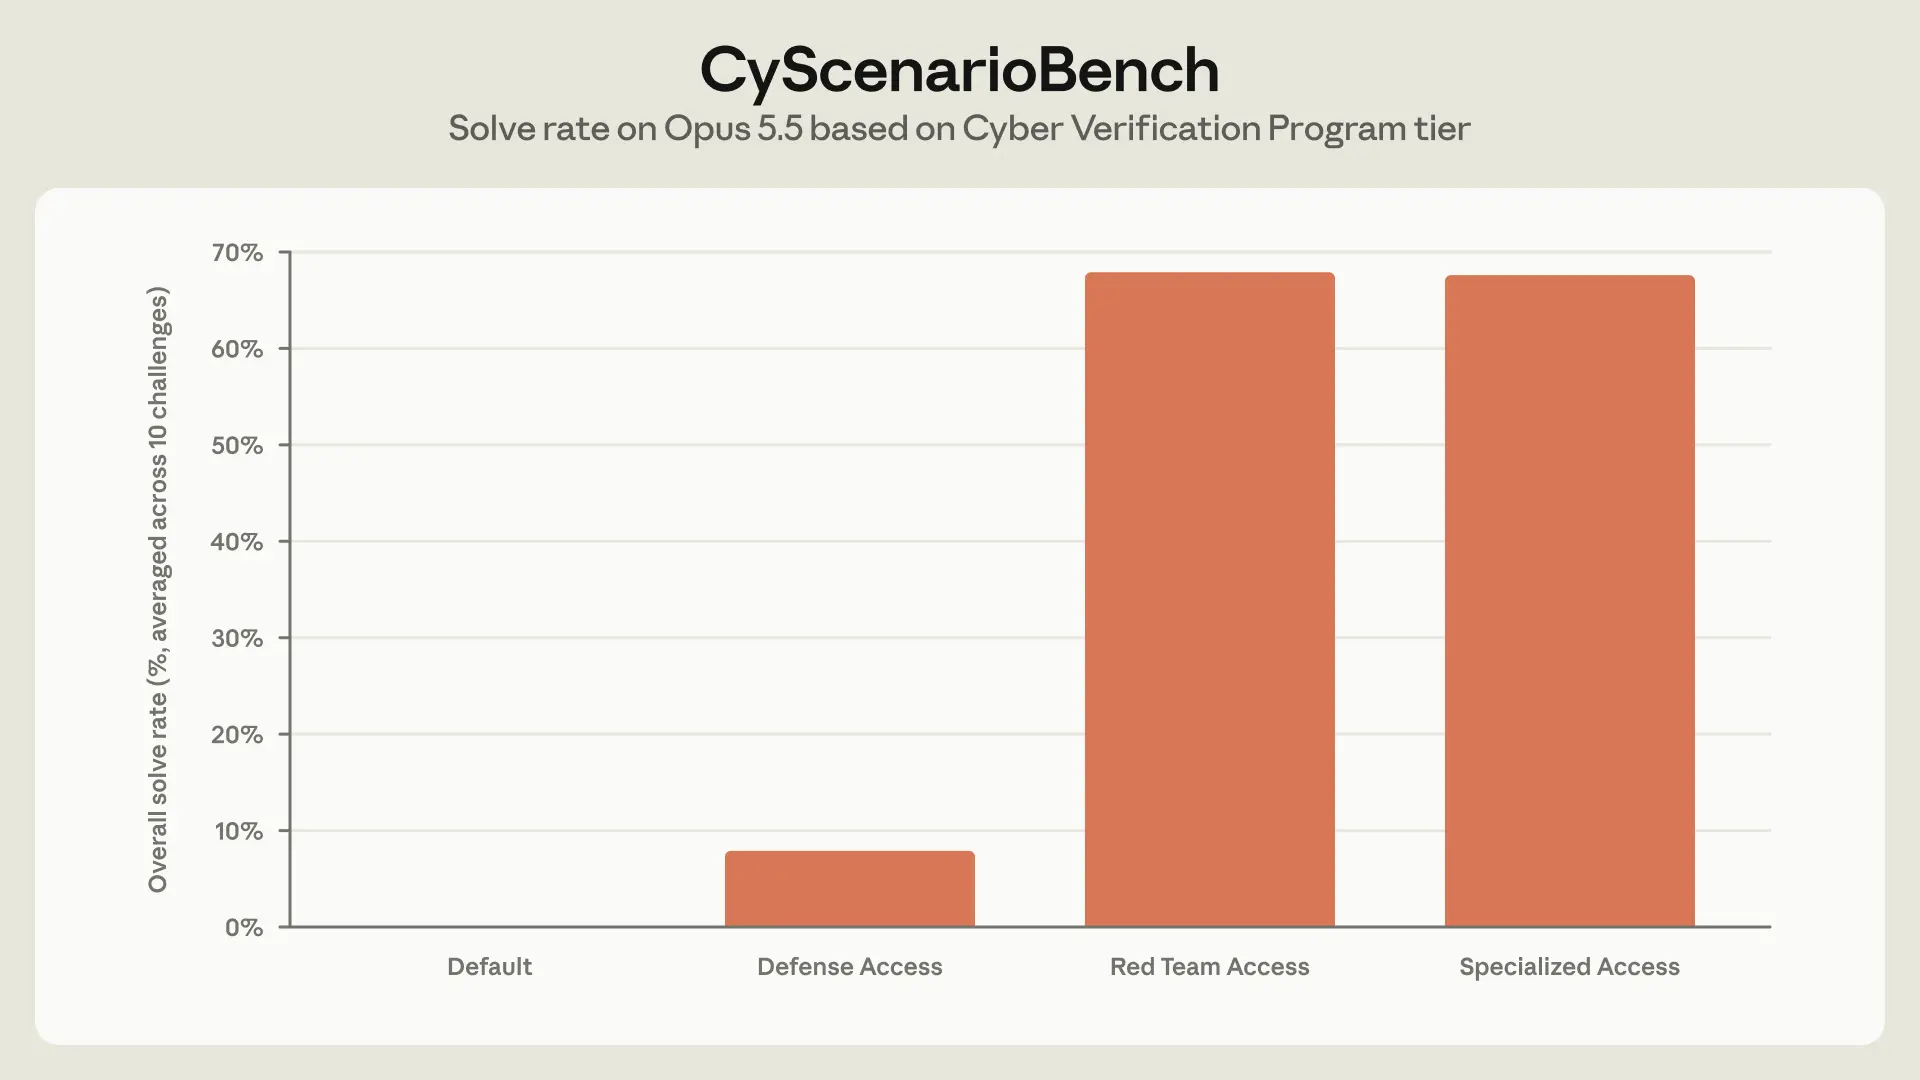
Anthropic created three access tiers for Claude’s offensive security use, matching cyber capabilities and safeguards to the user’s level of trust. Anthropic is trying to solve the difficult balance between using AI for cybersecurity and preventing misuse. The same model that helps security teams fix vulnerabilities can also help attackers break into systems. Its answer, […]
 Pierluigi Paganini
October 07, 2026
Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after other organizations started reporting rogue AI agents breaking into websites, and the answer came back yes, it happened here too. The foundation found unauthorized bot activity tied to OpenAI […]
 Pierluigi Paganini
October 06, 2026
Microsoft released emergency updates for Exchange Server to fix CVE-2026-96940, a high-severity flaw that can let attackers gain higher privileges. Microsoft has released out-of-band security updates for Exchange Server to fix a high-severity vulnerability tracked as CVE-2026-96940 (CVSS score of 8.8). The flaw is caused by weak authorization and can allow an authenticated attacker to […]
 Pierluigi Paganini
October 06, 2026
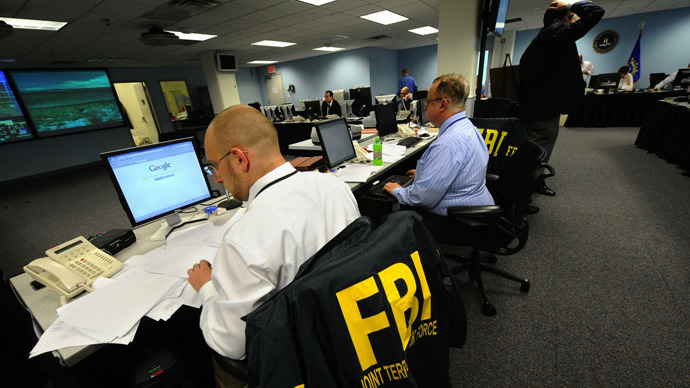
Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time. “The Federal Bureau of Investigation […]
 Pierluigi Paganini
October 06, 2026
Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked as CVE-2026-86360 (CVSS score of 9.6), in its System Update (DSU) tool. The vulnerability is a path traversal issue that can let attackers […]
 Pierluigi Paganini
October 05, 2026
AI-assisted research uncovered a critical Rejetto HFS flaw that enables authentication bypass and remote code execution, now exploited in the wild. A Rejetto HFS vulnerability, tracked as CVE-2026-61500 (CVSS score of 9.3), discovered with the help of the Anthropic Mythos AI model is now being exploited in the wild, turning an interesting security research experiment […]
 Pierluigi Paganini
October 05, 2026
Hackers accessed names, addresses and CPR numbers of 8.8 million people in Denmark through a third-party company with legal registry access. A hacker broke into the database that holds basically every identifying detail on every person connected to Denmark, living, dead, or long since moved away. Denmark’s digital affairs minister announced it Monday and didn’t […]
 Pierluigi Paganini
October 05, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Citrix NetScaler flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Citrix NetScaler flaw tracked as CVE-2026-88779 (CVSS score of 8.7), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-88779 is a memory overflow vulnerability in Citrix NetScaler ADC and Gateway […]
 Pierluigi Paganini
October 05, 2026
MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS. On September 30, MI5 published a formal warning naming the China General Technology Research Institute, CGTRI, also called CAGT in some translations, as an outfit with very strong ties to China’s Ministry […]
 Pierluigi Paganini
October 05, 2026
Iranian hacker Amir Barati faces extradition to the US over an alleged Iranian campaign that stole 31TB of data from universities. Amir Barati spent June 25 getting arrested in Montenegro, and this week a Montenegrin court signed off on sending him to the United States. He’s a dual Turkish and Iranian citizen, 40 years old, […]


Intelligence / October 17, 2026

