 Pierluigi Paganini
 April 04, 2023
Threat actors behind the 3CX supply chain attack have targeted a limited number of cryptocurrency companies with a second-state implant. As of Mar 22, 2023, SentinelOne observed a spike in behavioral detections of the 3CXDesktopApp, which is a popular voice and video conferencing software product. The products from multiple cybersecurity vendors started detecting the popular […]
 Pierluigi Paganini
November 16, 2022
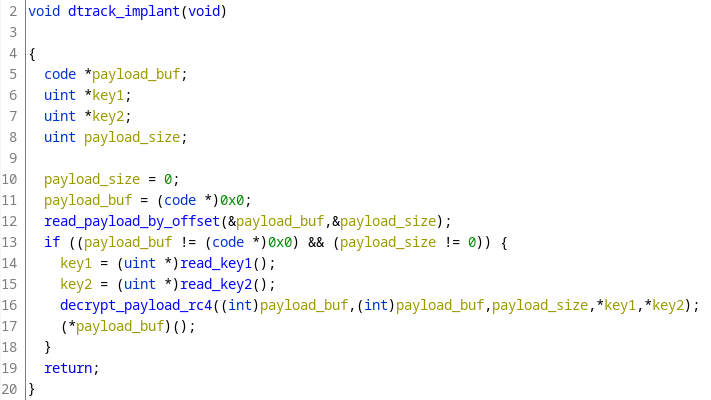
North Korea-linked Lazarus APT is using a new version of the DTrack backdoor in attacks aimed at organizations in Europe and Latin America. North Korea-linked APT Lazarus is using a new version of the DTrack backdoor to attack organizations in Europe and Latin America, Kaspersky researchers warn. DTrack is a modular backdoor used by the […]
 Pierluigi Paganini
October 04, 2022
North Korea-linked Lazarus APT has been spotted deploying a Windows rootkit by taking advantage of an exploit in a Dell firmware driver. The North Korea-backed Lazarus Group has been observed deploying a Windows rootkit by relying on exploit in a Dell firmware driver dbutil_2_3.sys, ESET researchers warn. The discovery was made by ESET researchers while […]
 Pierluigi Paganini
May 07, 2022
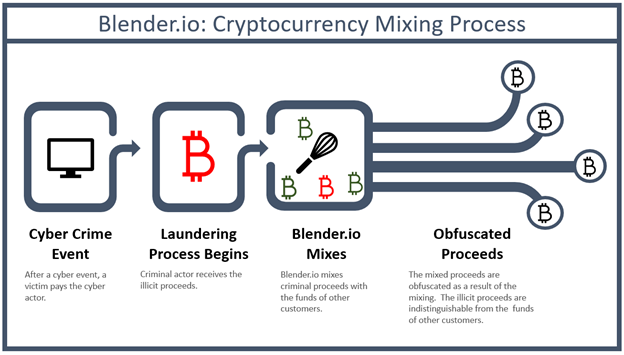
The U.S. Department of Treasury sanctioned cryptocurrency mixer Blender.io used by North Korea-linked Lazarus APT. The U.S. Department of Treasury sanctioned the cryptocurrency mixer Blender.io used by the North Korea-linked Lazarus APT to launder the funds stolen from Axie Infinity’s Ronin bridge. This is the first time ever, Treasury is sanctioning a virtual currency mixer. […]
 Pierluigi Paganini
November 15, 2021
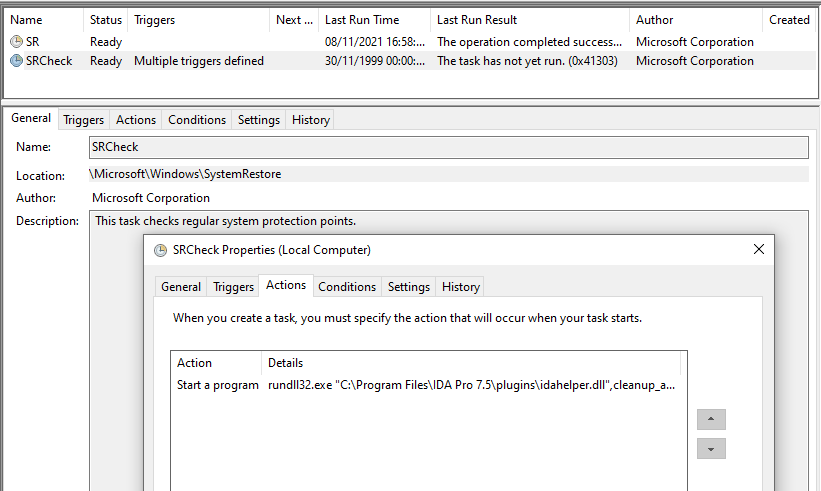
North Korea-linked APT Lazarus targets security researchers using a trojanized pirated version of the popular IDA Pro reverse engineering software. ESET researchers reported that the North Korea-linked Lazarus APT group is targeting cyber security community with a trojanized pirated version of the popular IDA Pro reverse engineering software. Threat actors bundled the IDA Pro 7.5 […]
 Pierluigi Paganini
April 16, 2021
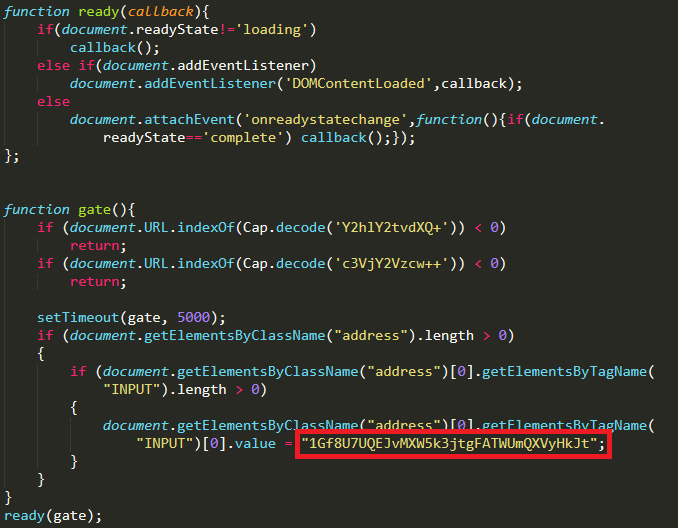
Group-IB observed the North Korea-linked Lazarus APT group stealing cryptocurrency using a never-before-seen tool. In the last five years, JavaScript sniffers have grown into one of the most dangerous threats for e-commerce businesses. The simple nature of such attacks combined with the use of malicious JavaScript code for intercepting payment data attract more and more […]
 Pierluigi Paganini
March 04, 2021
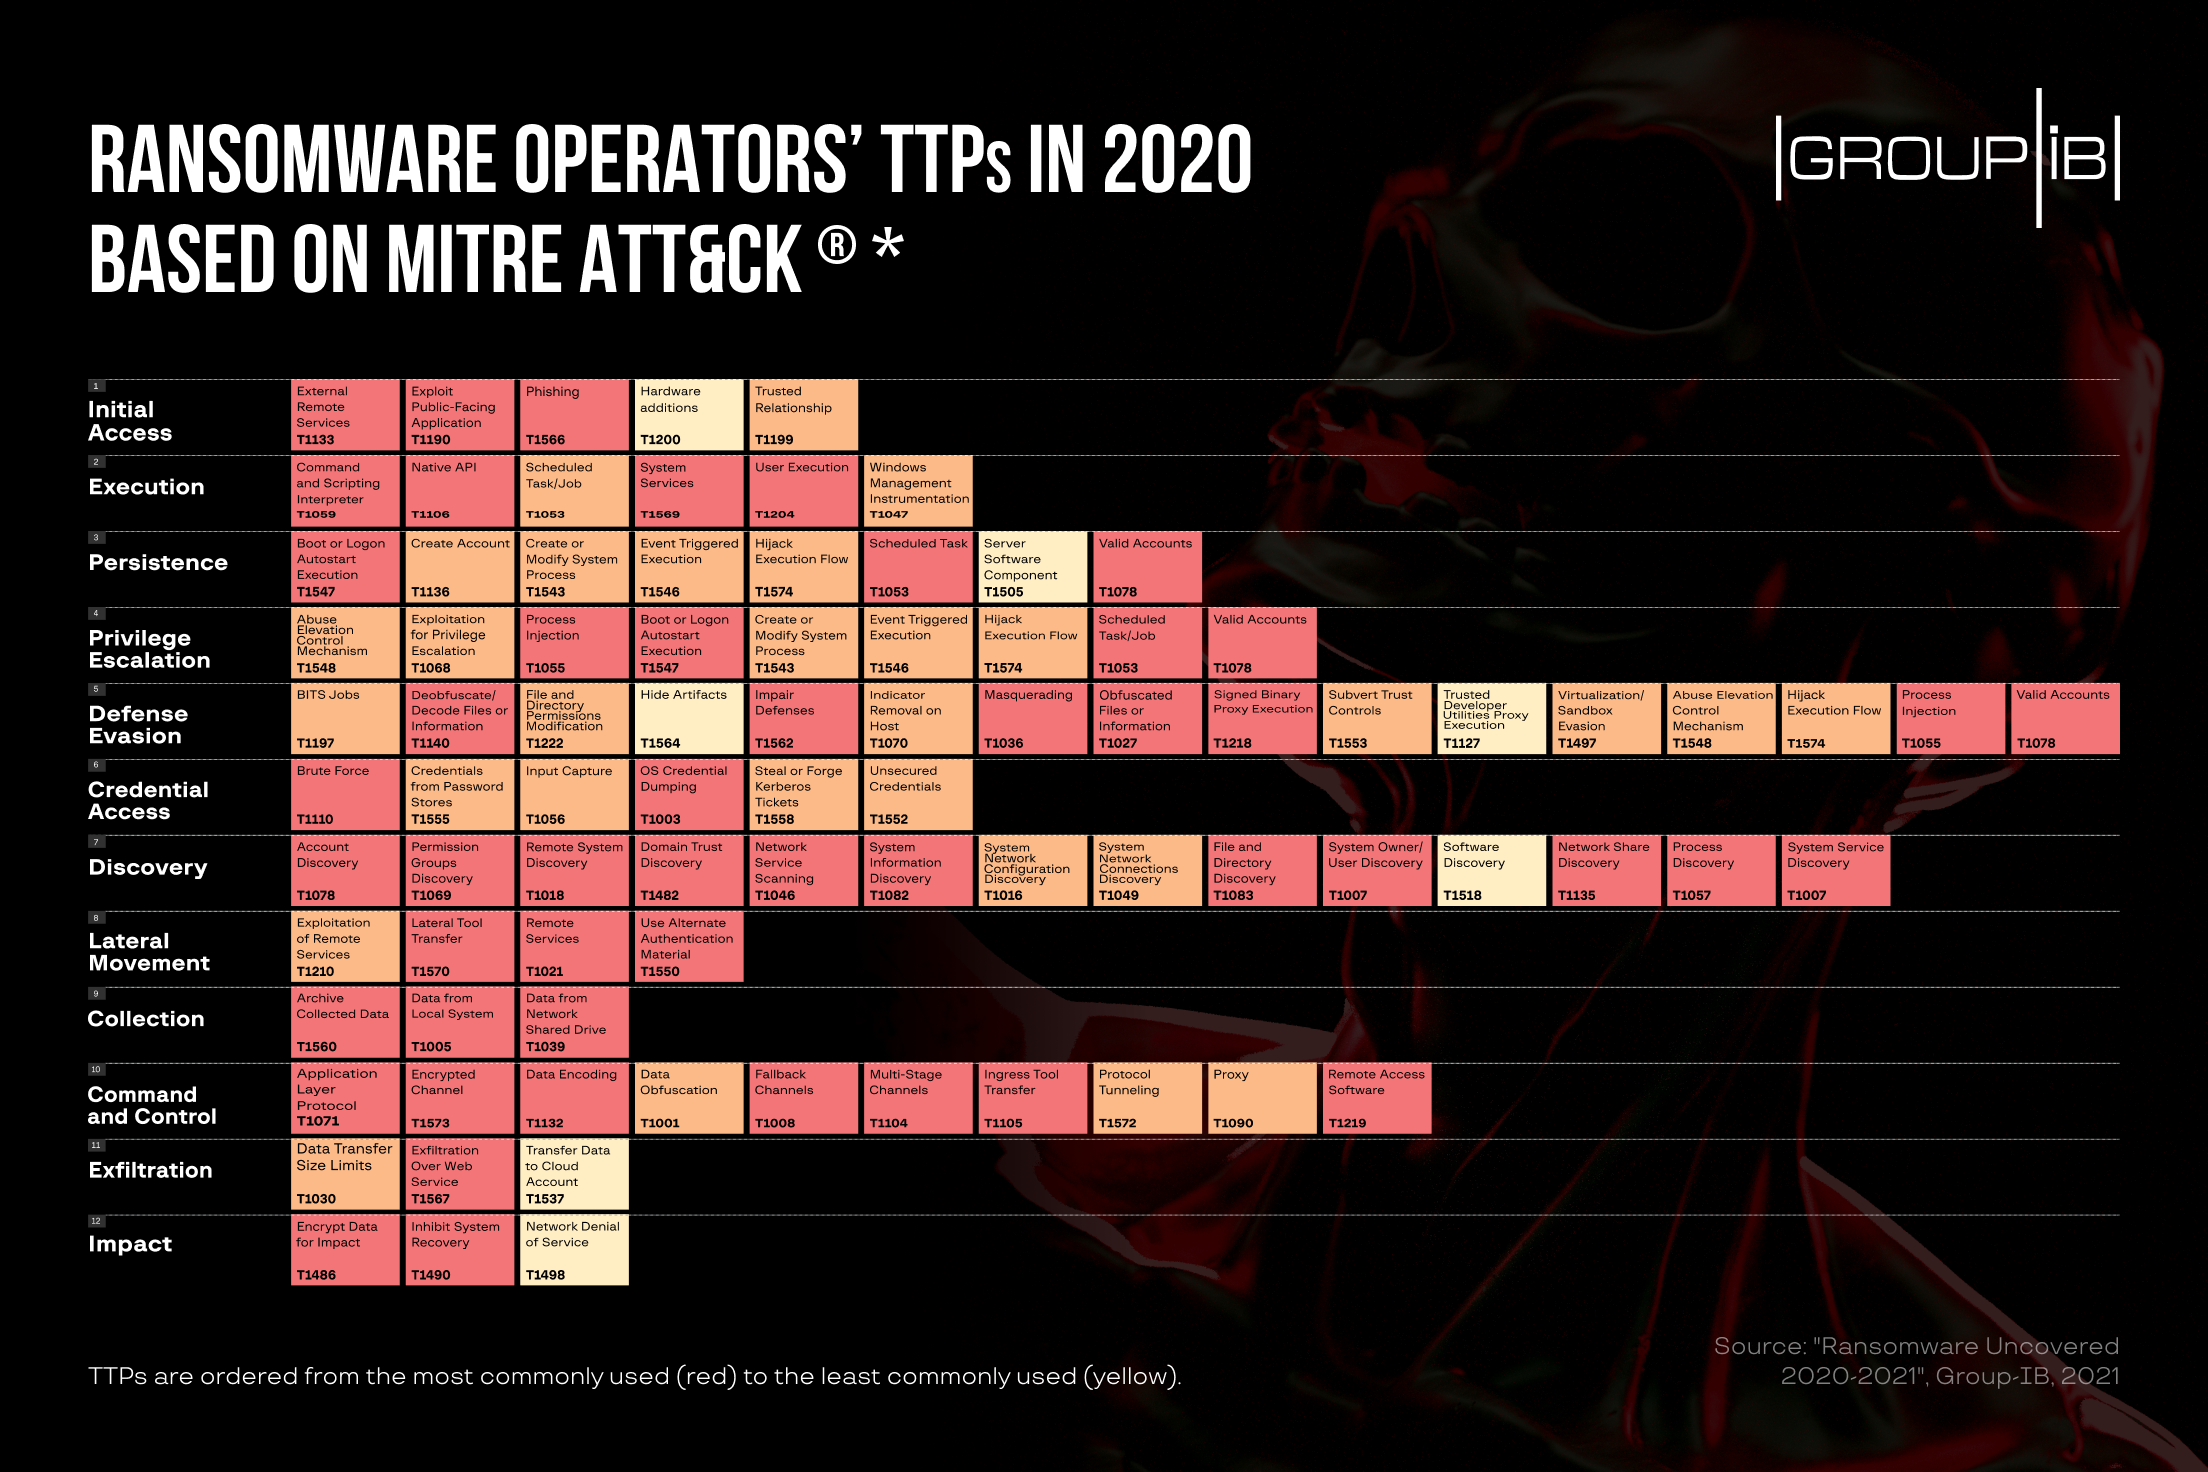
Group-IB published a report titled “Ransomware Uncovered 2020-2021”. analyzes ransomware landscape in 2020 and TTPs of major threat actors. Group-IB, a global threat hunting and adversary-centric cyber intelligence company, has presented its new report “Ransomware Uncovered 2020-2021”. The research dives deep into the global ransomware outbreak in 2020 and analyzes major players’ TTPs (tactics, techniques, and procedures). By […]
 Pierluigi Paganini
February 25, 2021
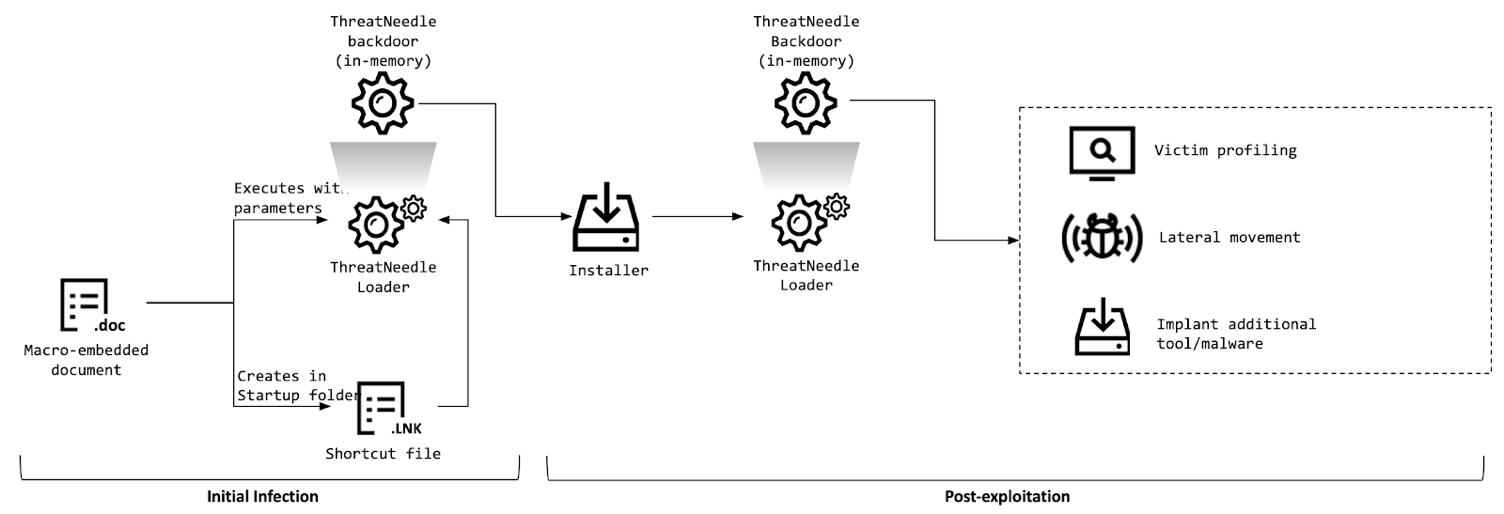
North Korea-linked Lazarus APT group has targeted the defense industry with the custom-backdoor dubbed ThreatNeedle since 2020. North Korea-linked Lazarus APT group has targeted the defense industry with the backdoor dubbed ThreatNeedle since early 2020. The state-sponsored hackers targeted organizations from more than a dozen countries. The experts discovered the custom backdoor while investigating an […]
 Pierluigi Paganini
August 13, 2020
Israel ‘s defence ministry announced to have foiled an attempted cyber attack by a foreign threat actors group targeting the country’s defence manufacturers. The Israeli defence ministry announced on Wednesday that it had foiled a cyber attack carried out by a foreign threat actor targeting the country’s defence manufacturers. According to the officials, the attack […]
 Pierluigi Paganini
January 10, 2020
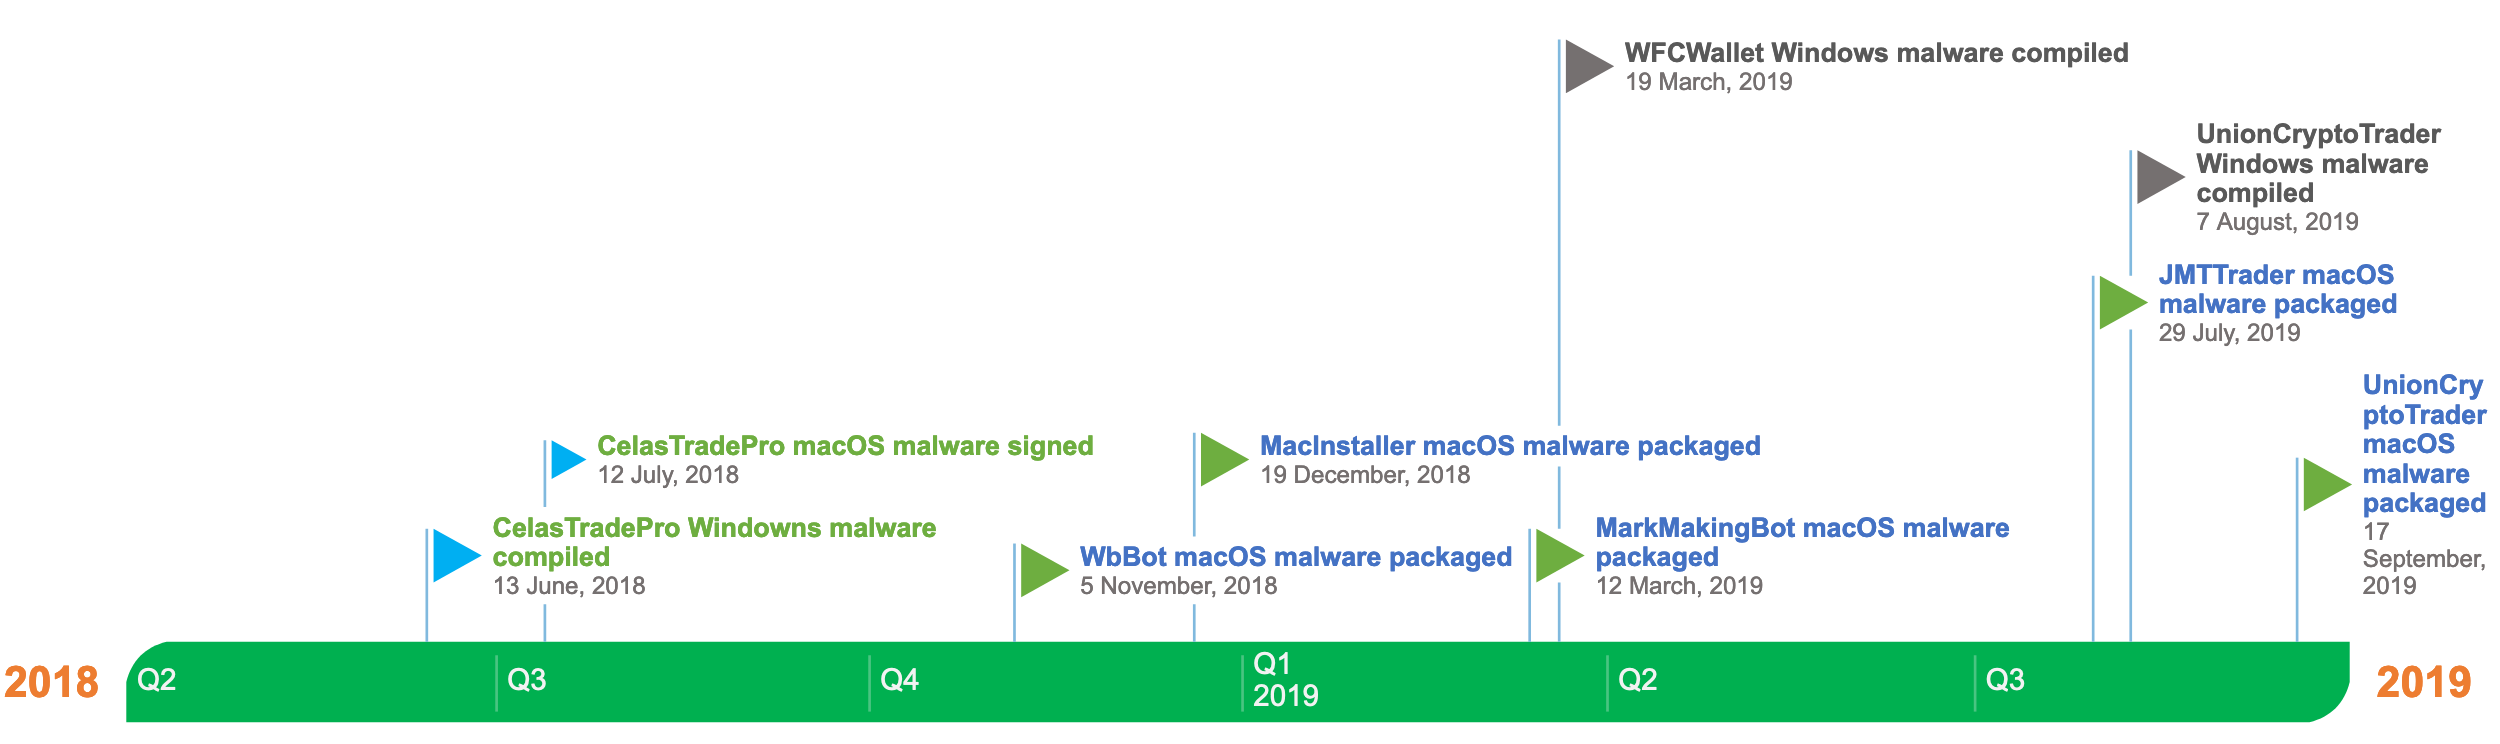
In the last 18 months, North Korea-linked Lazarus APT group has continued to target cryptocurrency exchanges evolving its TTPs. Kaspersky researchers have analyzed the attacks carried out by North Korea-linked Lazarus APT group in the past 18 months and confirmed their interest in banks and cryptocurrency exchanges. In the mid-2018, the APT targeted cryptocurrency exchanges and cryptocurrency […]