


 Pierluigi Paganini
 May 29, 2014
Researchers at SEC Consult Vulnerability Lab discovered that Nice Recording eXpress lawful intercept software contains numerous flaws, including a backdoor. Nice Recording eXpress voice-recording package software used by law enforcement to intercept communications of suspects under investigation contains various flaws, this is the discovery of security researchers at SEC Consult Vulnerability Lab. The researchers have recently published an […]
 Pierluigi Paganini
April 18, 2014
A new study conducted by the Ponemon Institute reveals the impact of successfully SQL injection attacks on organizations during the last year. The Ponemon Institute published a new study titled “The SQL Injection Threat Study“ to understand the reply of organizations to the SQL injection threat. The study is sponsored by DB Networks, its Chairman and CEO Brett Helm used the following […]
 Pierluigi Paganini
April 15, 2014
The security expert Ibrahim Raafat discovered critical SQL injection vulnerabilities in Flickr Photo Books which allow attackers to gain complete control of the server and its database. The giant of online photo management and sharing Flickr, a Yahoo-owned company, was affected by critical vulnerabilities which allow attackers to gain access to the webserver website database. The alarming discovery […]
 Pierluigi Paganini
December 14, 2013
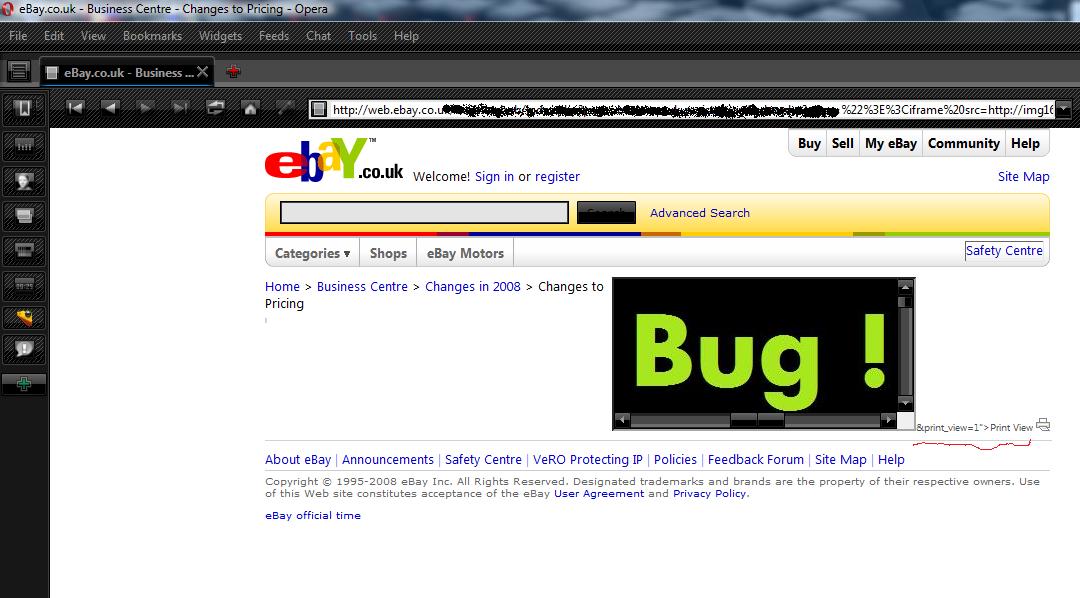
The German security researcher David Vieira-Kurz discovered a critical vulnerability in the Ebay website that allows an attacker a remote code execution. The German security researcher David Vieira-Kurz discovered a critical vulnerability in the official Ebay website in particular in its sub domain http://sea.ebay.com that allows an attacker a remote code execution. It’s not the first time […]
 Pierluigi Paganini
November 25, 2013
A study conducted by company’s enterprise security arm HP Fortify revealed that the majority of mobile apps based on iOS is vulnerable. The company’s enterprise security arm HP Fortify conducted a series of tests on mobile apps that produced concerning results, almost every app is vulnerable. Mike Armistead, vice president and general manager, Enterprise Security […]
 Pierluigi Paganini
November 07, 2013
Security experts at Securi firm have recently detected a series of SQL Injection attacks conducted abusing of the Google Bot activity. The exploitation of search engines like Google and Bing to conduct an attack represents an optimal choice for hackers that intend to stay hidden during the offensive. No IT administrator would block traffic from […]
 Pierluigi Paganini
November 03, 2013
Security Researcher Mohamed Osman Saeed has identified numerous vulnerabilities and reported them all, they include SQL Injection, XSS and URL Redirect. Security Researcher Mohamed Osman Saeed has identified numerous vulnerabilities and reported them all following an ethical conduct. The flaw interested principal security firms and private companies, following the complete list: Invalidated URL Redirect in […]
 Pierluigi Paganini
October 27, 2013
Hackers use to target subcontractors to hit big enterprises due the poor level of security they offer, in the energy sector this trend is very concerning. Let’s follow the discussion on the hacking world and the way hackers impact business with their activities. We discussed about the role of hackers for companies and their employment […]
 Pierluigi Paganini
September 17, 2013
It is very easy to hack the Nasdaq according the security expert Kolochenko that reported numerous vulnerabilities in the official website of the exchange. Just 10 minutes could be sufficient for an attacker to hack the Nasdaq Stock Market, this is the alert provided by Ilia Kolochenko, head of Swiss information security company High-Tech Bridge. The security expert […]
 Pierluigi Paganini
July 24, 2013
Context Information Security issued the report “Web Application Vulnerability Statistics 2013” that provides statistic on Web Application Vulnerabilities based on data gathered from a range of IT security activities and consultancy engagements during last three years. The number of data breaches is increasing in concerning way also thanks to numerous cyber attacks that exploited Web Application Vulnerabilities in many web […]

Security / October 08, 2026


