 Pierluigi Paganini
 July 21, 2018
Security experts from Kaspersky Lab have discovered a precursor of the infamous Proton macOS malware that was named Calisto. Malware researchers from Kaspersky Lab have discovered a malware, tracked as Calisto, that appears to be to the precursor of the Proton macOS malware. “We recently came across one such sample: a macOS backdoor that we named Calisto. The […]
 Pierluigi Paganini
July 18, 2018
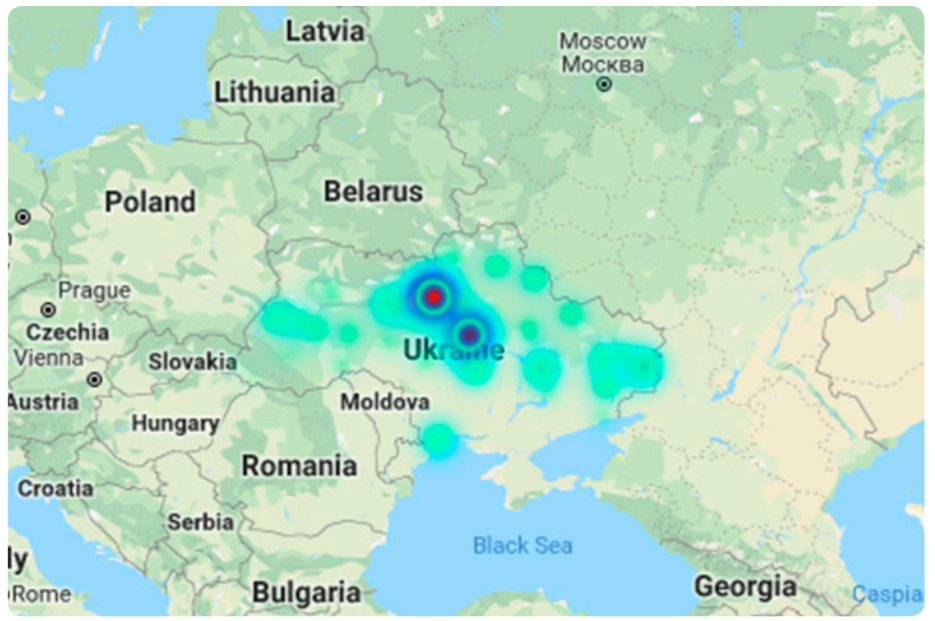
Security experts from ESET uncovered an ongoing cyber espionage campaign aimed at Ukrainian government institutions and involving three different RATs, including the custom-made VERMIN. Security researchers from ESET uncovered an ongoing cyber espionage campaign aimed at Ukrainian government institutions, attackers used at least three different remote access Trojans (RATs). The campaign was first spotted in January by […]
 Pierluigi Paganini
July 15, 2018
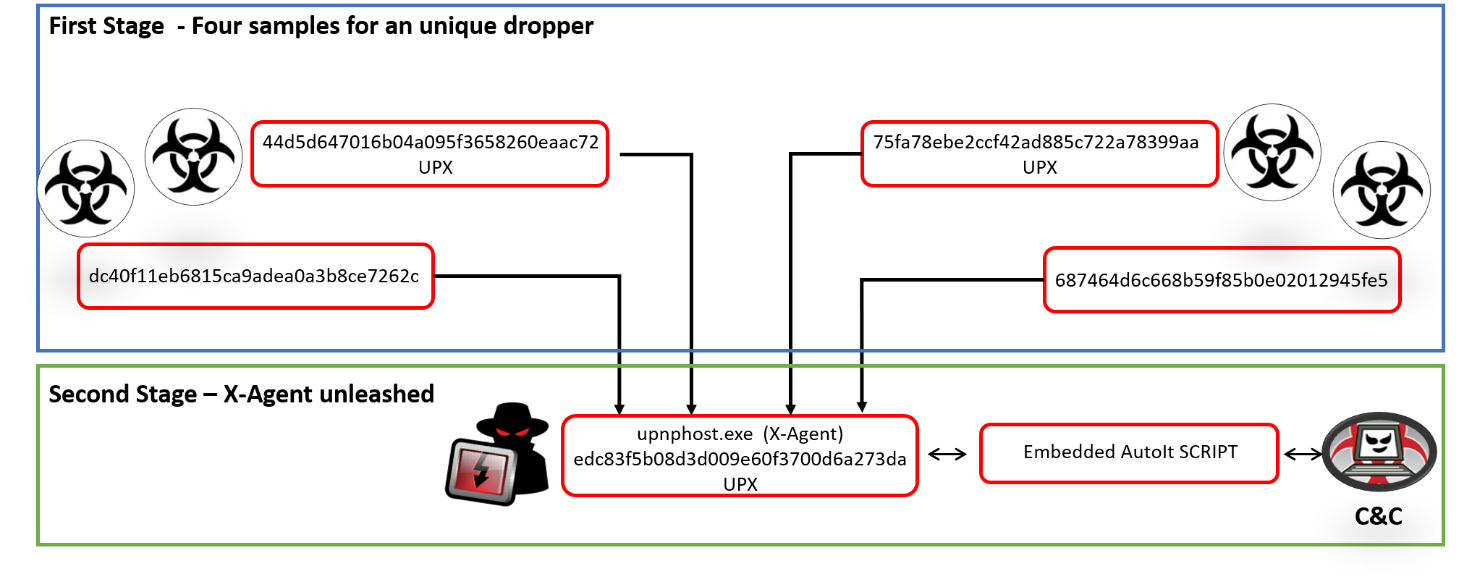
Researchers from the Z-Lab at CSE Cybsec analyzed a new collection of malware allegedly part of a new espionage campaign conducted by the APT28 group. It was a long weekend for the researchers from the Z-Lab at CSE Cybsec that completed the analysis a number of payloads being part of a new cyber espionage campaign […]
 Pierluigi Paganini
July 14, 2018
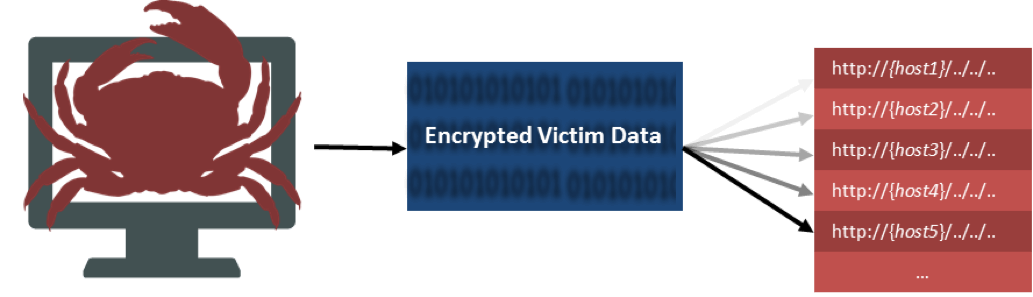
Security experts from Fortinet recently detected a new version of the GandCrab ransomware, ver 4.1, that is being distributed through compromised websites A few days ago, I wrote about the return of the GandCrab ransomware (v4), a new version appeared in the threat landscape and experts at BleepingComputer first reported it. GandCrab ransomware is a young threat, it first […]
 Pierluigi Paganini
July 13, 2018
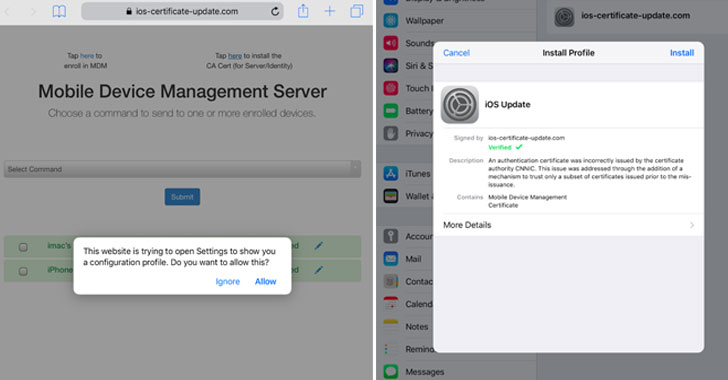
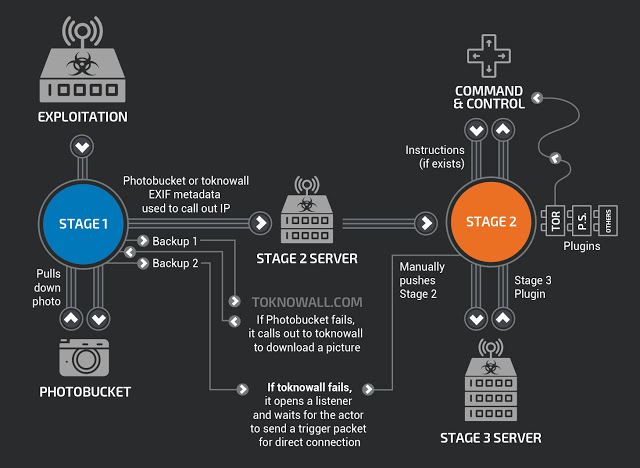
Talos Team have uncovered a “highly targeted” campaign leveraging a mobile malware distributed through a bogus MDM service Security experts from Talos Team have uncovered a “highly targeted” campaign leveraging a mobile malware that has been active at least since August 2015. The researchers believe that cyberspies are operating from China and they found spying […]
 Pierluigi Paganini
July 13, 2018
Ukraine ‘s SBU Security Service reportedly stopped VPNFilter attack at chlorine station, the malware infected the network equipment in the facility that supplies water treatment and sewage plants. According to the Interfax-Ukraine media outlet, the VPNFilter hit the LLC Aulska station in Auly (Dnipropetrovsk region), according to the experts the malware aimed at disrupting operations at the chlorine station. […]
 Pierluigi Paganini
July 12, 2018
Hackers have compromised the website of VSDC, (http://www.videosoftdev.com), a popular company that provides free audio and video conversion and editing software. Experts from Chinese security firm Qihoo 360 Total Security discovered that attackers hijacked the download links of the popular audio and video editor, VSDC. The experts discovered that hackers hijacked download links on the websites […]
 Pierluigi Paganini
July 12, 2018
FireEye uncovered a large-scale Chinese phishing and hacking campaign powered by Temp.periscope APT aimed at Cambodia’s elections. Security researchers at FireEye have uncovered a large-scale Chinese phishing and hacking campaign aimed at Cambodia’s elections. The hackers distributed a remote access trojan (RAT) and data exfiltration operation targeting the poll. The experts from FireEye attributed the attacks to an APT group tracked […]
 Pierluigi Paganini
July 11, 2018
Hackers have poisoned the Arch Linux PDF reader package named “acroread” that was found in a user-provided Arch User Repository (AUR), Hackers have poisoned the Arch Linux PDF reader package, this means that users who have downloaded recently a PDF viewer named “acroread” may have been compromised. ThePDF reader package has been tainted with a malware and Arch […]
 Pierluigi Paganini
July 10, 2018
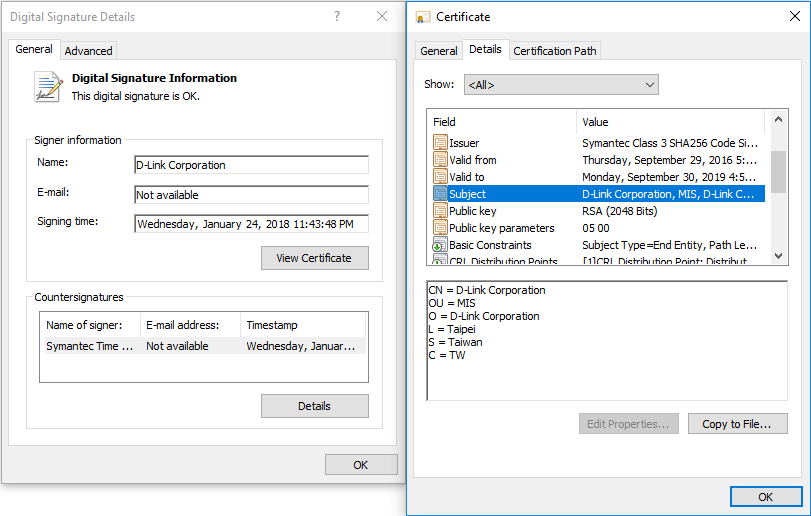
A cyber-espionage group tracked as BlackTech is abusing code-signing certificates stolen from D-Link for the distribution of their malware. Security experts from ESET discovered that an APT group tracked as BlackTech is using code-signing certificates stolen from Taiwanese-based tech firm D-Link and the security company Changing Information Technology Inc. According to the experts, the cyber espionage group […]