


 Pierluigi Paganini
 October 14, 2026
OpenAI employee charged with planting hidden audio recorders to capture sensitive discussions about AI research and company strategy. On September 30, OpenAI staff found a small audio recording device jammed into a USB port on the back of a television in an executive conference room in their San Francisco office. The device had been there […]
 Pierluigi Paganini
October 14, 2026
Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity at one of its monitoring customers and traced everything back to an Ivanti Connect Secure VPN appliance running version 22.8R2.4, the latest build available at the time. Three chained […]
 Pierluigi Paganini
October 14, 2026
Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold. Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions […]
 Pierluigi Paganini
October 13, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Ivanti Connect Secure flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Ivanti Connect Secure FortiMail flaw, tracked as CVE-2026-104935 (CVSS score of 8.6), to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability is an authentication bypass issue caused by […]
 Pierluigi Paganini
October 13, 2026
Anthropic researchers show how small AI models could autonomously replicate across IoT devices, raising concerns about adaptive, AI-powered botnets. Anthropic published a paper this week that should make anyone who manages IoT infrastructure sit down for a moment. The research shows that small AI models are approaching the capability to replicate themselves autonomously across networks […]
 Pierluigi Paganini
October 13, 2026
GitLab fixed a critical vulnerability with a maximum CVSS score of 10.0 that could let unauthenticated attackers run code on its servers. GitLab has addressed a critical security flaw, tracked as CVE-2026-97229 (CVSS score of 10.0), that could let attackers run code on its servers without logging in. The flaw affects Community Edition (CE) and […]
 Pierluigi Paganini
October 12, 2026
A Canadian ransomware negotiator faces extortion charges in the FBI’s ShinyHunters crackdown. Here’s what is known, and what isn’t. ShinyHunters is the focus of a global FBI investigation, and the crackdown has led to the October 8 arrest of a Canadian ransomware negotiator who now faces extortion charges. Reuters reported the arrest, citing court documents, […]
 Pierluigi Paganini
October 12, 2026
Canonical suffered its second DDoS attack this year, disrupting public websites for over four hours while Launchpad and the Snap Store remained online. Ubuntu’s parent company Canonical spent part of last week fighting off a sustained distributed denial of service (DDoS) attack, the second one to hit its infrastructure this year. The company revealed the […]
 Pierluigi Paganini
October 12, 2026
Attackers are exploiting SonicWall SMA 1000 vulnerability, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after its public disclosure. Attackers have begun exploiting a critical flaw in SonicWall SMA 1000 appliances, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after public disclosure. The vulnerability is a server-side request forgery (SSRF) flaw that requires no login. […]
 Pierluigi Paganini
October 12, 2026
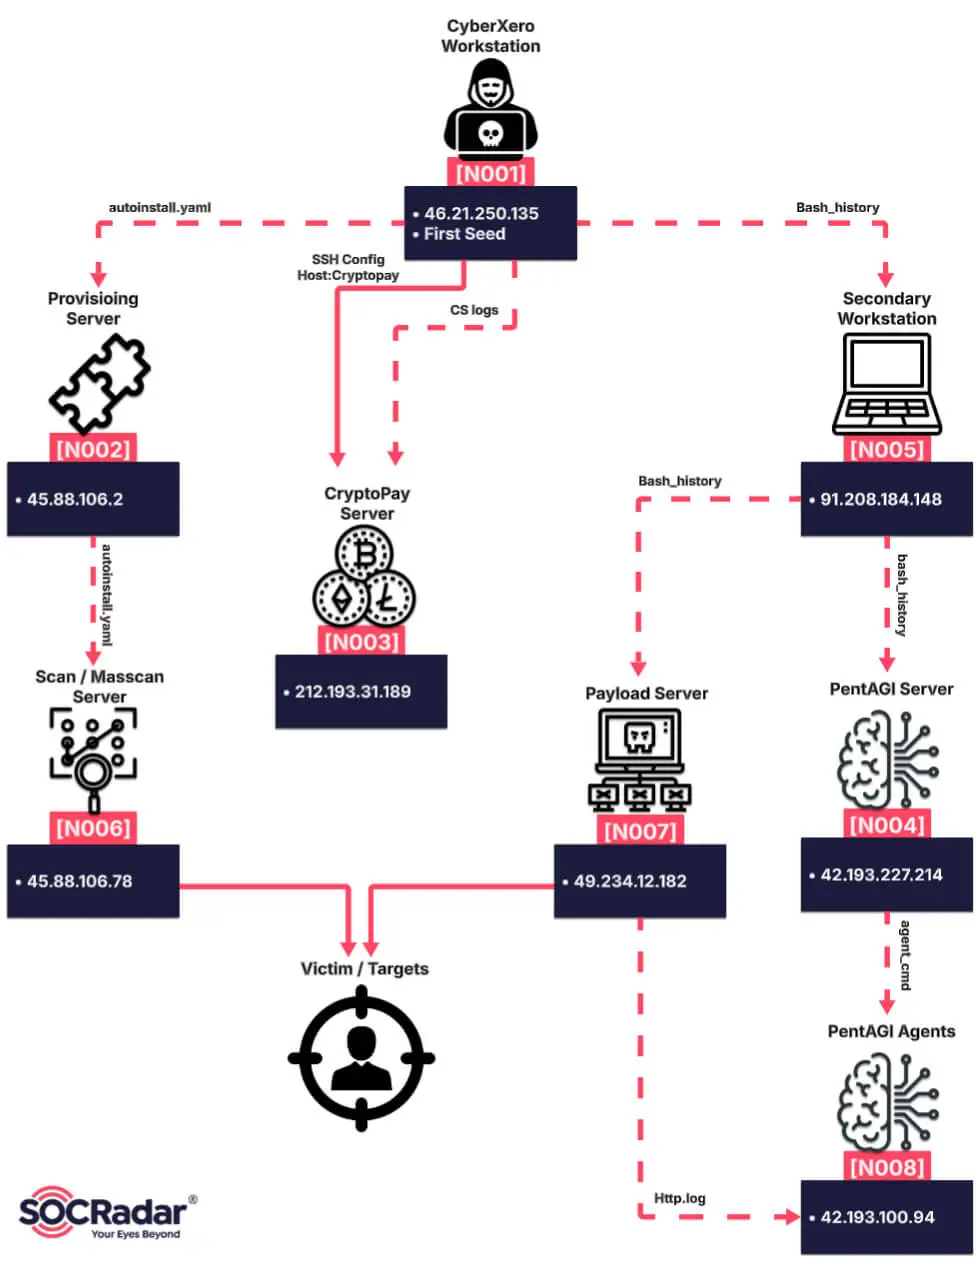
CyberXero used 51 AI agents to support cyberattacks, stealing 628,000 Ukrainian records, including sensitive data from energy infrastructure. CyberXero is an operation that combines traditional hacking tools with AI agents to carry out cyberattacks. According to SOCRadar researchers, the attackers use the same infrastructure for two different campaigns: one targets WordPress websites and e-commerce platforms […]


Intelligence / October 17, 2026

