


 Pierluigi Paganini
 June 08, 2020
A researcher is warning that Google is indexing the phone numbers of WhatsApp users raising serious privacy concerns. Google is indexing the phone numbers of WhatsApp users that could be abused by threat actors for malicious activities. Even if Google Search only revealed the phone numbers and not the identities of associated users, ill-intentioned attackers […]
 Pierluigi Paganini
June 08, 2020
IBM has released open-source toolkits implementing fully homomorphic encryption (FHE) that allow researchers to process data while it’s still encrypted. IBM has released open-source toolkits implementing fully homomorphic encryption (FHE), which allows researchers to process encrypted data without having access to the actual data. The toolkits released by IBM are already available for macOS and […]
 Pierluigi Paganini
June 05, 2020
Cyber Defense Magazine June 2020 Edition has arrived. We hope you enjoy this month’s edition…packed with over 165 pages of excellent content. Cyber Defense Magazine June 2020 Edition has arrived. Tips, tricks, ideas, secrets and insider information on the best practices in cybersecurity. Please read it and share it with your friends. With much appreciation to […]
 Pierluigi Paganini
June 02, 2020
A flaw in the IP-in-IP tunneling protocol that can be exploited for DoS attacks and to bypass security controls impact devices from Cisco and other vendors. A vulnerability that affects the IP-in-IP tunneling protocol (aka IP Encapsulation within IP) implemented by Cisco and other vendors could be exploited for denial-of-service (DoS) attacks and to bypass […]
 Pierluigi Paganini
June 02, 2020
This week Apple released security patches to address the CVE-2020-9859 zero-day vulnerability that had been used to jailbreak iPhones devices. Apple released security patches to address the CVE-2020-9859 zero-day vulnerability in the iOS kernel that had been used to jailbreak iPhones. The flaw was discovered by a team of cyber-security researchers and hackers that also […]
 Pierluigi Paganini
June 01, 2020
VMware has released an update to address a privilege escalation flaw in VMware for the macOS version of Fusion that was introduced by a previous patch. In March, VMware patched a high-severity privilege escalation vulnerability (CVE-2020-3950) in Fusion, Remote Console (VMRC) and Horizon Client for Mac. The CVE-2020-3950 is a privilege escalation vulnerability caused by the […]
 Pierluigi Paganini
May 31, 2020
EU Agency for Cybersecurity ENISA has published a new report of the proactive detection of incidents, including measures and information sources. The EU Agency for Cybersecurity ENISA has published a new report and accompanying repository on measures and information sources that could help security experts and operators of IT and critical infrastructure to proactively detect […]
 Pierluigi Paganini
May 30, 2020
API Security – There is a considerable demand for data-centric projects, that is why companies have quickly opened their data to their ecosystem through REST or SOAP APIs. APIs work as doors for a company – closely guarding data of an organization. However, there are some challenges created: how do we hold the doors open […]
 Pierluigi Paganini
May 28, 2020
The U.S. NSA warns that Russia-linked APT group known as Sandworm Team have been exploiting a critical flaw in the Exim mail transfer agent (MTA). The U.S. National Security Agency (NSA) is warning that Russia-linked APT group tracked Sandworm Team has been exploiting a critical vulnerability (CVE-2019-10149) in the Exim mail transfer agent (MTA) software since […]
 Pierluigi Paganini
May 26, 2020
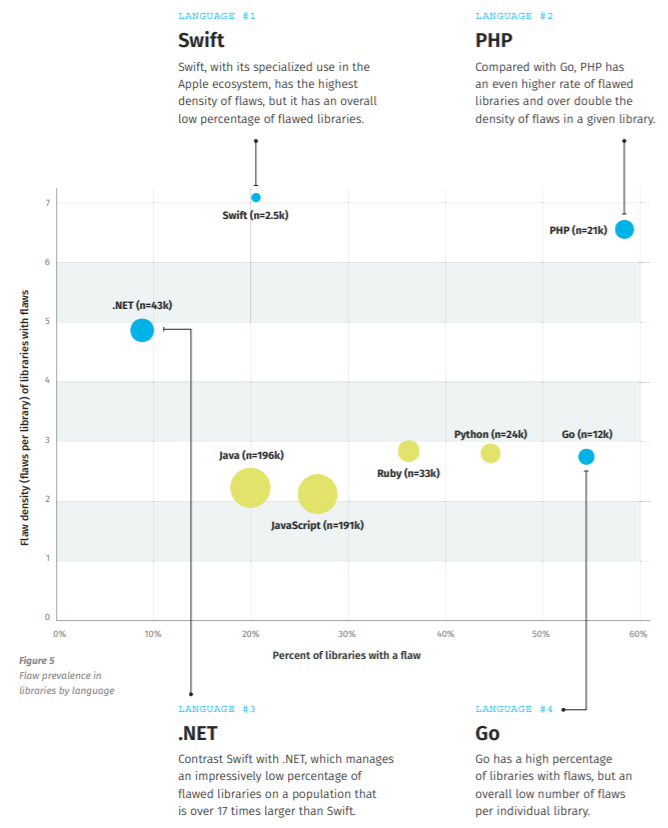
70 percent of mobile and desktop applications that today we use are affected at least by one security flaw that is present in open-source libraries. According to the Veracode’s annual State of Software Security report, 70 percent of mobile and desktop applications being used today have at least one security flaw that is the result of the […]
Malware / September 21, 2026
Uncategorized / September 21, 2026

Security / September 20, 2026

