


 Pierluigi Paganini
 September 20, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gray Rabbits and the Tale of a One-Click Backdoor Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot […]
 Pierluigi Paganini
September 20, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Google Gemini also Broke Out of Its Test Environment AI Helps Hackers Hijack OpenAI Staff Accounts Through […]
 Pierluigi Paganini
September 18, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients include eBay, Louis Vuitton and Michelin. The company was first compromised on September 10, when attackers exploited a vulnerability in its […]
 Pierluigi Paganini
September 18, 2026
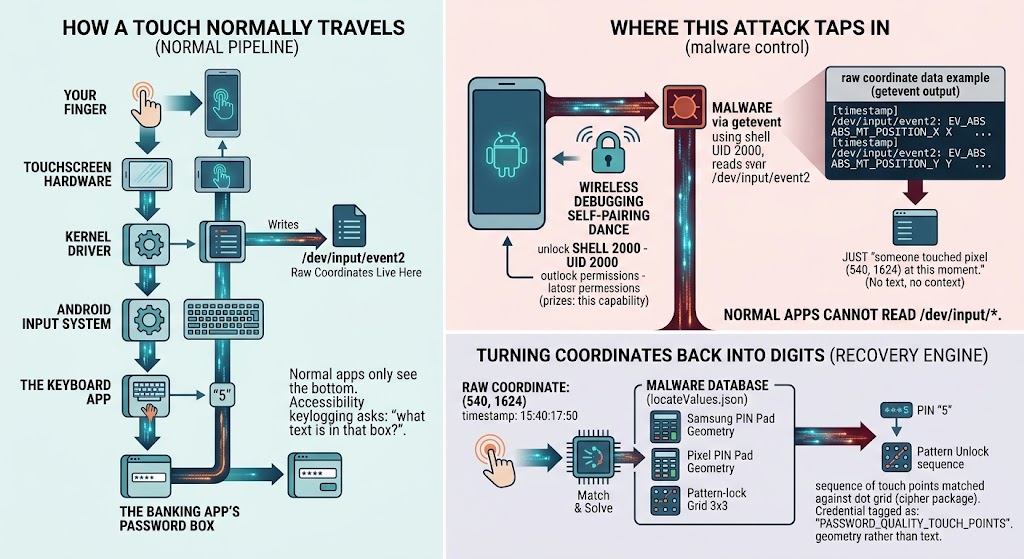
RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know about. Zimperium researchers just published a breakdown of a strain they’ve traced to China-based operators, and what makes it different isn’t the credential theft, which is […]
 Pierluigi Paganini
September 17, 2026
UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the […]
 Pierluigi Paganini
September 16, 2026
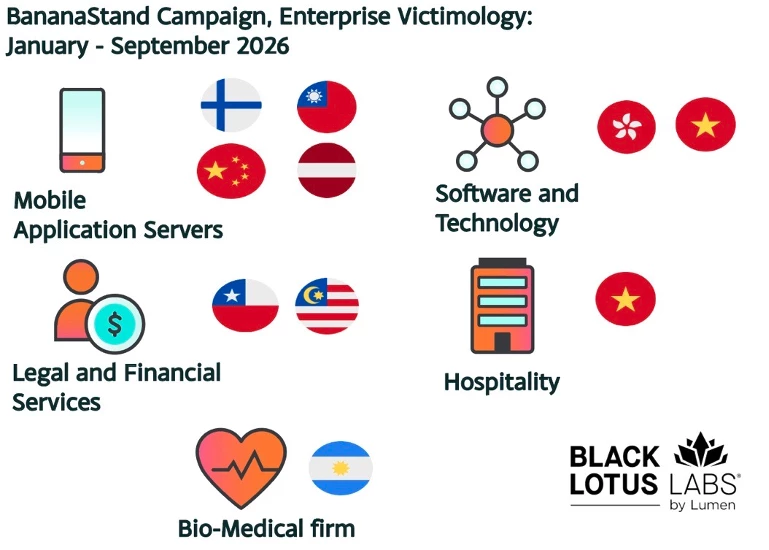
Lumen exposes BambooToken, a stealthy malware family using MQTT and sideloading to quietly infect targets across Asia and beyond. BambooToken is a new malware family that uses MQTT, a lightweight messaging protocol commonly found in smart devices and industrial systems, to quietly control infected Windows and Linux machines. Most malware connects directly to a command-and-control […]
Pierluigi Paganini
September 13, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter REVSTEALER ramps up Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode GuardBreaker: Derailing AI-assisted malware analysis with a code comment DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive […]
Pierluigi Paganini
September 13, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. The AI Supply Chain Has a Security Problem, and Much of It Is Sitting on the Open […]
 Pierluigi Paganini
September 13, 2026
Ukrainian lawyer and Conti malware developer Oleksii Lytvynenko was sentenced to four years in U.S. prison for ransomware attacks. Oleksii Oleksiyovych Lytvynenko had, by most accounts, a fairly ordinary legal career in Ukraine before he switched to writing malware. A US federal court sentenced the 44-year-old to four years in prison this week for conspiracy […]
 Pierluigi Paganini
September 11, 2026
Three threat groups are exploiting two Cisco FMC flaws to steal credentials, gain root access and deploy Qilin ransomware. Cisco Talos says three separate threat groups are exploiting two recently patched Secure Firewall Management Center (FMC) flaws. The main target is CVE-2026-20079, a critical authentication bypass that lets unauthenticated attackers remotely bypass security controls, run […]
Security / November 12, 2026
Security / November 12, 2026


