Pierluigi Paganini
 October 11, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure UAC-0277: ClickFix on compromised websites to spread LUNEXSTEALER MALFEX – A malicious npm postinstall no advisory has caught for fourteen months Canto incognito: tracking the PoeLLM malware […]
 Pierluigi Paganini
October 11, 2026
Bitdefender finds Midnight Mimosa, preinstalled Android malware on cheap MediaTek phones that fakes ad clicks, drops apps and builds a proxy botnet. Bitdefender researchers discovered a campaign called Midnight Mimosa involving preinstalled Android malware on low-cost phones from different brands that use MediaTek platforms. The malware is built into the device firmware and may be […]
 Pierluigi Paganini
October 11, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Anthropic Restricts Live Internet Access After Claude Evaluation Failures Silent Ransom Group Allegedly Extorted $207 Million Without […]
 Pierluigi Paganini
October 11, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The five vulnerabilities have been added to a broader list of flaws linked to cyber […]
 Pierluigi Paganini
October 10, 2026
Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluations and internal use. The cases involved real websites and real organizations outside the company. Anthropic says the impact was minimal, and it published them anyway. The […]
 Pierluigi Paganini
October 10, 2026
Silent Ransom Group allegedly extorted $207 million from 27 law firms in six months using phone calls and social engineering, not encryption. Silent Ransom Group doesn’t rely on encryption. No malware payload, no locked files, just phone calls and social engineering aimed almost entirely at law firms, and apparently it works extraordinarily well. A new […]
 Pierluigi Paganini
October 10, 2026
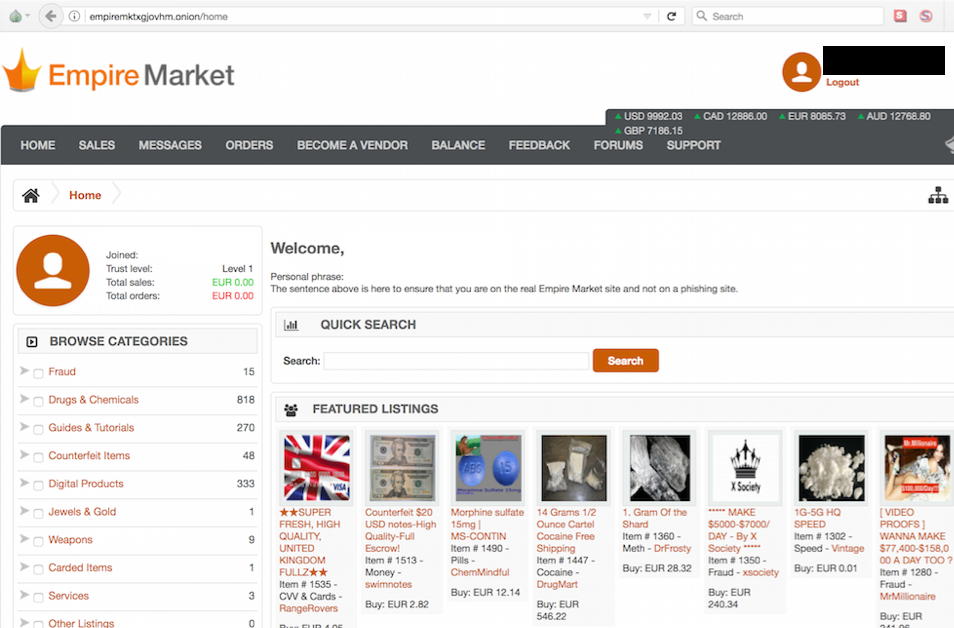
Empire Market co-creator Raheim Hamilton was sentenced to 40 years in prison for running a dark web marketplace linked to $430 million in illegal trades. The case against Empire Market shows how a dark web marketplace can become a major criminal business, bringing together drug trafficking, stolen credentials, personal data and hacking tools. “A Virginia […]
 Pierluigi Paganini
October 09, 2026
Japan helped extradite a Russian suspect linked to Qilin ransomware to Germany, but the gang continued attacking victims after his arrest. Germany has arrested a Russian national believed to be a leading figure in the Qilin ransomware group, and Japan’s National Police Agency just put its own role in that arrest on the record. The […]
Pierluigi Paganini
October 09, 2026
Anthropic launches free OSS Scanner, using AI to find open-source vulnerabilities and help maintainers fix bugs before attackers exploit them. Anthropic is launching OSS Scanner, a vulnerability scanner for open-source code that costs nothing for projects to join. It grew directly out of lessons learned running Claude against real-world targets during Project Glasswing. The backdrop […]
 Pierluigi Paganini
October 09, 2026
DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in […]