


 Pierluigi Paganini
 June 23, 2021
A critical vulnerability, tracked as CVE-2021-20019, in SonicWall VPN appliances was only partially patched last year and could allow a remote attacker to steal sensitive data. In October last year, experts reported a critical stack-based Buffer Overflow vulnerability, tracked as CVE-2020-5135, in SonicWall Network Security Appliance (NSA) appliances. At the time of the discovery, security experts from the Tripwire VERT […]
 Pierluigi Paganini
May 25, 2021
A flaw in Pulse Connect Secure VPN could allow an authenticated remote attacker to execute arbitrary code with elevated privileges. Ivanti addressed a high severity Buffer Overflow vulnerability in Secure VPN appliances that could allow a remote authenticated attacker to execute arbitrary code with elevated privileges. The vulnerability tracked as CVE-2021-22908, has received a CVSS […]
 Pierluigi Paganini
April 13, 2021
Pulse Secure VPN users were not able to login due to the expiration of a code signing certificate used to digitally sign and verify software components. Pulse Secure VPN users were not able to login after a code signing certificate used to digitally sign and verify software components has expired. Multiple users have reported on […]
 Pierluigi Paganini
December 22, 2020
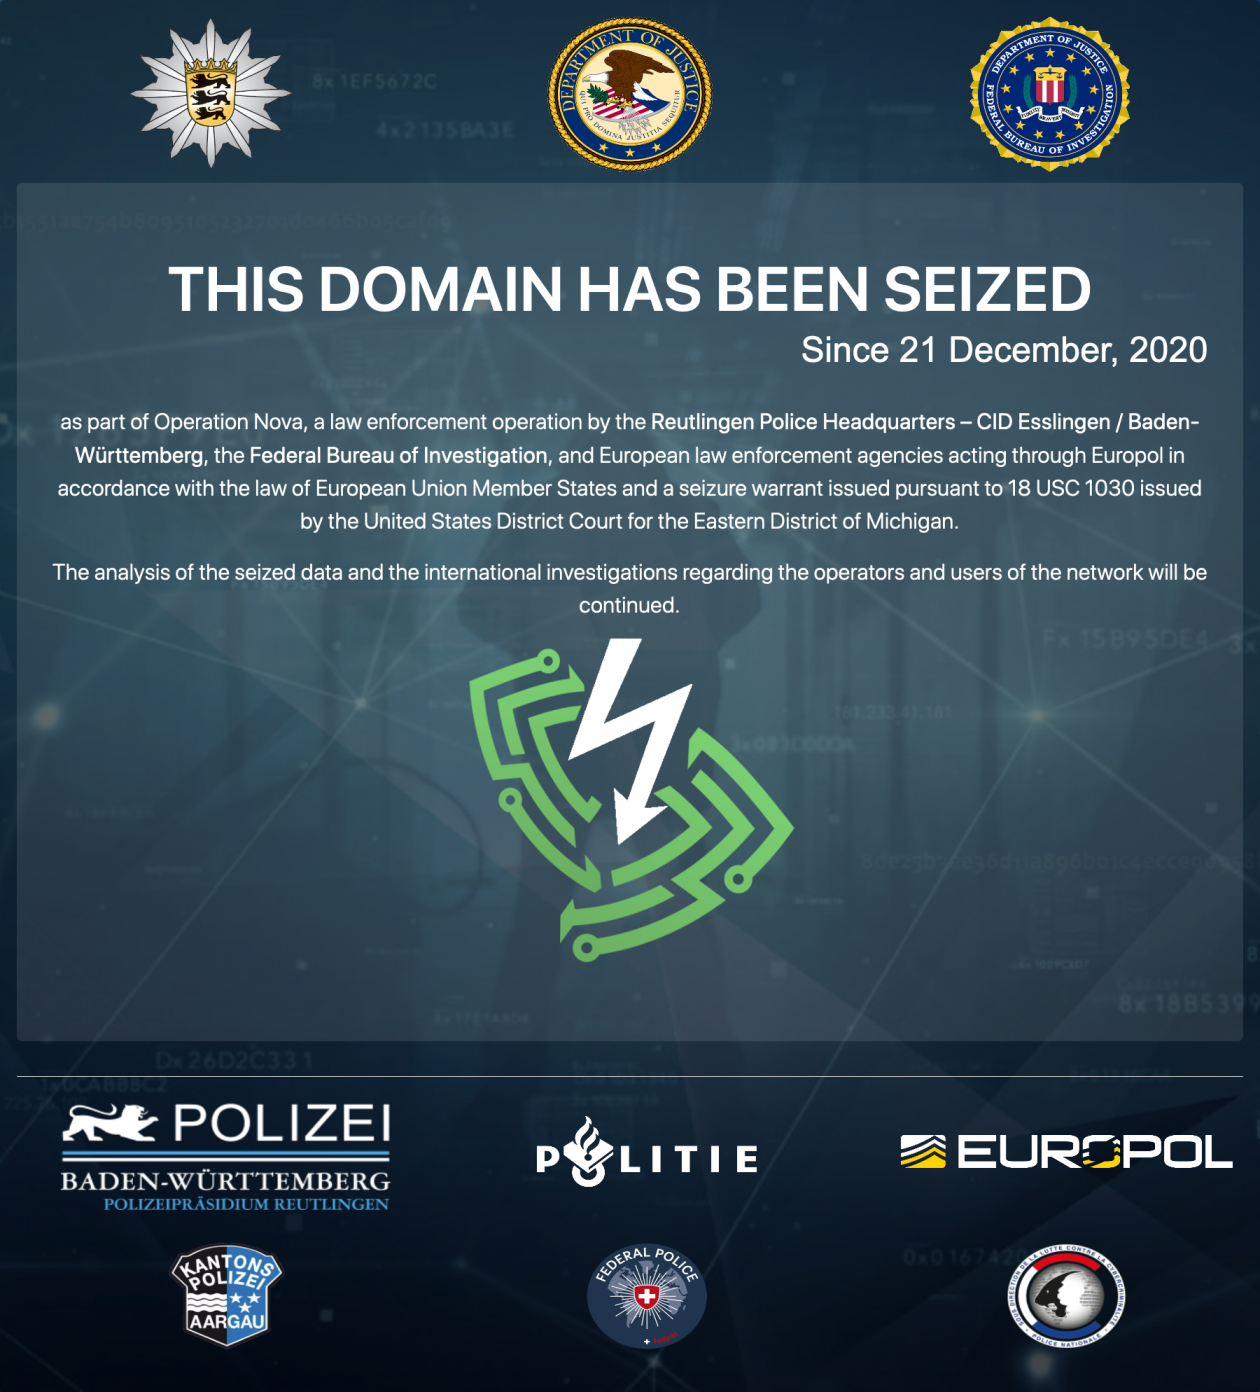
A joint operation conducted by law European enforcement agencies resulted in the seizure of the infrastructure of three bulletproof VPN services. A joint operation conducted by law enforcement agencies from the US, Germany, France, Switzerland, and the Netherlands resulted in the seizure of the infrastructure used by three VPN bulletproof services. VPN bulletproof services are […]
 Pierluigi Paganini
November 27, 2020
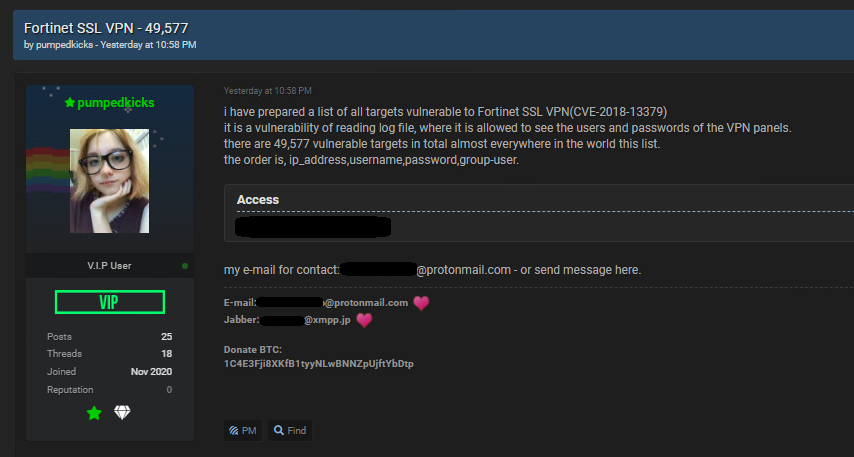
The global impact of the Fortinet 50.000 VPN leak posted online, with many countries impacted, including Portugal. A compilation of one-line exploit tracked as CVE-2018-13379 and that could be used to steal VPN credentials from nearly 50.000 Fortinet VPN devices has posted online. This vulnerability resides in an improper limitation of a pathname to a restricted directory […]
Pierluigi Paganini
October 16, 2020
The Tripwire VERT security team spotted almost 800,000 SonicWall VPN appliances exposed online that are vulnerable to the CVE-2020-5135 RCE flaw. Security experts from the Tripwire VERT security team have discovered 795,357 SonicWall VPN appliances that were exposed online that are vulnerable to the CVE-2020-5135 RCE flaw. “A buffer overflow vulnerability in SonicOS allows a […]
 Pierluigi Paganini
October 12, 2020
US government networks are under attack, threat actors chained VPN and Windows Zerologon flaws to gain unauthorized access to elections support systems. The Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) published a joint security alert to warn of attackers combining VPN and Windows Zerologon flaws to target government networks. […]
 Pierluigi Paganini
September 25, 2020
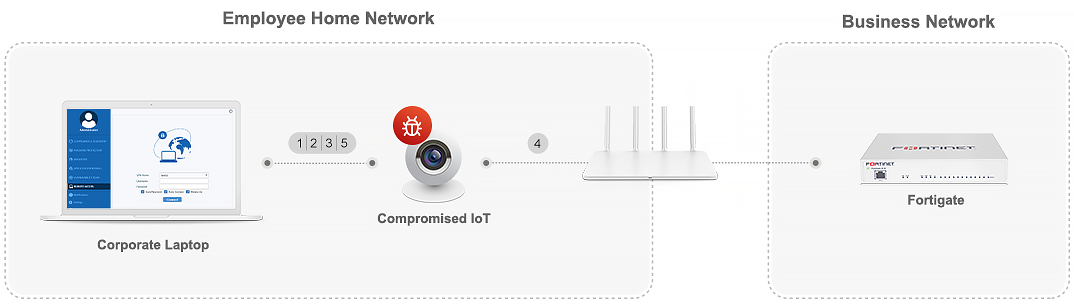
According to SAM Seamless Network, over 200,000 businesses are using Fortigate VPN with default settings, exposing them to the risk of a hack. In response to the spreading of Coronavirus across the world, many organizations deployed VPN solutions, including Fortigate VPN, to allow their employers to work from their homes. The configuration of the VPN […]
 Pierluigi Paganini
August 05, 2020
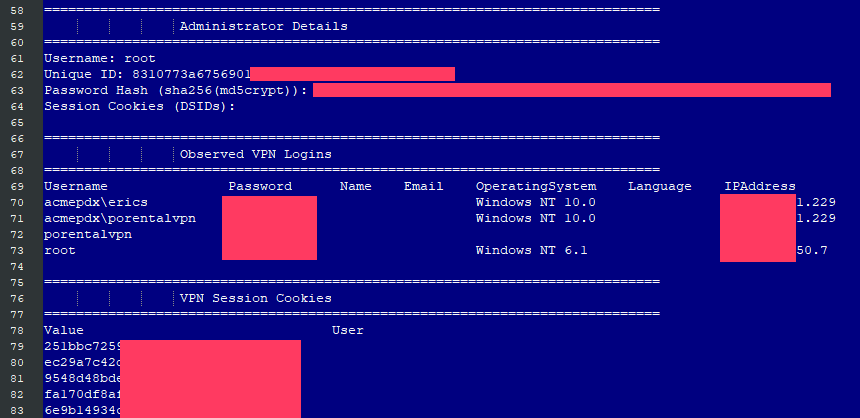
ZDNet reported in exclusive that a list of passwords for 900+ enterprise VPN servers has been shared on a Russian-speaking hacker forum. ZDNet has reported in exclusive that a list of plaintext usernames and passwords for 900 Pulse Secure VPN enterprise servers, along with IP addresses, has been shared on a Russian-speaking hacker forum. ZDNet […]
 Pierluigi Paganini
July 21, 2020
vpnMentor experts reported that seven Virtual Private Network (VPN) recently left 1.2 terabytes of private user data exposed to online. Security experts from vpnMentor have discovered a group of seven free VPN (virtual private network) apps that left their server unsecured online exposing private user data for anyone to see. The impacted VPN services are UFO […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026


