 Pierluigi Paganini
 September 13, 2018
Security experts from Trend Micro have spotted a new strain of ransomware involved in attacks in July and August, the malicious code was posing as the Locky ransomware. Researchers at Trend Micro have detected a new ransomware family, dubbed PyLocky, that was used in attacks between July and August, the malware was posing as the Locky ransomware using its ransom […]
 Pierluigi Paganini
September 11, 2018
Thousands of unpatched MikroTik Routers are involved in new cryptocurrency mining campaigns. The exploit code for the CVE-2018-14847 vulnerabilities is becoming a commodity in the hacking underground, just after its disclosure crooks started using it to compromise MikroTik routers. Thousands of unpatched devices are mining for cryptocurrency at the moment. Earlier August, experts uncovered a massive […]
 Pierluigi Paganini
September 10, 2018
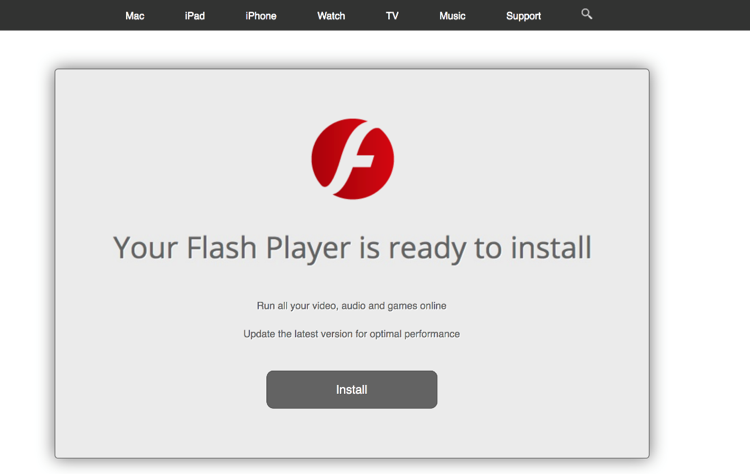
Security experts with Unit 42 at Palo Alto Networks have discovered new variants of the Mirai and Gafgyt IoT malware targeting enterprises. Both botnets appear very interesting for two main reasons: The new Mirai variant targets the same Apache Struts vulnerability exploited in the 2017 Equifax data breach. The vulnerability affects the Jakarta Multipart parser upload […]
 Pierluigi Paganini
September 10, 2018
At the end of August, security experts discovered a new exploit kit called Fallout that is being used to distribute the GandCrab ransomware. At the end of August, the threat analyst nao_sec discovered a new exploit kit called Fallout that is being used to distribute the GandCrab ransomware and other malicious codes, including droppers and potentially unwanted […]
 Pierluigi Paganini
September 09, 2018
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Let me inform you that my new book, “Digging in the Deep Web” is online with a special deal 20% discount Kindle Edition Paper Copy Once again thank you! · John McAfees Bitfi cryptocurrency wallet was hacked by […]
 Pierluigi Paganini
September 08, 2018
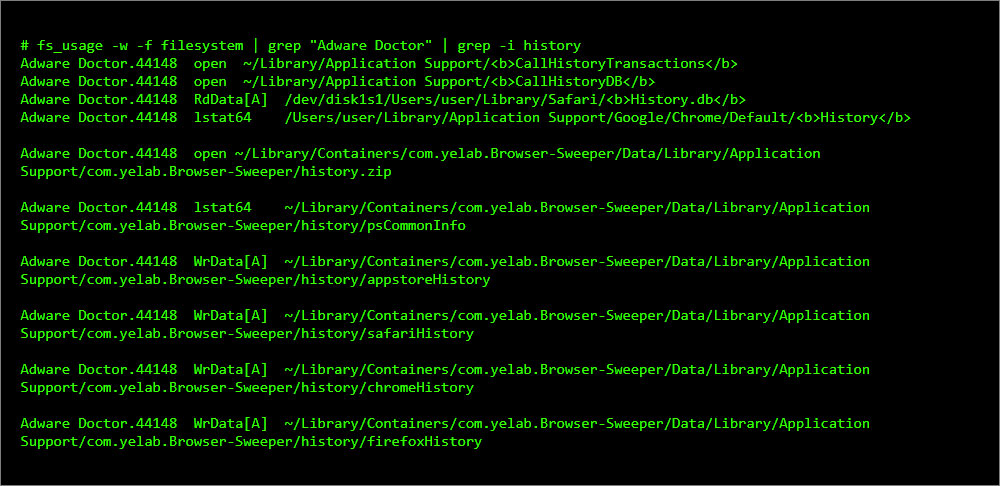
Apple has removed one of the most popular anti-malware app called Adware Doctor:Anti Malware &Ad from the official macOS App Store Apple has removed one of the most popular anti-malware app called Adware Doctor:Anti Malware &Ad from the official macOS App Store because it was gathering users’ browser histories and other sensitive data and then upload them to a […]
 Pierluigi Paganini
September 07, 2018
Schneider Electric announced that some of the USB drives it has shipped with its Conext ComBox and Conext Battery Monitor products were infected with malware. Schneider Electric has found a malicious code on the USB drives that have been shipped with Conext ComBox and Conext Battery Monitor products. Both products are part of the solar energy […]
 Pierluigi Paganini
September 06, 2018
Security experts from ESET observed a treat actor, tracked as PowerPool, exploiting the recently disclosed Windows zero-day flaw in targeted attacks. The vulnerability was publicly disclosed on August 27 by the security expert “@SandboxEscaper,” the researcher also published the exploit code for the vulnerability. The vulnerability affects Microsoft’s Windows operating systems that could be exploited by a […]
 Pierluigi Paganini
September 06, 2018
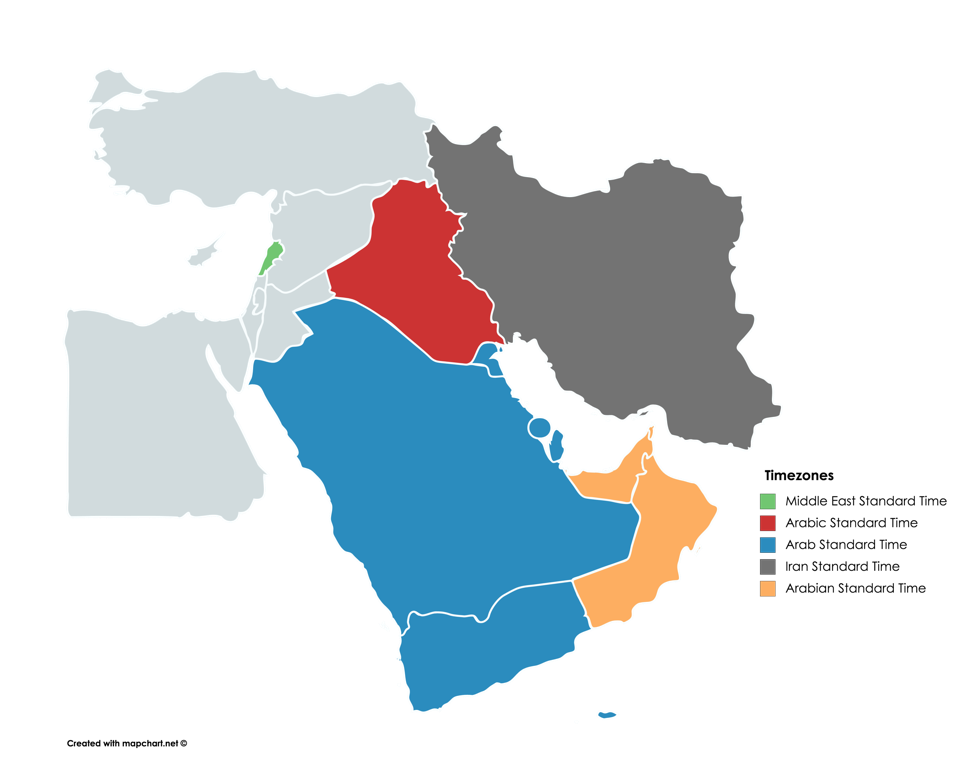
The Iran-linked APT group OilRig was recently observed using a new variant of the OopsIE Trojan that implements news evasion capabilities. Experts at Palo Alto Networks observed a new campaign carried out by the Iran-linked APT group OilRig that was leveraging on a new variant of the OopsIE Trojan. The OilRig hacker group is an Iran-linked APT that has been […]
 Pierluigi Paganini
September 03, 2018
Last week, security researchers from Trend Micro discovered a new threat actor, tracked as Urpage, that shares similarities with other three hacking crews. Researchers from Trend Micro linked a recently discovered actor, tracked as Urpage, to the hacking groups known as Bahamut, Confucius, and Patchwork. Trend Micro first connected the Confucius group to the Patchwork […]