 Pierluigi Paganini
 May 15, 2017
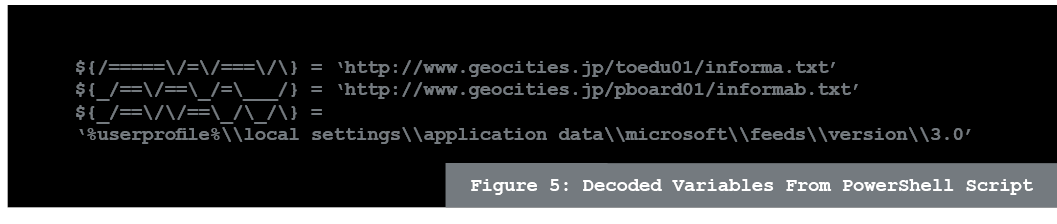
Security researchers from Cylance discovered a new fileless malware dubbed BAIJIU that was used to targets North Korea. Security experts believe the threat has a Chinese origin, attackers delivered it through a phishing campaign. “BAIJIU, which evades widespread detection, abuses global concern about the dire humanitarian situation in North Korea. It enters the target environment through an […]
 Pierluigi Paganini
April 28, 2017
According to the experts at the security firm Morphisec that massive attack against Israeli targets was powered by the OilRig APT group. Yesterday the Israeli Cyber Defense Authority announced it has thwarted a major cyberattack against 120 targets just days after harsh criticism of new cyber defense bill. In a first time, the authorities blamed a foreign […]
 Pierluigi Paganini
March 26, 2017
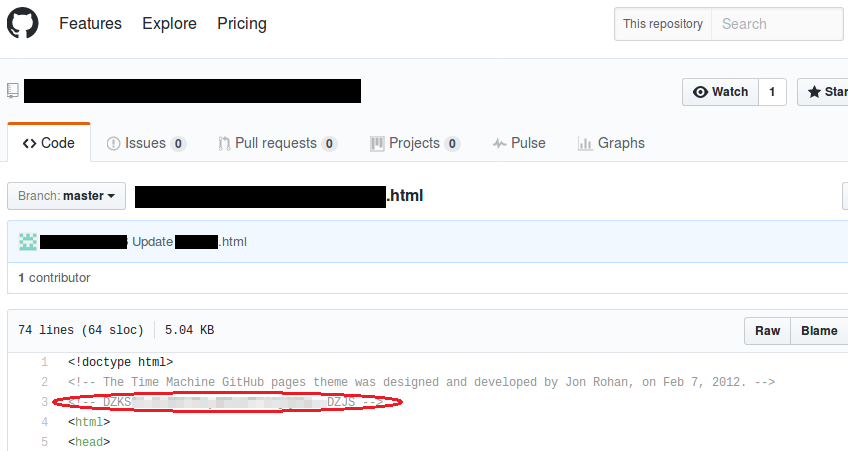
Trend Micro discovered the Chinese threat actor Winnti has been abusing GitHub service for command and control (C&C) communications. Security experts at Trend Micro continue to monitor the activities of the Chinese Winnti hacker group, this time the hackers have been abusing GitHub for command and control (C&C) communications. “Recently, the Winnti group, a threat actor with […]
 Pierluigi Paganini
January 26, 2017
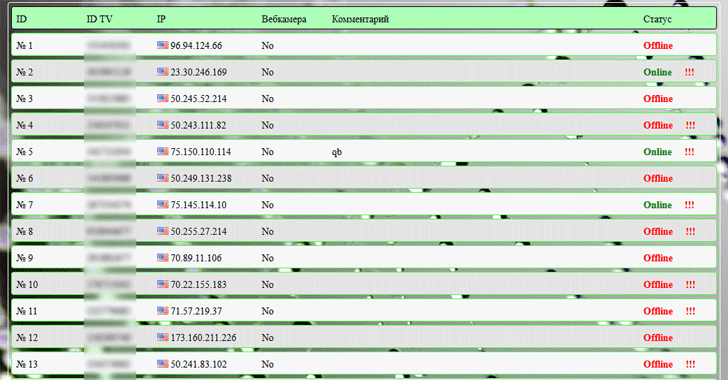
According to the security firm Dr. Web , thousands of Linux-based devices have already been infected with the Linux.Proxy.10 Trojan. A new Trojan dubbed Linux.Proxy.10 is targeting Linux-based devices transforming them into proxy servers that are used by attackers to protect their anonymity while launching cyber attacks from the hacked systems. Linux.Proxy.10 was first discovered by […]
 Pierluigi Paganini
December 14, 2016
Experts from Trustwave discovered an authentication bypass vulnerability affecting the Mac version of Skype, experts classified it as a Skype backdoor. Security experts from Trustwave have discovered a backdoor in the Mac version of Skype. The flaw, aAn authentication bypass vulnerability, affects the Desktop API that could be used by third-party apps to implement a Skype communication. […]
 Pierluigi Paganini
December 14, 2016
Experts from Doctor Web spotted new Trojans into the firmware of several dozens of low-cost Android smartphones and tablets. Again problems with low-cost Android smartphones and tablets, once again experts discovered certain mobile devices shipped with malicious firmware. According to malware researchers from antivirus firm Dr.Web, the firmware of a large number of popular Android devices […]
 Pierluigi Paganini
December 09, 2016
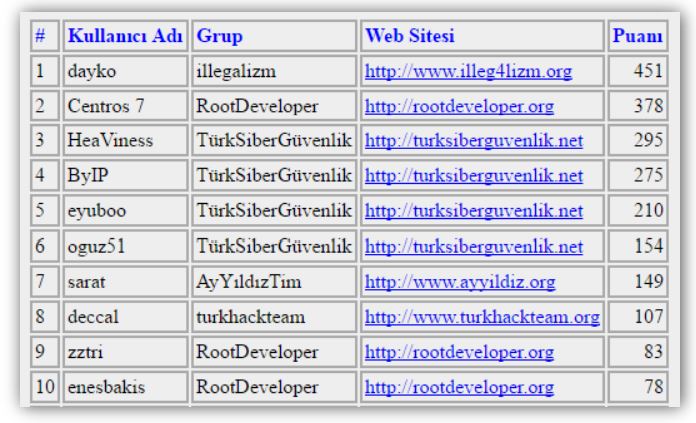
A Turkish hacker is advertising into the hacking underground a new DDoS platform, dubbed Surface Defense (Translation to English). According to the security firm Forcepoint the hacker started prompting the DDoS platform in Turkey. He was offering a tool known as Balyoz, the Turkish word for Sledgehammer, that can be exploited by hackers to launch […]
 Pierluigi Paganini
November 20, 2016
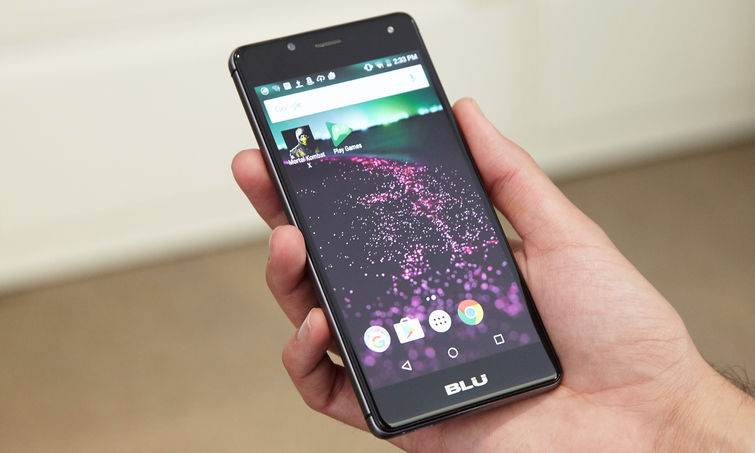
For the second time in a few days, security experts spotted a backdoor in the firmware of low-cost Android devices. Last week, security experts from Kryptowire firm have discovered a backdoor in the firmware installed on low-cost Android phones. The backdoor affects mobile phones from BLU Products that are available for sale on both Amazon and Best Buy. The […]
Pierluigi Paganini
November 15, 2016
Experts at Kryptowire discovered a mobile phone firmware that transmitted personally identifiable information without user consent due to a backdoor. Security experts from Kryptowire firm have discovered a backdoor in the firmware installed on low-cost Android phones. The backdoor affects mobile phones from BLU Products that are available for sale on both Amazon and Best Buy. […]
 Pierluigi Paganini
November 12, 2016
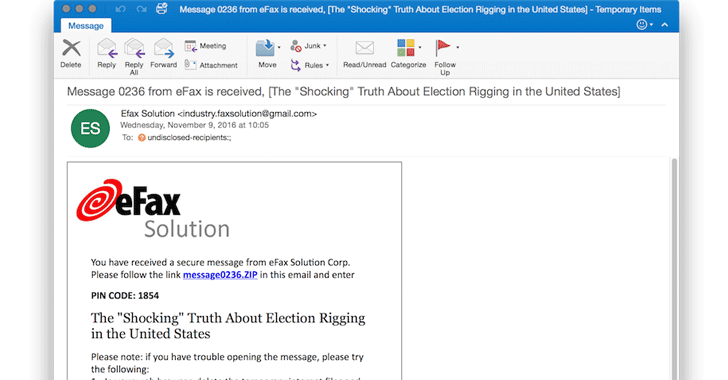
Cozy Bear launched new spear-phishing attacks against US policy think-tanks aiming to infect their systems with a malware. Trump is the new US President, a few hours after he won the election, a hacking crew powered several spear-phishing attacks against US policy think-tanks aiming to infect their systems with a malware. The security experts believe […]