


 Pierluigi Paganini
 September 10, 2026
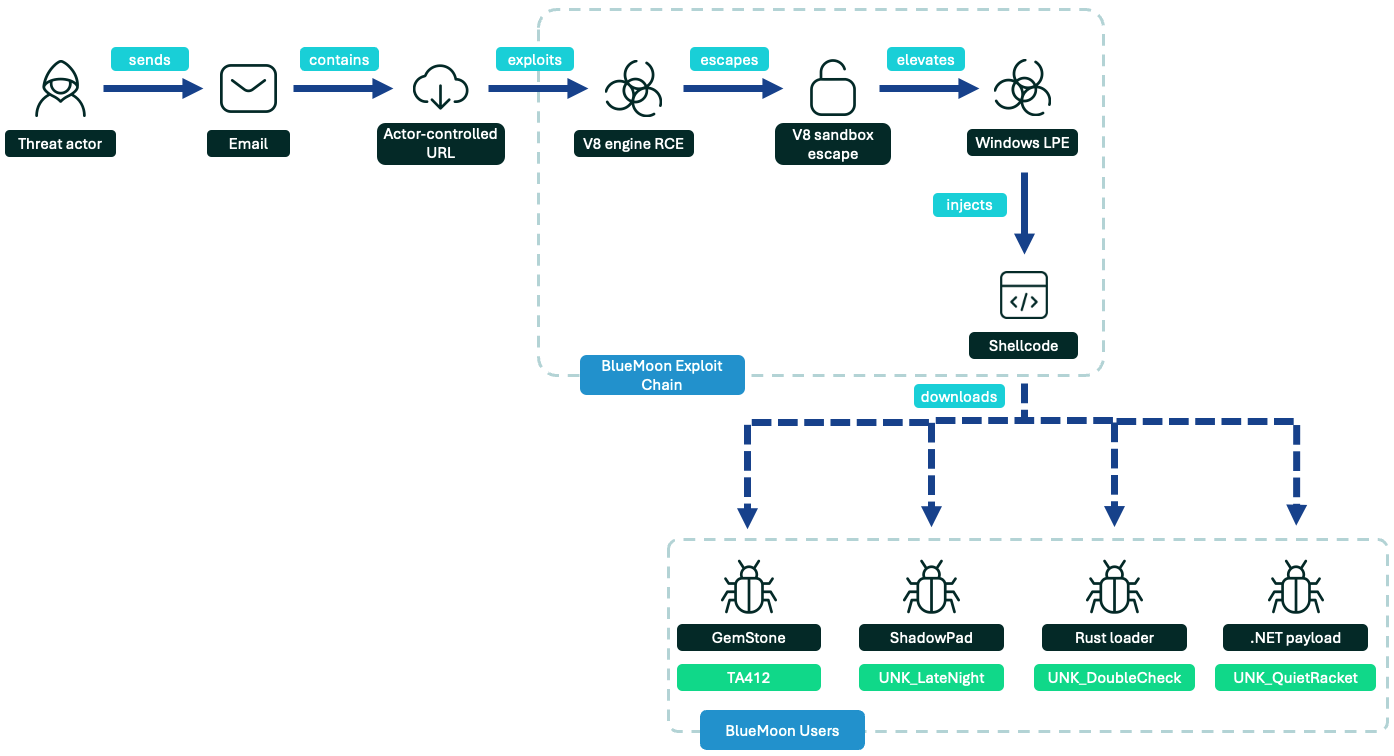
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 09, 2026
US agencies accuse six Chinese AI firms of extracting billions of tokens from US AI models to accelerate development and copy advanced capabilities. NSA, CISA, and the FBI jointly published an advisory accusing six Chinese AI companies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, of running industrial-scale extraction campaigns against US frontier models since […]
 Pierluigi Paganini
September 09, 2026
Google patched 230 Chrome flaws, including an actively exploited V8 bug that could let attackers run arbitrary code through a crafted HTML page. Google released a Chrome update fixing 230 security vulnerabilities, including one already exploited in the wild tracked as CVE-2026-87491 (CVSS score of 8.8). The medium-severity flaw affects V8, Google’s open source high-performance […]
 Pierluigi Paganini
September 09, 2026
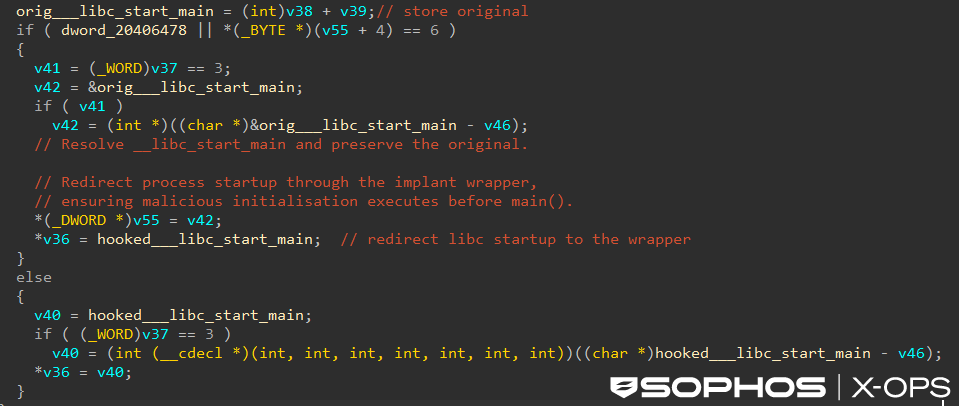
PoisonedRefresh rootkit injects PHP web shells into F5 BIG-IP APM Apache memory, leaving no disk artifacts. SophosLabs published a detailed technical analysis on September 8, 2026, of a Linux implant, dubbed PoisonedRefresh by ESET, they found in compromised F5 BIG-IP Access Policy Manager environments. Sophos tracks it as Linux/Agnt-IC. F5 has confirmed exploitation of the […]
 Pierluigi Paganini
September 09, 2026
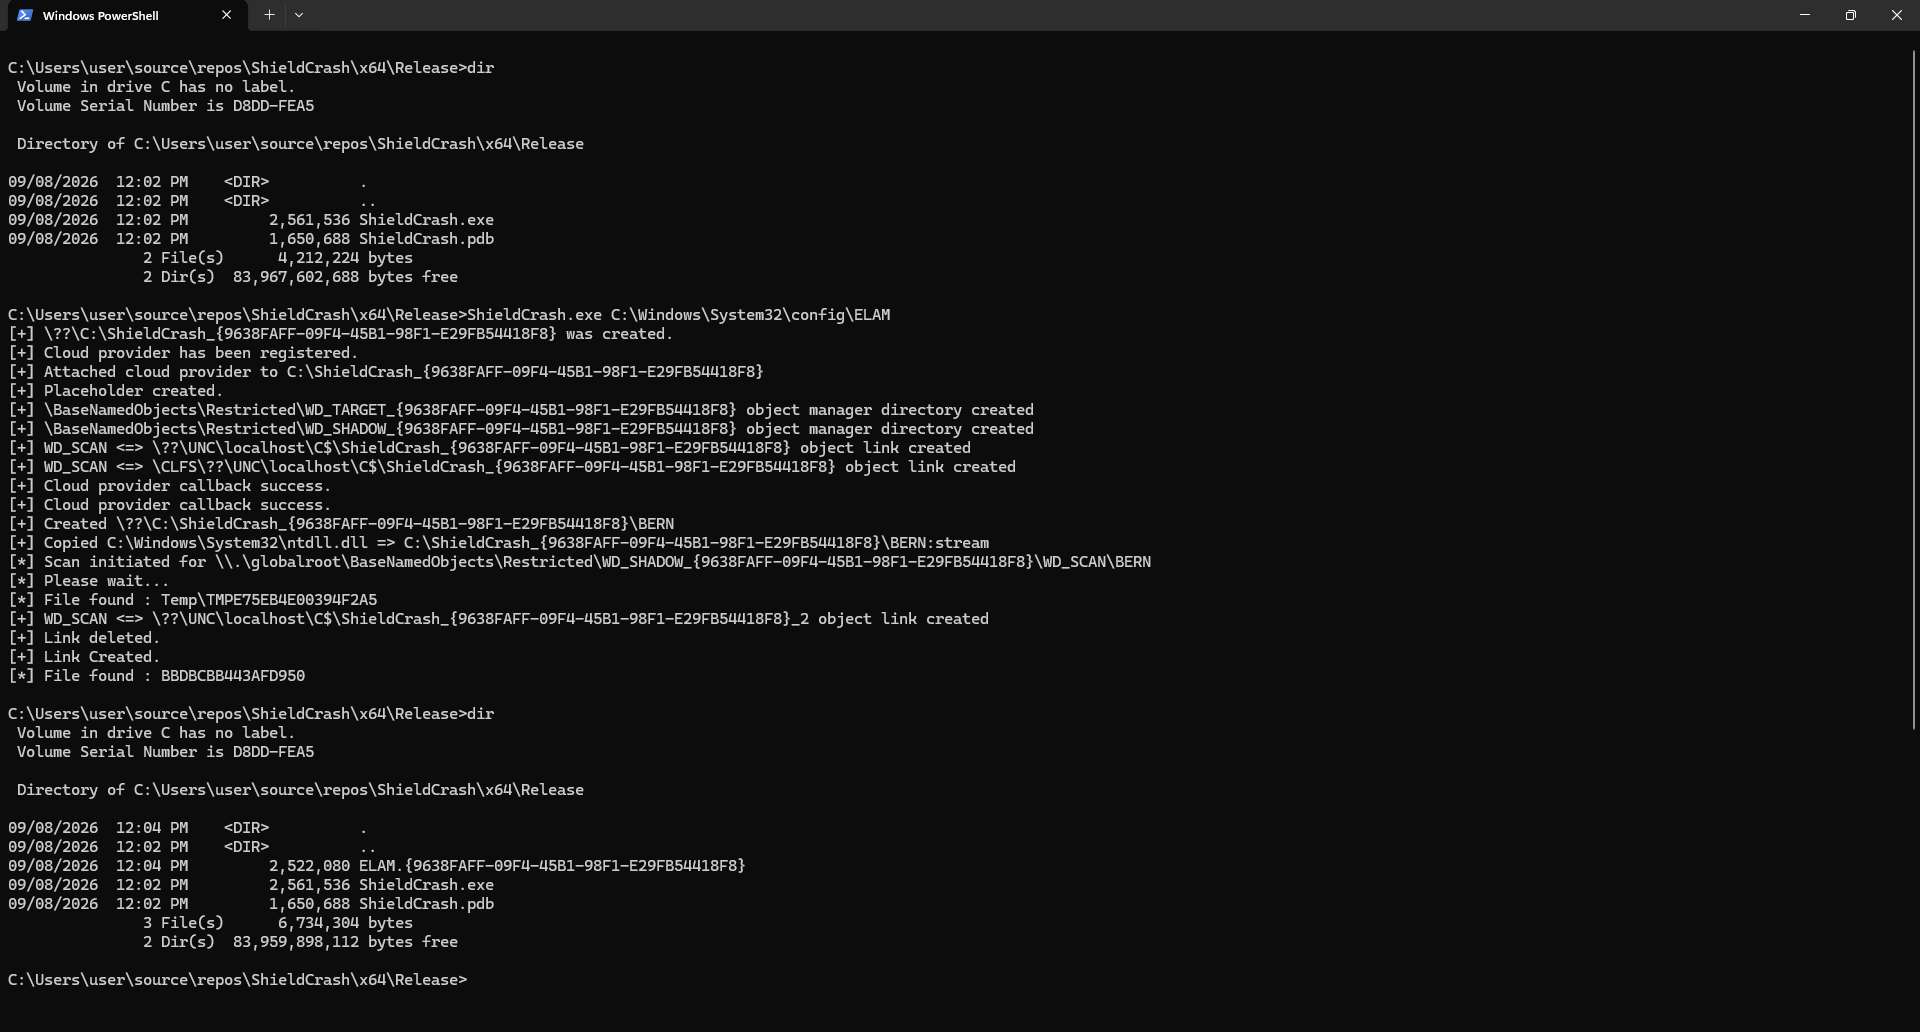
The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft Defender Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit ShieldCrash, it triggers an arbitrary file read as SYSTEM. The researcher claims that Microsoft has not fully […]
 Pierluigi Paganini
September 09, 2026
September 2026 Patch Tuesday fixes a record 974 CVEs including 2 exploited zero-days, 20 wormable bugs, and a critical Exchange RCE via Visio email. Microsoft’s September 2026 Patch Tuesday set a new record. Depending on how researchers count external and Chromium bugs, Microsoft fixed between 966 and 997 CVEs in this update. The company also […]
 Pierluigi Paganini
September 08, 2026
Crypto exchange network Liquid Network lost $320 million overnight, then got most of it back after the hackers demanded a bug fix instead of a ransom Bitcoin’s Liquid Network, a sidechain built by Blockstream and used by dozens of exchanges to move funds faster and more privately than the main Bitcoin blockchain allows, got drained […]
 Pierluigi Paganini
September 08, 2026
Researchers built a WeChat worm that spreads through incoming calls without user action. Tencent has blocked the exploit. Researchers at Calif created a WeChat worm that can take over an account through an incoming call, even if the victim never answers or touches the phone. The attack works only when the caller already appears in […]
 Pierluigi Paganini
September 08, 2026
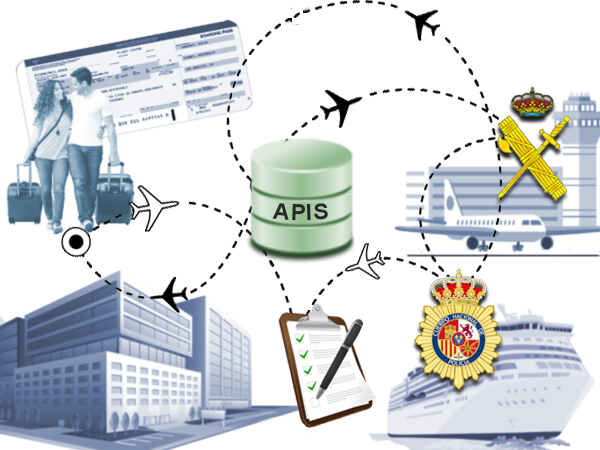
An exposed Vietnam-linked APIS database contained 220.8 million passenger and crew records, including passport and flight data. Researchers found an exposed Advance Passenger Information System (APIS) database containing 220.8 million passenger and crew records from January 2017 to April 2026. The data includes sensitive details such as passport numbers, identities and flight information, potentially affecting […]
 Pierluigi Paganini
September 08, 2026
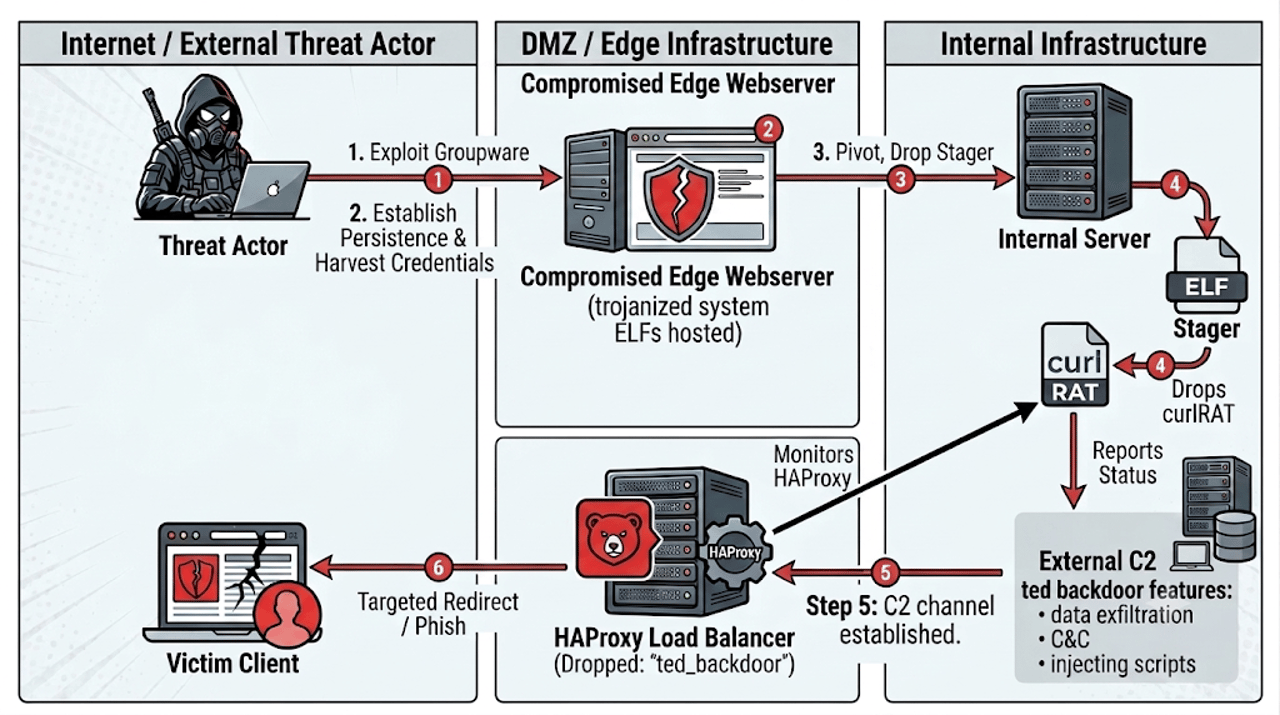
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]

Data Breach / September 16, 2026


