 Pierluigi Paganini
 October 16, 2026
F5 addressed multiple vulnerabilities, including critical RCE flaws in NGINX that attackers could exploit without authentication. Security and application delivery firm F5 announced fixes for eleven security issues in NGINX. Among them, critical vulnerabilities tracked as CVE-2026-15176 and CVE-2026-93479 could be exploited without authentication via crafted HTTP requests. Under certain conditions beyond their control, an […]
 Pierluigi Paganini
July 20, 2026
F5 fixes critical nginx flaw CVE-2026-42533 that can crash servers and, in some cases, allow remote code execution through crafted HTTP requests. F5 released patches for a critical nginx vulnerability, tracked as CVE-2026-42533 (CVSS score of 9.2), that can allow an unauthenticated attacker to trigger a heap buffer overflow using specially crafted HTTP requests. “heap […]
Pierluigi Paganini
June 18, 2026
F5 released emergency updates for critical NGINX flaws (CVE-2026-42530, CVE-2026-42055) that could enable unauthenticated code execution. F5 has issued out-of-band patches for multiple NGINX vulnerabilities, including two critical flaws, respectively tracked as CVE-2026-42530 and CVE-2026-42055 (CVSS 9.2). The bugs affect HTTP modules and can be exploited remotely without authentication to trigger memory corruption, potentially causing […]
Pierluigi Paganini
May 18, 2026
A critical NGINX flaw (CVE-2026-42945) is actively exploited, allowing crashes or possible code execution via malicious HTTP requests. A critical vulnerability in NGINX Plus and NGINX Open, tracked as CVE-2026-42945 (CVSS v4 score of 9.2), is already being actively exploited shortly after disclosure. “We’re seeing active exploitation of CVE-2026-42945 in F5 NGINX, a heap buffer […]
Pierluigi Paganini
May 14, 2026
Researchers found a critical 18-year-old buffer overflow flaw in NGINX, tracked as CVE-2026-42945 and named NGINX Rift. If you run NGINX, and statistically speaking, there is a very good chance you do, this week brought news worth stopping for. Security researchers at depthfirst disclosed a critical heap buffer overflow vulnerability in both NGINX Plus and […]
Pierluigi Paganini
April 15, 2026
An actively exploited critical nginx-ui flaw (CVE-2026-33032) lets attackers bypass authentication and take full control of Nginx servers. A critical vulnerability in nginx-ui, tracked as CVE-2026-33032 (CVSS score of 9.8), is being actively exploited, allowing attackers to bypass authentication and fully take over Nginx servers. The issue stems from improper protection of the /mcp_message endpoint, […]
Pierluigi Paganini
April 12, 2022
The maintainers of the NGINX web server project addressed a zero-day vulnerability in the Lightweight Directory Access Protocol (LDAP) Reference Implementation. The maintainers of the NGINX web server project have released security updates to address a zero-day vulnerability that resides in its Lightweight Directory Access Protocol (LDAP) Reference Implementation. The NGINX LDAP reference implementation uses […]
 Pierluigi Paganini
January 24, 2022
Cybersecurity provider F5 released security patches to address 25 vulnerabilities affecting its BIG-IP, BIG-IQ, and NGINX products. Cybersecurity firm F5 announced security patches for 25 vulnerabilities affecting its BIG-IP, BIG-IQ, and NGINX products. Most of the vulnerabilities (23) addressed by the company affect the BIG-IP application delivery controller (ADC), 13 of them have been rated […]
 Pierluigi Paganini
December 02, 2021
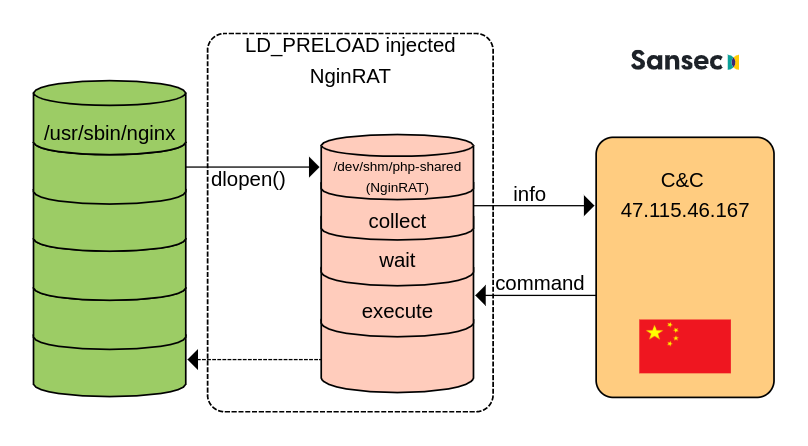
Threat actors are targeting e-stores with remote access malware, dubbed NginRAT, that hides on Nginx servers bypassing security solutions. Researchers from security firm Sansec recently discovered a new Linux remote access trojan (RAT), tracked as CronRAT, that hides in the Linux task scheduling system (cron) on February 31st. CronRAT is employed in Magecart attacks against online stores […]
 Pierluigi Paganini
October 26, 2019
asty PHP7 remote code execution bug exploited in the wild Experts warn of a remote code execution vulnerability in PHP7, tracked as CVE-2019-11043, has been exploited in attacks in the wild. A remote code execution vulnerability in PHP7, tracked as CVE-2019-11043, has been exploited in attacks in the wild. On October 22, the security expert […]



Hacking / October 29, 2026