


 Pierluigi Paganini
 September 18, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients include eBay, Louis Vuitton and Michelin. The company was first compromised on September 10, when attackers exploited a vulnerability in its […]
 Pierluigi Paganini
September 02, 2025
Palo Alto Networks hit by Drift-linked supply-chain attack, exposing Salesforce customer data and support cases via stolen OAuth tokens. Palo Alto Networks is another victim of the Salesloft Drift incident, which allowed attackers to access its Salesforce account, as per BleepingComputer. The company discloses a breach after attackers used stolen OAuth tokens from Salesloft Drift, […]
 Pierluigi Paganini
May 14, 2021
Rapid7 disclosed that unauthorized third-party had access to source code and customer data as result of Codecov supply chain attack. Cyber security vendor Rapid7 reveals it was impacted by the Codecov software supply chain attack, attackers had access to data for part of its customers and a small subset of its source code repositories for […]
 Pierluigi Paganini
January 06, 2021
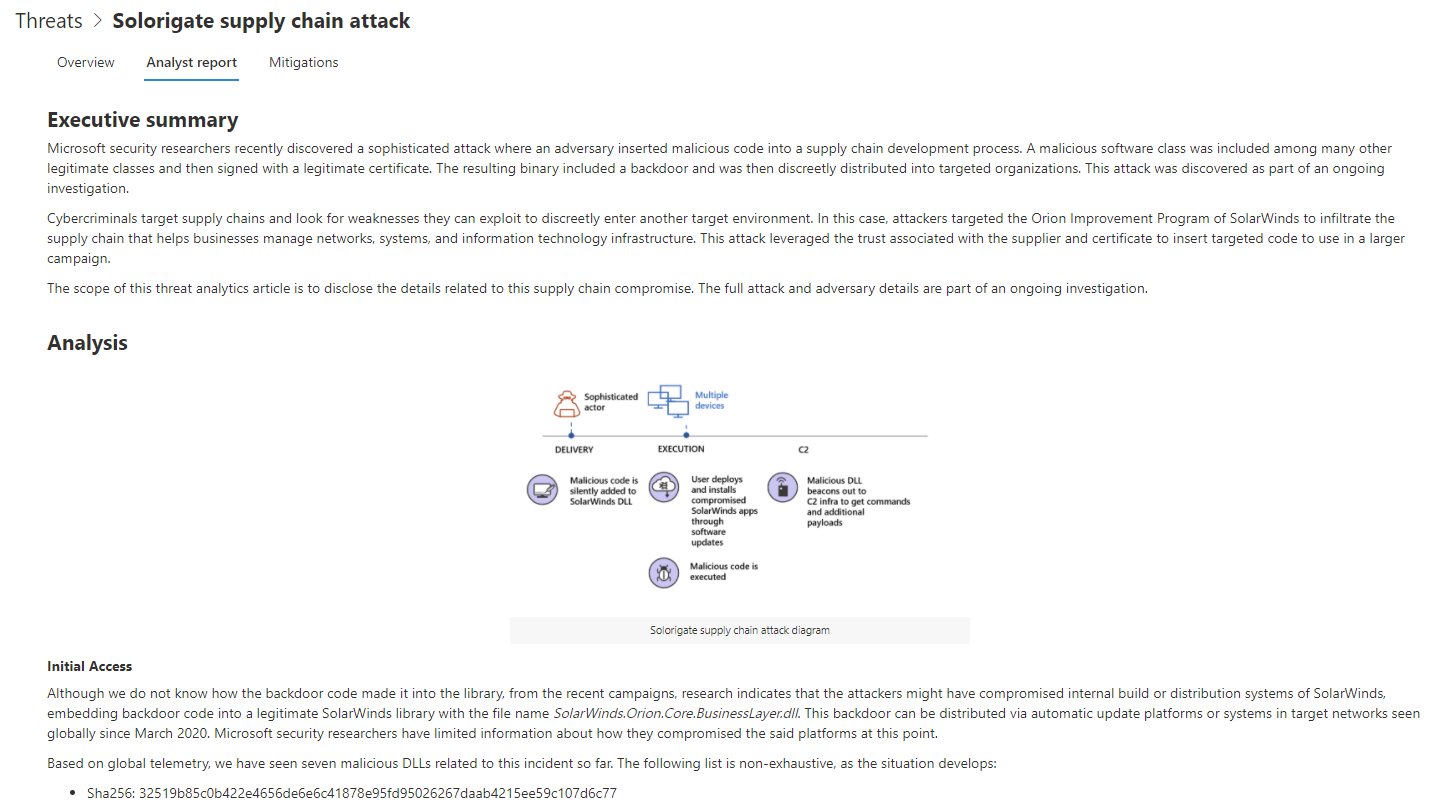
A joint statement issued by US security agencies confirmed that Russia was likely the origin of the SolarWinds supply chain attack. The US agencies FBI, CISA, ODNI, and the NSA released a joint statement that blames Russia for the SolarWinds supply chain attack. On behalf of President Trump, the four agencies were part of the task force […]
Uncategorized / September 27, 2026
Cyber Crime / September 26, 2026

Security / September 26, 2026
