


 Pierluigi Paganini
 August 25, 2016
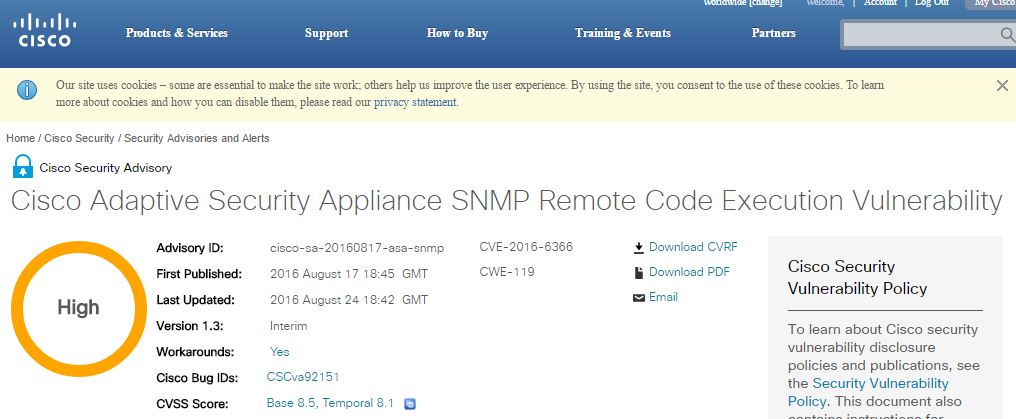
Cisco has started releasing patches for its ASA software to address the Equation Group’s EXTRABACON exploit included in the NSA data dump leaked online. Security firms and IT giants are analyzing the huge archive leaked by the Shadow Brokers crew after the hack of the NSA-linked Equation Group. We reported that some of the exploits […]
 Pierluigi Paganini
August 20, 2016
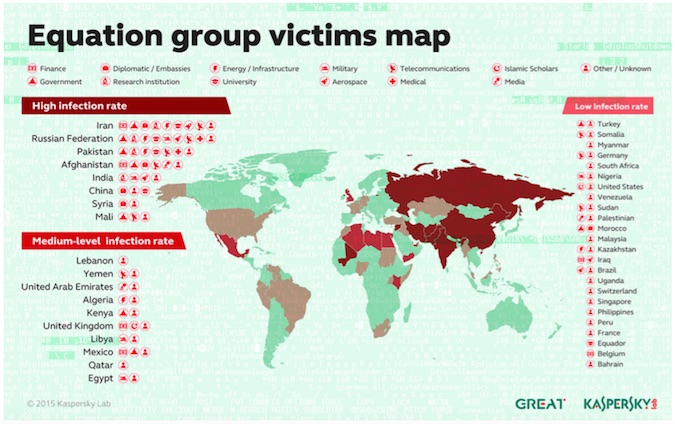
Researchers tested the BENIGNCERTAIN tool included in the NSA data dump that allows attackers to extract VPN passwords from certain Cisco devices. Following the disclosure of the NSA dump, IT vendors Cisco and Fortinet issued security patches to fix the flaws exploited by the Equation Group in their products. Now, security researchers have uncovered another […]
 Pierluigi Paganini
June 16, 2016
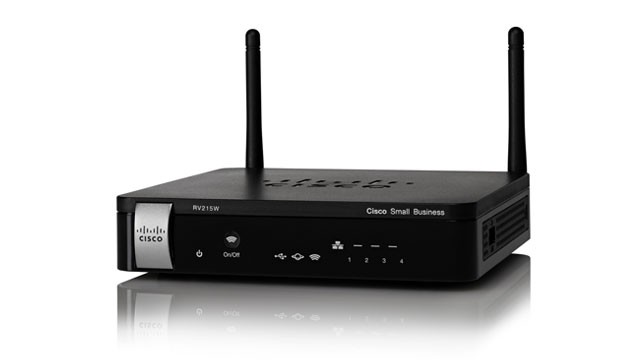
A security advisory recently released by CISCO announce that three Cisco wireless kits are affected by a critical bug, but no fix is available at the moment. SOHO devices are among most targeted network components in the wild, they are often poorly protected or not properly configured exposing users to serious risks. In these cases, […]
 Pierluigi Paganini
January 27, 2016
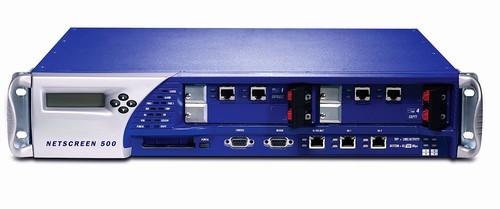
The U.S. House Oversight and Government Reform Committee is probing US Government Agencies over use of backdoored Juniper equipment. A number of US Government Agencies are concerned about the use of Juniper firewalls affected by the recently uncovered backdoor. The U.S. House Oversight and Government Reform Committee has sent letters to dozens of government agencies and departments asking […]
 Pierluigi Paganini
December 18, 2015
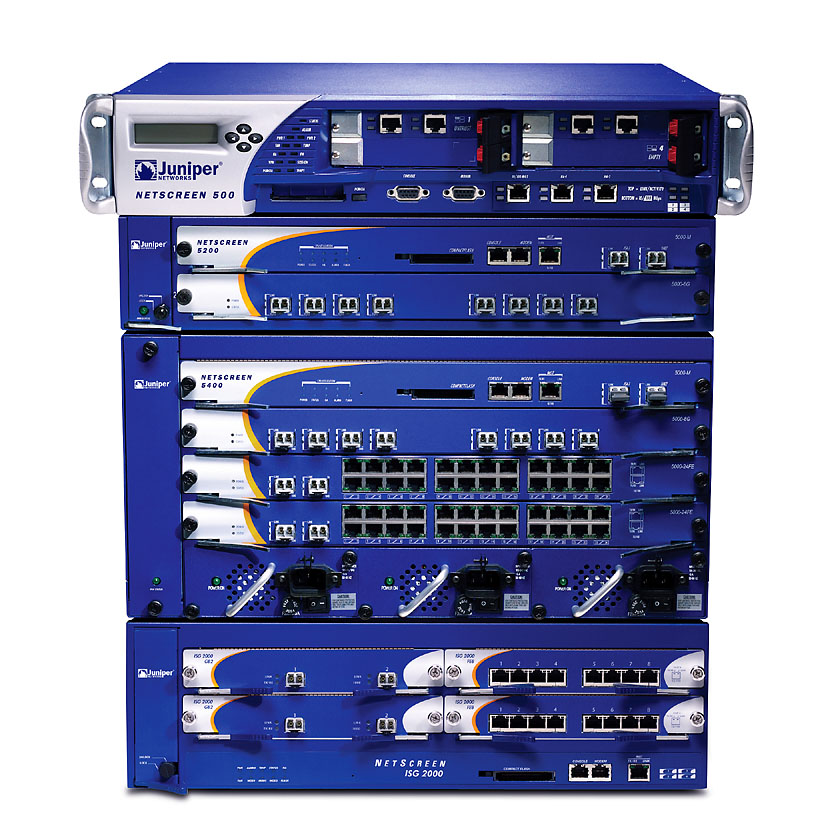
An operating system running on firewalls sold by Juniper Networks contains unauthorized code that could be exploited to decrypt traffic sent through virtual private networks. An “unauthorized code” was discovered in the operating system for Juniper NetScreen firewalls. The company admitted the presence of the “unauthorized code” that could allow an attacker to decrypt VPN traffic. [“unauthorized code”] “could allow […]
 Pierluigi Paganini
November 27, 2015
Security experts at the VPN provider Perfect Privacy discovered a new vulnerability dubbed Port Fail that could be exploited to de-anonymize VPN users. Security experts at the VPN provider Perfect Privacy discovered a new vulnerability dubbed Port Fail which affect all VPN (Virtual Private Network) protocols and operating systems. An attacker can exploit the Port Fail flaw […]
 Pierluigi Paganini
October 24, 2015
Now that it is known a critical flaw in the Diffie-Hellman key-exchange protocol was exploited by the NSA to break the internet encryption, how to stop it? Recently a group of researchers has revealed how the NSA has cracked HTTPS, SSH, and VPNs rely on the Diffie-Hellman encryption by exploiting a wrong implementation of the cryptographic algorithm. The […]
 Pierluigi Paganini
October 09, 2015
Experts at Volexity discovered a hacking campaign targeting the CISCO WebVPN VPN product, attackers aim to steal corporate login credentials. A virtual private network (VPN) allows to extend a private network across a public connection, they are mainly used to protect users’ privacy and improve security for data in transit. Virtual Private Networks are commonly used many companies and organizations […]
 Pierluigi Paganini
December 30, 2014
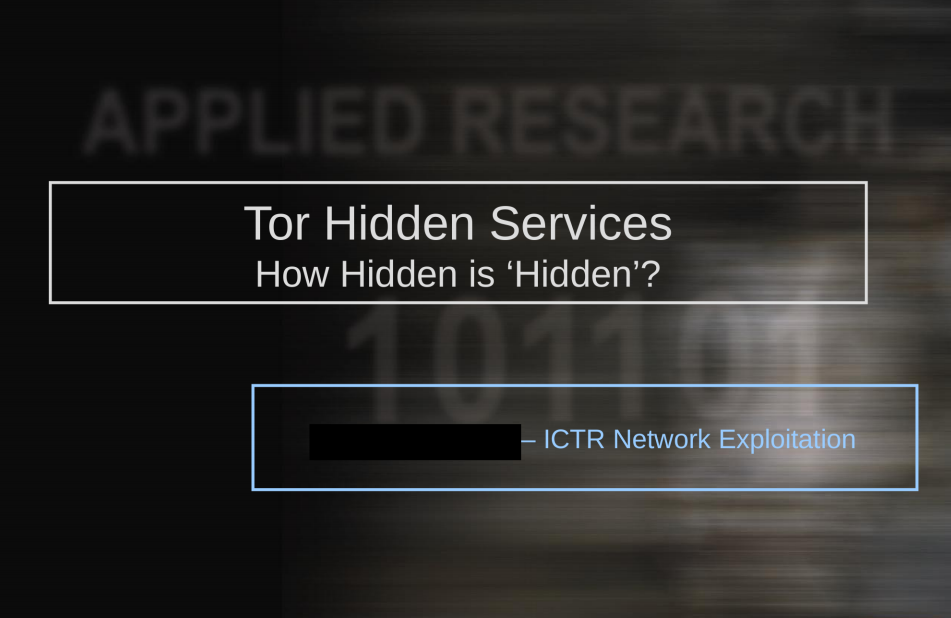
A new collection of documents leaked by Snowden and disclosed by the Der Spiegel reveals the difficulties of Intelligence agencies to de-anonymize Tor users A new collection of NSA documents crawled by the Edward Snowden was leaked online during the weekend, the German news agency Der Spiegel has published online a dump of PDF files […]
 Pierluigi Paganini
August 03, 2014
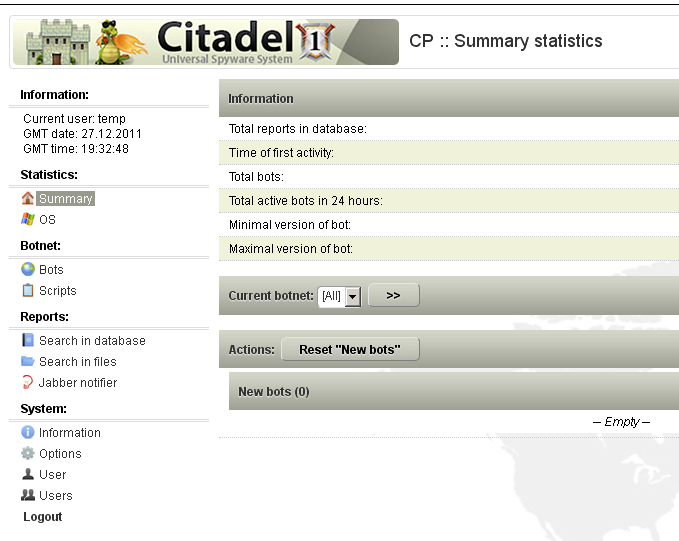
Experts at IBM discovered a new variant of Citadel banking malware which includes different remote management tools to maintain persistence on victims’ PC. Researchers at IBM discovered a new variant of the Citadel banking malware which includes a new interesting feature that allows attackers to maintain persistence in the victim’s machine through remote management tools. Citadel is directly […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026


